

secure-agent-playbook
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
ai-securityapi-securitycloud-security+9
1996 days ago
owasp/secure-agent-playbookOWASP Secure Agent Playbook Project
 mastyf-ai/mastyf.ai
Open-source AI security platform providing perimeter defense for LLMs and AI agents through swarm analysis, policy enforcement, adversarial testing,…
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 ksnnd32/redis_exploit
🔍 Explore and test the CVE-2025-49844 (RediShell) vulnerability in Redis with this practical lab environment for secure education and research.
 chipsec/chipsec
Platform Security Assessment Framework
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.

 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
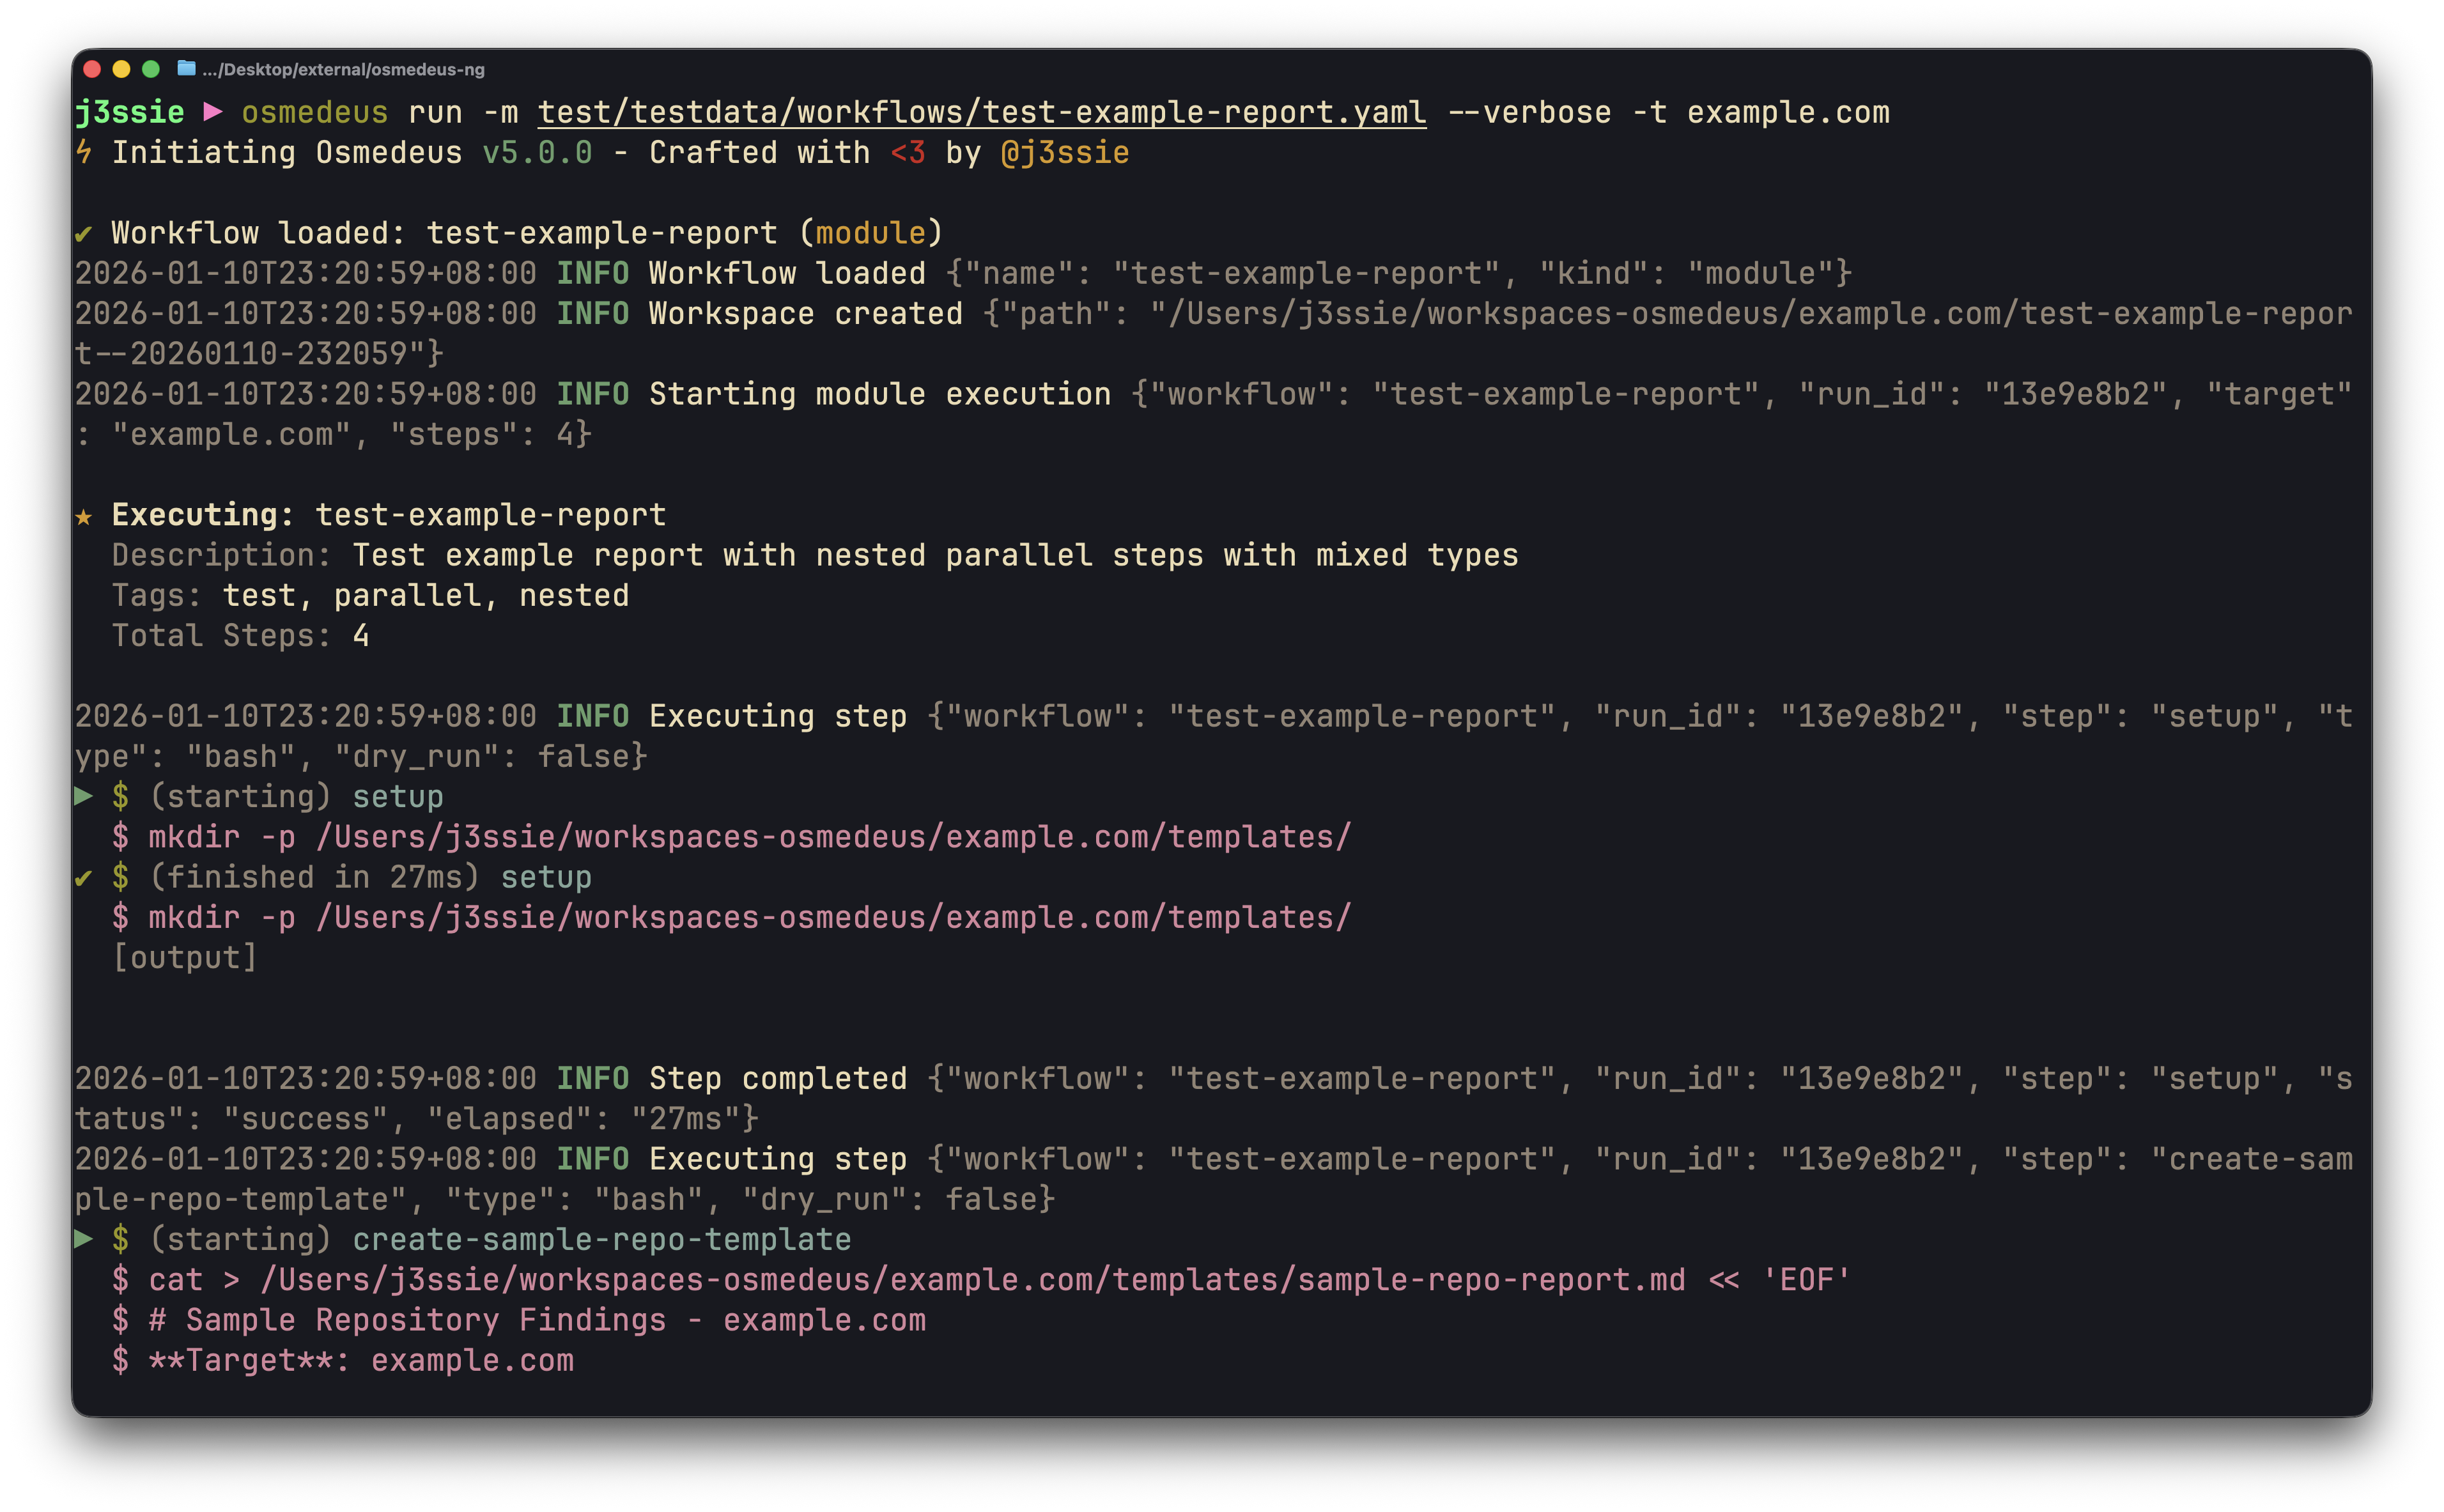 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…