
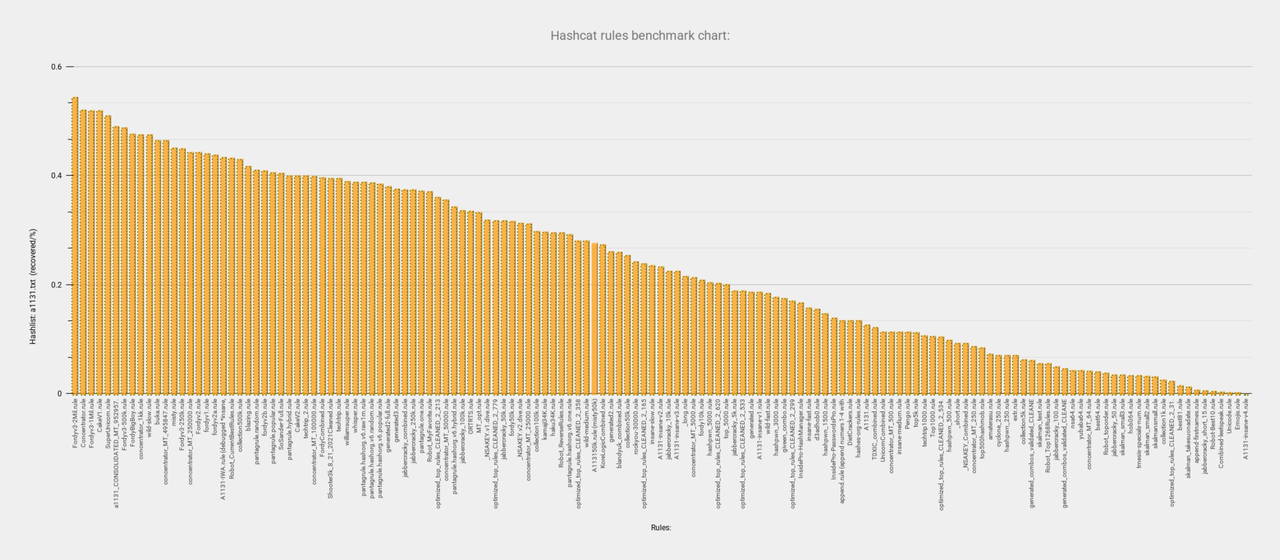
rules
 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
curated-resourcespassword-attackspassword-cracking+2
74
ibnaleem/rulesCurated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 eqstlab/cve-2026-72898
Unauthenticated blind SQL injection exploit for Metabase, exploiting a raw SQL injection in the password reset endpoint to extract data via…
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 s3cur3th1ssh1t/creds
Some usefull Scripts and Executables for Pentest & Forensics
 zzzteph/weakpass
Browser-based password cracking toolkit with hash lookup, wordlist generation, rule-based attack simulation, and client-side hash cracking for…
 jenderal92/prepos-login-checker
Prepostseo Login Checker
 groppoxx/cve-2025-25198-poc
PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.
 mananispiwpiw/cve-2025-58434-poc
CVE-2025-58434 Proof of Concept
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
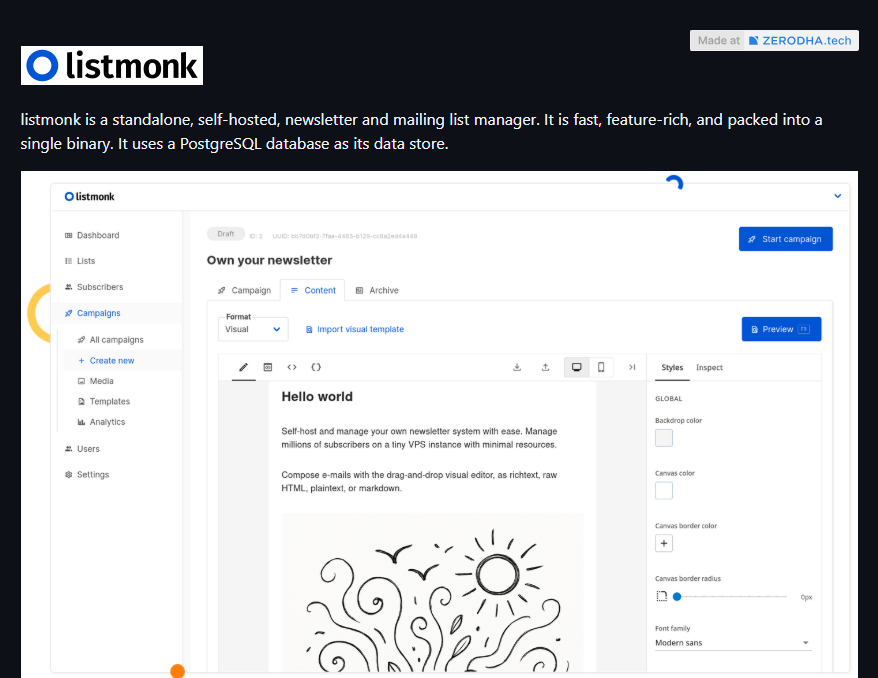 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
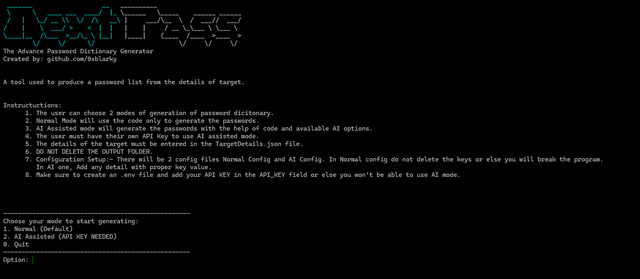 0xblarky/nextpass
A tool which can be used to generate password list or dictionary from the details of the target
 enzocipher/cve-2025-25198
Captures password reset tokens from Mailcow Host header injection attacks.
 mirchr/security-research
Security Research