
CVE-2026-24061
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
authenticationeducationexploitation+3
obrunolima1910/cve-2026-24061🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
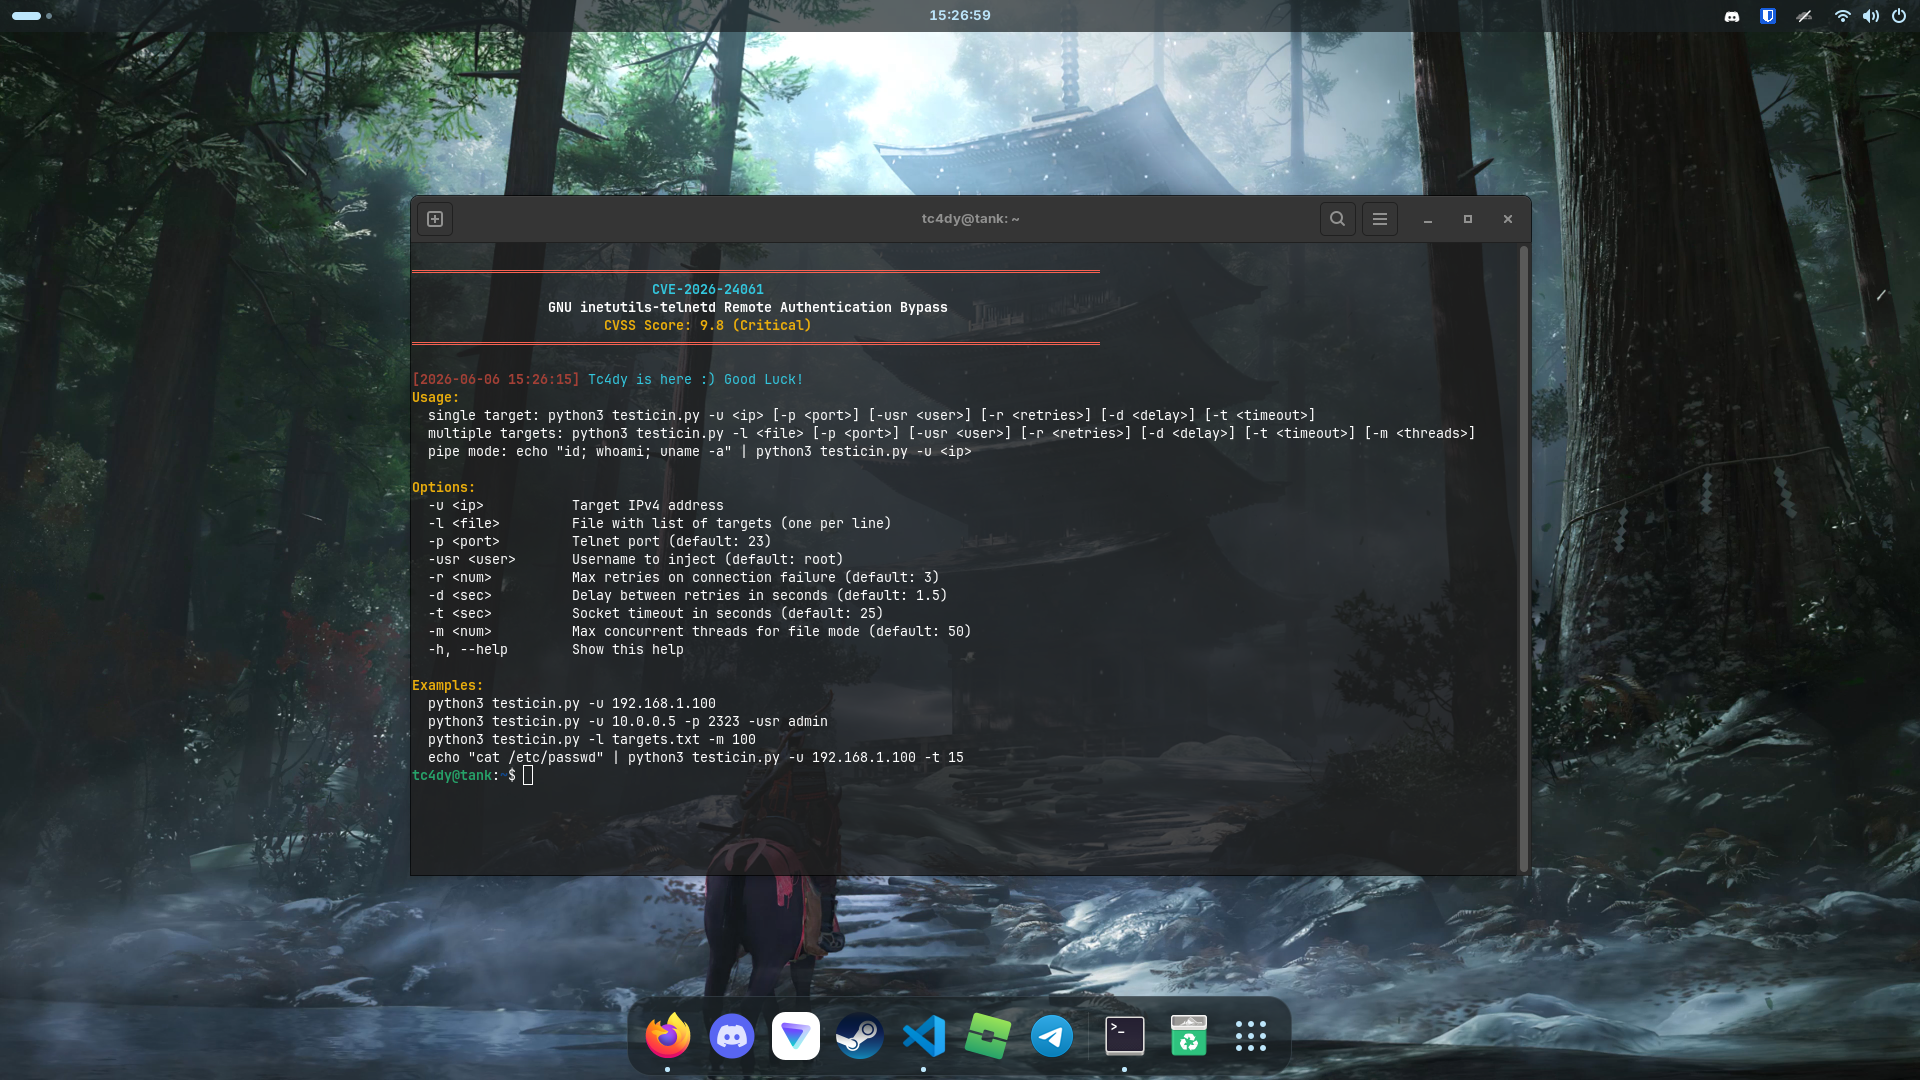 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 ilokaas/cve-2026-24061-payload
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 0xblackash/cve-2026-24061
CVE-2026-24061
 akpmarcelin/cve-2026-24061-lab
Reproduction lab for CVE-2026-24061, an authentication bypass in GNU InetUtils telnetd. Provides a Vagrant-based isolated environment and…
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 supermagnum/gr-qradiolink
GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
 ahmadsadeeq/telnetdbypass-
CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 kaleth4/cve-2026-32746
Proof-of-concept exploit for CVE-2026-32746, a critical remote code execution vulnerability in GNU Inetutils telnetd via LINEMODE SLC buffer…
 midox008/cve-2026-24061
GNU Inetutils telnetd Remote Authentication Bypass
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.
 mbanyamer/cve-2026-28372-gnu-inetutils-telnetd-privilege-escalation
Proof-of-concept exploit for CVE-2026-28372, demonstrating local privilege escalation in GNU inetutils telnetd via CREDENTIALS_DIRECTORY and…