
cve-2025-24893
 hackersonsteroids/cve-2025-24893
Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…
educationexploitationpayload-development+3
5
hackersonsteroids/cve-2025-24893Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…
 deeexcee-io/cve-2021-44731-snap-confine-suid
Local privilege escalation exploit for CVE-2021-44731 targeting snap-confine versions 2.54.2 and lower. Automatically detects vulnerable binaries and…
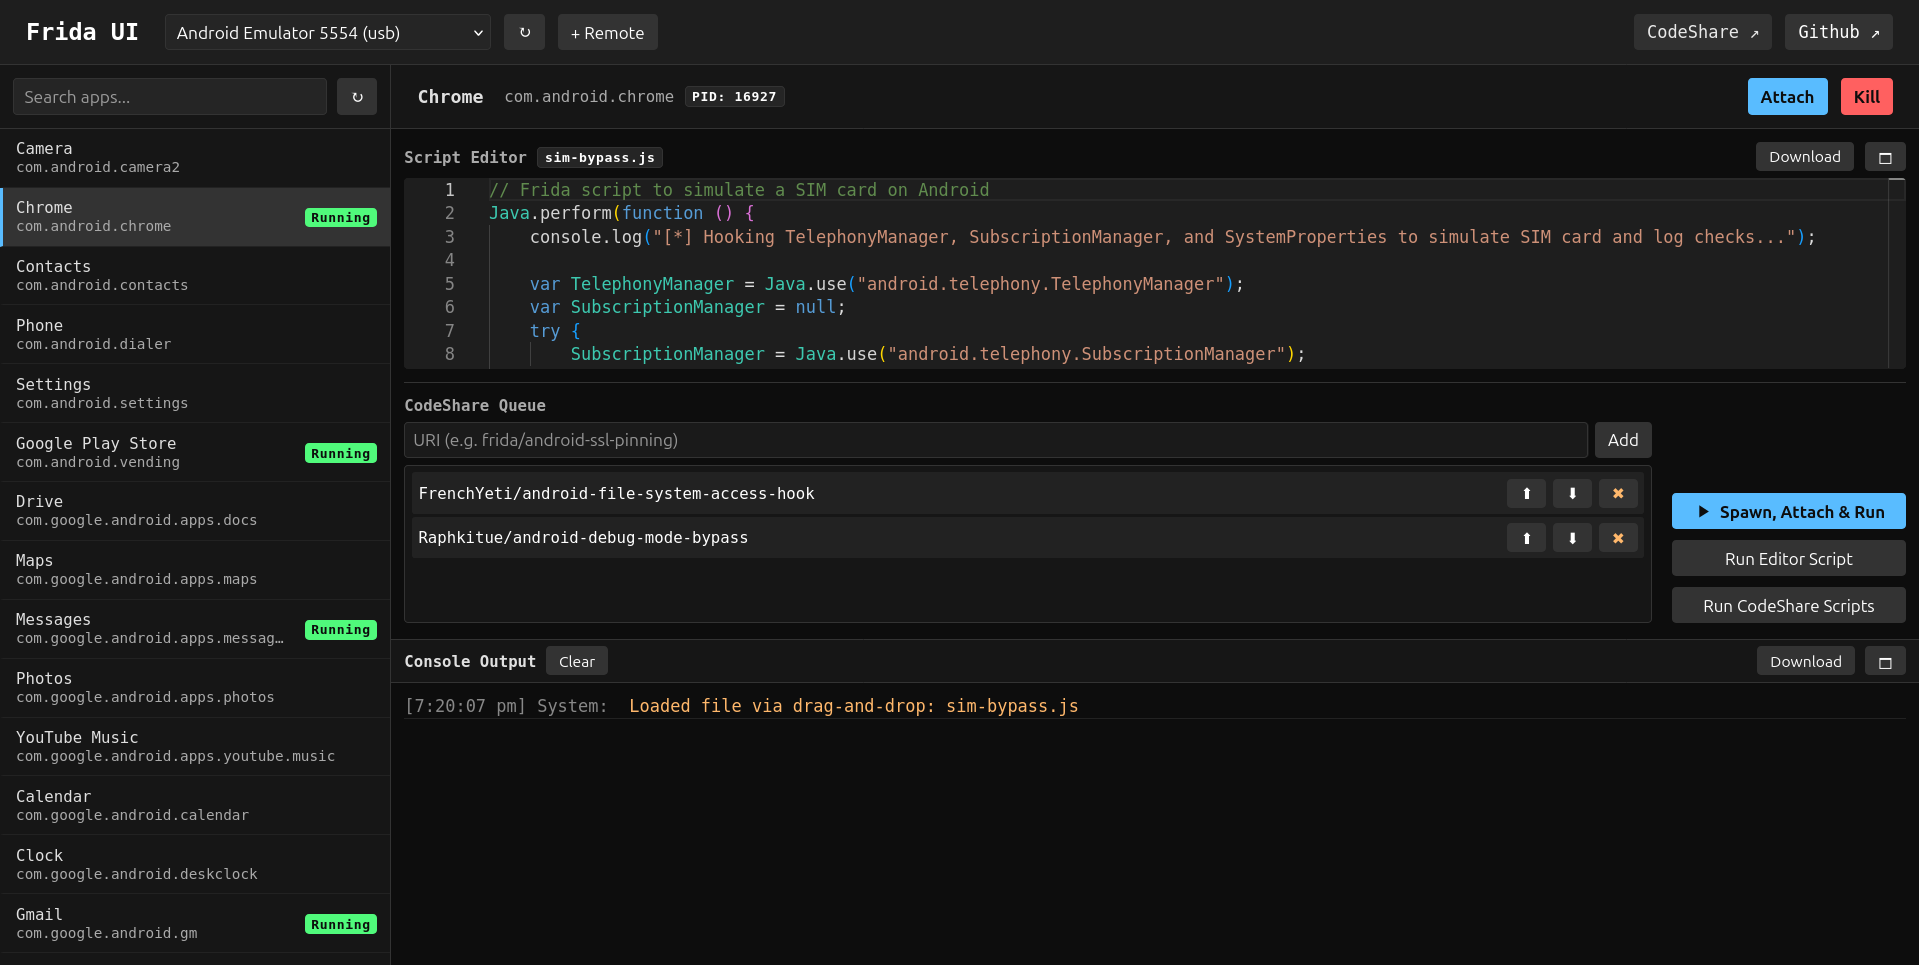 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…