
CVE-2026-26980
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
database-securityeducationexploitation+5
1
yym8538/cve-2026-26980Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 hyderpwn/weblogic
Unauthenticated authentication bypass and remote code execution exploit for Oracle WebLogic Server, targeting CVE-2020-14882 and CVE-2020-14750.
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 samael0x4/cve-2026-21962
Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…
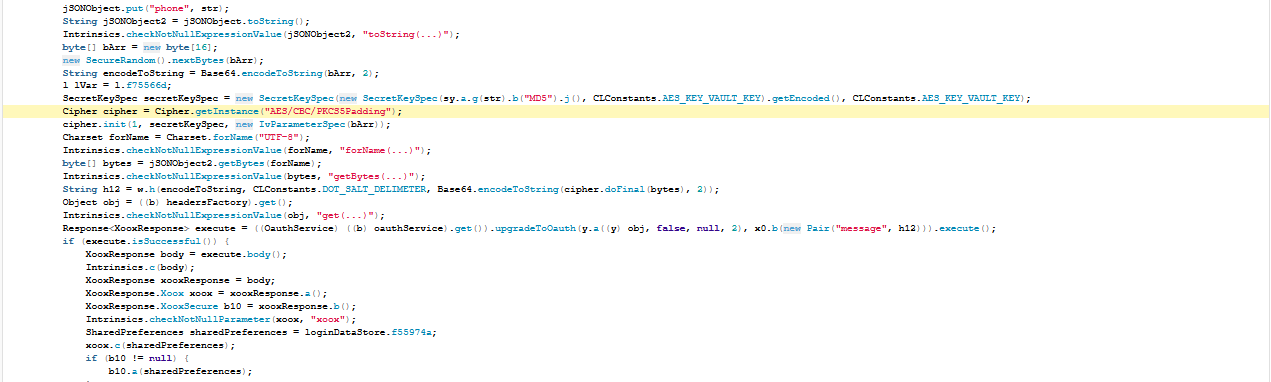 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 gregk4sec/cve-2026-21962
Proof-of-concept exploit for CVE-2026-21962, a critical path traversal vulnerability in Oracle OHS and WebLogic Server proxy plugins leading to…
 gregk4sec/cve-2026-21962-o
Proof-of-concept for CVE-2026-21962, a critical unauthenticated remote vulnerability in Oracle HTTP Server and WebLogic Proxy Plug-in, demonstrating…
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 zz-socmap/cve-2021-35587
Proof-of-concept exploit for CVE-2021-35587, an unauthenticated remote code execution vulnerability in Oracle Access Manager, allowing full takeover…
 sachinart/cve-2025-61882
Multi-threaded scanner for CVE-2025-61882 in Oracle E-Business Suite, exploiting HTTP request smuggling to achieve unauthenticated remote code…
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 george0papasotiriou/cve-2026-21962-oracle-http-server-weblogic-proxy-plug-in-critical-
Oracle Fusion Middleware Oracle HTTP Server / WebLogic Server Proxy Plug-in has an easily exploitable, unauthenticated, network-reachable flaw…
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…