CVE-2026-55794-craftcms-ssti

Dry-run-first Python PoC for Craft CMS CVE-2026-55794 signed-referrer SSTI, authenticating and confirming signed redirects before optional command…

Dry-run-first Python PoC for Craft CMS CVE-2026-55794 signed-referrer SSTI, authenticating and confirming signed redirects before optional command…

Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…

An in-memory minimal CPU for agnostic on-the-fly protocols creation

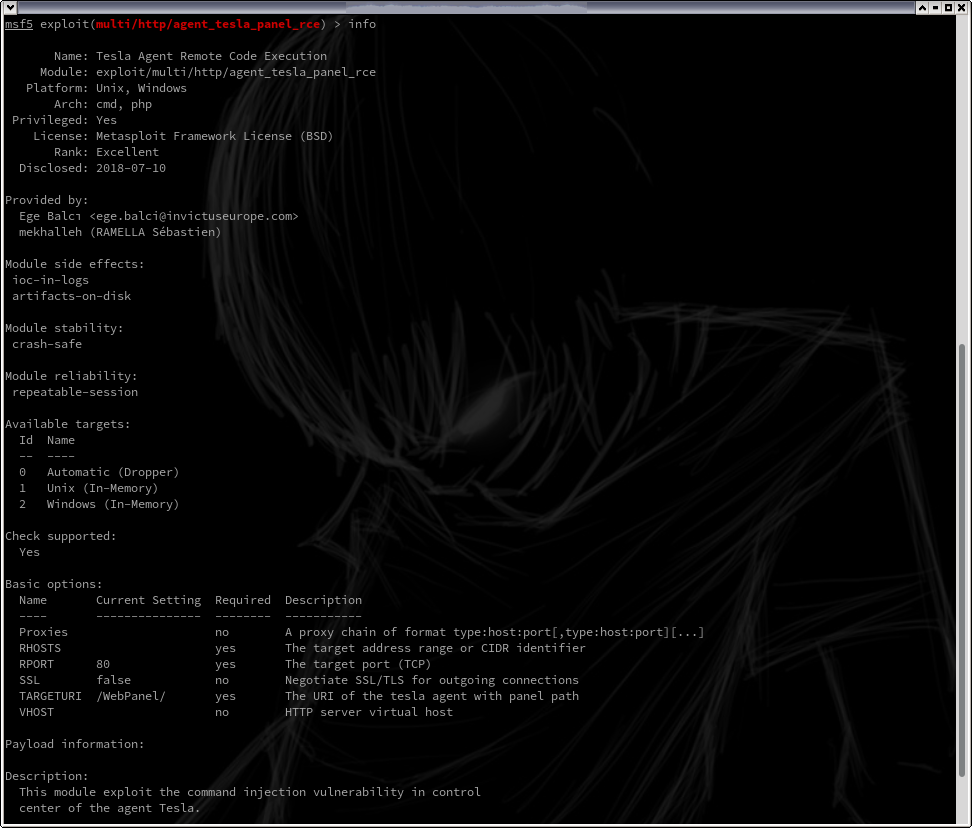
This is Metasploit module who exploit the command injection vulnerability in control center of the agent Tesla.

Google App Engine Flask C2 redirector

flask heroku C2 redirector template

Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]

React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)

Proof-of-concept exploit for CVE-2021-45026 targeting Rocket Software Zena. Chains stored XSS to remote code execution via REST API task injection on…

Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…

Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.

Proof of Concept of CVE-2022-30190

CVE Description

Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…

Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…

CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.

OpenPLC 3 WebServer Authenticated Remote Code Execution.

Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header