
spark-history-store-path
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
code-analysisexploitationlabs-practice+4
abraxas/spark-history-store-pathApache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
 abraxas/spark-history-zip-symlink
Apache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 hackwarts12/burp-recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
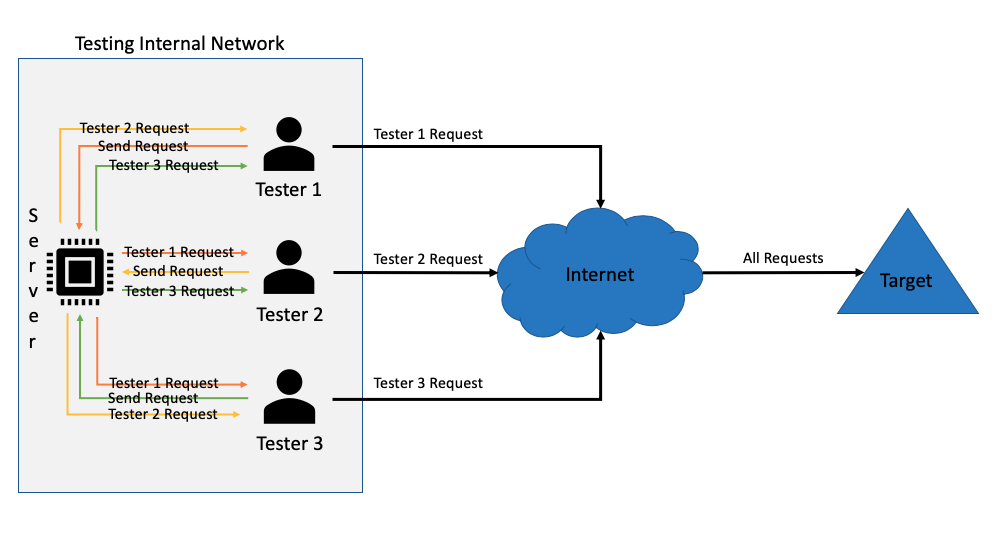 static-flow/burpsuite-team-extension
This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your…
 caido-community/burp2caido
A tool to migrate Burpsuite HTTP history to Caido
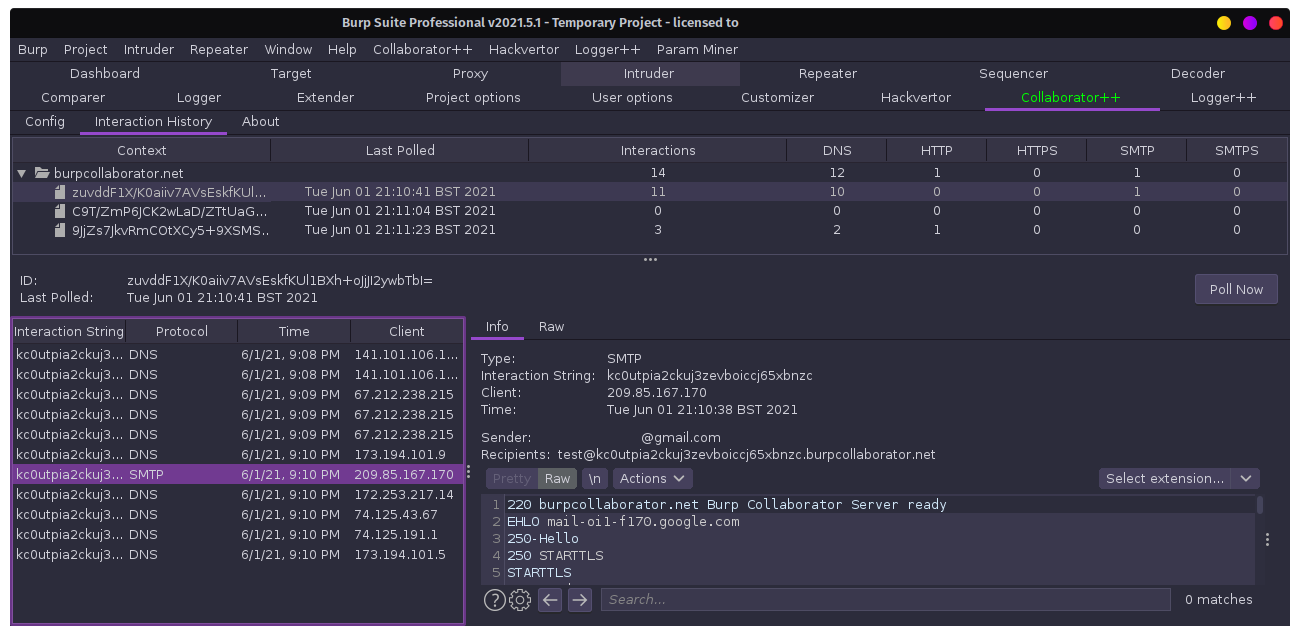 nccgroup/collaboratorplusplus
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…
 cappricio-securities/shell-history-leaks
This tool is used to find shell history leaking
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
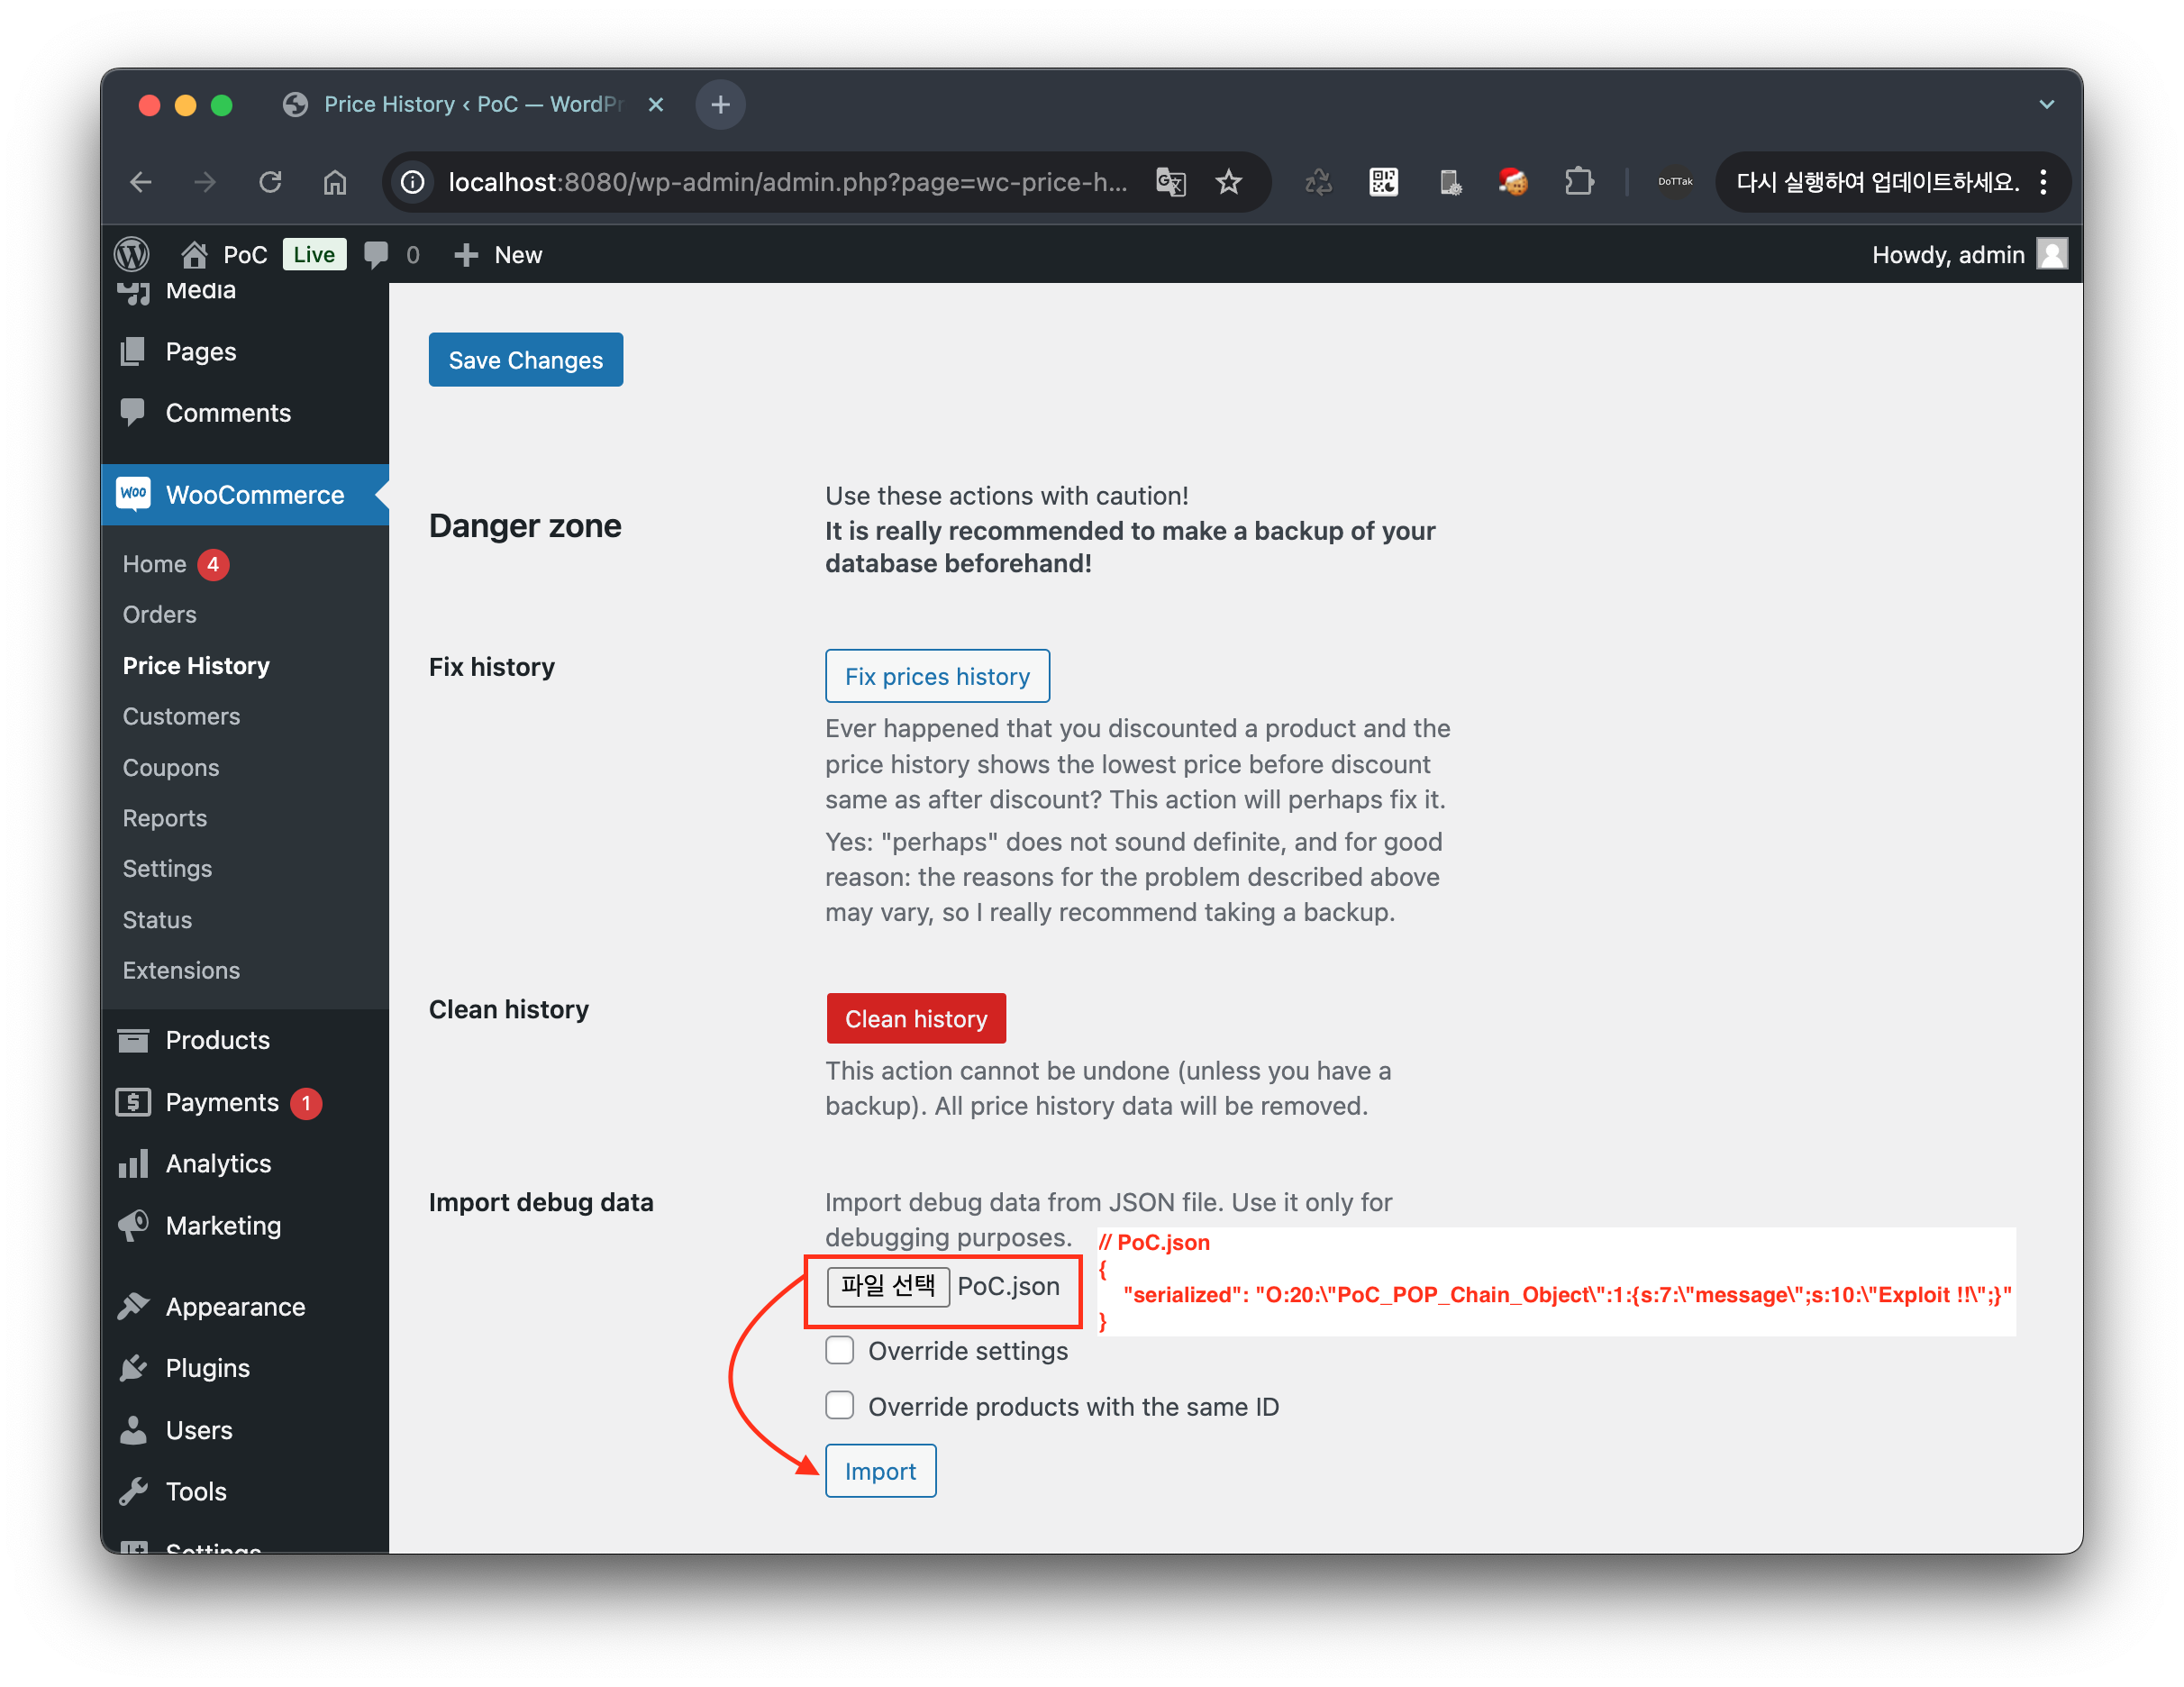 dottak/cve-2025-22510
PoC of CVE-2025-22510
 mrr0b0t19/cve-2025-55182-shellinteractive
Interactive RCE exploit for CVE-2025-55182 targeting Next.js/React Server Components deserialization vulnerability. Features automatic detection,…
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…
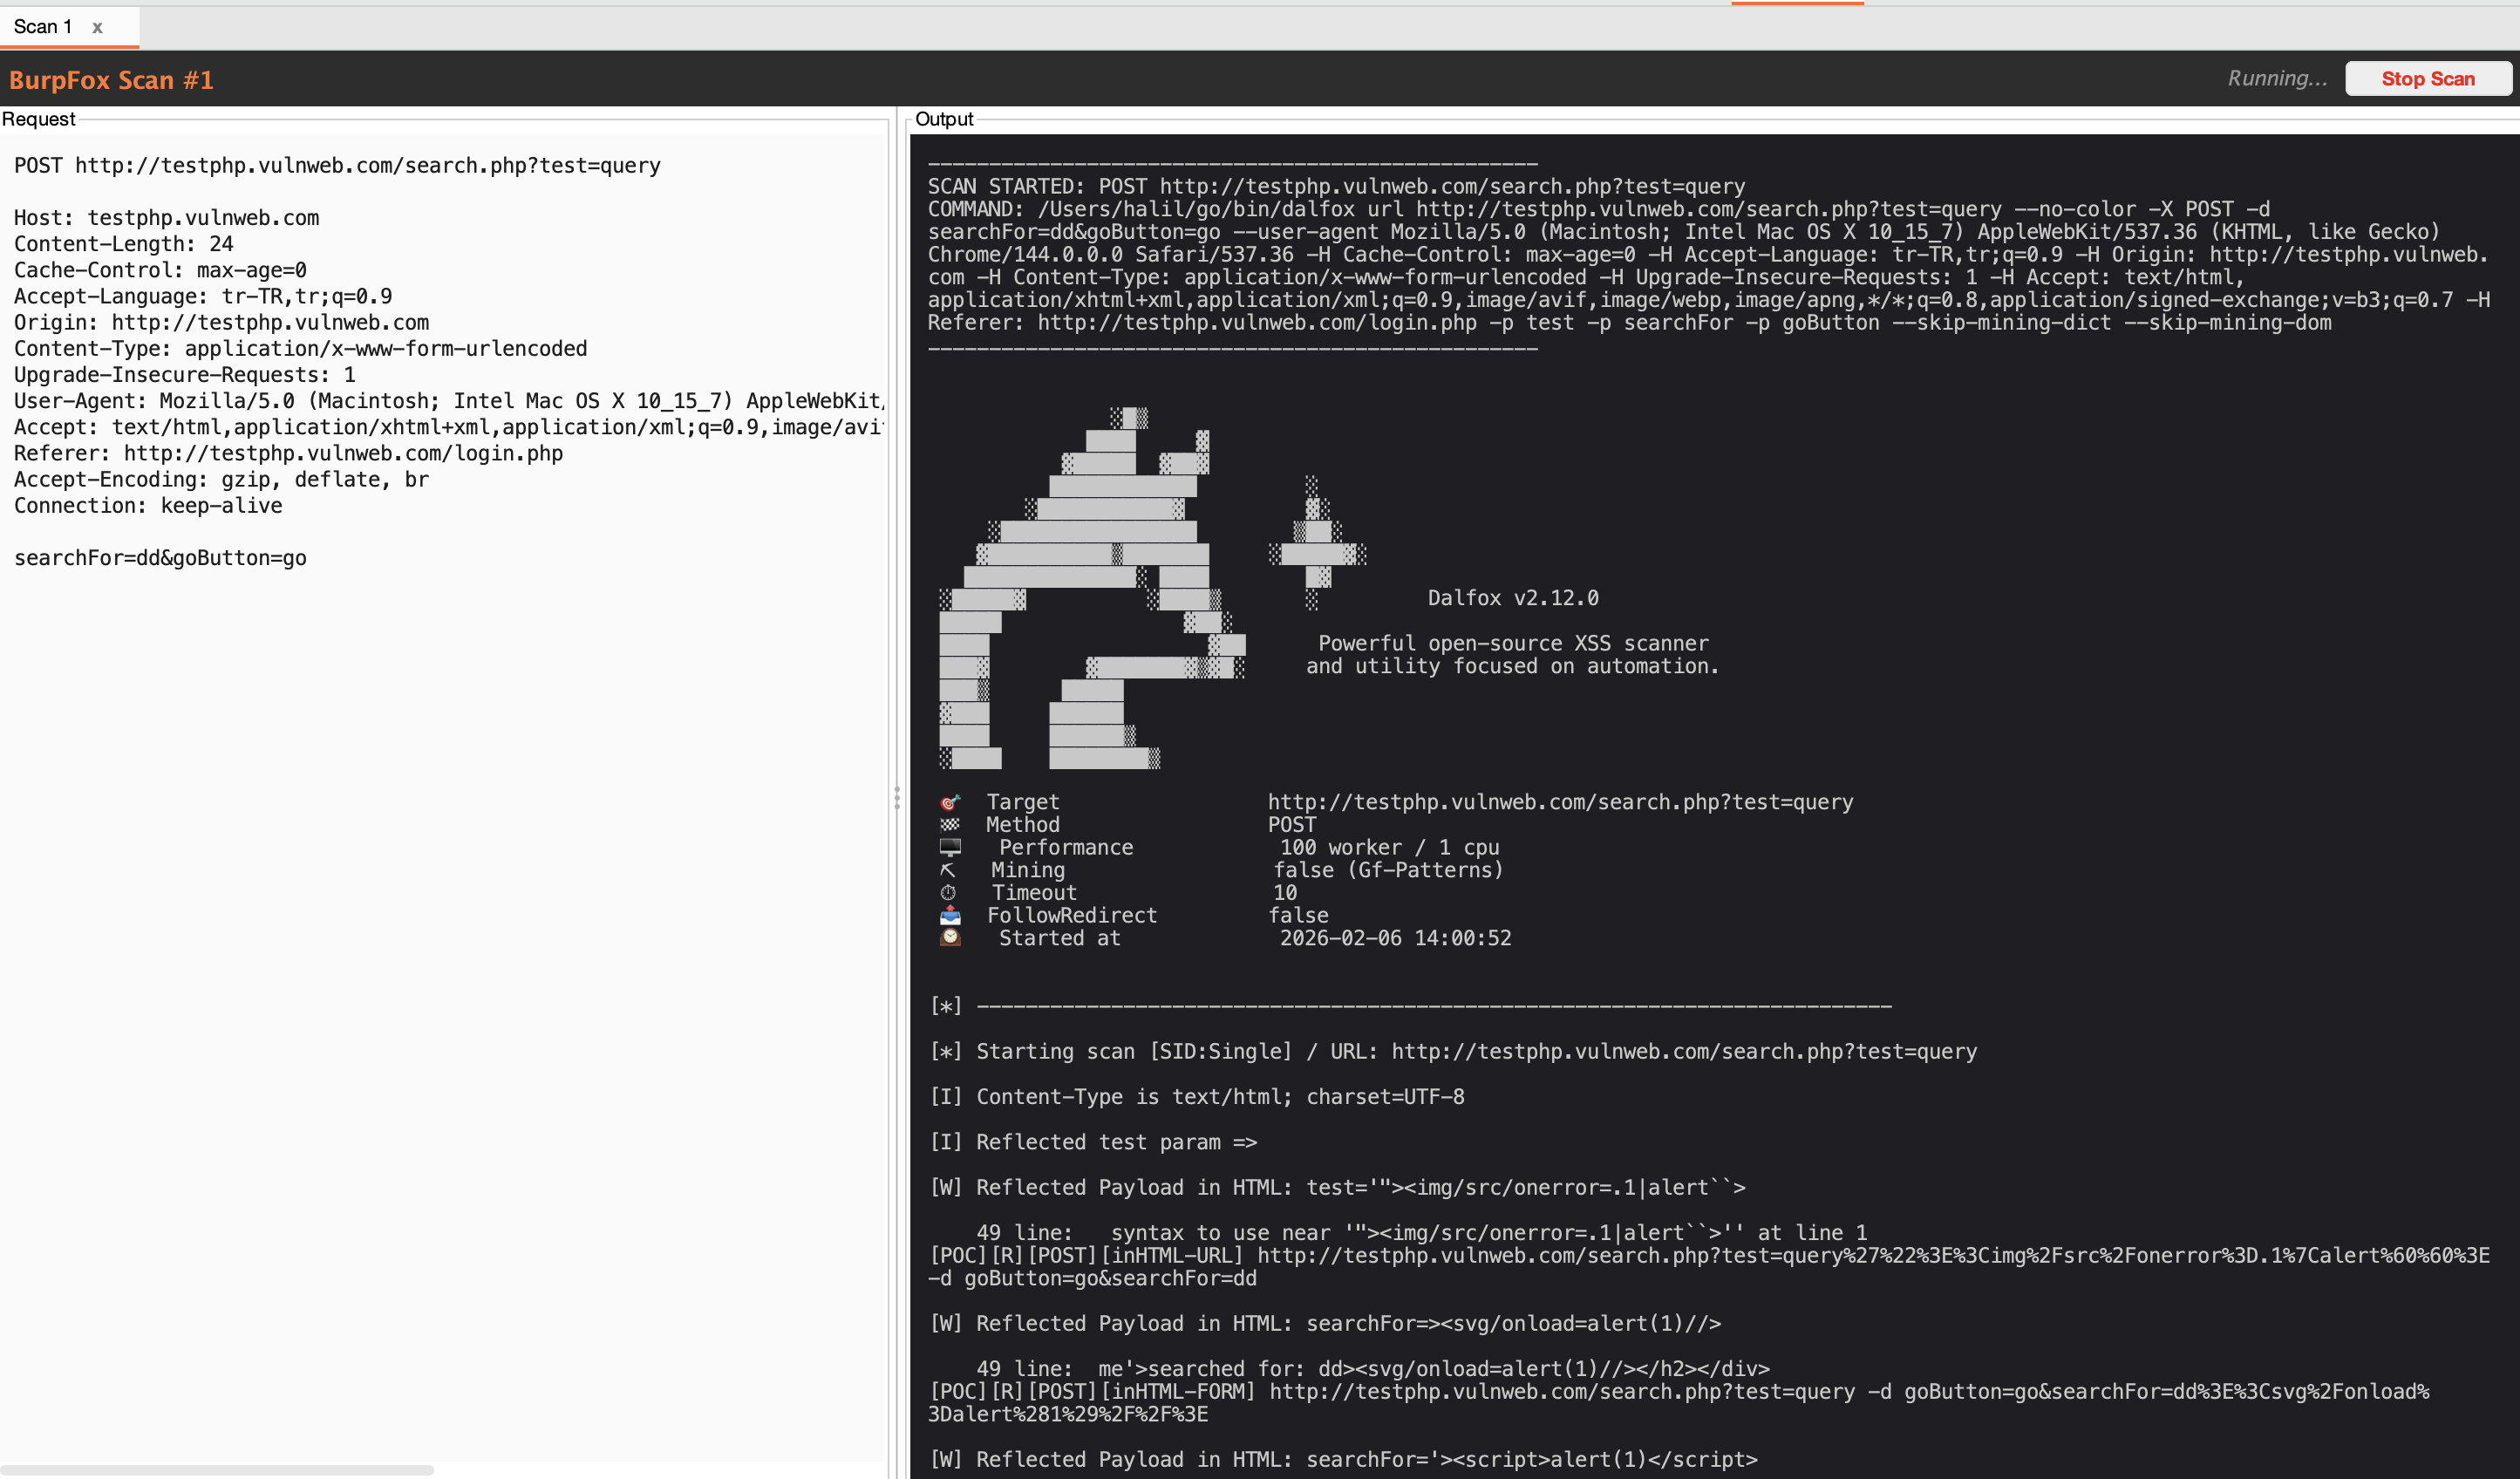 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 0xzerosec/cve-2025-55886
Advisory documenting an authenticated IDOR vulnerability in ARD's payment history API, allowing unauthorized access to other users' payment records…