
CVE-2026-20896
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
authenticationcontainer-securityexploitation+5
1
yym8538/cve-2026-20896Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 dinosn/cve-2026-23989-opencloud-lab
Reproduction lab (A/B Docker) for CVE-2026-23989 — OpenCloud / ownCloud Infinite Scale public-link scope-validation bypass in Reva
 kalilinux/build-scripts/kali-vm
Kali Linux VM images build script
 kalilinux/build-scripts/kali-arm
Kali Linux ARM build scripts https://arm.kali.org/
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 neko205-mx/cve-2025-6019_exploit
Local privilege escalation exploit for CVE-2025-6019 using crafted XFS filesystem images to gain root shell access on Linux systems.
 mirmeweu/cve-2025-22294
the task from C*****k
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 ctf-o-matic/capture-the-flag
Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…
 matejsmycka/cve-2019-14811-in-pdf-exploit
This exploit targets CVE-2019-14811 in GS environments where PostScript output is not reflected, but is executed such as PDF previews via png images.
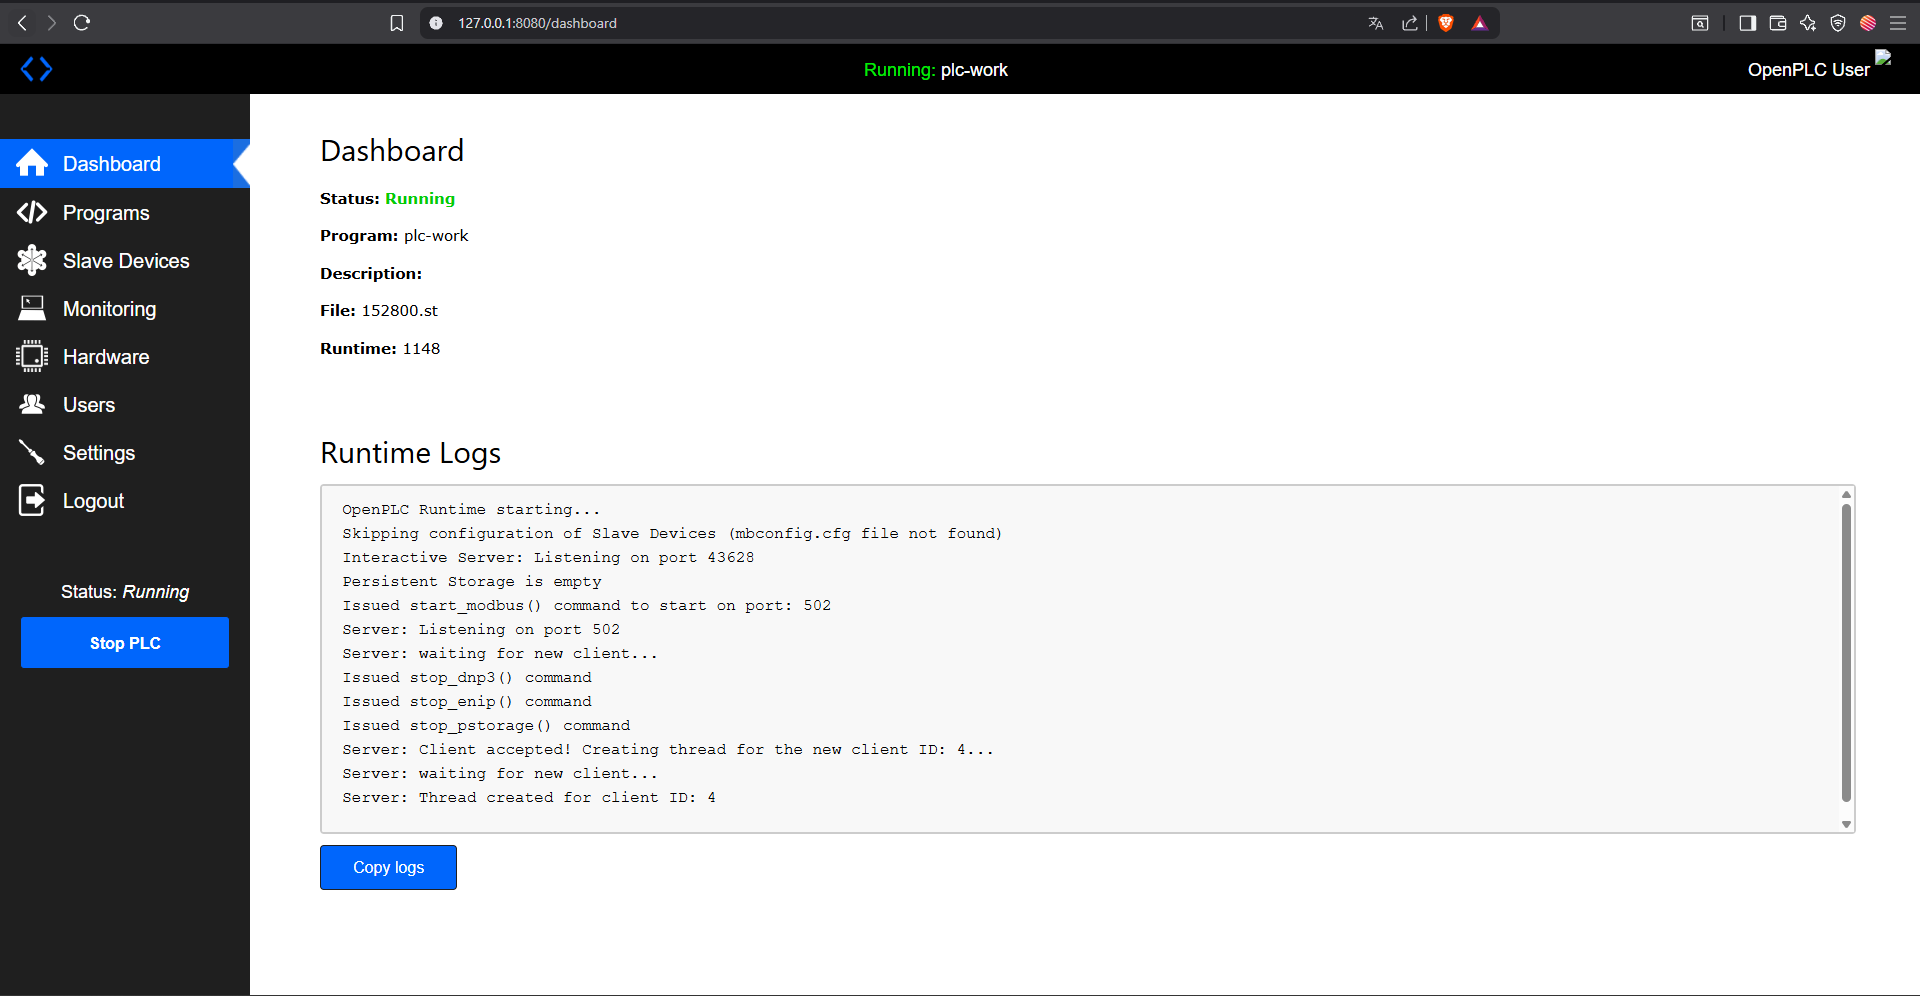 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 fa1c0n35/cve-2023-38831-winrar-exploit
Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…
 robbin0919/cve-2025-6019
Technical analysis and proof-of-concept for CVE-2025-6019, a local privilege escalation vulnerability in libblockdev and udisks2, enabling root…