IsolatedAnarchy-Public

Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…

Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…

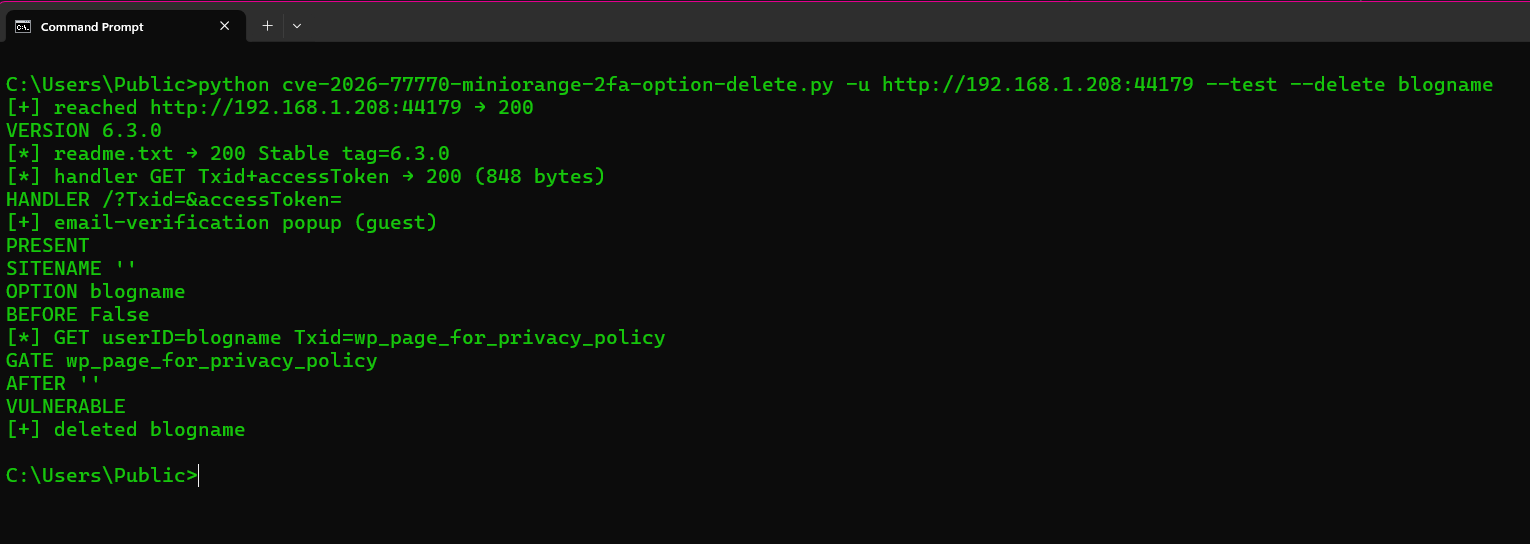
Python PoC for CVE-2026-77770, an unauthenticated arbitrary WordPress option deletion flaw in the miniOrange 2FA plugin (<= 6.3.0) via the…

This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).

Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.

Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…

Proof-of-concept exploit scripts for CVE-2026-63642 and CVE-2026-63643, SSRF vulnerabilities in MagicMirror²'s Calendar module allowing…

Python proof-of-concept exploiting CVE-2026-77578, an authenticated path traversal in Xibo CMS that reads arbitrary local files via crafted XML…

Proof-of-concept exploit for CVE-2026-13181 affecting Telerik web components, demonstrating remote code execution via crafted requests.

PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.

Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…

Proof-of-concept exploit for CVE-2026-34159, demonstrating the vulnerability and providing exploitation code for security testing and research.

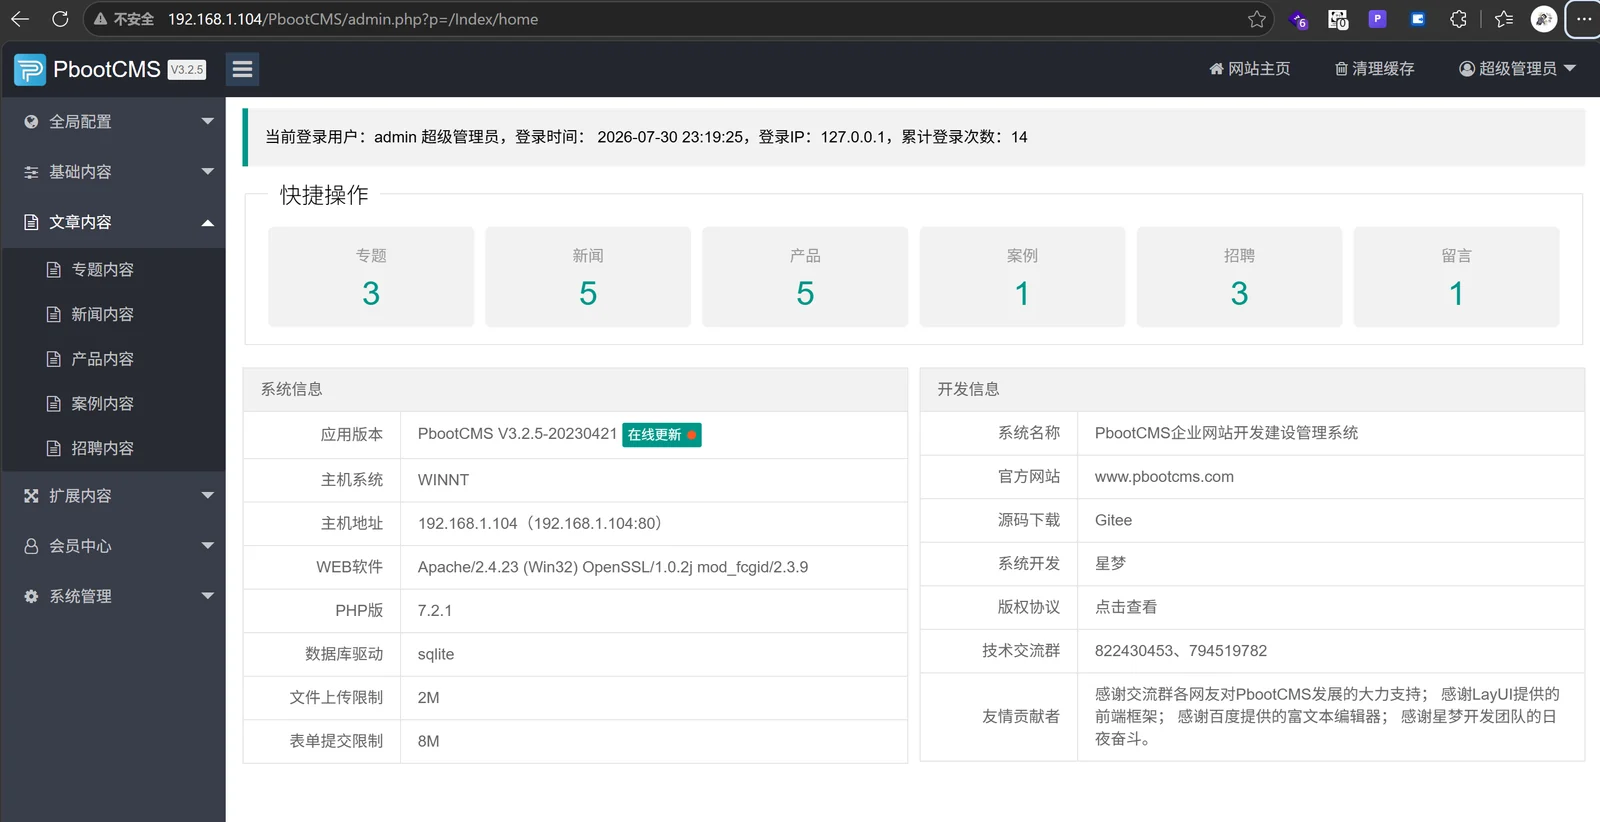
Proof-of-concept for CVE-2026-79387, an authenticated SQL injection in PbootCMS user management allowing arbitrary field updates and account takeover.

Proof-of-concept exploit code for CVE-2024-38077, a remote code execution vulnerability in Windows Remote Desktop Licensing Service. Backup copy, not…

Proof of concept and technical write-up for CVE-2026-74239, a path traversal vulnerability in XenForo style archive imports on Windows, allowing file…

Proof-of-concept for CVE-2026-52307, an authenticated stored XSS in 1CMS v5.6 Column Management, with reproduction steps and impact analysis.

WordPress plugin Welcart e-Commerce < 2.8.5 - Arbitrary File Read

Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.

Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…