thm_steelmountain_CVE-2014-6287

a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…

a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…

TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…

Subdomains analysis and generation tool. Reveal the hidden!

A write up on the THM room Vulnerability Capstone & Exploit script for CVE-2018-16763.

Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…

This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…

A write up on the TryHackMe room Source & a python script to exploit the vulnerability

Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…

A TryHackme room covering the CVE-2025-53779 exploitation using windows

This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…

Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053

Python-based exploit for Hotel Druid 3.0.3 Remote Code Execution (CVE-2022-22909). Injects PHP payloads via room names to achieve command execution…

A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

Advisory: CVE-2026-38361 multiple DoS vulnerabilities (CWE-400/CWE-670) in dash-uploader (Python/PyPI)

CVE-2017-0144 (Eternal Blue) | CVE-2023-3881 | CVE-2011-2523

Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…

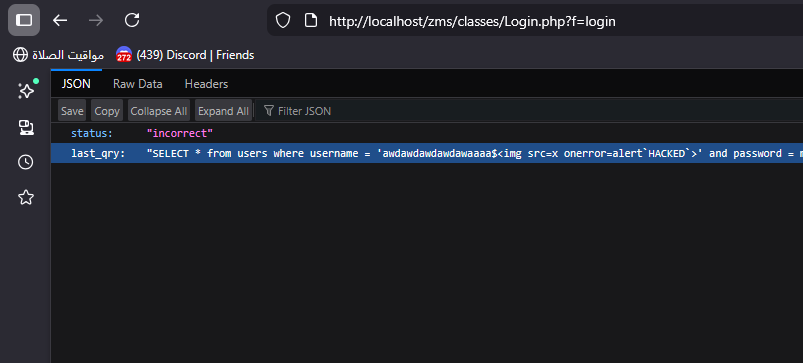
Sourcecodester Zoo Management System v1.0 is vulnerable to Cross Site Scripting (XSS) in /classes/Login.php Due to invalid Content-Type