Phantom-Evasion-Loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

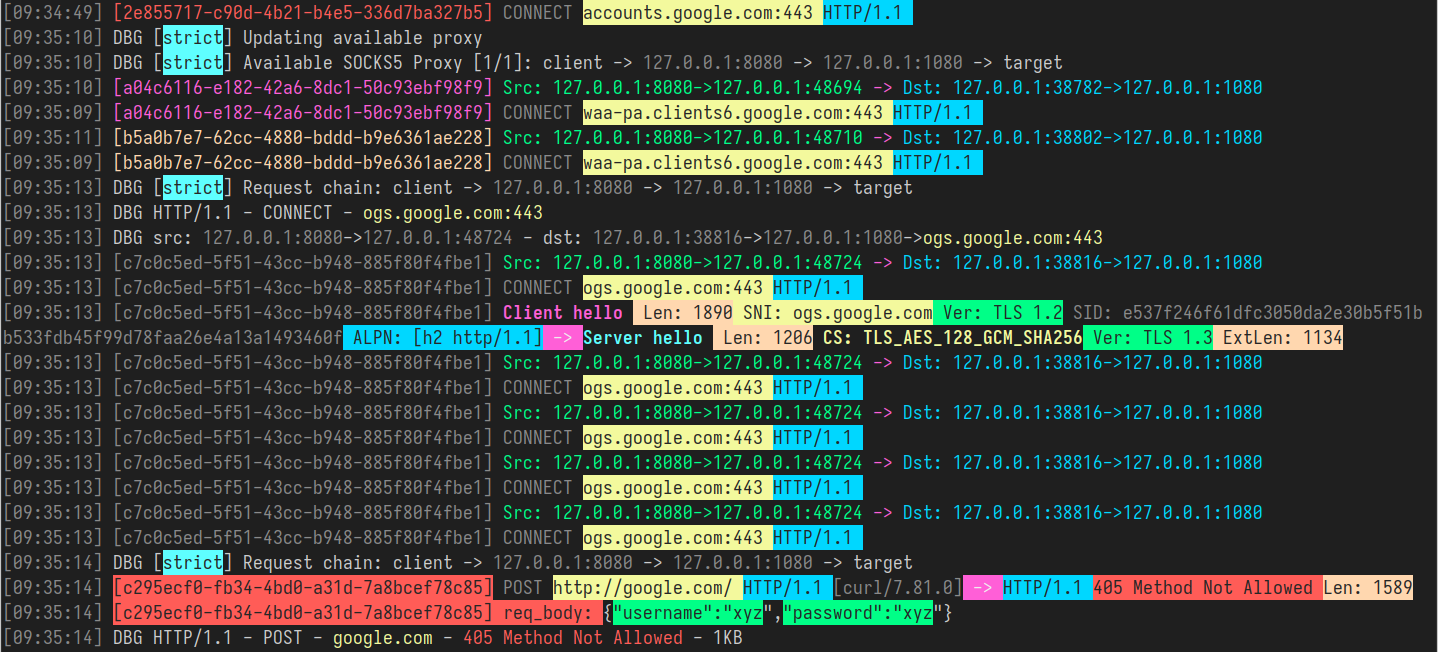
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…

Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)

a fast password wordlist generator, Smartlist creation and password hybrid-mask analysis tool written in pure safe Rust

global rate-limiting in Linux (CVE-2016-5696) scanner

pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory

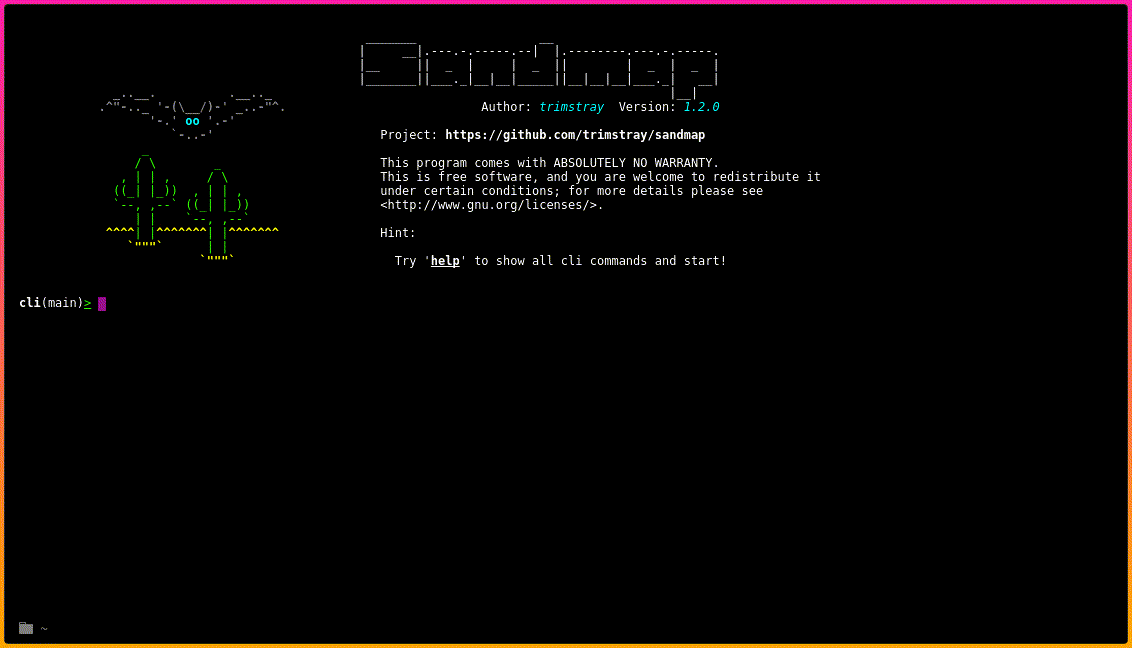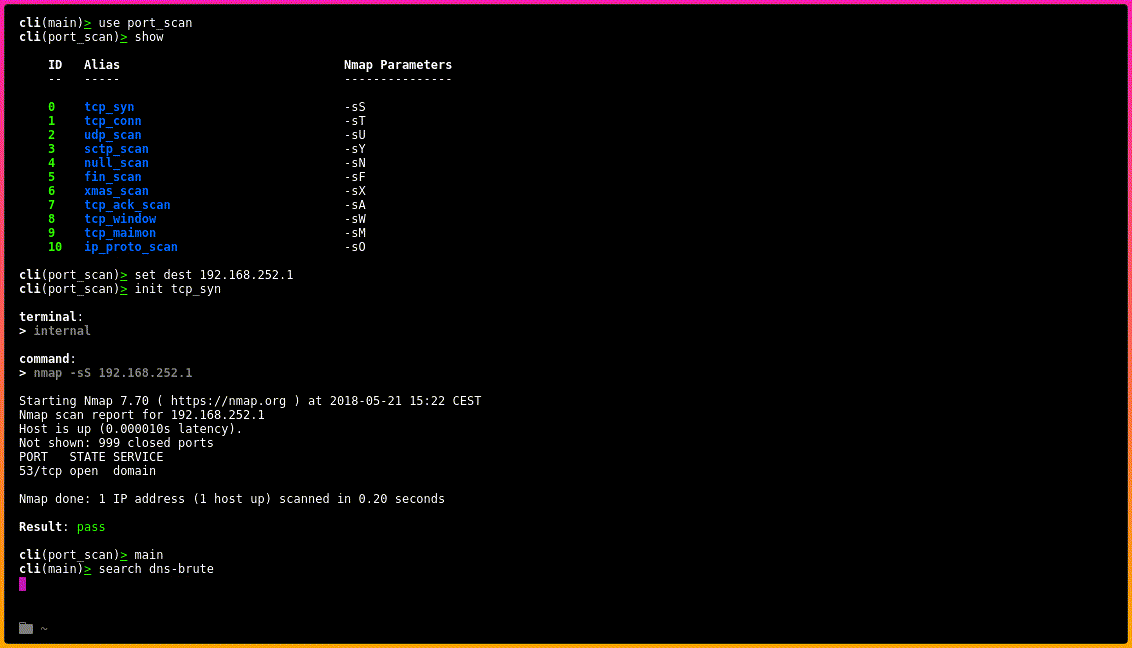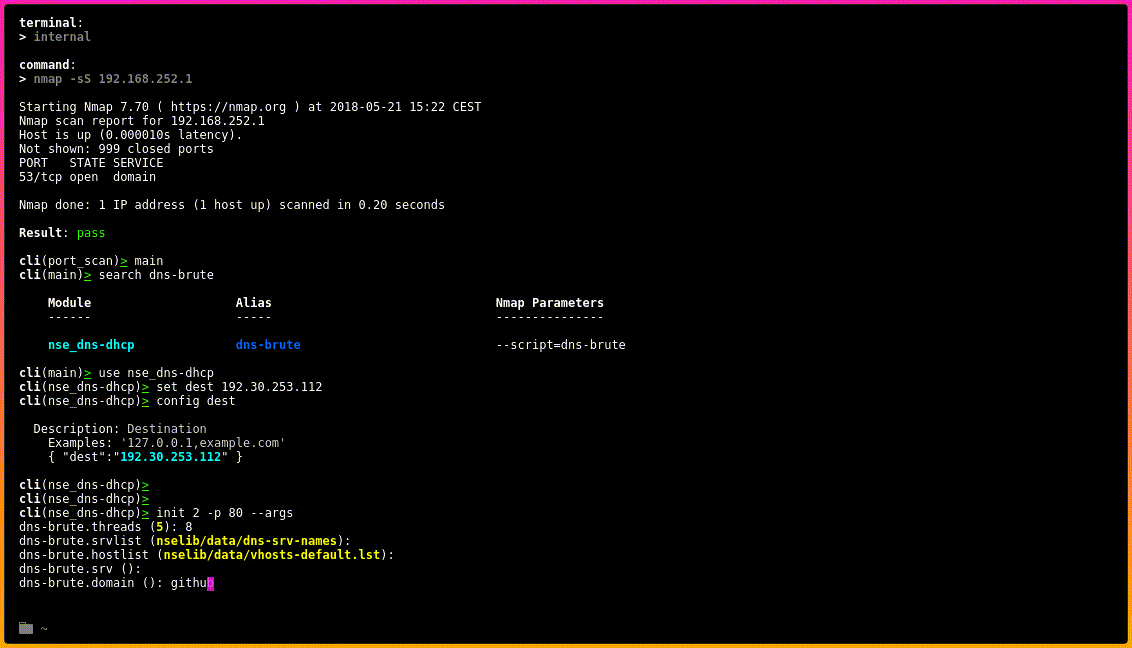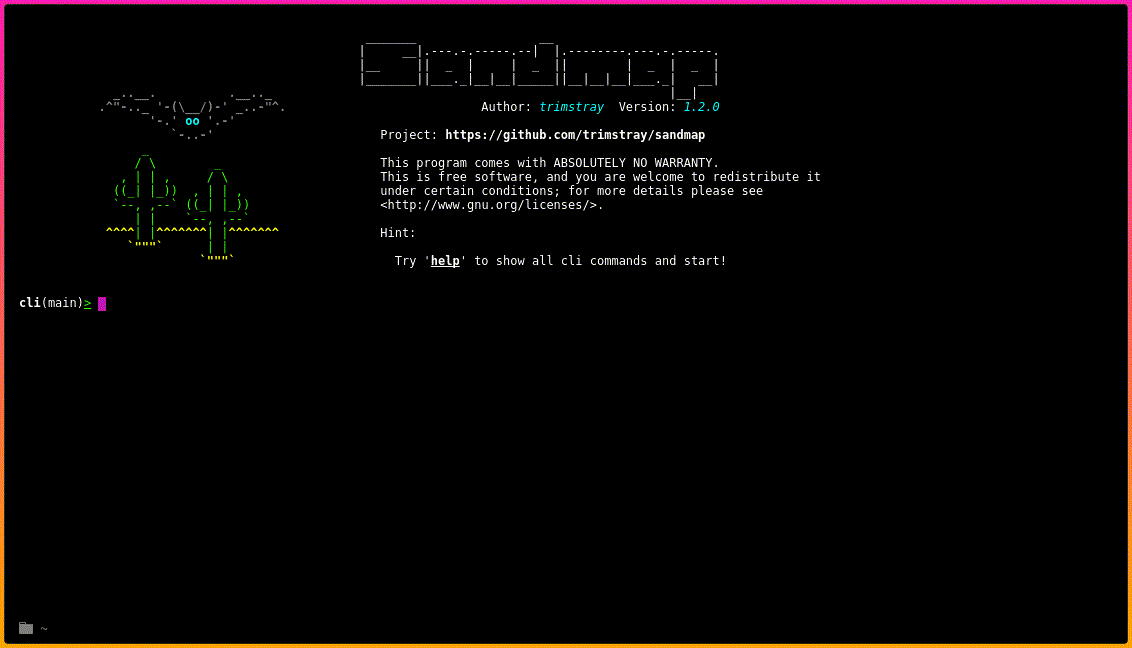
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.

Mimikatz implementation in pure Python

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…

Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…

Remote Desktop Protocol in Twisted Python

HTTP/2 attack simulation & defense lab - Slowloris, Rapid Reset (CVE-2023-44487), HPACK Bomb attacks with 5 layered defenses. Built in pure Python…

A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.

Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.

Pure PowerShell implementation of CVE-2021-1675 Print Spooler Local Privilege Escalation (PrintNightmare)

Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…

Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc