
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
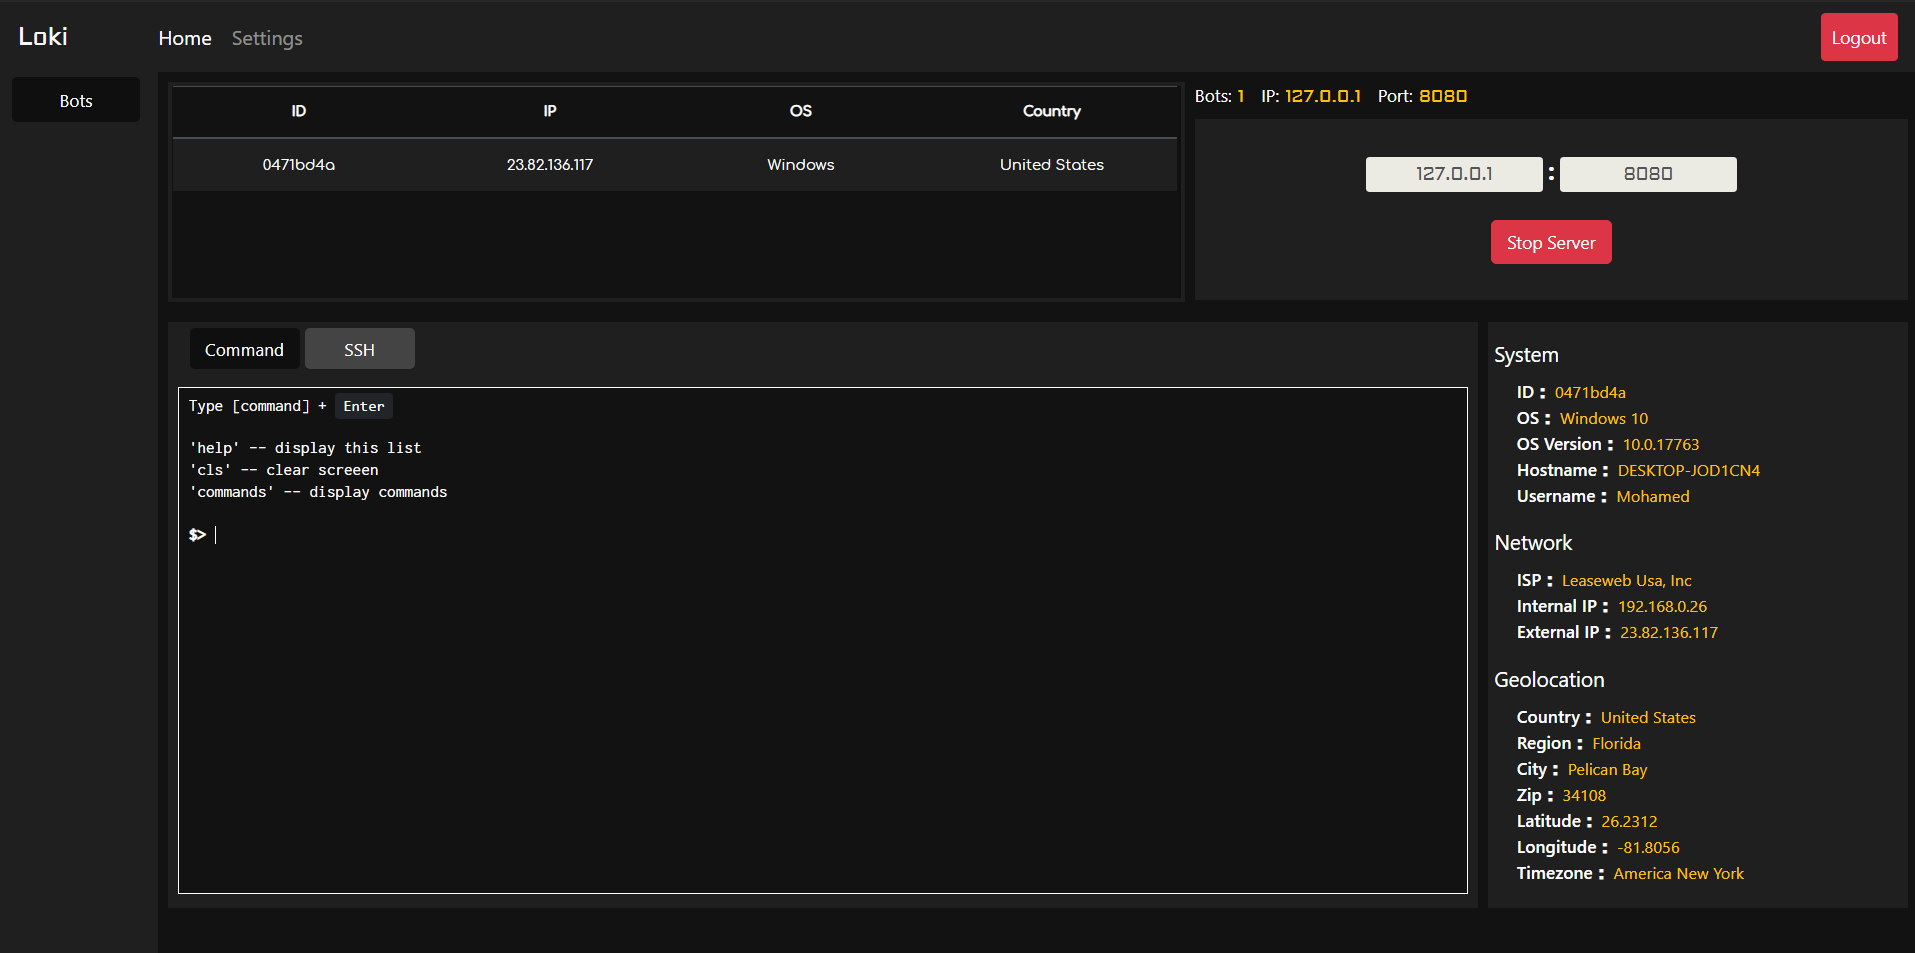
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 sh4den/cve-2022-29464
A bots loader for CVE-2022-29464 with multithreading
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 sweetsoftware/ares
Python botnet and backdoor
 sh1n0g1/shinobot
RAT / Botnet Simulator for pentest / education
 jeffbezosispogg/cve-2021-4045
TP-Link Tapo c200 ver <1.1.15 - Remote Code Execution (RCE)