

CVE-2017-0199
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
exploitationexploit-frameworkspayload-generation+3
2
n1shant-sinha/cve-2017-0199Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
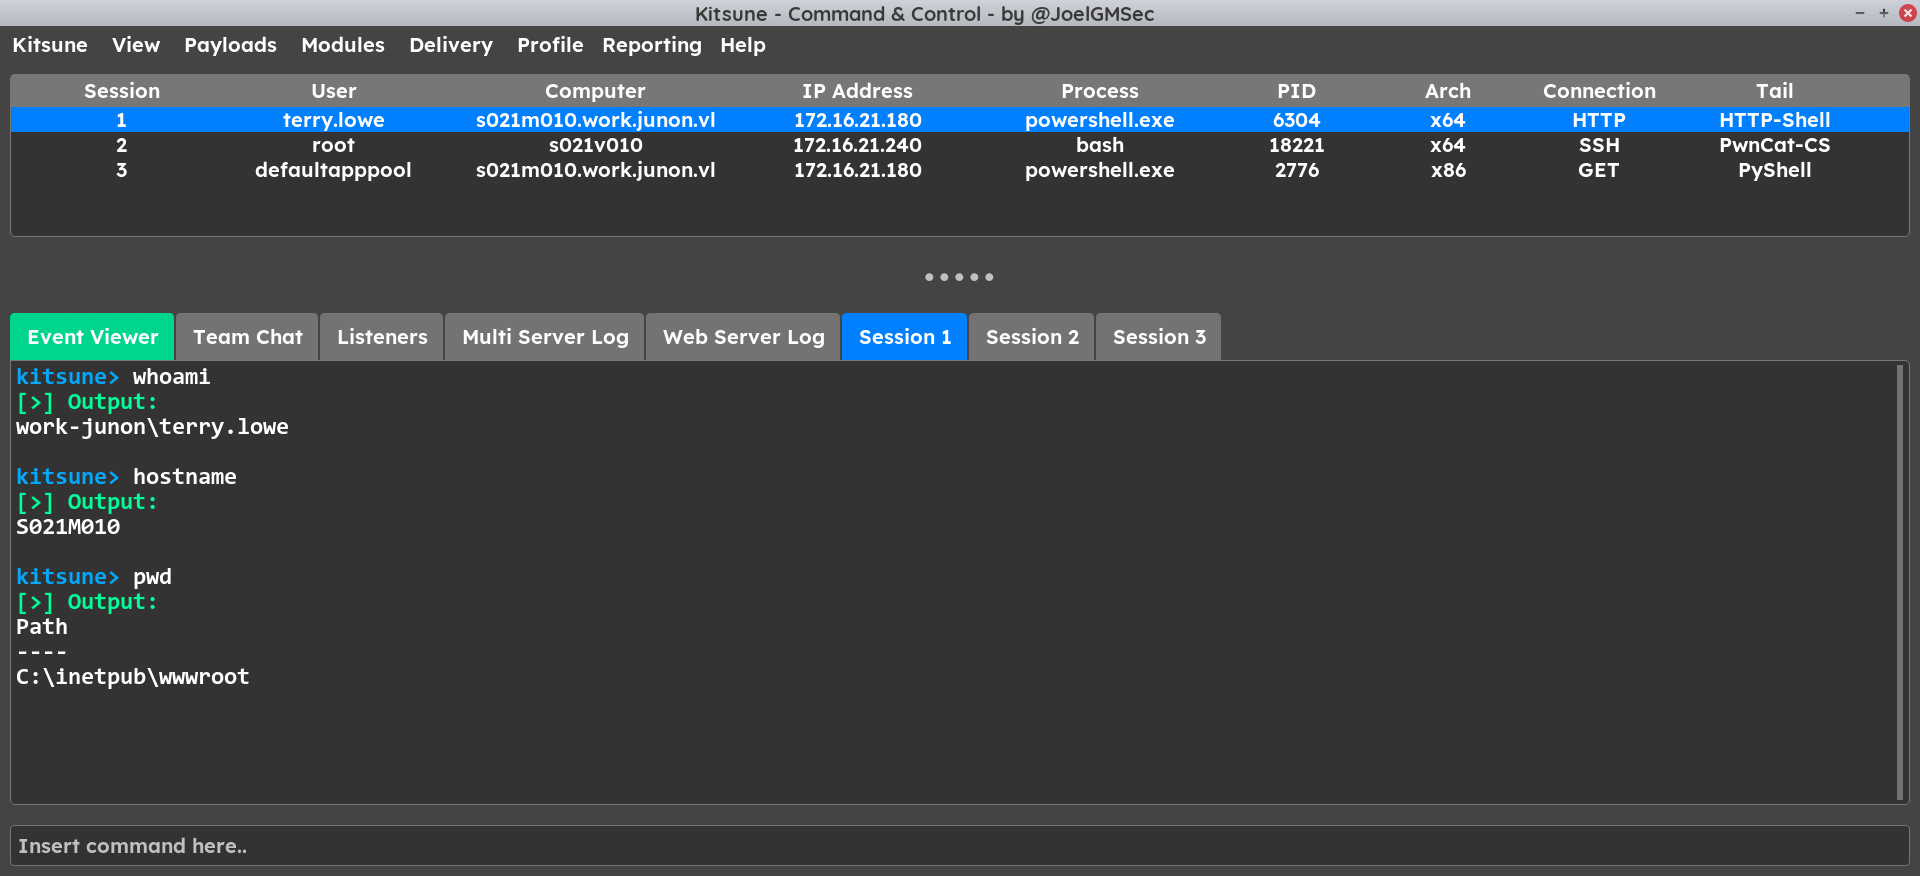 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 kimd155/quickresponsec2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…
 jpeanut/imagetragick-cve-2016-3714-rshell
Proof-of-concept exploit scripts for CVE-2016-3714 (ImageTragick) using MVG/SVG files to deliver reverse shells via bash, nc, and PHP for ethical…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 subc0ol/apache-struts2-rce-exploit-v2-cve-2017-5638
Automated remote code execution exploit for Apache Struts2 (CVE-2017-5638) with auto-exploitation capabilities for penetration testing and…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 shishirghimir/cve-2024-53677-exploit
Automated Python exploit script for CVE-2024-53677 with JSP web payload delivery, enabling targeted vulnerability exploitation and penetration…
 peewpw/exploithosting
Host-based exploitation utility for penetration testing and red team operations, enabling payload delivery and post-exploitation actions on target…
 phamchie/cve-2022-4611
Python exploit script for CVE-2022-4611, providing targeted vulnerability exploitation for penetration testing and security assessment purposes.
 elm0d/cve-2017-8464
Proof-of-concept exploit for CVE-2017-8464 targeting USB drives with automatic payload execution. Supports x86 and x64 architectures for penetration…
 damit5/cve-2020-11546
Go-based proof-of-concept exploit for CVE-2020-11546, targeting a remote code execution vulnerability in SuperWebMailer 5.50. Provides a ready-to-use…