
ezXSS
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
information-gatheringpayload-generationpenetration-testing+2
2.3k
ssl/ezxssBlind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 nullarray/roothelper
A Bash script that downloads and unzips scripts that will aid with privilege escalation on a Linux system.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 redtimmy/enumjavalibs
Remote Java classpath enumeration via deserialization
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
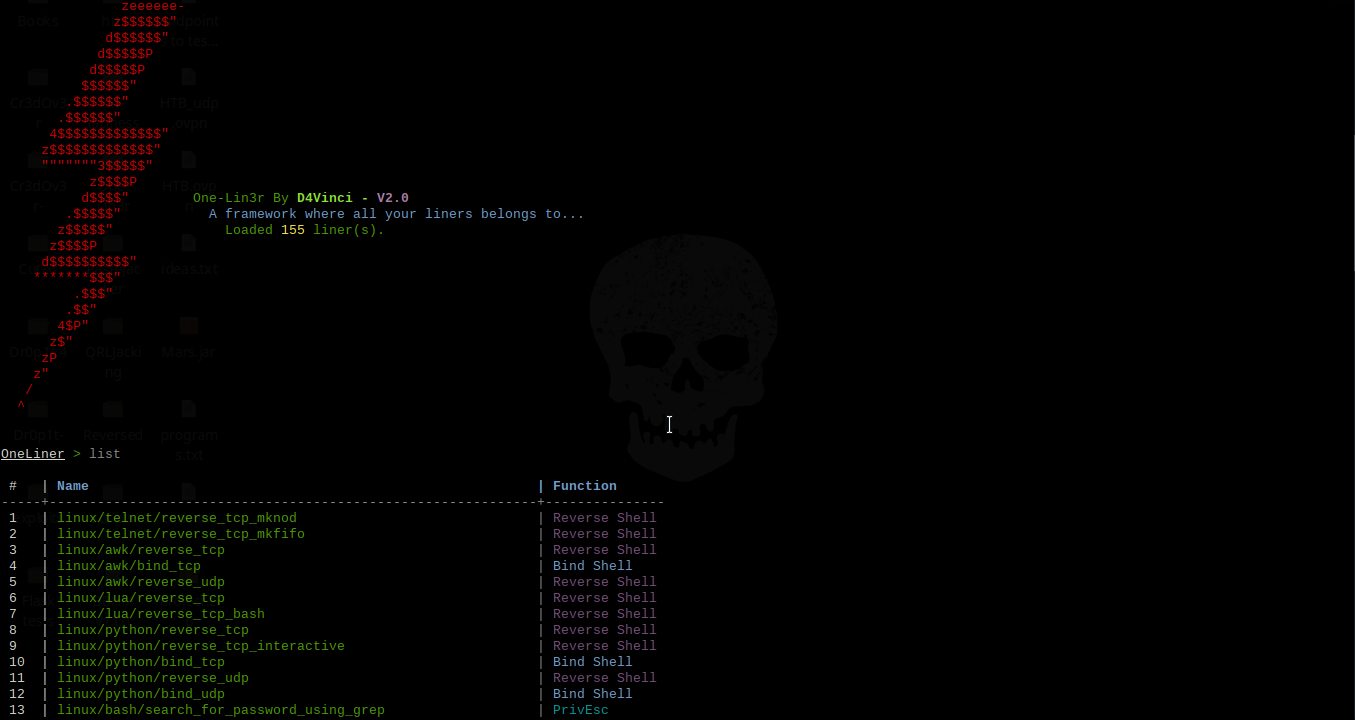 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 harleyqu1nn/aggressorscripts
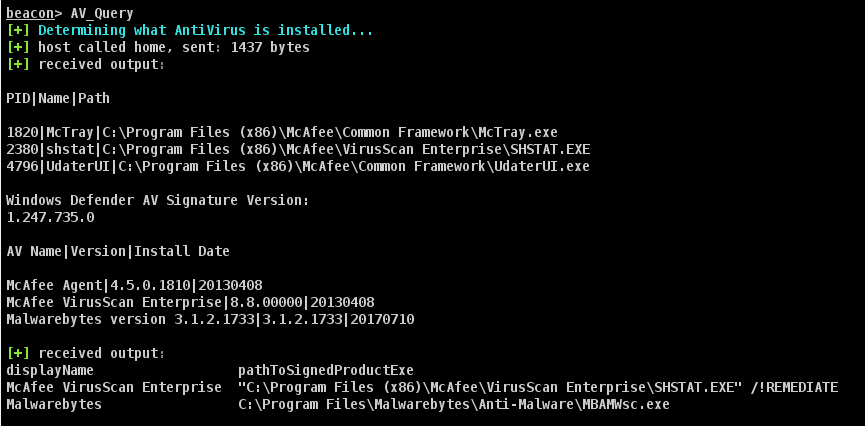
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 wireghoul/htshells
Self contained htaccess shells and attacks
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 samdenty/injectify
Perform advanced MiTM attacks on websites with ease 💉