
MacroShop
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
payload-developmentpayload-generationpenetration-testing+2
408
khr0x40sh/macroshopCollection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
 securityward/mousejack
All the details and steps needed to perform tactical mousejacking using Autojack
 aelmokhtar/cve-2024-34716
Proof-of-concept exploit for CVE-2024-34716, a PNG-driven XSS to RCE chain in PrestaShop 8.1.5, enabling remote code execution via crafted image…
 atiilla/sqlmap-ai
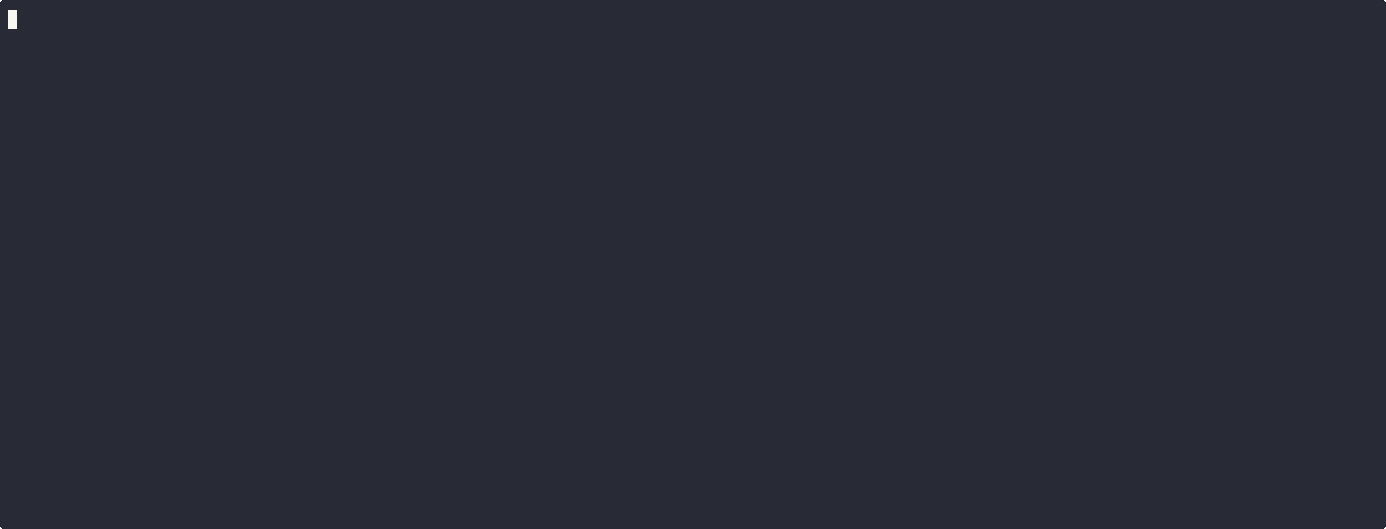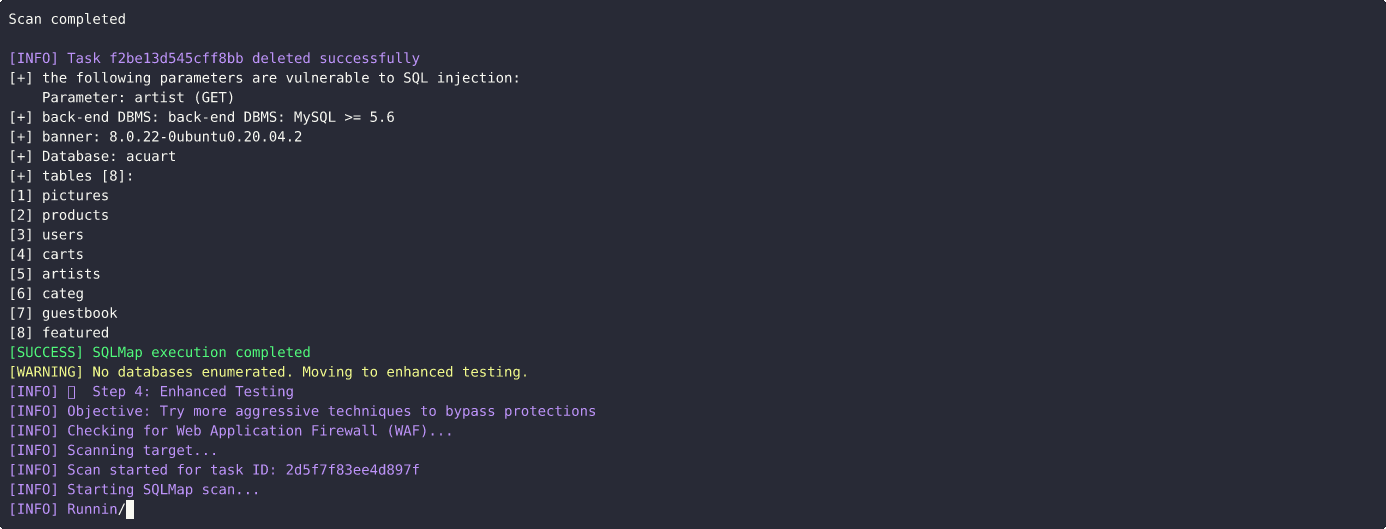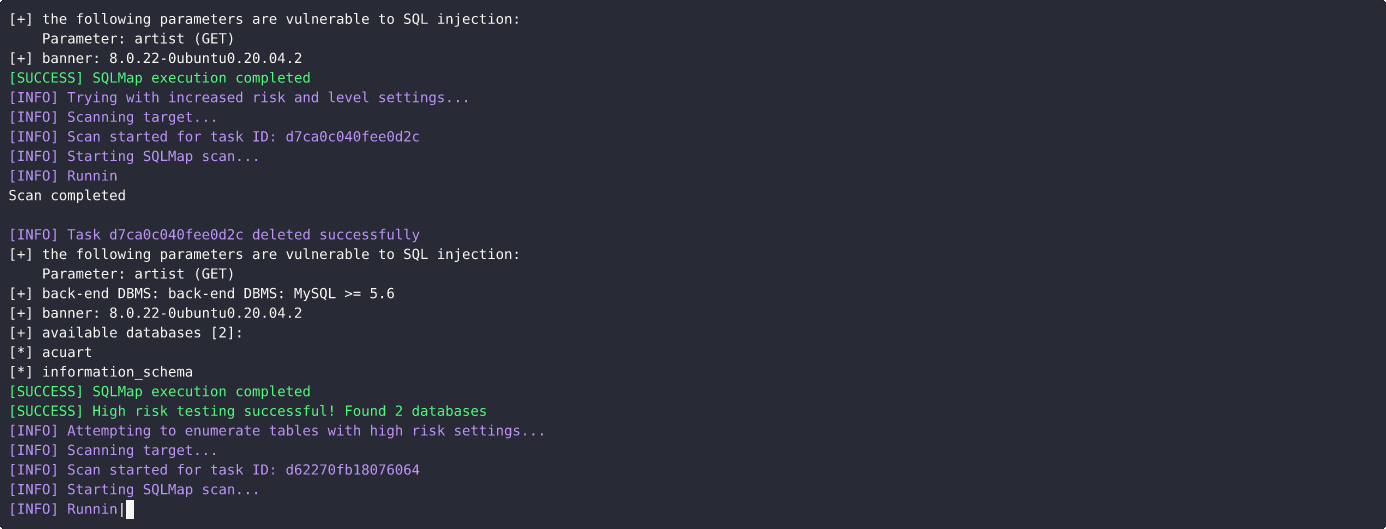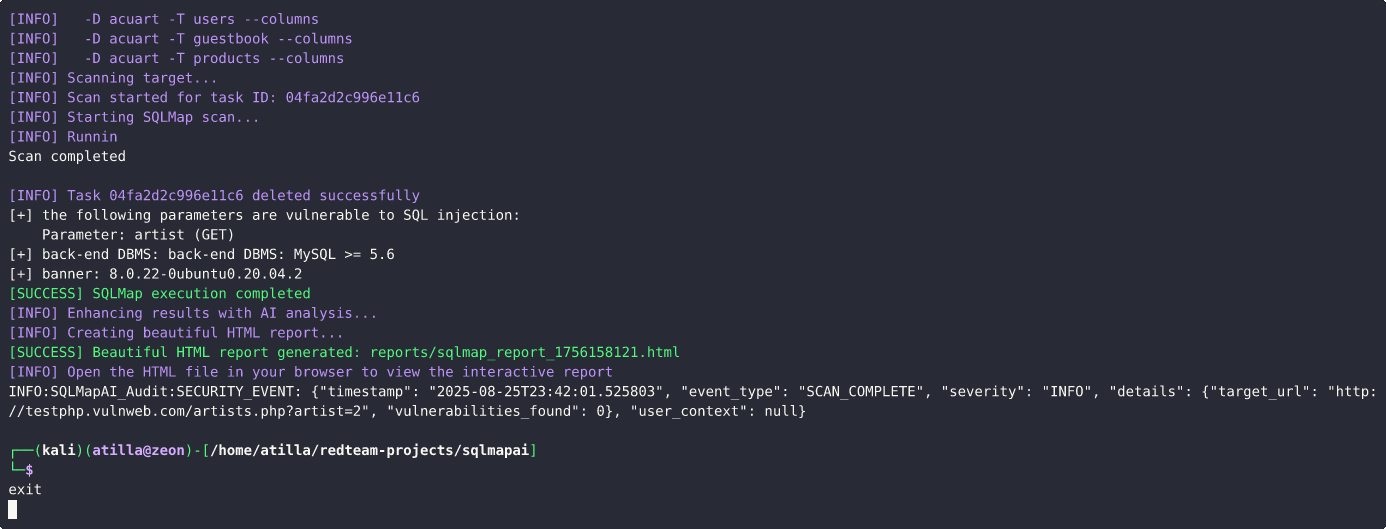
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 nevasec/cve-2022-46485
An issue in Data Illusion Survey Software Solutions NGSurvey v2.4.28 and below allows attackers to cause a Denial of Service (DoS) via a crafted…
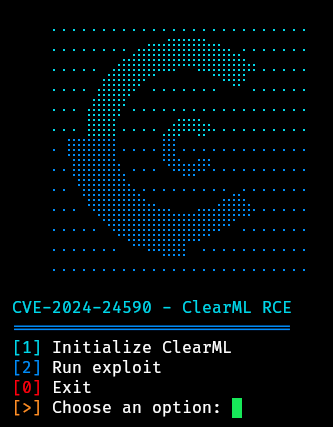 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 xooxo/cve-2019-14745
weaponized radare2 vulnerability found by @CaptnBanana and blenk92
 ambionics/prestashop-exploits
Collection of exploits/POC for PrestaShop cookie vulnerabilities (CVE-2018-13784)
 billskico/cve-2023-23397_exploit
Generates meeting requests taking advantage of CVE-2023-23397. This requires the outlook thick client to send.
 davids52/cve-2021-29447_auto-script
This repo describes about cve-2021-29447 and a small script for exploiting automatically
 watchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257
Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…
 watchtowrlabs/watchtowr-vs-oracle-e-business-suite-cve-2025-61882
Generates detection artifacts for Oracle E-Business Suite CVE-2025-61882 by serving a reverse shell payload to verify pre-auth RCE.
 wytchwulf/cve-2015-1397-magento-shoplift
Exploit scripts for CVE-2015-1397 in Magento CMS, including a pre-auth exploit to gain admin credentials and a post-auth RCE module for reverse shell…
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 wguest/craftcms-vcard-exploit
This repository has details on a vulnerability found with the "vCard" plugin for CraftCMS 3.
 walidpyh/cve-2025-8088
Proof-of-concept demonstrating Alternate Data Stream (ADS) payload delivery via crafted WinRAR archives for educational research and controlled lab…
 mandiant/heyserial
Programmatically create hunting rules for deserialization exploitation with multiple keywords, gadget chains, object types, encodings, and rule types
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228