
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
cerebro-red-v2 preview

cerebro-red-v2

GitHubleviticus-triage/cerebro-red-v2

CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation

adversarial-attackai-securitydynamic-analysis-sandboxing+8
16
6 months ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
21816 days ago
goshs preview

goshs

GitHubgoshs-labs/goshs

Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

command-and-controlctfdns-analysis+5
9843 days ago
Forblaze preview

Forblaze

GitHubasaurusrex/forblaze

Forblaze - A Python Mac Steganography Payload Generator
exploitationpayload-generationpenetration-testing+2
564 years ago
SynthAPT preview

SynthAPT

GitHubacedef/synthapt

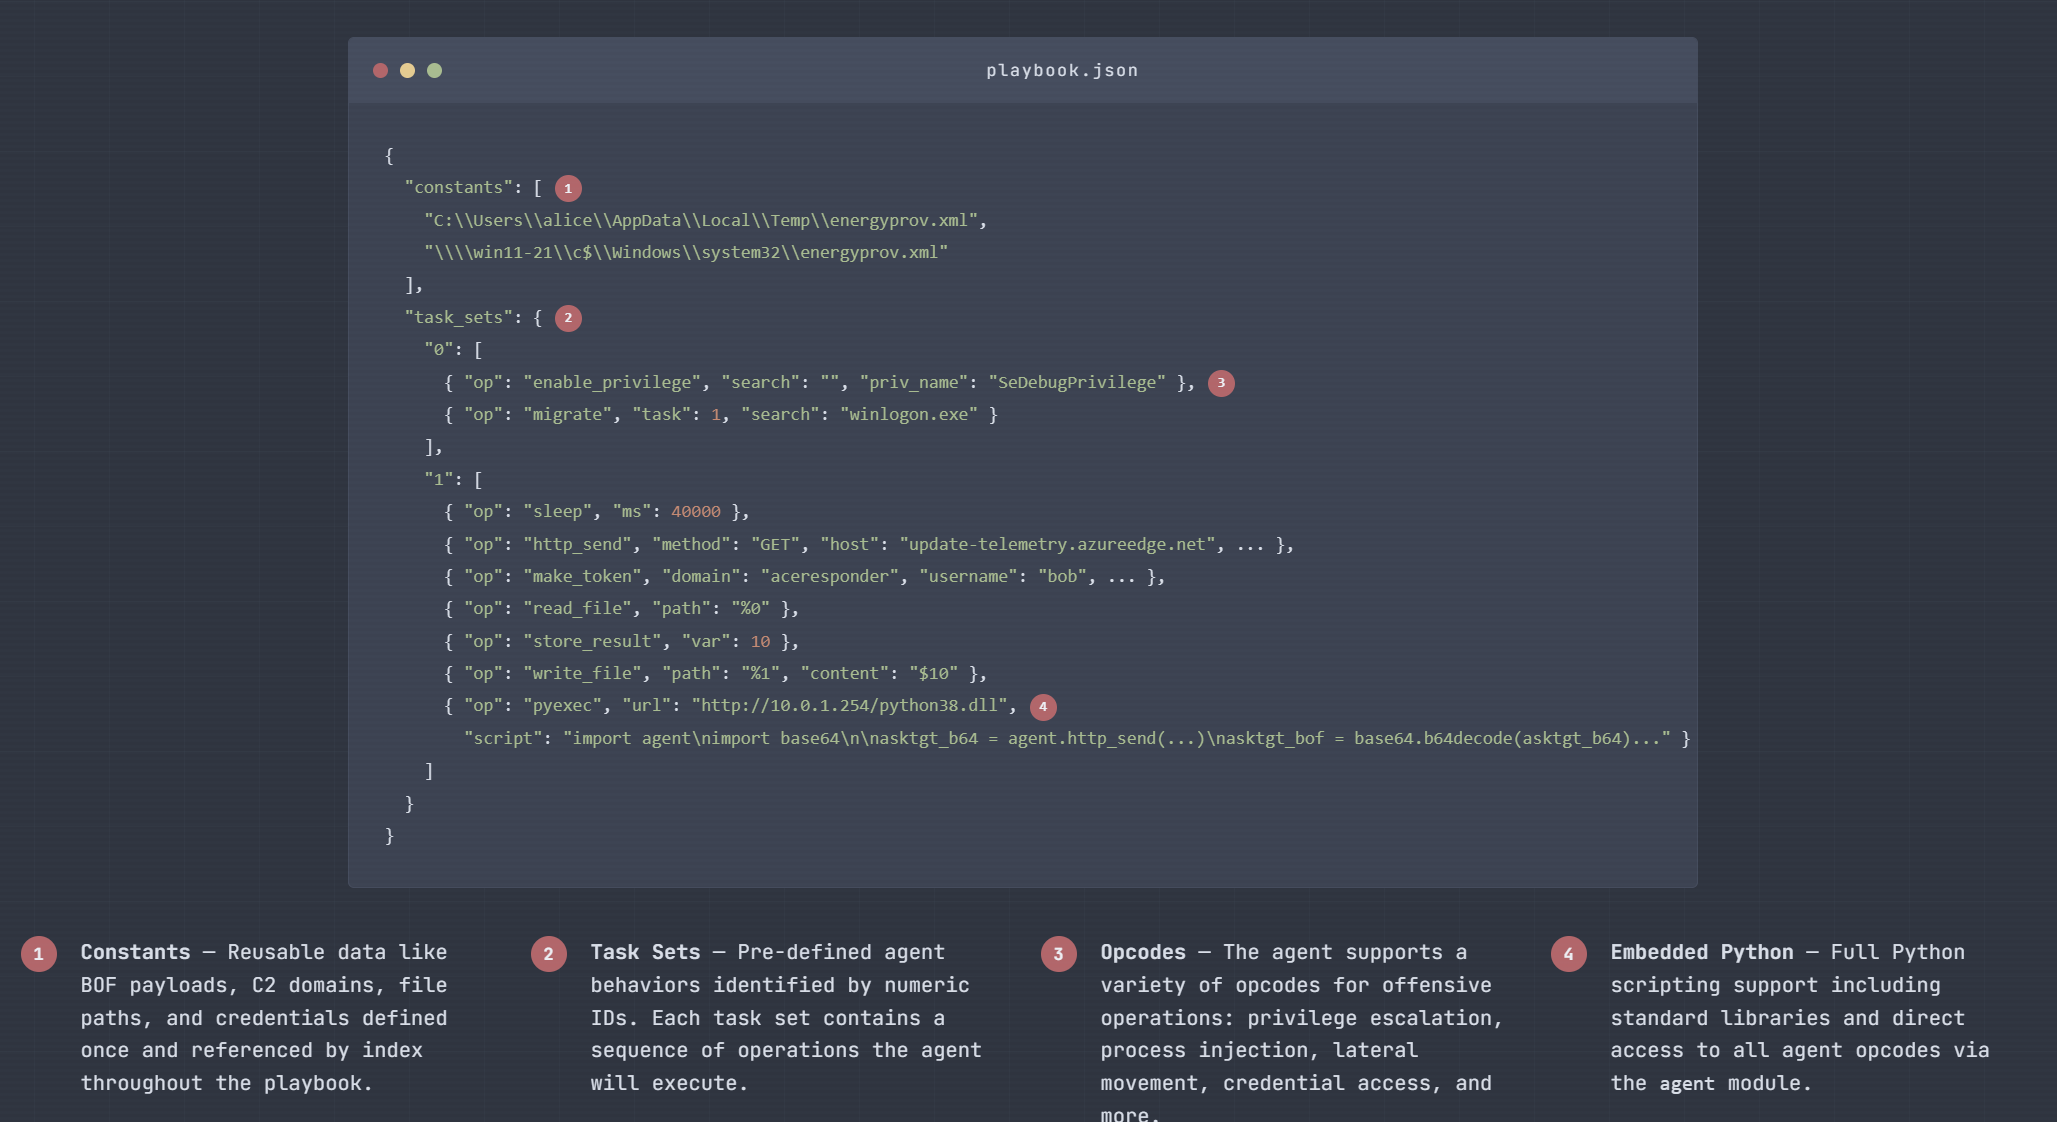
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…

adversarial-attackai-securitycommand-and-control+8
2355 months ago
arducky preview

arducky

GitLabcreased/arducky

Arducky - Arduino Ducky Script Interpreter
hardware-hackingpayload-generationpenetration-testing+2
18 years ago
endgame preview

endgame

GitHubendgamec2framework/endgame

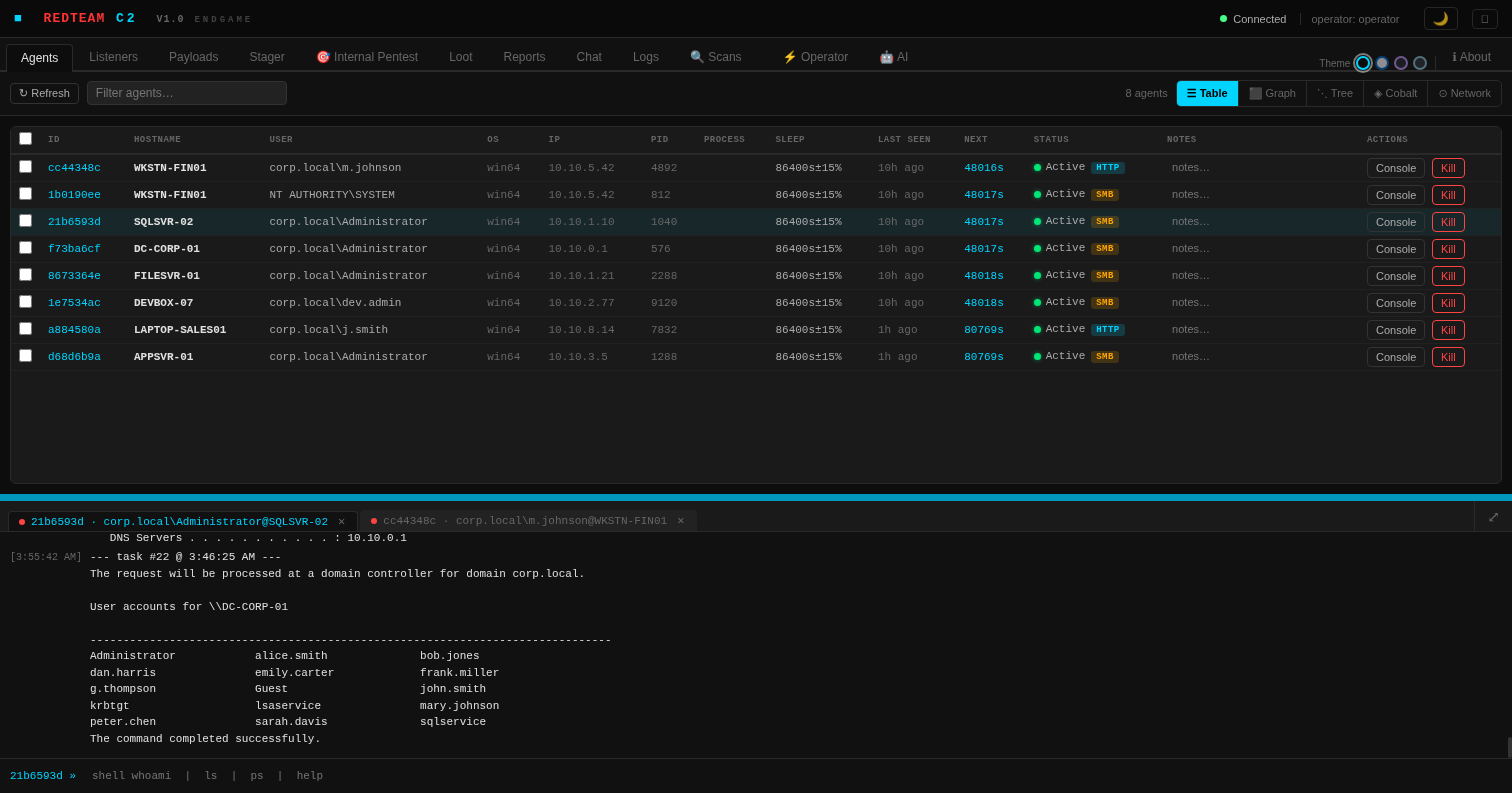
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
ai-securitycommand-and-controleducation+8
354 days ago
PISmith preview

PISmith

GitHubalbert-y1n/pismith

PISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses

adversarial-attackai-securitymachine-learning+3
312 months ago
Gideon preview

Gideon

GitHubcogensec/gideon

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

ai-securitycommand-and-controleducation+9
343 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k19 days ago
nishang preview

nishang

GitHubsamratashok/nishang

Nishang - Offensive PowerShell for red team, penetration testing and offensive security.

command-and-controldata-exfiltrationexploitation+9
10.1k3 years ago
SocialFish preview

SocialFish

GitHubundeadsec/socialfish

Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…

command-and-controleducationids-ips-evasion+9
4.9k4 months ago
malicious-pdf preview

malicious-pdf

GitHubjonaslejon/malicious-pdf

Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…

data-exfiltrationeducationexploitation+6
4.4k1 month ago
Covenant preview

Covenant

GitHubcobbr/covenant

Covenant is a collaborative .NET C2 framework for red teamers.
command-and-controlexploit-frameworkspayload-generation+2
4.7k5 years ago
Bashfuscator preview

Bashfuscator

GitHubbashfuscator/bashfuscator

A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
defensive-toolseducationids-ips-evasion+3
2.0k6 years ago
PowerSharpPack preview

PowerSharpPack

GitHubs3cur3th1ssh1t/powersharppack

PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
exploit-frameworksinformation-gatheringlateral-movement+5
1.7k1 year ago
PoshC2 preview

PoshC2

GitHubnettitude/poshc2

A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
command-and-controllateral-movementpayload-generation+3
2.1k1 year ago
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
Previous12345Next