
backdoor-apk
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
android-securityeducationexploit-frameworks+2
2.4k
dana-at-cp/backdoor-apkbackdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 tylous/sourcepoint
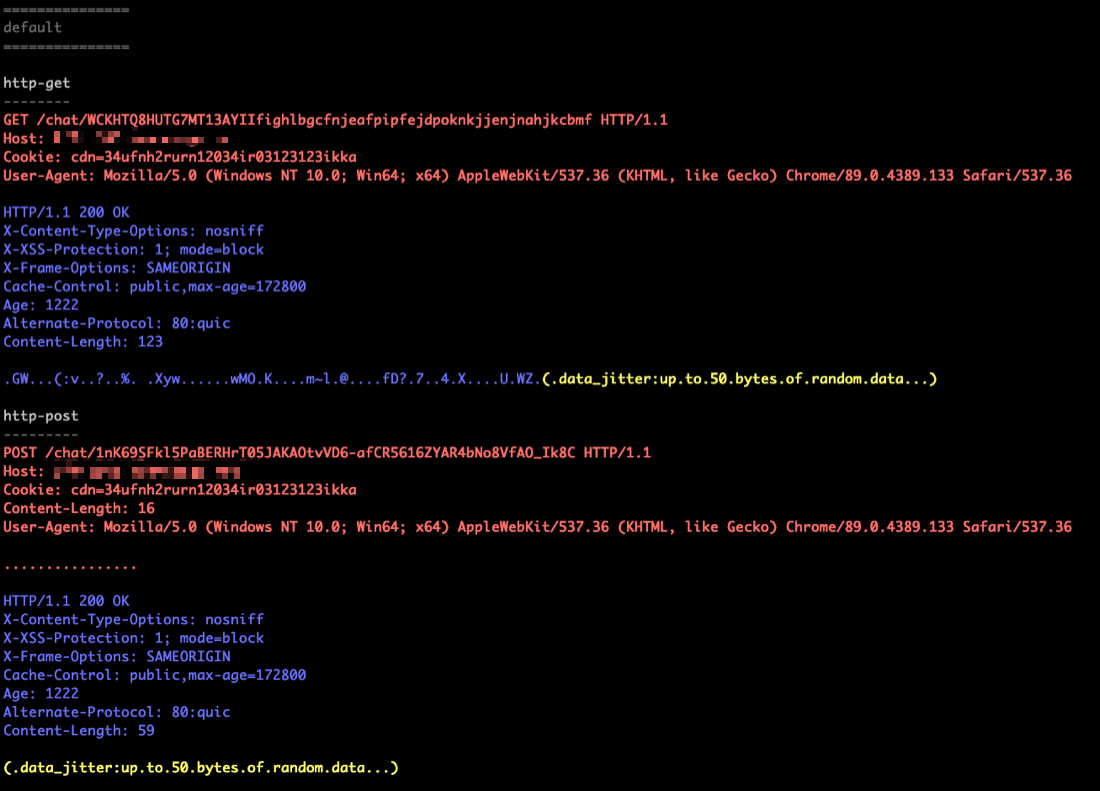
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 mr-un1k0d3r/maliciousmacrogenerator
Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 flangvik/amsi.fail
C# Azure Function with an HTTP trigger that generates obfuscated PowerShell snippets that break or disable AMSI for the current process.
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
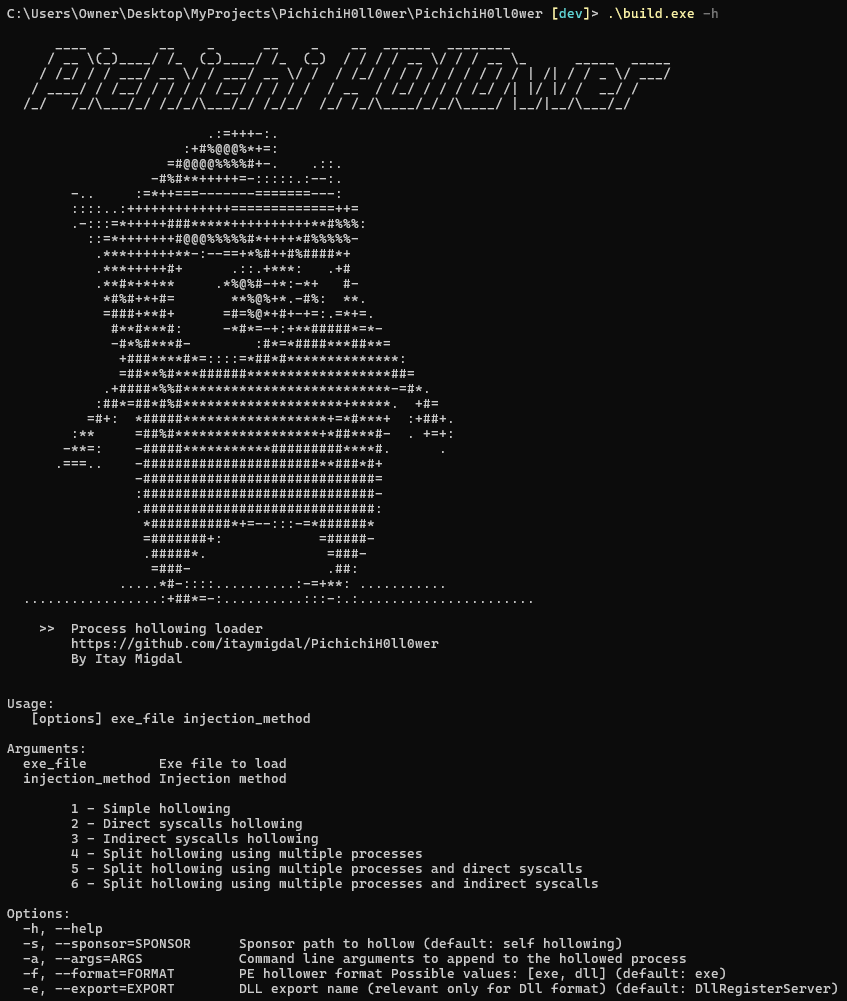 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 alealeluyah/cve-2022-42889-text4shell-poc
This repository contains a Python script to automate the process of testing for a vulnerability known as Text4Shell, referenced under the CVE id:…
 talatumlabs/cve-2024-0012_cve-2024-9474_poc
This PoC is targeting vulnerabilities in Palo Alto PAN-OS, specifically CVE-2024-0012 and CVE-2024-9474. This script automates the exploitation…
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 5ma1l/cve-2024-25641
This repository automates the process of exploiting CVE-2024-25641 on Cacti 1.2.26
 magicpipersec/wps-cve-2022-24934
PoC exploit server for CVE-2022-24934 that delivers a malicious payload via a fake WPS Update Server, targeting the wpsupdate.exe process for…
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…