

Exploit-Win32.CVE-2012-0158.F.doc
 robertoleonfr-es/exploit-win32.cve-2012-0158.f.doc
the name of virus is the detection of microsoft defender, is the tipic antivirus
exploitationpayload-generationpenetration-testing+2
robertoleonfr-es/exploit-win32.cve-2012-0158.f.docthe name of virus is the detection of microsoft defender, is the tipic antivirus
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 murataydemir/cve-2020-0688
[CVE-2020-0688] Microsoft Exchange Server Fixed Cryptographic Key Remote Code Execution (RCE)
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…
 pushkarup/cve-2023-23397
This script exploits CVE-2023-23397, a Zero-Day vulnerability in Microsoft Outlook, allowing the generation of malicious emails for testing and…
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
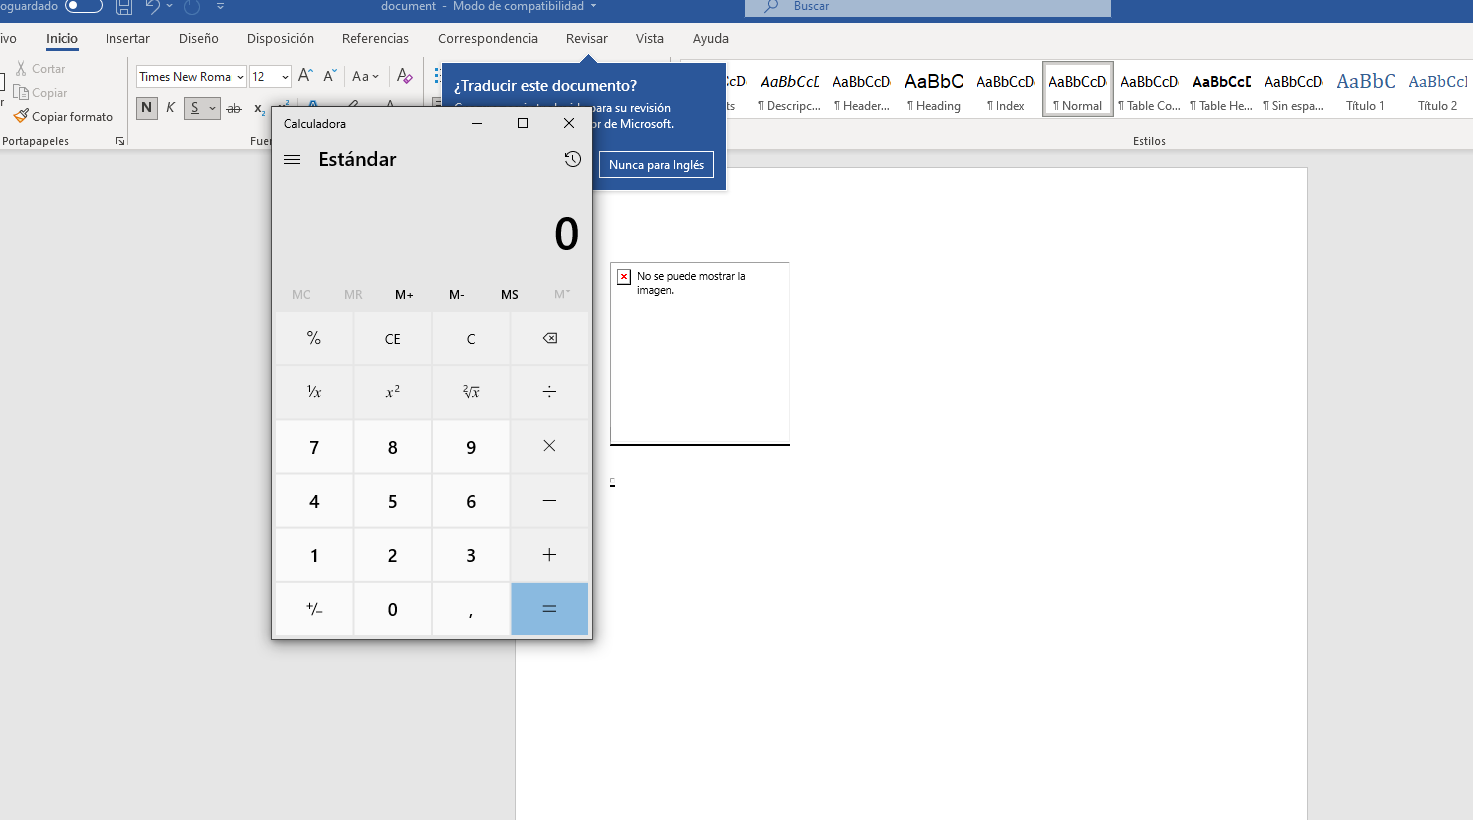 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
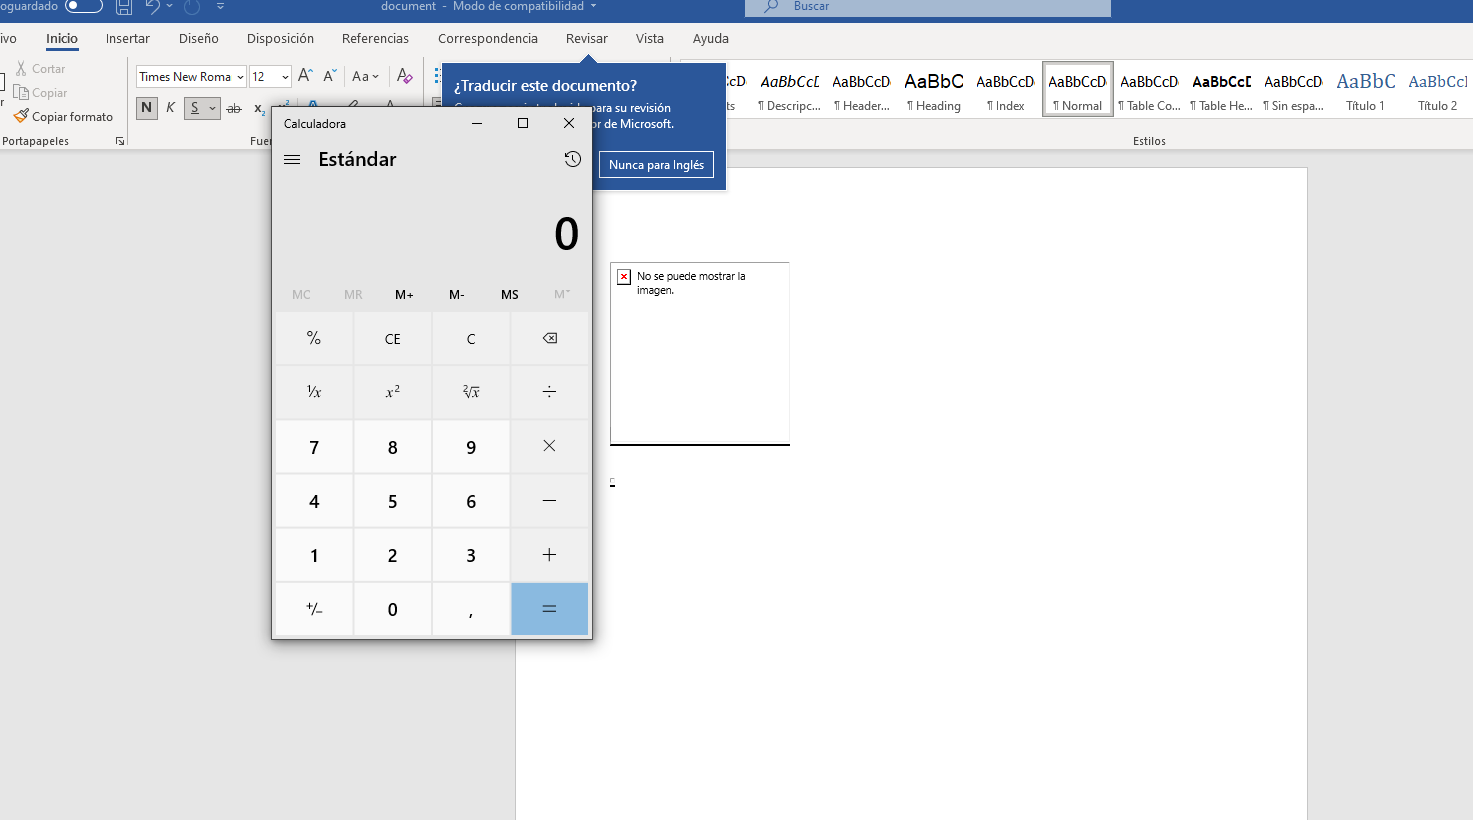 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 mbanyamer/mbanyamer-microsoft-powerpoint-use-after-free-remote-code-execution-rce
This repository contains a Proof of Concept (PoC) exploit for the **CVE-2025-47175** vulnerability found in Microsoft PowerPoint. The vulnerability…
 shubhamkanhere307/cve-2024-21413
This script is the Proof of Concept (PoC) of the CVE-2024-21413, a significant security vulnerability discovered in the Microsoft Windows Outlook…