
CVE-2023-26039
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
command-and-controlexploitationpayload-generation+3
ungabunga-ctf/cve-2023-26039CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
 th3r4ven/bifrost
Bifrost C2. Open-source post-exploitation using Discord API
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 kukrimate/cve-2020-14372
Proof-of-concept exploit and write-up for CVE-2020-14372, demonstrating Secure Boot bypass via malicious ACPI SSDT to disable kernel lockdown and…
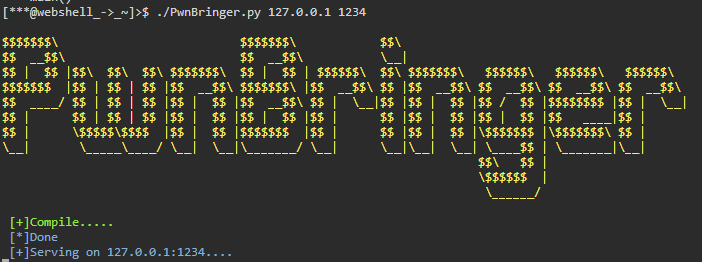 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 wavvs/doctrack
Tool to manipulate and weaponize Office Open XML documents.
 lesnuages/hershell
Multiplatform reverse shell generator
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.