

micr0_shell
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
exploitationpayload-developmentpayload-generation+2
225
senzee1984/micr0_shellmicr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 0x7n6/cve-2022-24500
Standalone exploit for CVE-2022-24500 targeting Windows SMB, generating and executing shellcode to deliver a reverse Meterpreter payload.
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
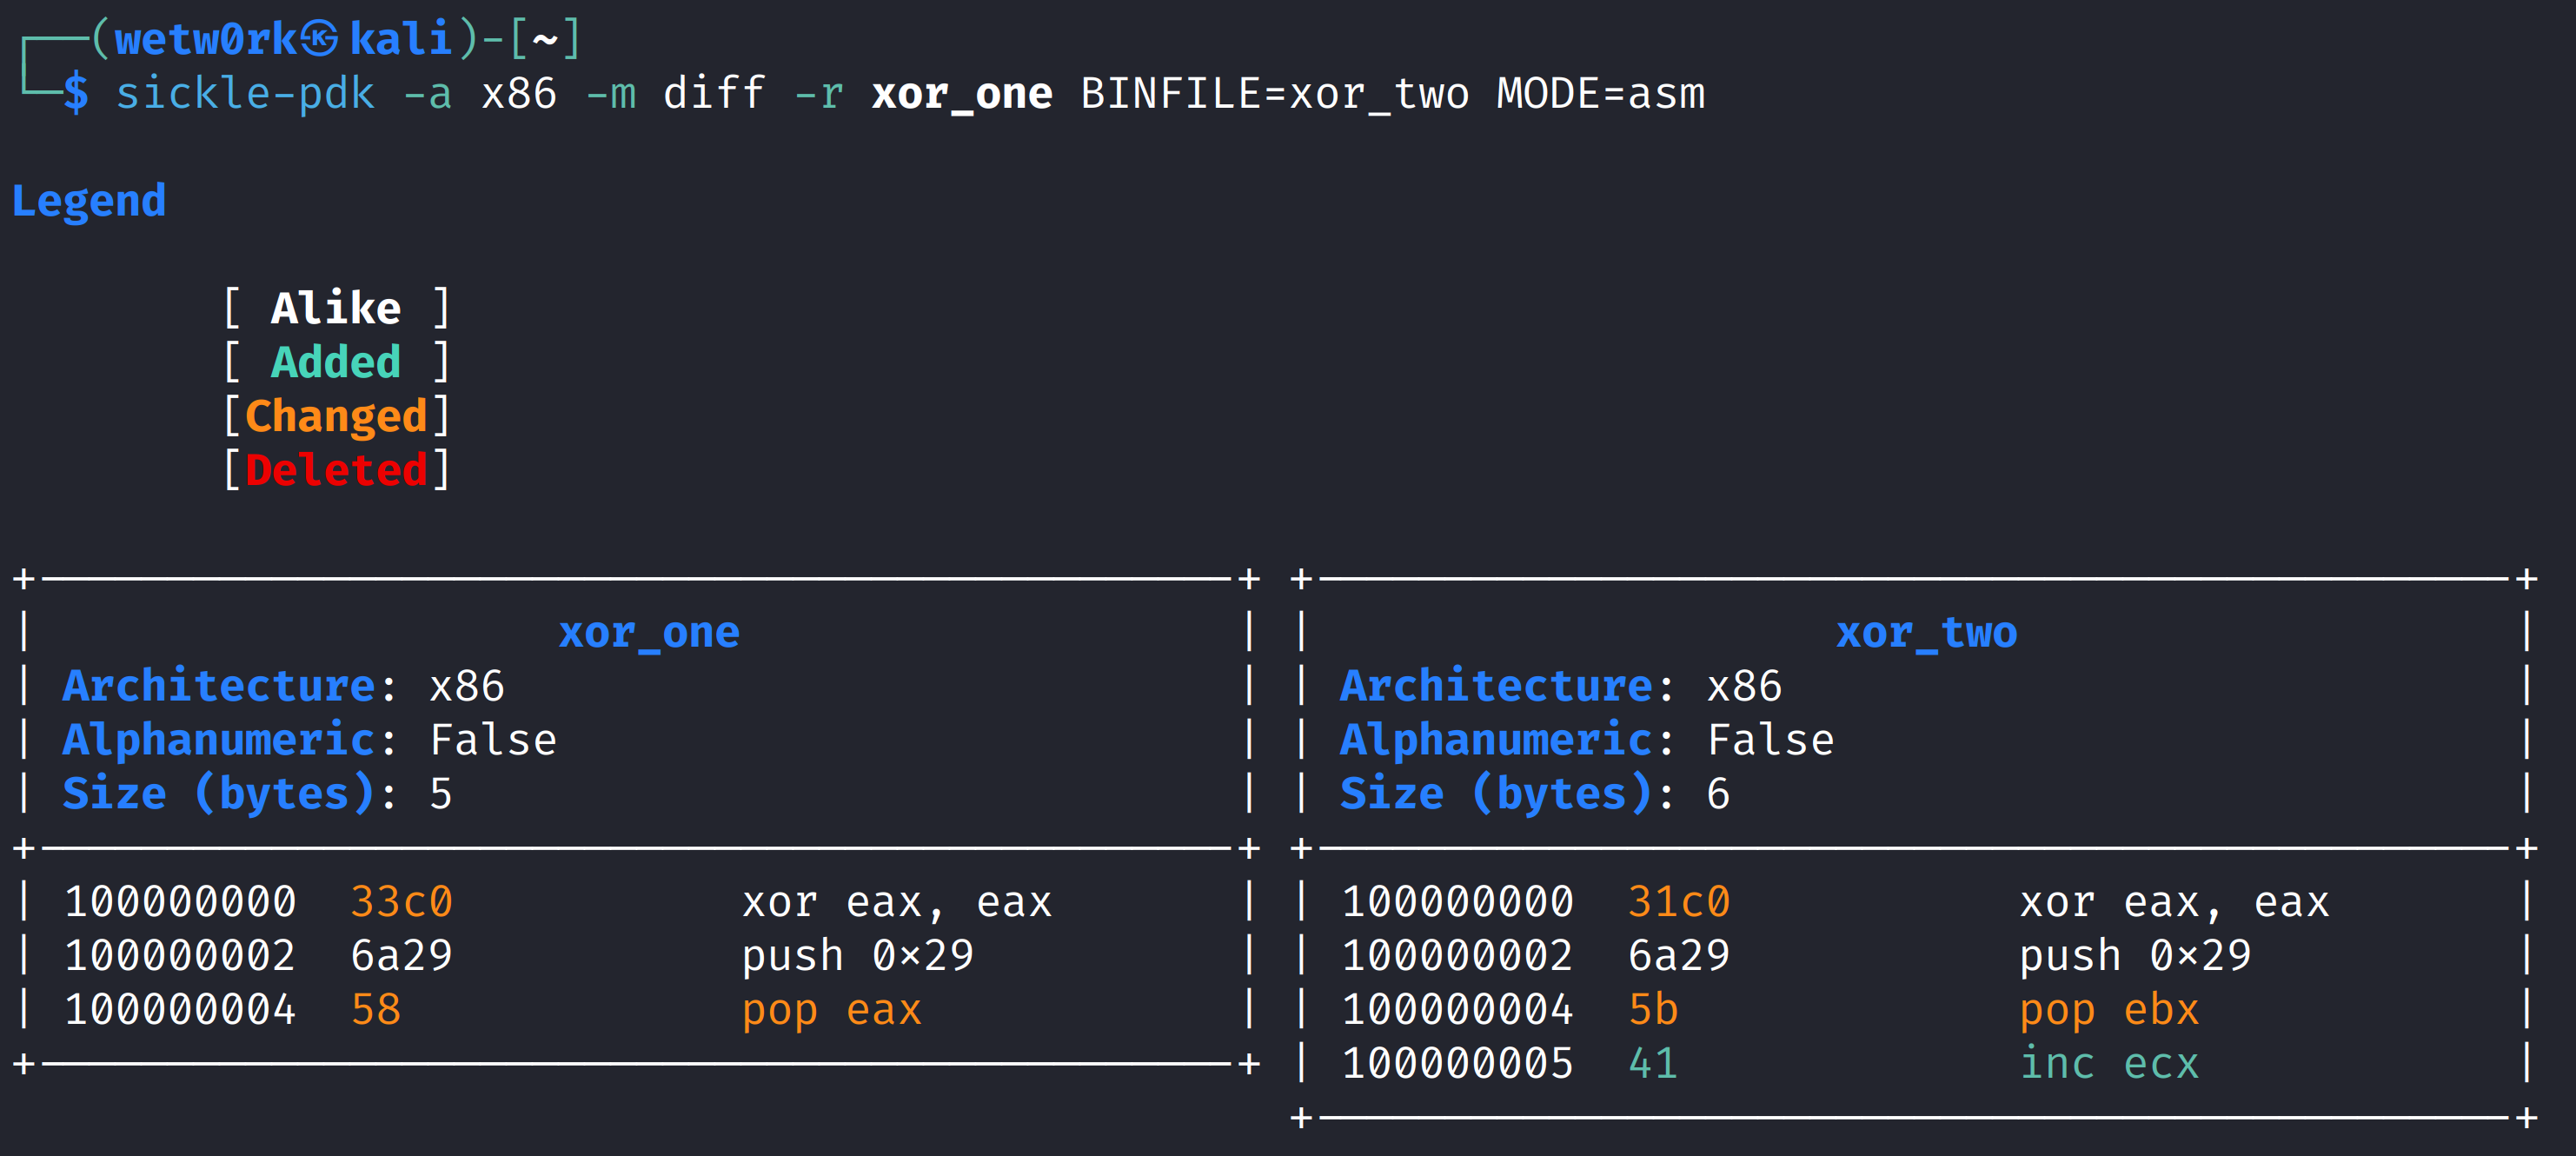 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 infobyte/exploit-cve-2021-21086
Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.