

Stitch
 nathanlopez/stitch
Python Remote Administration Tool (RAT)
educationpassword-crackingpayload-generation+2
3.7k9 years ago
nathanlopez/stitchPython Remote Administration Tool (RAT)
 badb33f/apache-log4j-poc
Proof of Concept of apache log4j LDAP lookup vulnerability. CVE-2021-44228
 tshaq17/vsftpd-2.3.4---backdoor-command-execution
vsftpd 2.3.4 (CVE-2011-2523) a critical vulnerability that leads to Reverse Root Shell. In this repo I will do a PoC how to exploit it step by step,…
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
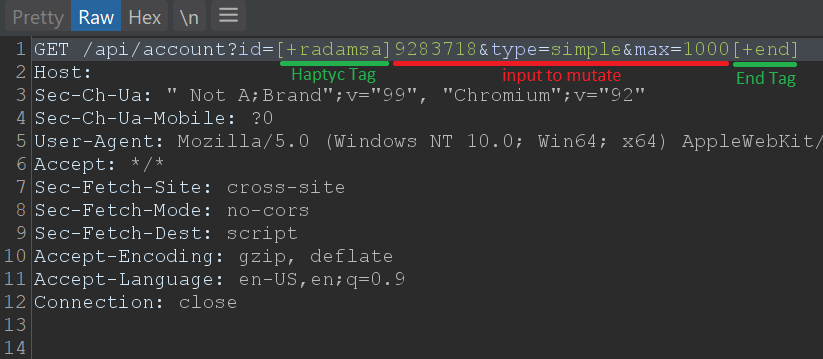 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 likekabin/cve-2018-20250
Python exploit script for CVE-2018-20250 that generates a malicious RAR archive to achieve code execution via WinRAR's ACE file extraction…
 tzwlhack/cve-2018-20250
Automated exploit script for CVE-2018-20250 (WinRAR ACE extraction code execution) that generates a malicious archive file embedding a payload into…
 pimps/cve-2017-1000486
Primefaces <= 5.2.21, 5.3.8 or 6.0 - Remote Code Execution Exploit
 tomasmussi/activemq-cve-2023-46604
Repository to exploit CVE-2023-46604 reported for ActiveMQ
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 skilfoy/cve-2024-4323-exploit-poc
This proof-of-concept script demonstrates how to exploit CVE-2024-4323, a memory corruption vulnerability in Fluent Bit, enabling remote code…
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 kossatzd/log4j-cve-2021-44228-test
demo project to highlight how to execute the log4j (CVE-2021-44228) vulnerability
 vidura2/cve-2024-46377
Python PoC script exploiting an arbitrary file upload vulnerability in Best House Rental Management System 1.0 to upload a PHP web shell and execute…
 aeolustf/cve-2018-20250
Generates malicious RAR archives automatically to exploit CVE-2018-20250 and achieve code execution via WinRAR ACE path traversal.
 wyatu/cve-2018-20250
exp for https://research.checkpoint.com/extracting-code-execution-from-winrar
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590