

Villain
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
command-and-controlexploit-frameworkspayload-generation+4
4.5k
t3l3machus/villainVillain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
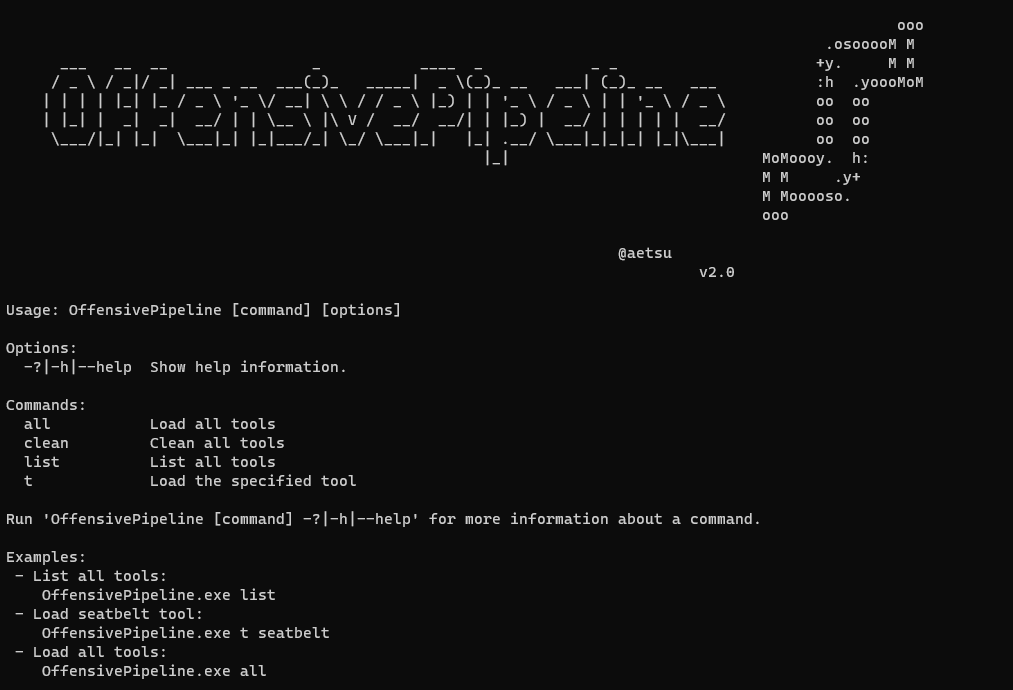 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 simoesctt/sctt-2026-33-0007-the-ole-vortex-laminar-bypass-
Microsoft just released emergency patches for CVE-2026-21509, a zero-day in the Office Suite that bypasses OLE/COM mitigations when a user simply…
 ptoomey3/evilarc
Create tar/zip archives that can exploit directory traversal vulnerabilities
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 geniuszly/cve-2022-44149
Python script to test CVE-2022-44149 router vulnerability via authenticated payload delivery to the web interface, with logging for security…
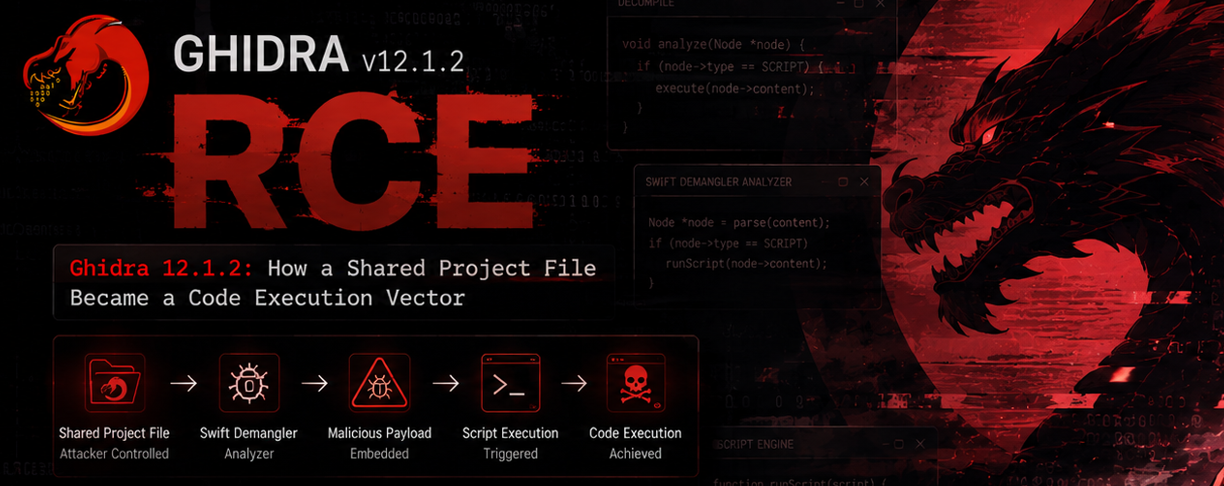 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 sud0x00/log4j-cve-2021-44228
CVE-2021-44228
 nanaao/csv-plus_vulnerability
👻 [PoC] CSV+ 0.8.0 - Arbitrary Code Execution (CVE-2022-21241)
 ahajnik/cve-2022-34919
Proof-of-concept exploit for CVE-2022-34919, demonstrating unauthenticated arbitrary file upload and RCE in Contensis CMS Classic interface via…
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
 cfalta/powershellarmoury
A PowerShell armoury for security guys and girls
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 cujanovic/ssrf-testing
SSRF (Server Side Request Forgery) testing resources
 cyberark/shimit
A tool that implements the Golden SAML attack
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing