
CVE-2026-34197
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
exploitationlabs-practicepayload-generation+4
kondordevsecuritycorp/cve-2026-34197Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 oscerd/cve-2026-40473
Reproducer for CVE-2026-40473: Apache Camel camel-mina MinaConverter.toObjectInput unsafe deserialization (RCE over TCP/UDP)
 asdasddqwdq29-a11y/cve-2026-34197
Apache ActiveMQ RCE via Jolokia vulnerability analysis and reproduction notes
 joshuavanderpoll/cve-2026-3891
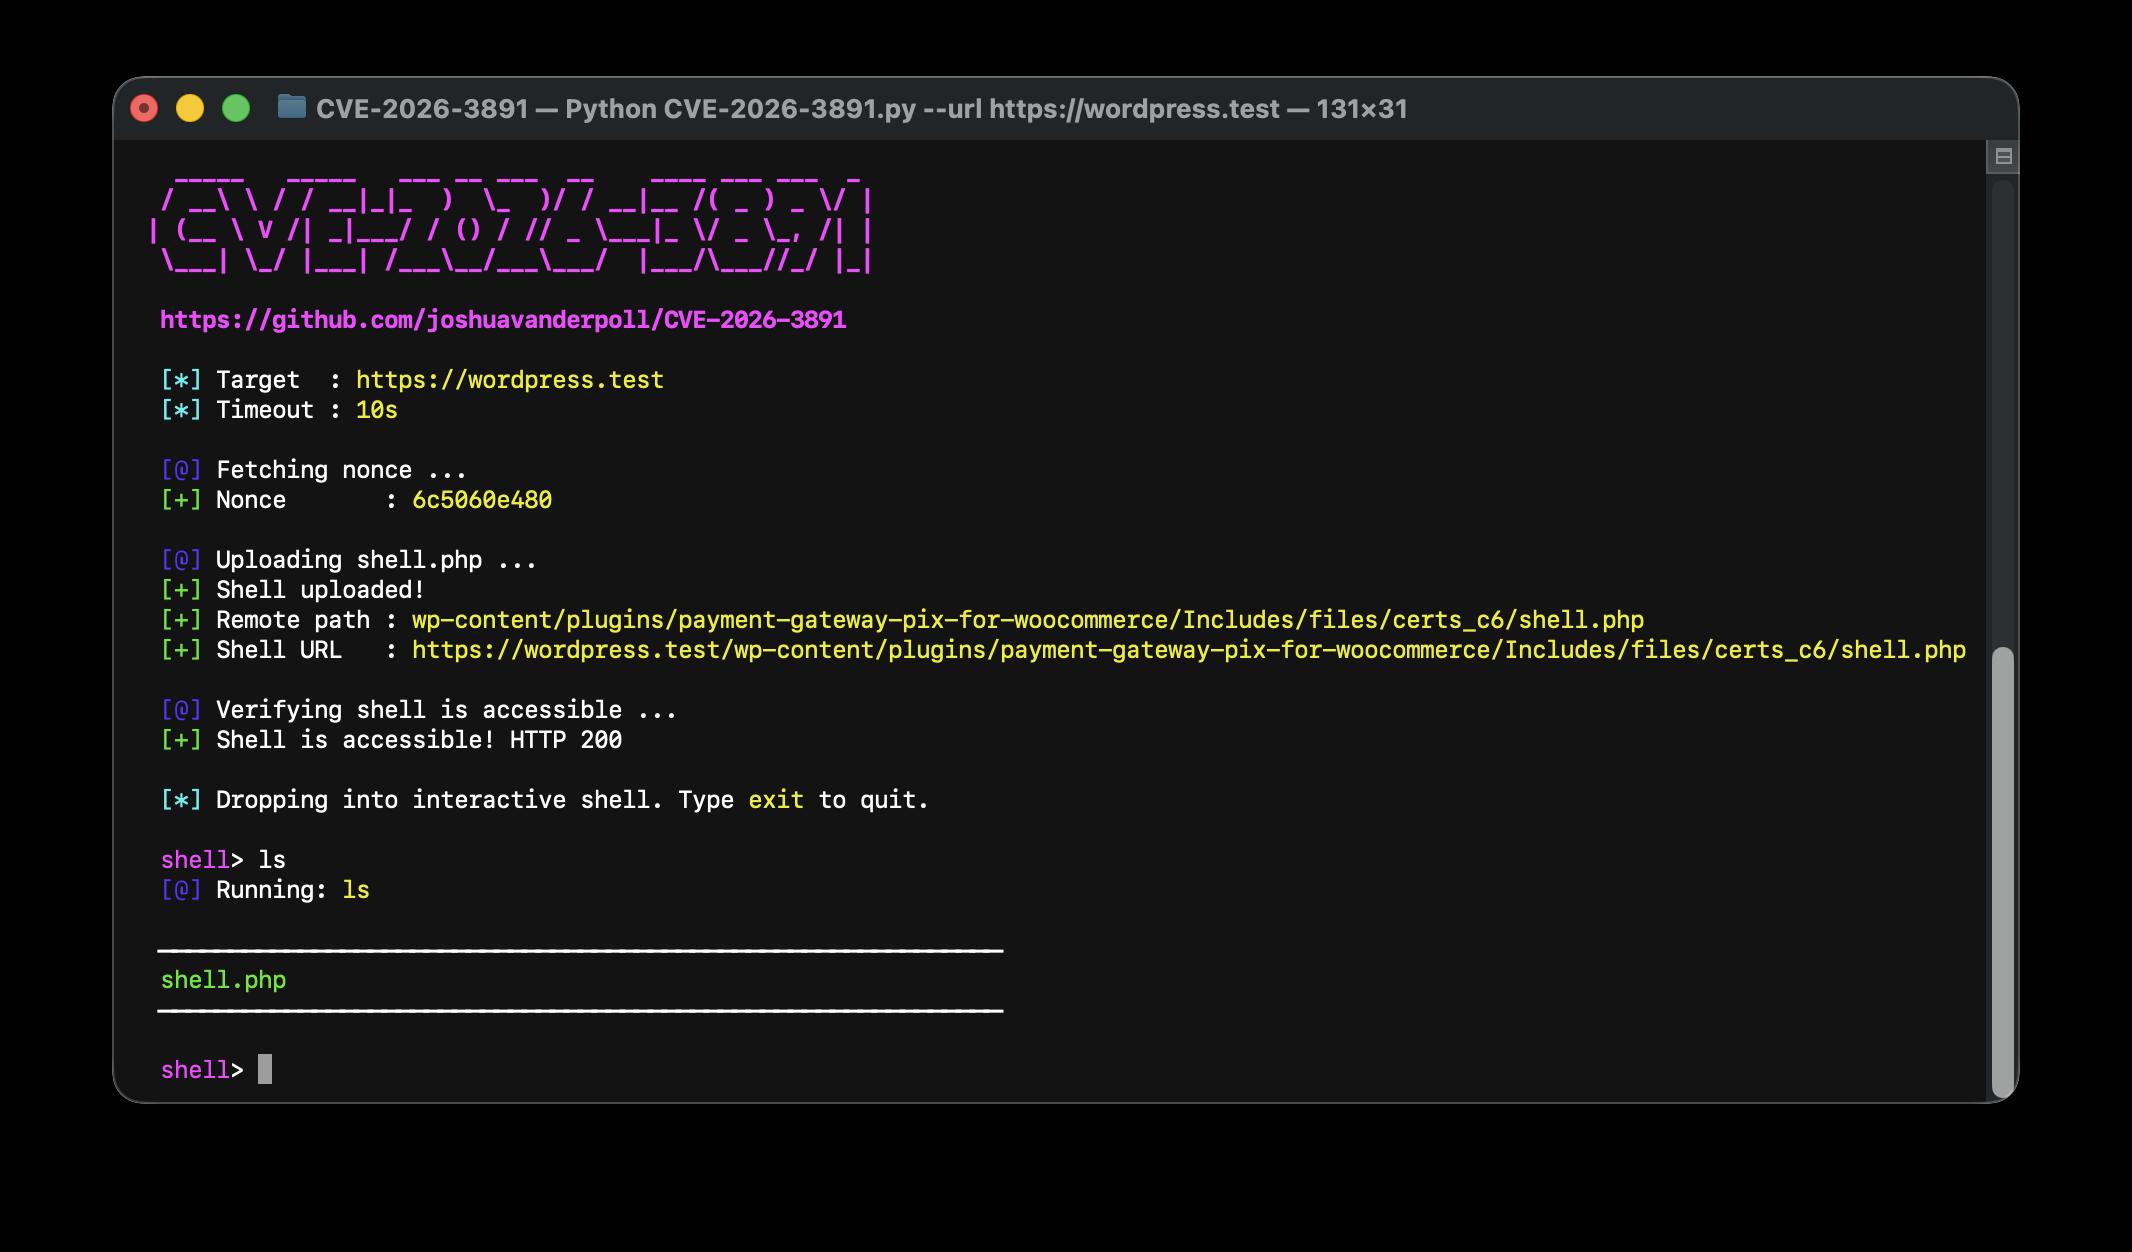
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload (CVE-2026-3891) PoC
 shinthink/cve-2026-3891
Pix for WooCommerce Unauthenticated File Upload via certificate_crt_path Parameter | CVSS 9.8
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 tausifzaman/cve-2026-3844
PoC exploit for CVE-2026-3844, a critical unauthenticated file upload vulnerability in the WordPress Breeze plugin leading to RCE.
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 razureink/cve-2026-21509-office_security_bypass_reproduction
CVE Reproduction: cve-2026-21509-office_security_bypass_reproduction
 shinthink/cve-2026-56291
Balbooa Forms (com_baforms) < 2.4.1 — Unauthenticated File Upload to RCE via form.uploadAttachmentFile | CVSS 9.8 | CISA KEV
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8