

PayloadsAllTheThings
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
ctfcurated-resourceseducation+8
82.0k
swisskyrepo/payloadsallthethingsA list of useful payloads and bypass for Web Application Security and Pentest/CTF
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
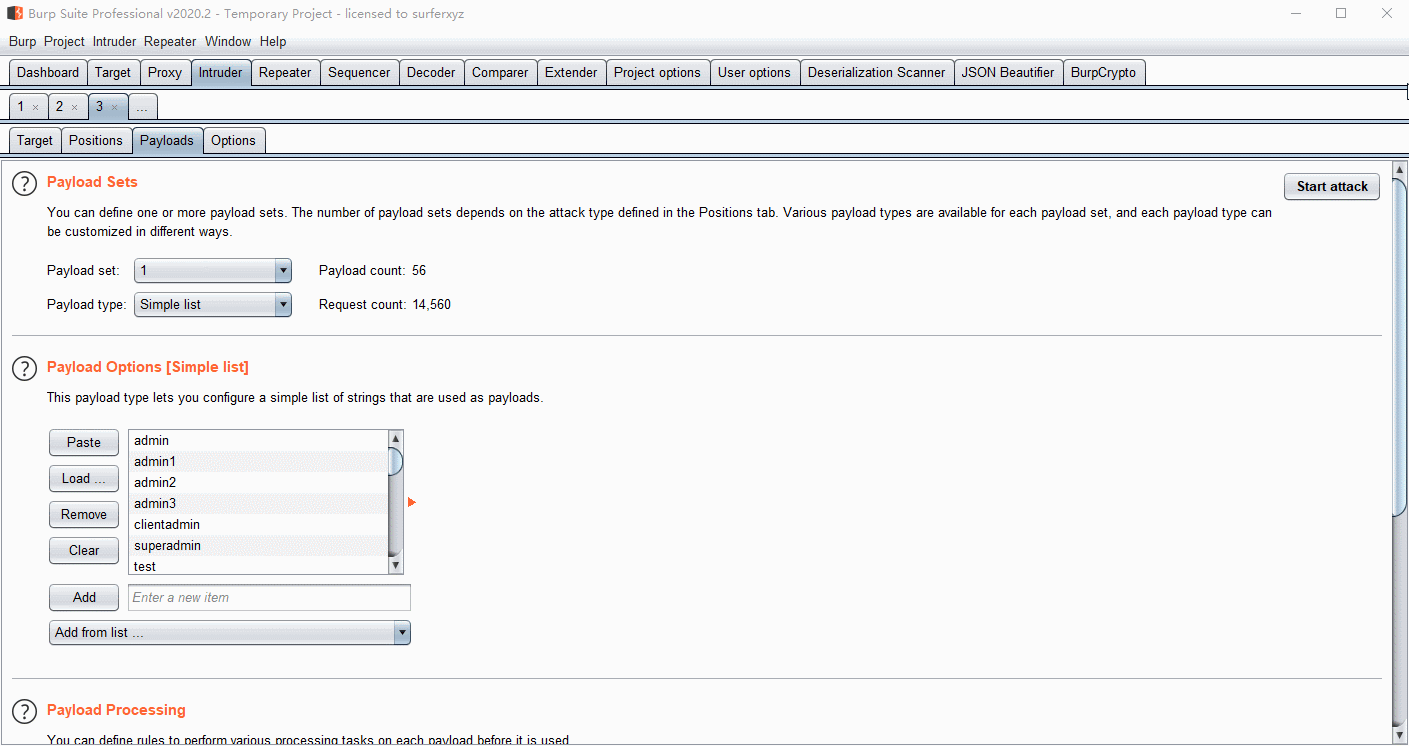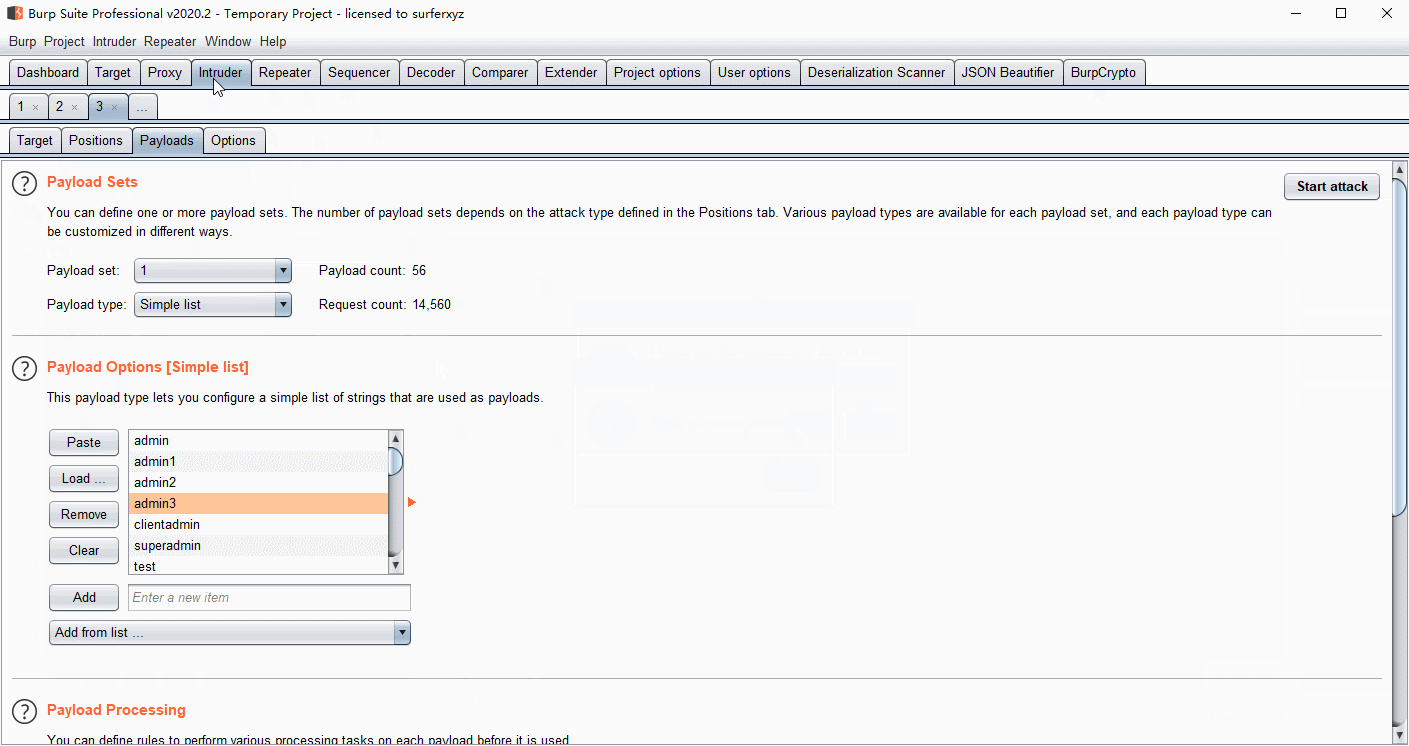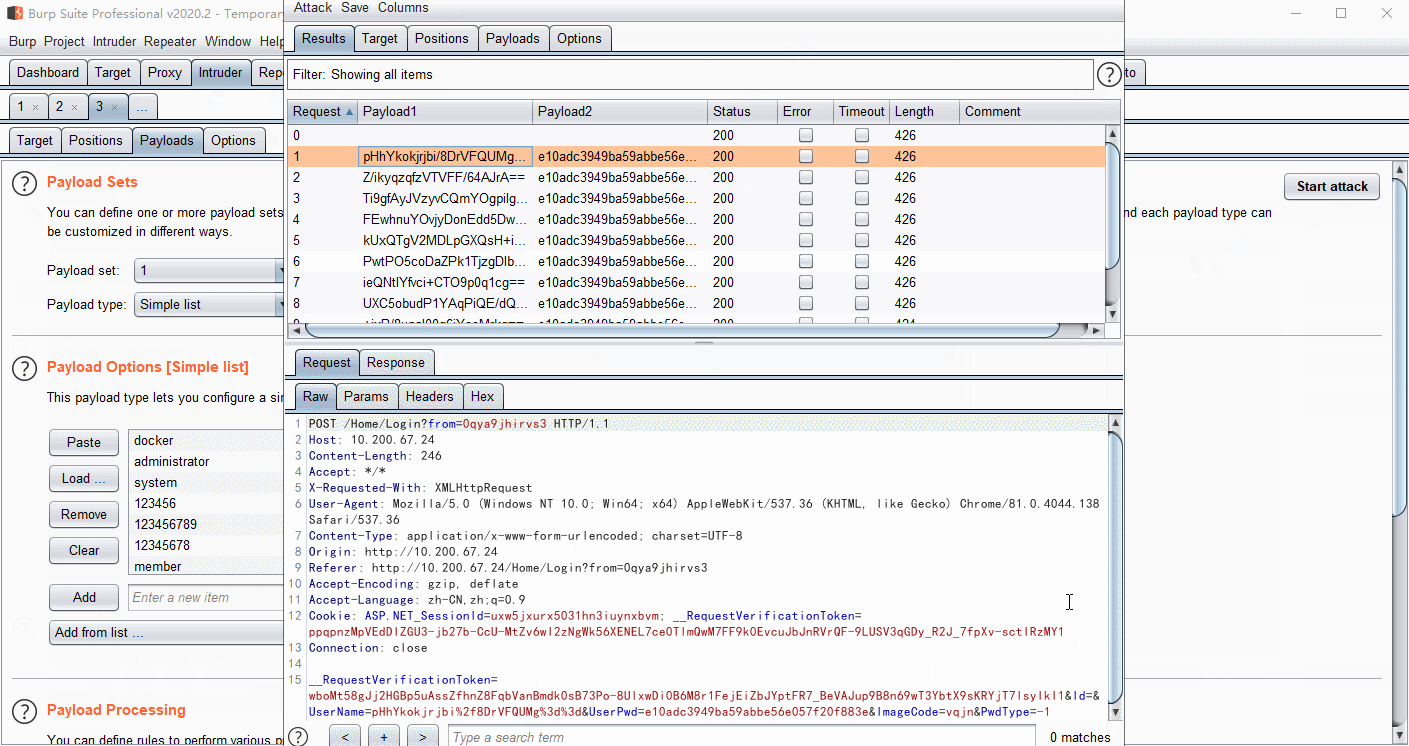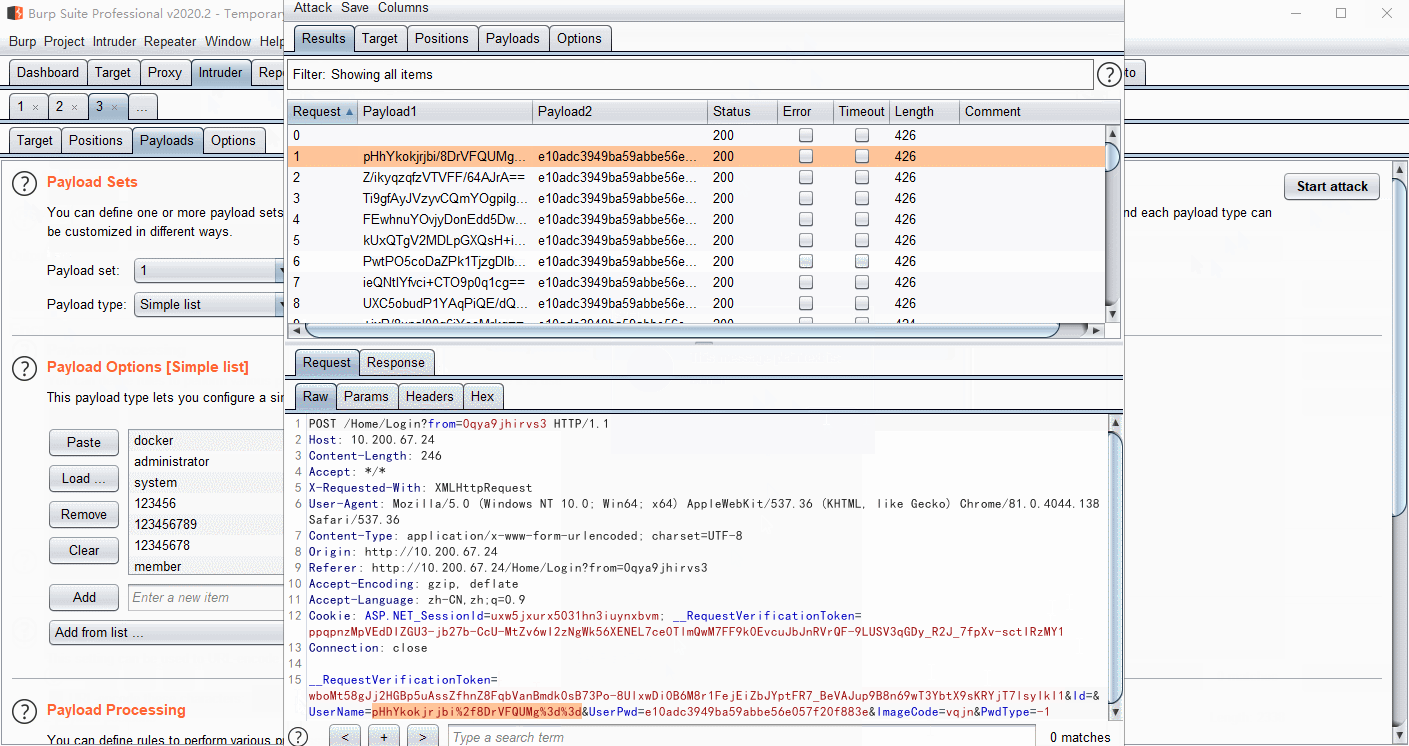 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 dlegs/php-jpeg-injector
Injects PHP payloads into JPEG images for web application exploitation, bypassing GD library image processing to achieve remote code execution.
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 fidjiw/cve-2023-38646-poc
Proof-of-concept exploit for CVE-2023-38646, demonstrating remote code execution in a web application. Intended for security testing and…
 securifera/cve-2018-16156-exploit
Exploit for CVE-2018-16156 targeting a remote code execution vulnerability in a web application, providing a proof-of-concept payload for security…
 mrsqar-ye/door404
Web application backdoor builder
 adnanapriliyansyahh/cve-2022-1592
Python-based proof-of-concept for CVE-2022-1592 that accepts a target URL and runs vulnerability checks against the specified web application.
 darkvirus-7x/exploit-cve-2020-24815
Proof-of-concept Python exploit for CVE-2020-24815 targeting a web application POST endpoint with cookie-based session handling and automated payload…
 neowans/cve-2018-19246
Proof-of-concept exploit for CVE-2018-19246 with Docker-based deployment and Pocsuite integration for automated web application vulnerability testing.
 rampanic/cve-2019-19609-exploit
Exploit for CVE-2019-19609, a remote code execution vulnerability in a web application, providing proof-of-concept code for security testing.
 projectforsix/cve-2021-45428-defacer
Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.
 junnythemarksman/cve-2021-31630
Modified proof-of-concept exploit for CVE-2021-31630 targeting a web application vulnerability with reverse shell payload generation and remote code…
 cdedmondson/modified-cve-2019-15107
Modified exploit for CVE-2019-15107 with a Perl reverse shell payload. Designed for penetration testing of the targeted web application vulnerability.
 griffinsectio/cve-2023-30800_poc_go
Proof-of-concept exploit for CVE-2023-30800, demonstrating a web application vulnerability with a Go-based payload generator for security testing and…
 xmohamed0/cve-2021-21315-poc
Proof-of-concept exploit for CVE-2021-21315, demonstrating remote code execution in a web application framework. Intended for security testing and…
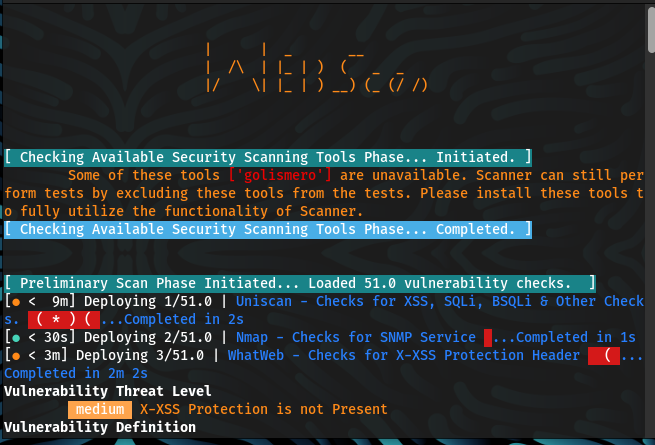 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher