
CVE-2026-63223
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
exploitationpayload-generationpenetration-testing+3
2
shinthink/cve-2026-63223CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 sunnyvale-it/cve-2022-42889-poc
CVE-2022-42889 (a.k.a. Text4Shell) RCE Proof of Concept
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 anothersec/cve-2014-4725
MailPoet Newsletters <= Arbitrary File Upload (exploiter)
 xshadow-here/cve-2026-4883
Piotnet Forms Pro <= 2.1.40 - Unauthenticated Arbitrary File Upload → RCE
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
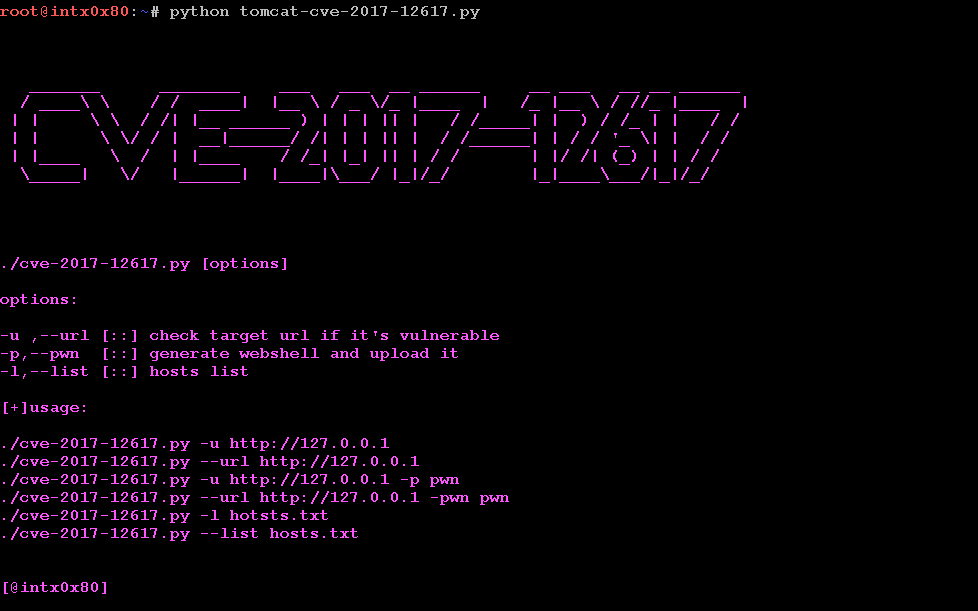 devadj/cve-2017-12617
Improved version of PikaChu CVE
 ktn1990/cve-2024-31351_wordpress_exploit
Wordpress - Copymatic – AI Content Writer & Generator <= 1.6 - Unauthenticated Arbitrary File Upload
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…