MaliciousMacroGenerator

Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.

Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.

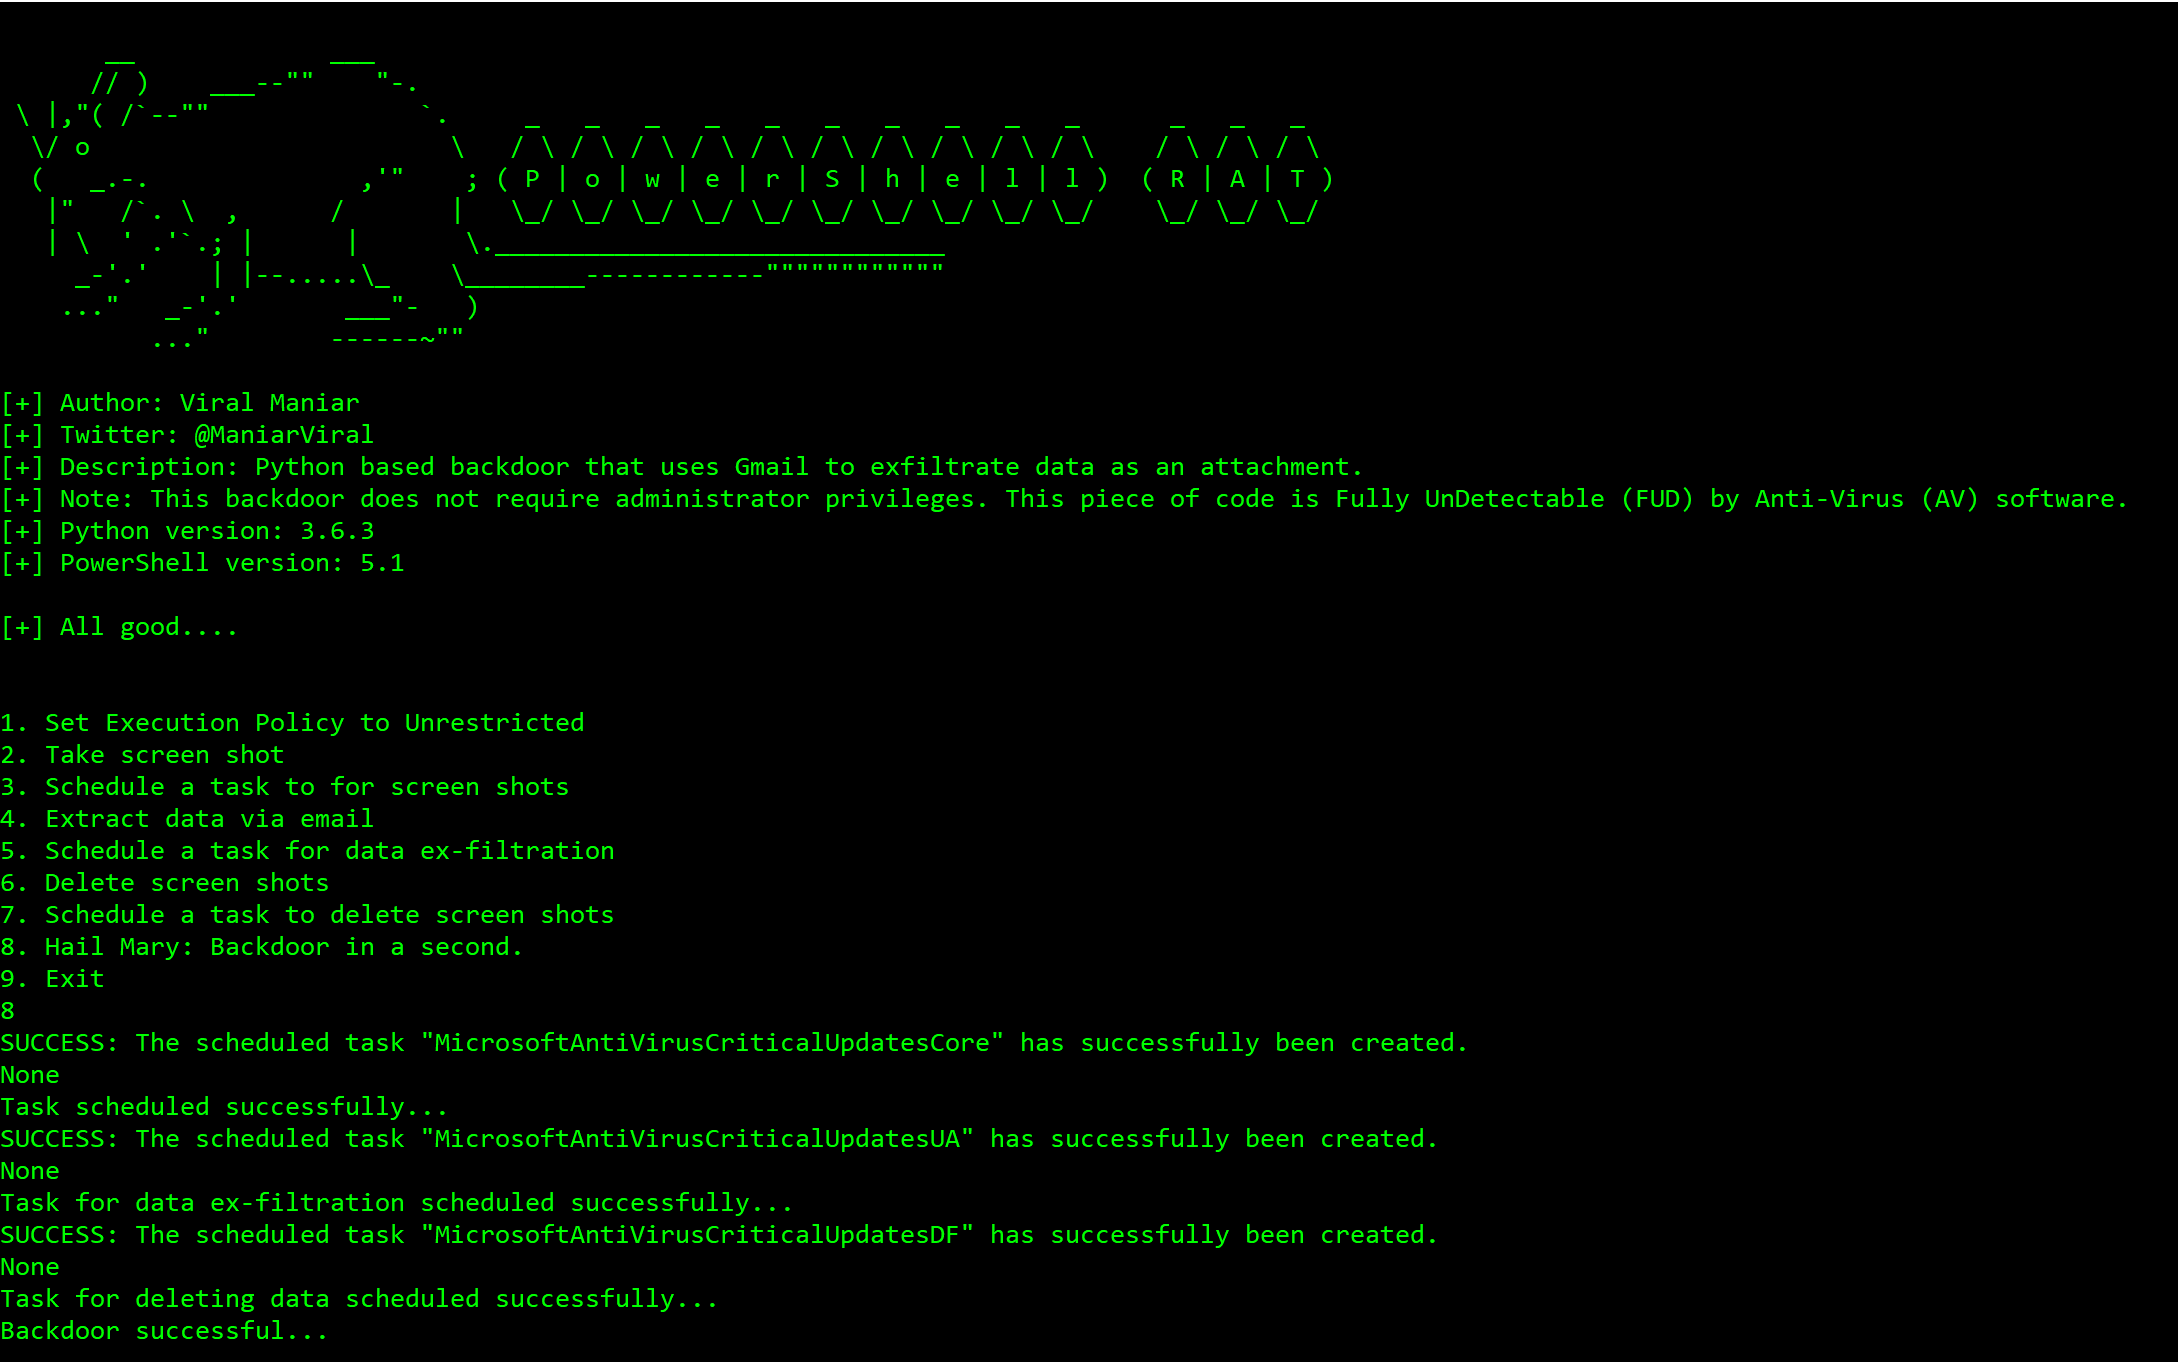
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…

evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)

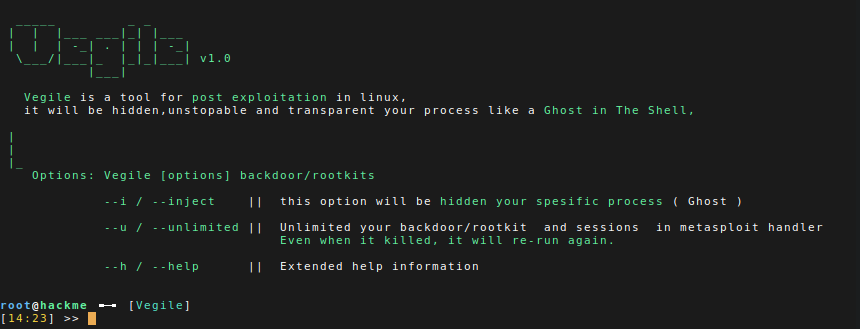
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…

DeimosC2 is a Golang command and control framework for post-exploitation.

BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…

Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…

A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.

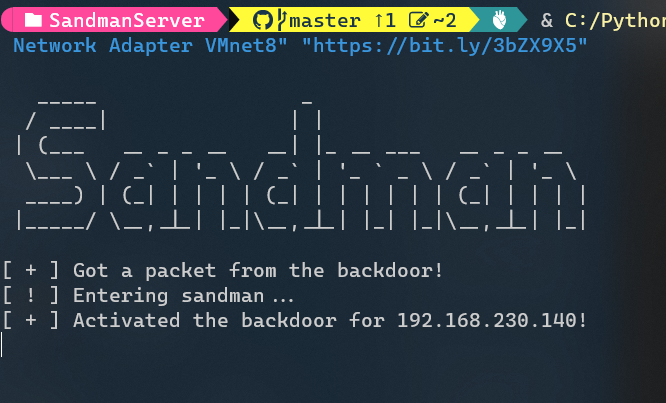
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.

Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.

Exploit toolkit for Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS. Generates crafted serialized payloads…

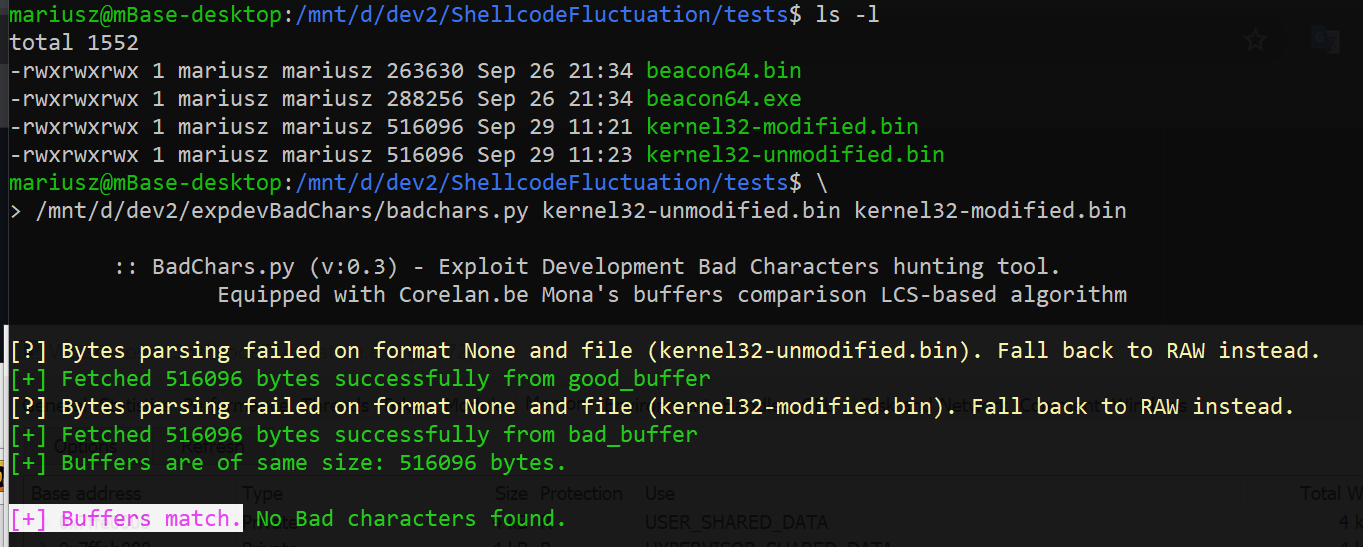
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

Exploit toolkit CVE-2017-0199 - v4.0 is a handy python script which provides pentesters and security researchers a quick and effective way to test…

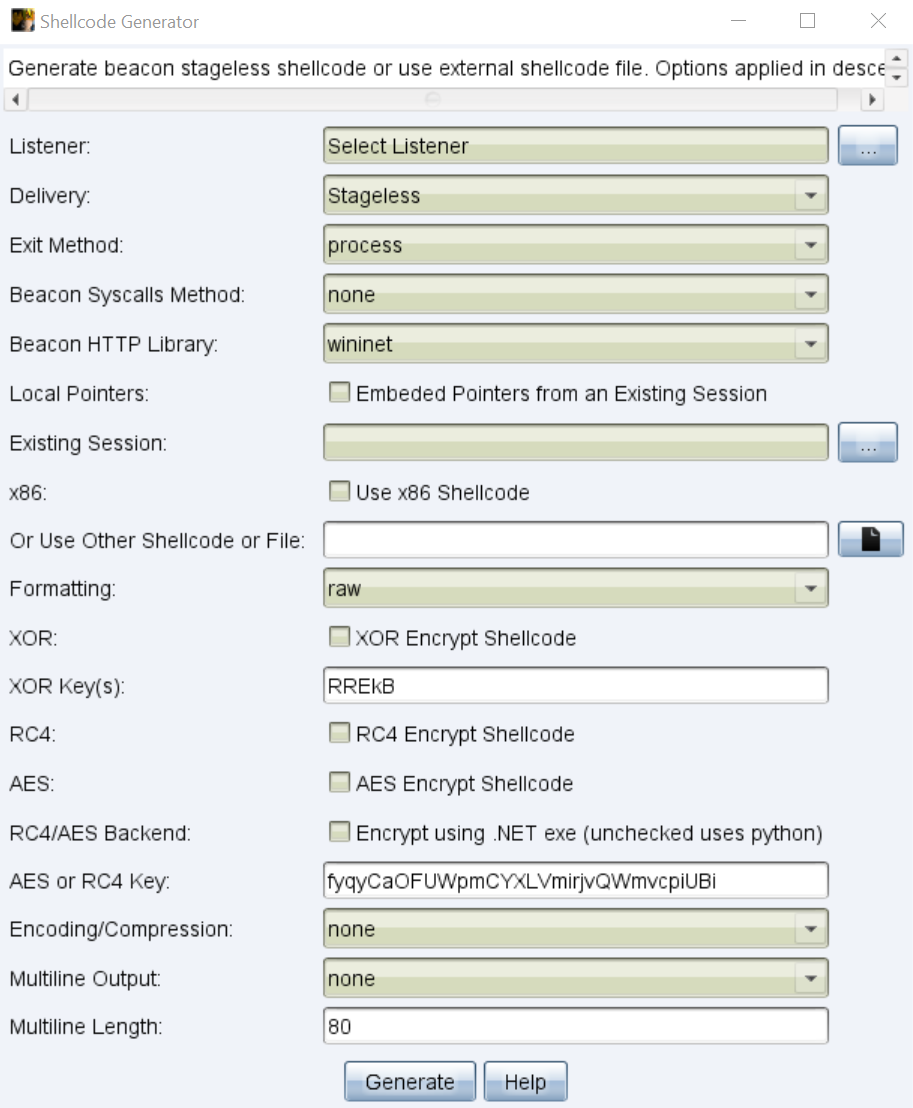
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…

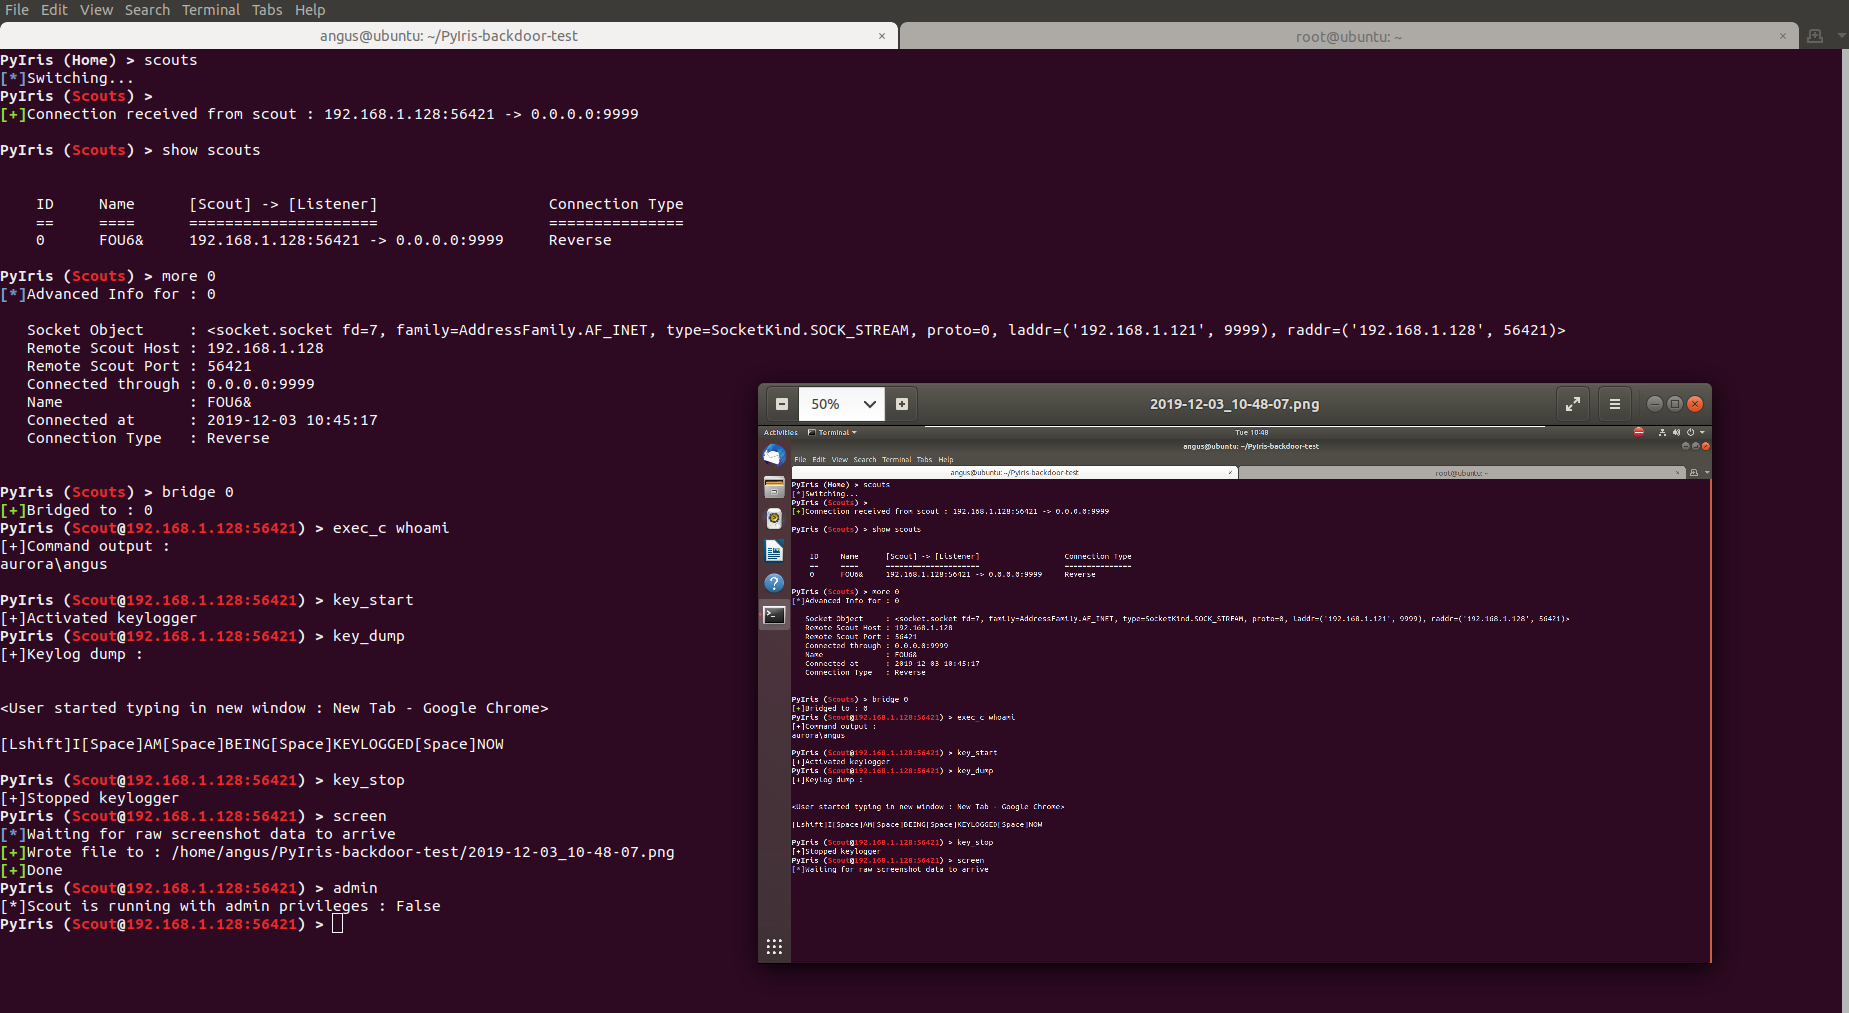
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.

All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities